
DeepLink security record
As of 3 Nov 2026, DeepLink has 2 audit reports by 1 security firm on Trustblock; the latest is by CertiK, dated 16 Jan 2025. Those reports list no open critical findings. It also holds 2 deployed contracts on 2 chains.
Record last updated . It holds audits, findings and contracts up to Nov 2026, and incidents up to Oct 2026. Trustblock does not review code.
Audits2
Newest first
Findings31
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 5 | 0 | 1 |
| Medium | 0 | 0 | 3 |
| Low | 6 | 0 | 16 |
HighCentralization Related RisksDeeplink · CertiK · 16 Jan 2025Open
In the contract `MultiSigTimeLock`, the role `_signer` has authority over the functions shown in the diagram below. Any compromise to the `_signer` account may allow the hacker to take advantage of this authority and remove a signer from the signers list, create a new proposal with execution delay, approve a proposal, revoke approval for a proposal, update required approval count, add a new signer, authorize upgrade for a new implementation address, and update the minimum delay seconds. 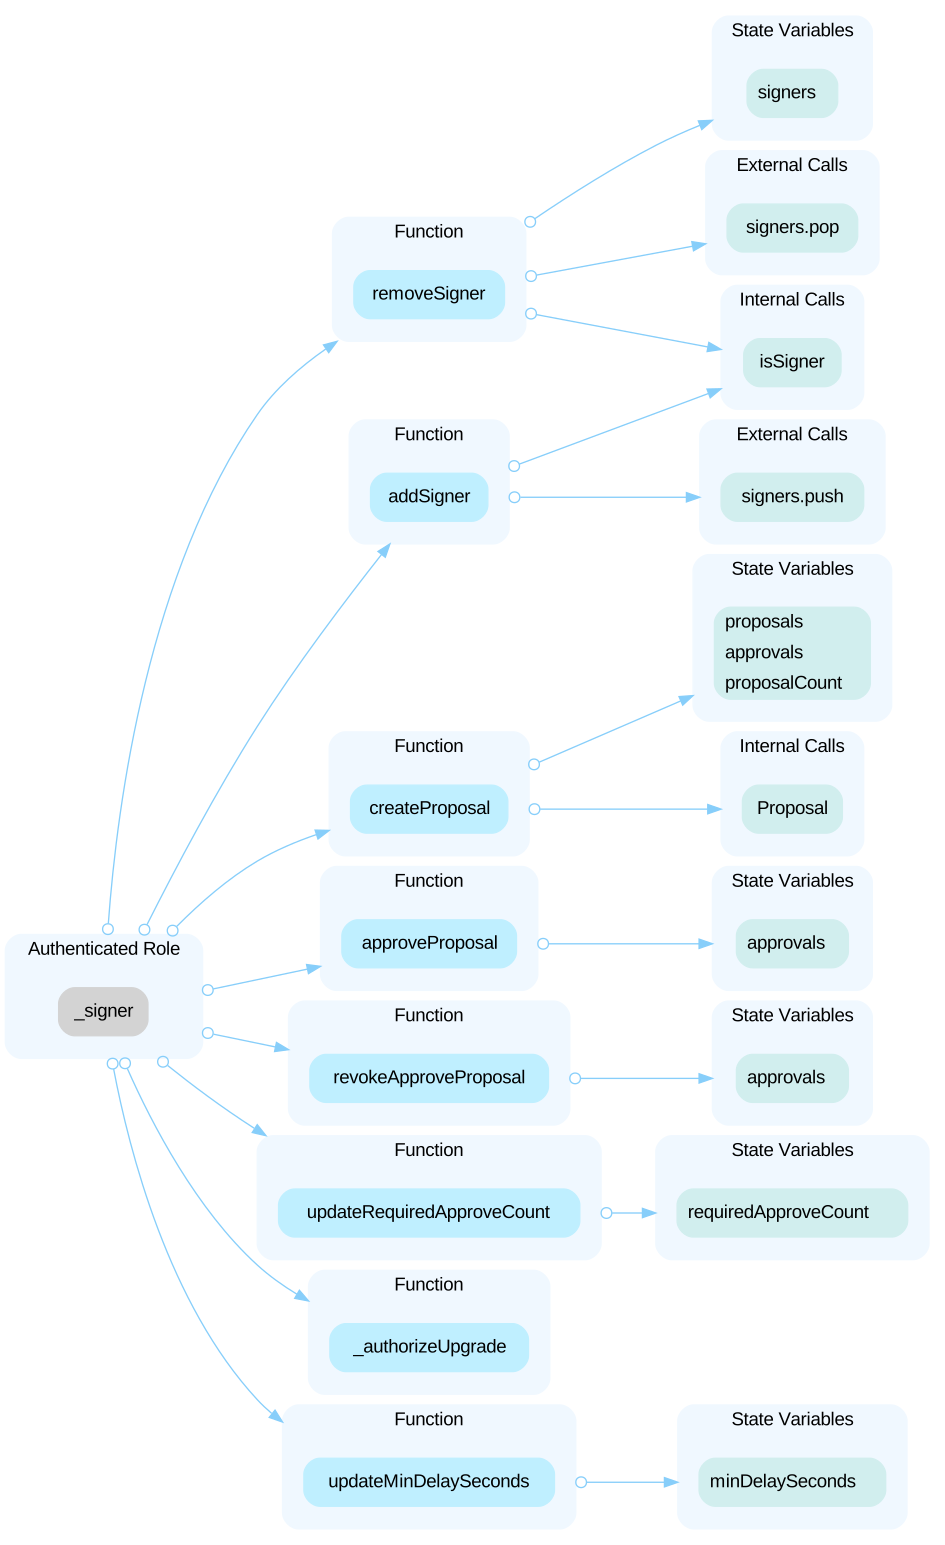 ---- In the contract `Token`, the role `timeLock` has authority over the functions shown in the diagram below. Any compromise to the `_multisigtimelockcontract` account may allow the hacker to take advantage of this authority and disable lock permanently, set the mint amount for a minter, remove lock transfer admin status, update lock duration for a wallet address, add transfer lock admin address, and enable lock permanently. 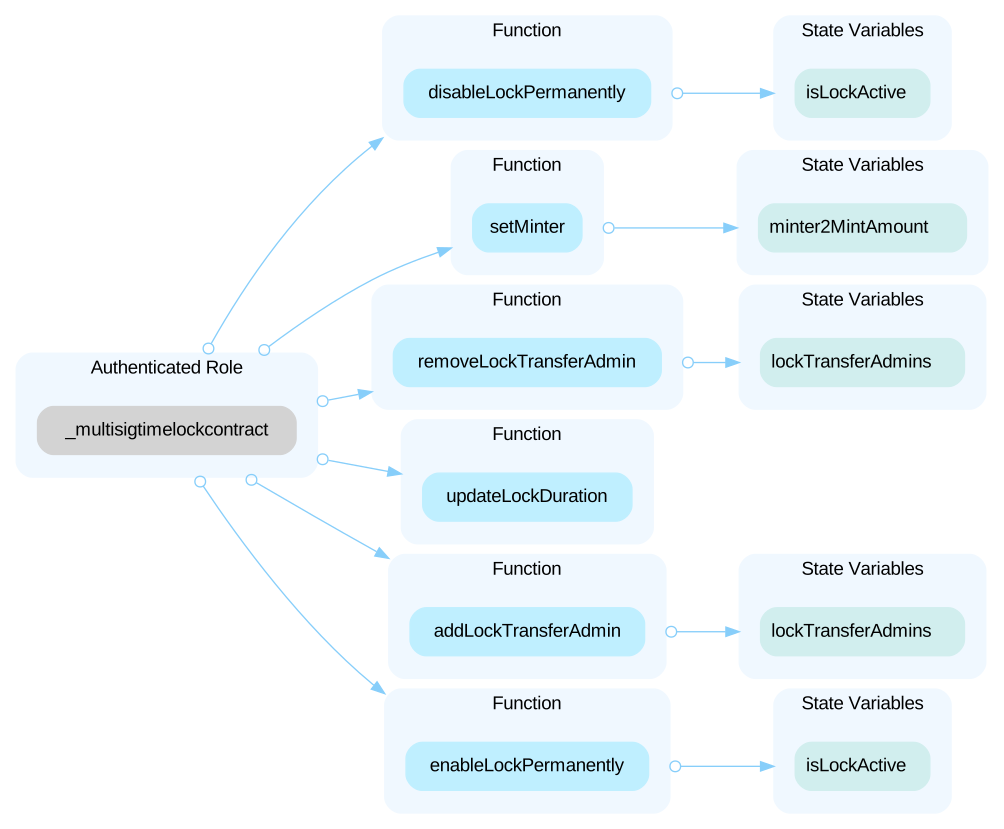 In the contract `Token`, the role `lockTransferAdmins` has authority over the functions shown in the diagram below. Any compromise to the `lockTransferAdmins` account may allow the hacker to take advantage of this authority and transfer and lock tokens for a specified duration. 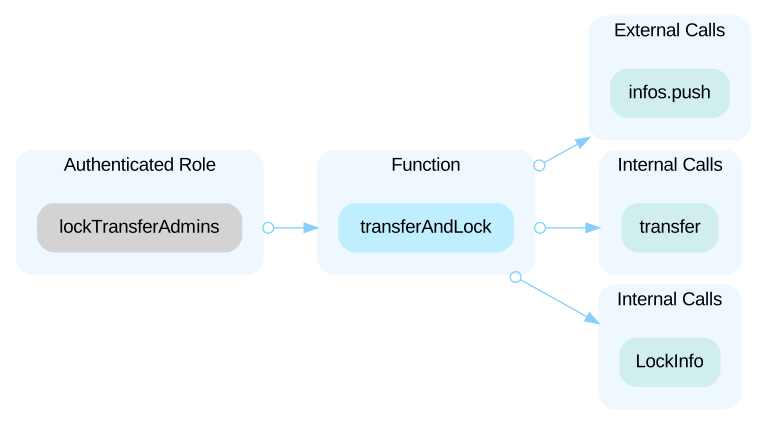 In the contract `Token`, the role `minter` has authority over the function below. Any compromise to the `minter` account may allow the hacker to take advantage of this authority and mint tokens to any accounts. - `mint()`
Open the reportHighCentralized Control of Contract UpgradeDeeplink · CertiK · 16 Jan 2025Open
In the contracts `Token` and `MultiSigTimeLock`, the role `canUpgradeAddress` of the `Token` contract and the role `canUpgradeAddress` of the `MultiSigTimeLock` contract have the authority to update the implementation contract behind the `Token` and `MultiSigTimeLock` contracts. Any compromise to these accounts may allow a hacker to take advantage of this authority and change the implementation contract, which is pointed by proxy, and therefore execute potential malicious functionality in the implementation contract.
Open the reportHighInitial Token DistributionDeeplink · CertiK · 16 Jan 2025Open
All of the **DLC** tokens are sent to the contract deployer or one or several externally-owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportHighCentralization Risksdeeplink · CertiK · 26 Sep 2024Open
**Address 0xD610Be30b06A3828A27D608a38F1E85faAFdEDcC:** In the contract `DeepLink`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and claim stuck tokens to owner, update wallet lock block, disable the lock permanently, transfer and lock tokens. 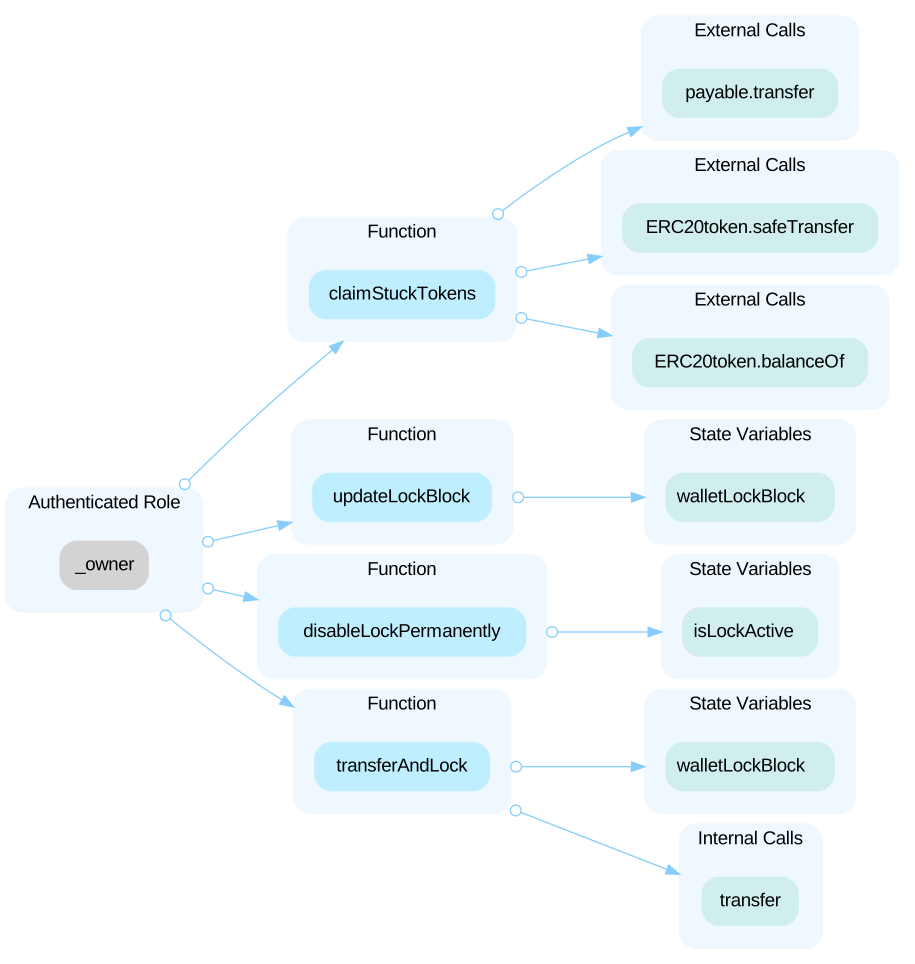 In the contract `Ownable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer ownership, renounce ownership. 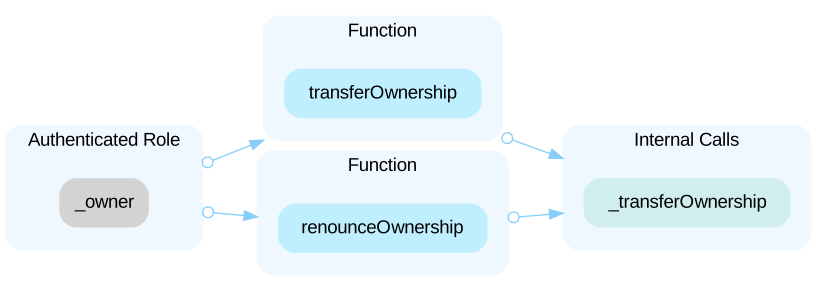 ----- **Address 0x0e933b304C9585B35546FE0aE6D0B01A72f0FdCF:** In the contract `DeepLink` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and enable trading, enable/disable addresses from transferring tokens before trading enabled. 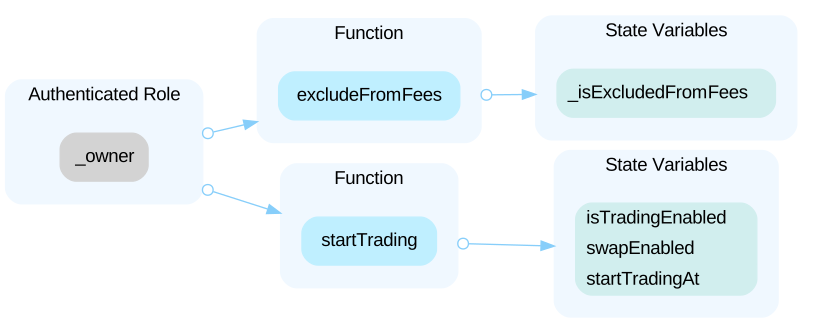 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer ownership, renounce ownership. 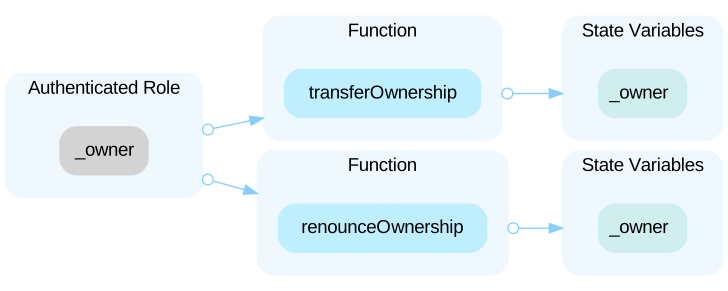
Open the reportHighInitial Token Distributiondeeplink · CertiK · 26 Sep 2024Open
All of the DLC tokens are sent to the corresponding contract owner. This is a centralization risk because the owners can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Open the reportLowDiscussion on Potential DoS with Malicious LockTrDeeplink · CertiK · 16 Jan 2025Open
The `transferAndLock` function adds a lock entry for each user, ensuring that the total number of entries does not exceed 100 to avoid potential DoS on gas: ```solidity require(infos.length < 100, "Too many lock entries"); // Limit lock entries ``` However, assigning this role to non-admin users could pose a risk of a Denial-of-Service (DoS) attack on the lock mechanism that occupies all entries with redundant entries if a user becomes malicious.
Open the reportLowDiscussion on Potential Missing Update of SupplyDeeplink · CertiK · 16 Jan 2025Open
The `Token` contract inherits from `ERC20BurnableUpgradeable`, allowing users to burn tokens through the `burn` and `burnFrom` functions. As a result of token burning, the actual token supply can decrease below the `maxSupply`. Similarly, the user may burn extra tokens compared with the available amount at the time.
Open the reportLowLocked Blockchain Native Tokensdeeplink · CertiK · 26 Sep 2024Open
The contract has a `receive()` function or payable functions, making it able to receive native tokens. However, it does not have a function to withdraw the funds, which can lead to permanently locked tokens within the contract. ```solidity=675 receive() external payable {} ```
Open the reportLowState Variable Should Be Declared Constantdeeplink · CertiK · 26 Sep 2024Open
State variables that never change should be declared as `constant` to save gas. ```solidity=640 address private DEAD = 0x000000000000000000000000000000000000dEaD; ``` - `DEAD` should be declared `constant`.
Open the reportLowUsage of `transfer()` for sending Etherdeeplink · CertiK · 26 Sep 2024Open
It is not recommended to use Solidity's `transfer()` and `send()` functions for transferring native tokens, since some contracts may not be able to receive the funds. Those functions forward only a fixed amount of gas (2300 specifically) and the receiving contracts may run out of gas before finishing the transfer. Also, EVM instructions' gas costs may increase in the future. Thus, some contracts that can receive now may stop working in the future due to the gas limitation. ```solidity=769 payable(msg.sender).transfer(address(this).balance); ``` - `DeepLink.claimStuckTokens` uses `transfer()`.
Open the reportShow 1 more
LowVariables That Could Be Declared as Immutabledeeplink · CertiK · 26 Sep 2024Open
The linked variable assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
Open the reportContracts2
| Address | Chain | Source code |
|---|---|---|
| 0x0e933b304c9585b35546fe0ae6d0b01a72f0fdcf | Chain: Ethereum | Source code: Verified source |
| 0xd610be30b06a3828a27d608a38f1e85faafdedcc | Chain: BNB Chain | Source code: Verified source |
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="deeplink"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us