Deeplink
CertiK reviewed DeepLink on 16 Jan 2025: 25 findings, 0 critical; 20 marked fixed, 5 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings25
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 1 |
| Medium | 0 | 0 | 3 |
| Low | 2 | 0 | 16 |
HighCentralization Related RisksOpen
In the contract `MultiSigTimeLock`, the role `_signer` has authority over the functions shown in the diagram below. Any compromise to the `_signer` account may allow the hacker to take advantage of this authority and remove a signer from the signers list, create a new proposal with execution delay, approve a proposal, revoke approval for a proposal, update required approval count, add a new signer, authorize upgrade for a new implementation address, and update the minimum delay seconds. 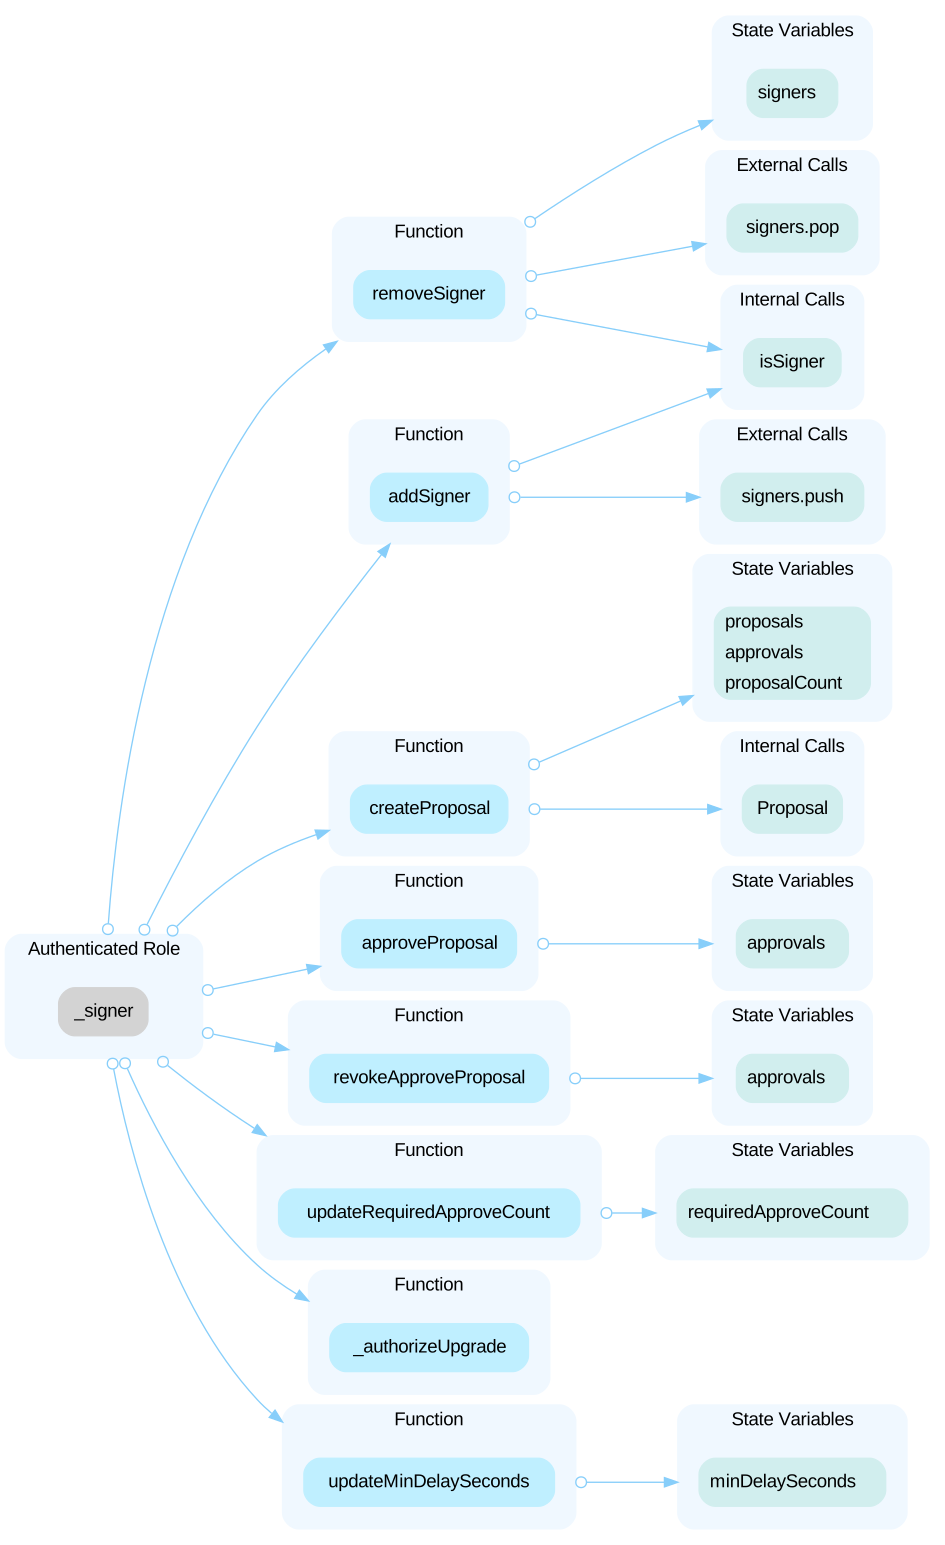 ---- In the contract `Token`, the role `timeLock` has authority over the functions shown in the diagram below. Any compromise to the `_multisigtimelockcontract` account may allow the hacker to take advantage of this authority and disable lock permanently, set the mint amount for a minter, remove lock transfer admin status, update lock duration for a wallet address, add transfer lock admin address, and enable lock permanently. 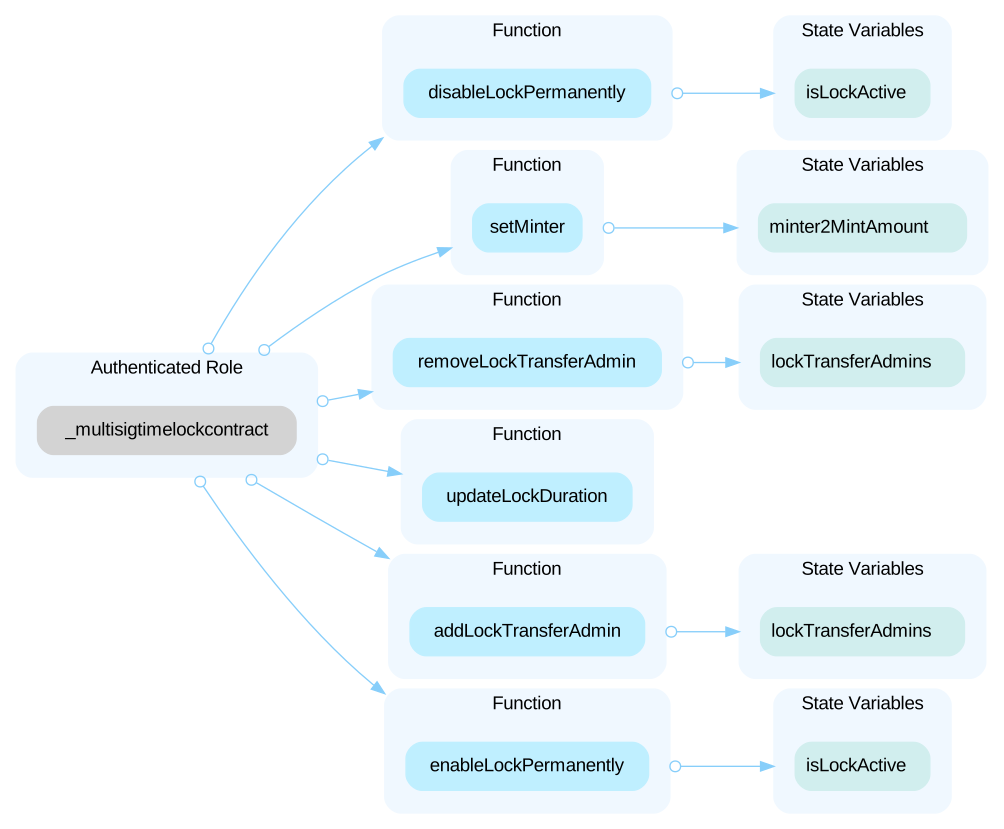 In the contract `Token`, the role `lockTransferAdmins` has authority over the functions shown in the diagram below. Any compromise to the `lockTransferAdmins` account may allow the hacker to take advantage of this authority and transfer and lock tokens for a specified duration. 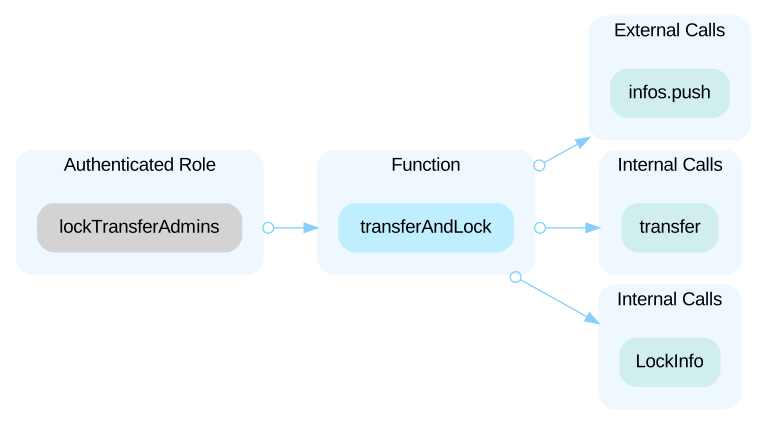 In the contract `Token`, the role `minter` has authority over the function below. Any compromise to the `minter` account may allow the hacker to take advantage of this authority and mint tokens to any accounts. - `mint()`
HighCentralized Control of Contract UpgradeOpen
In the contracts `Token` and `MultiSigTimeLock`, the role `canUpgradeAddress` of the `Token` contract and the role `canUpgradeAddress` of the `MultiSigTimeLock` contract have the authority to update the implementation contract behind the `Token` and `MultiSigTimeLock` contracts. Any compromise to these accounts may allow a hacker to take advantage of this authority and change the implementation contract, which is pointed by proxy, and therefore execute potential malicious functionality in the implementation contract.
HighInitial Token DistributionOpen
All of the **DLC** tokens are sent to the contract deployer or one or several externally-owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
LowDiscussion on Potential DoS with Malicious LockTrOpen
The `transferAndLock` function adds a lock entry for each user, ensuring that the total number of entries does not exceed 100 to avoid potential DoS on gas: ```solidity require(infos.length < 100, "Too many lock entries"); // Limit lock entries ``` However, assigning this role to non-admin users could pose a risk of a Denial-of-Service (DoS) attack on the lock mechanism that occupies all entries with redundant entries if a user becomes malicious.
LowDiscussion on Potential Missing Update of SupplyOpen
The `Token` contract inherits from `ERC20BurnableUpgradeable`, allowing users to burn tokens through the `burn` and `burnFrom` functions. As a result of token burning, the actual token supply can decrease below the `maxSupply`. Similarly, the user may burn extra tokens compared with the available amount at the time.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (2)
- https://github.com/DeepLinkProtocol/DeepLinkTokenContact/contracts/DeepLink.sol at commit 98c2f2838478bfdb8dac29b5bda034c73b32dec7
- https://github.com/DeepLinkProtocol/DeepLinkTokenContact/contracts/MuiltiSignTimeLock.sol at commit 98c2f2838478bfdb8dac29b5bda034c73b32dec7
Part of DeepLink’s security record
 DeepLink
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us