0x1f557fb2aa33dce484902695ca1374f413875519
As of 21 Nov 2026, Trustblock’s record holds 0x1f557fb2aa33dce484902695ca1374f413875519 on Ethereum as a contract of Vestate. 1 audit report on Trustblock lists this address: CertiK, 17 May 2024. 3 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Ethereum.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| VESTATE (VES) | CertiK | Not recorded (see the report) | Open |
2 High, 1 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `VES` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the addresses of `marketingWallet` and `uniswapV2Pair`, exclude accounts from fees, and set buy or sell fees of up to 10%. 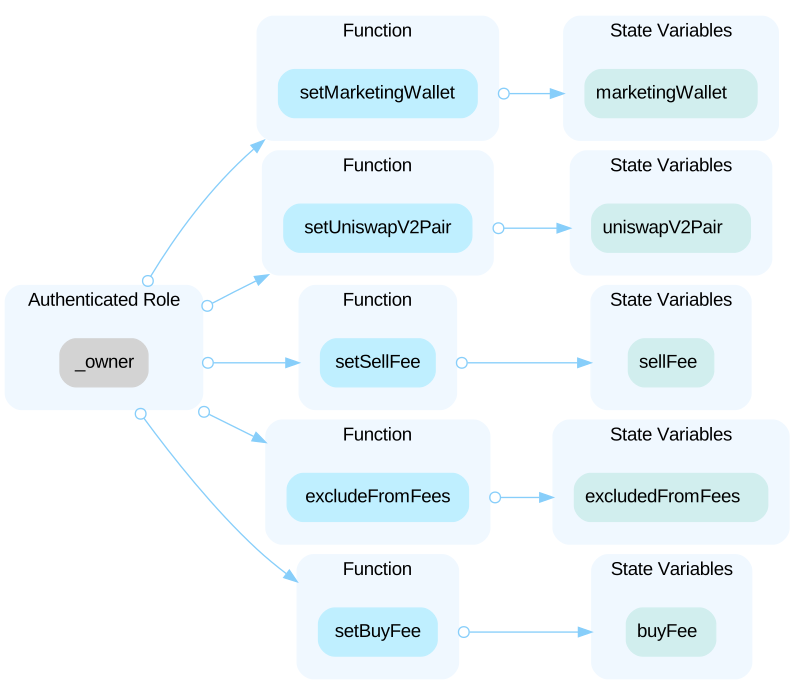
The audit on Trustblock · Open the reportAll of the VES tokens are sent to the contract deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on Trustblock · Open the reportAddresses are not validated before assignment or external calls, potentially allowing the use of zero addresses and leading to unexpected behavior. ```solidity=23 marketingWallet = marketingWallet_; ``` - `marketingWallet_` is not zero-checked before being used. Allowing tokens to be transferred to a zero address will result in the permanent loss of those tokens. --- ```solidity=53 uniswapV2Pair = uniswapV2Pair_; ``` - `uniswapV2Pair_` is not zero-checked before being used. Allow free buying and selling fees.
The audit on Trustblock · Open the reportThe Vestate security record · Every Vestate address · This address on the explorer