0xbee20b9df360b8442534ed8059f3e5baeeb74eaf
As of 21 Nov 2026, Trustblock’s record holds 0xbee20b9df360b8442534ed8059f3e5baeeb74eaf on Ethereum as a contract of Mossland. 1 audit report on Trustblock lists this address: CertiK, 15 Aug 2023. 3 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Ethereum.
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| MossLand Swap - Audit | CertiK | Not recorded (see the report) | Open |
2 High, 1 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `AccessControl` the role `adminRole` has authority over the following functions: - grantRole() - revokeRole() Any compromise to the `adminRole` account may allow the hacker to take advantage of this authority and grant associated role to any account or revoke the role from any account. Note that `DEFAULT_ADMIN_ROLE` is the admin role for all roles. --- In the contract `AccessControl` the role `role` has authority over the following function: - renounceRole() Any compromise to the `role` account may allow the hacker to take advantage of this authority and renounce corresponding privileges to functions within other contracts. --- In the contract `ERC20Migratable` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and mint/burn tokens in the contract and pause/unpause the functions `deposit()` and `withdraw()`. 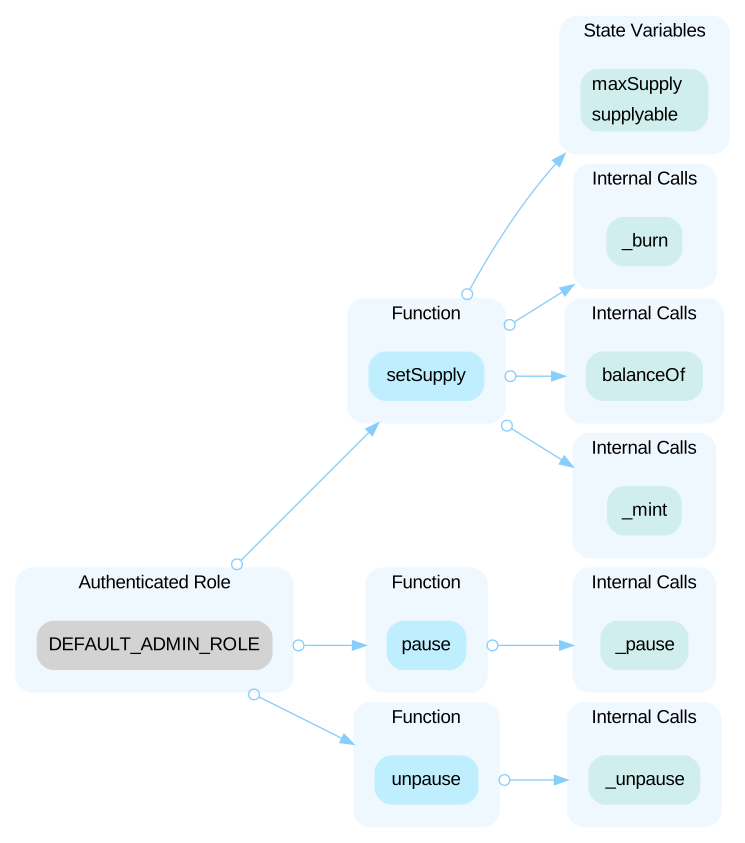 --- In the contract `ERC20Migratable` the role `REGISTRAR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `REGISTRAR_ROLE` account may allow the hacker to take advantage of this authority and alter the withdrawal allowances of users. 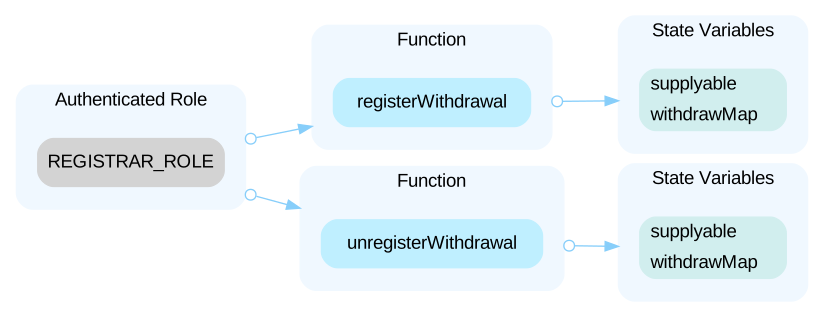
The audit on Trustblock · Open the reportIn the contract, the `DEFAULT_ADMIN_ROLE` has the capability to mint an arbitrary amount of tokens, while the `REGISTRAR_ROLE` permits users to withdraw tokens. If both these roles are compromised, an attacker could get a significant quantity of tokens and sell those tokens to cause the token price to drop.
The audit on Trustblock · Open the reportThe contract has a payable constructor, making it able to receive native tokens. However, it does not have a function to withdraw the funds, which can lead to permanently locked tokens within the contract. ```solidity=670 constructor(string memory name, string memory symbol) payable ERC20(name, symbol) { ```
The audit on Trustblock · Open the reportThe Mossland security record · Every Mossland address · This address on the explorer