
Mossland audit reports
Mossland has 2 public audit reports from CertiK; the latest is CertiK, 15 Aug 2023; no critical findings reported. It also holds 1 deployed contract on 1 chain.
Last updated . It holds audits and findings, contracts and incidents up to Nov 2026. Trustblock does not review code.
Open findings across every firm12
Statuses are the security firms’ own
12 findings are still open or acknowledged in the firms’ reports: 5 high, 7 low (all open).
- High
- 5
- Low
- 7
- High Open
Centralization Related Risks
MossLand Swap - Audit · CertiK · 15 Aug 2023 · Report ↗
- High Open
Minting Centralization Risk
MossLand Swap - Audit · CertiK · 15 Aug 2023 · Report ↗
- High Open
Centralization Related Risks
MossCoin - Audit · CertiK · 30 May 2023 · Report ↗
- High Open
Initial Token Distribution
MossCoin - Audit · CertiK · 30 May 2023 · Report ↗
- High Open
Minting Centralization Risk
MossCoin - Audit · CertiK · 30 May 2023 · Report ↗
- Low Open
Locked Blockchain Native Tokens
MossLand Swap - Audit · CertiK · 15 Aug 2023 · Report ↗
- Low Open
Arbitrary external calls
MossCoin - Audit · CertiK · 30 May 2023 · Report ↗
- Low Open
Confusing implementation in function `calculateMi
MossCoin - Audit · CertiK · 30 May 2023 · Report ↗
- Low Open
Missing Emit Events
MossCoin - Audit · CertiK · 30 May 2023 · Report ↗
- Low Open
Missing Error Messages
MossCoin - Audit · CertiK · 30 May 2023 · Report ↗
Audits2
Newest first
| Report | Security firm | Date | Scope | Critical findings | Findings | Source |
|---|---|---|---|---|---|---|
| MossLand Swap - Audit | Security firm: CertiK | Date: | Scope: 1 address on Ethereum | None open | Findings: 2 high · 1 low 3 open | skynet.certik.com ↗ |
| MossCoin - Audit | Security firm: CertiK | Date: | Scope: Files listed | None open | Findings: 3 high · 6 low 9 open | skynet.certik.com ↗ |
Findings12
Statuses are the security firm’s own, from each report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 5 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 7 | 0 | 0 |
HighCentralization Related RisksMossLand Swap - Audit · CertiK · 15 Aug 2023Open
In the contract `AccessControl` the role `adminRole` has authority over the following functions: - grantRole() - revokeRole() Any compromise to the `adminRole` account may allow the hacker to take advantage of this authority and grant associated role to any account or revoke the role from any account. Note that `DEFAULT_ADMIN_ROLE` is the admin role for all roles. --- In the contract `AccessControl` the role `role` has authority over the following function: - renounceRole() Any compromise to the `role` account may allow the hacker to take advantage of this authority and renounce corresponding privileges to functions within other contracts. --- In the contract `ERC20Migratable` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and mint/burn tokens in the contract and pause/unpause the functions `deposit()` and `withdraw()`. 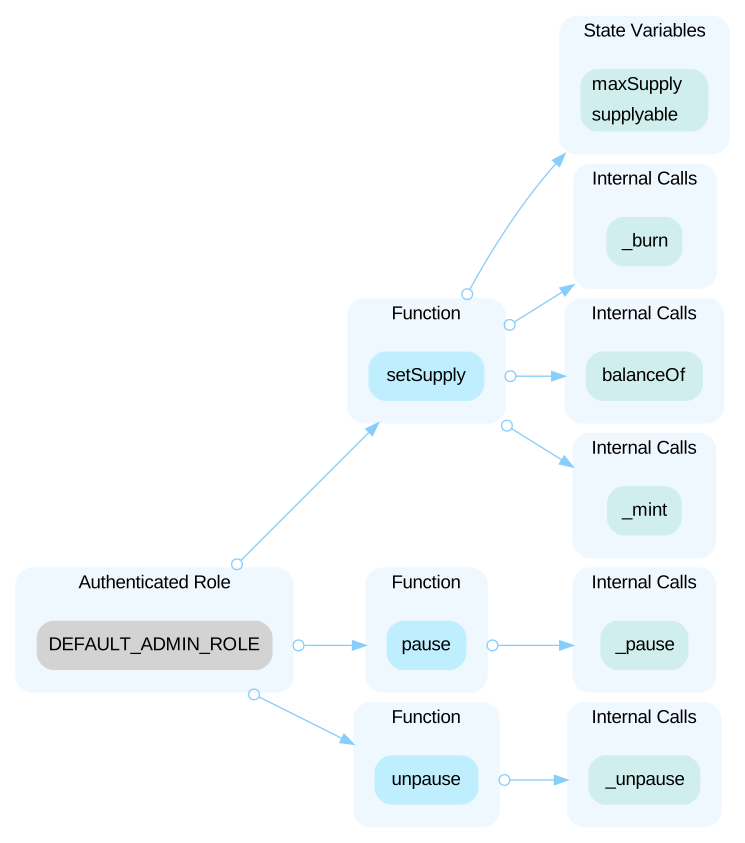 --- In the contract `ERC20Migratable` the role `REGISTRAR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `REGISTRAR_ROLE` account may allow the hacker to take advantage of this authority and alter the withdrawal allowances of users. 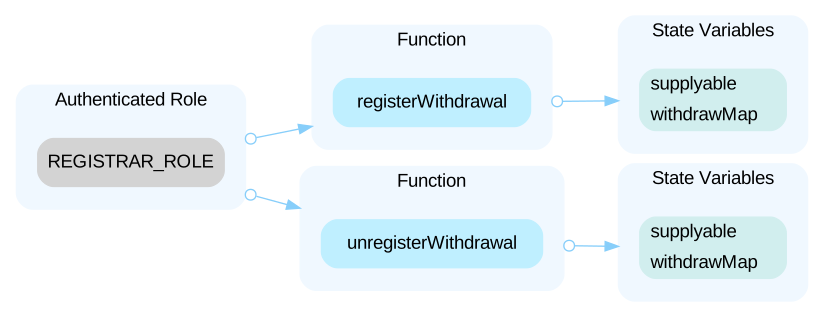
Open the reportHighMinting Centralization RiskMossLand Swap - Audit · CertiK · 15 Aug 2023Open
In the contract, the `DEFAULT_ADMIN_ROLE` has the capability to mint an arbitrary amount of tokens, while the `REGISTRAR_ROLE` permits users to withdraw tokens. If both these roles are compromised, an attacker could get a significant quantity of tokens and sell those tokens to cause the token price to drop.
Open the reportHighCentralization Related RisksMossCoin - Audit · CertiK · 30 May 2023Open
In the contract `MainToken` the role `_owner` has authority over the functions shown in the diagram below. 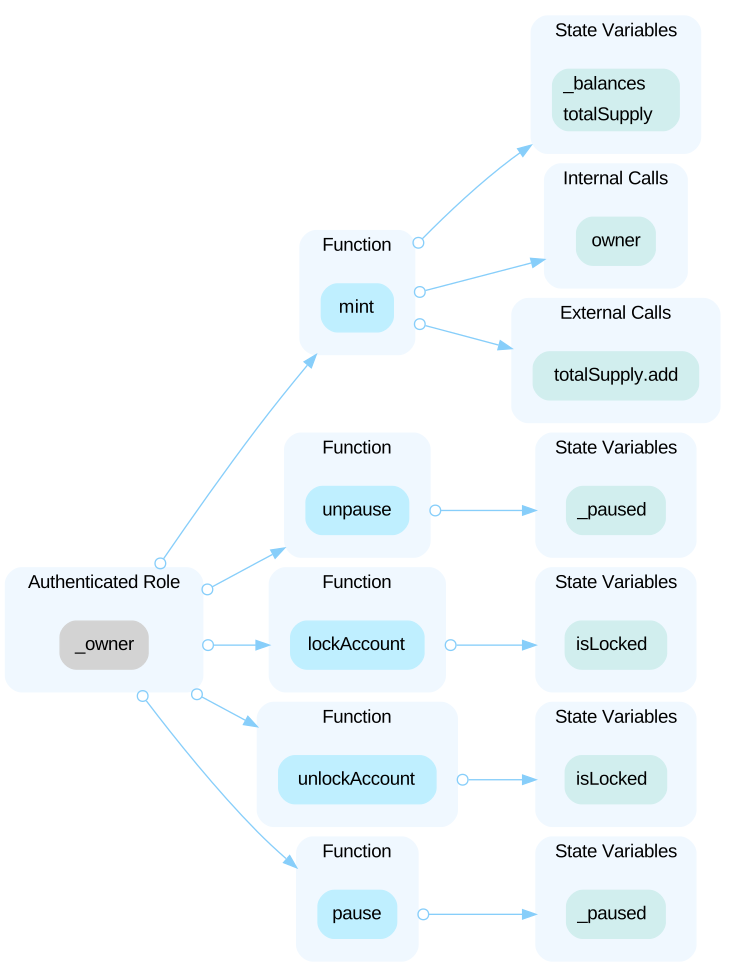 Any compromise to the private key of the `owner` may allow hackers to take advantage of this authority and allow/prevent external user access to the sensitive functionalities controlled by the whenNotPaused modifier. - function `lockAccount()`, to lock any account. Once locked the account cannot access all the functions in the contract. - function `unlockAccount()`, to unlock any account. - function `pause()`, to pause the contract by controlling the `whenNotPaused` status and die or lose the private key. All the users' funds can get stuck in the contract. - function `unpause()`, to unpause the contract. In the contract `LinearMintableToken` the role `_owner` has authority over the functions shown in the diagram below. 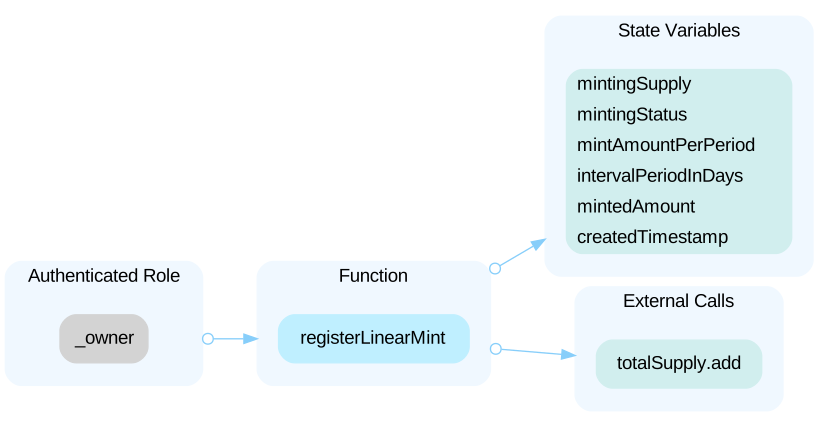 Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the sensitive state variables in the `linearMint()`. In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 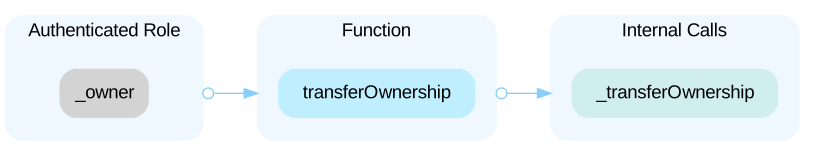 Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer control of the contract to a `newOwner`.
Open the reportHighInitial Token DistributionMossCoin - Audit · CertiK · 30 May 2023Open
All MOC tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute MOC tokens without the consensus of the community.
Open the reportHighMinting Centralization RiskMossCoin - Audit · CertiK · 30 May 2023Open
In the contract `MainToken`, the role `owner` has the authority to mint tokens to the `owner` given the `totalSupply` does not exceed the `maxSupply`. Any compromise to the `owner` account may allow a hacker to take advantage of this authority and mint a huge amount of tokens for themselves. The hacker could sell those tokens and cause the token price to drop. In the contracts `LinearMintableToken`, tokens are gradually minted into the `_owner` EOA address overtime via the `linearMint()` function. This creates a severe centralization risk and can lead to manipulation the tokenomics of the project.
Open the reportLowLocked Blockchain Native TokensMossLand Swap - Audit · CertiK · 15 Aug 2023Open
The contract has a payable constructor, making it able to receive native tokens. However, it does not have a function to withdraw the funds, which can lead to permanently locked tokens within the contract. ```solidity=670 constructor(string memory name, string memory symbol) payable ERC20(name, symbol) { ```
Open the reportLowArbitrary external callsMossCoin - Audit · CertiK · 30 May 2023Open
The function `approveAndCall` will call unpredictable contracts with arbitrary parameters, which is unsafe.
Open the reportLowConfusing implementation in function `calculateMiMossCoin - Audit · CertiK · 30 May 2023Open
`calculateMintAmount` is used for calculating the mint amount of the token. In the function, `pastDays` is calculated as follows: `blockTimestamp.sub(createdTimestamp).div(SECONDS_IN_A_DAY);`, where `blockTimestamp` equals `block.timestamp`. block.timestamp is specified in milliseconds, not seconds, which will cause `pastDays` become inaccurate. Since `intervalPeriodInDays` and `mintAmountPerPeriod` is set by the owner, it is difficult to determine the impact of this issue.
Open the reportLowMissing Emit EventsMossCoin - Audit · CertiK · 30 May 2023Open
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
Open the reportLowMissing Error MessagesMossCoin - Audit · CertiK · 30 May 2023Open
The **require** can be used to check for conditions and throw an exception if the condition is not met. It is better to provide a string message containing details about the error that will be passed back to the caller.
Open the reportShow 2 more
LowRedundant StatementsMossCoin - Audit · CertiK · 30 May 2023Open
According to the logic in the function `calculateMintAmount()`, the `mintingAmount` will never be zero. ```solidity=15 if ( mintingAmount == 0 ) return; ``` The below state variable is declared but never used. ```solidity=15 uint256 public intervalCount; ```
Open the reportLowVariables That Could Be Declared as ImmutableMossCoin - Audit · CertiK · 30 May 2023Open
The linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
Open the reportContracts1
| Address | Chain | Source code |
|---|---|---|
| 0xbee20b9df360b8442534ed8059f3e5baeeb74eaf | Chain: Ethereum | Source code: Verified source |
Mossland: questions
Is Mossland audited?
Trustblock holds 2 public audit reports for Mossland, dated 30 May 2023 to 15 Aug 2023. The latest is by CertiK (“MossLand Swap - Audit”).
Who audited Mossland?
CertiK wrote the 2 reports Trustblock holds for Mossland.
Are there open findings in Mossland’s audits?
12 findings are still open or acknowledged in the firms’ reports: 5 high, 7 low (all open). No critical finding is reported. Statuses are the security firms’ own.
Show this on your site
Is this your project? Show this record on your own website. The label states what the record holds, links to this page and updates by itself. It is free and needs no sign-in.
Content
Automatic: the three strongest facts of this project’s own record (its last audit and two more), highlighted. They update with the record. Picking a fact turns Automatic off.
Style
Format
<head><script src="https://widget.trustblock.run/project-widget.min.js" defer></script></head><body><divdata-tb-project-widgetdata-tb-project-slug="mossland"></div></body>
Paste the code where the label should appear. It uses no API credit and updates by itself.
Something wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us