MossCoin - Audit
CertiK reviewed Mossland (MossCoin - Audit) on 30 May 2023: 9 findings, 0 critical; none marked fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings9
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 6 | 0 | 0 |
HighCentralization Related RisksOpen
In the contract `MainToken` the role `_owner` has authority over the functions shown in the diagram below. 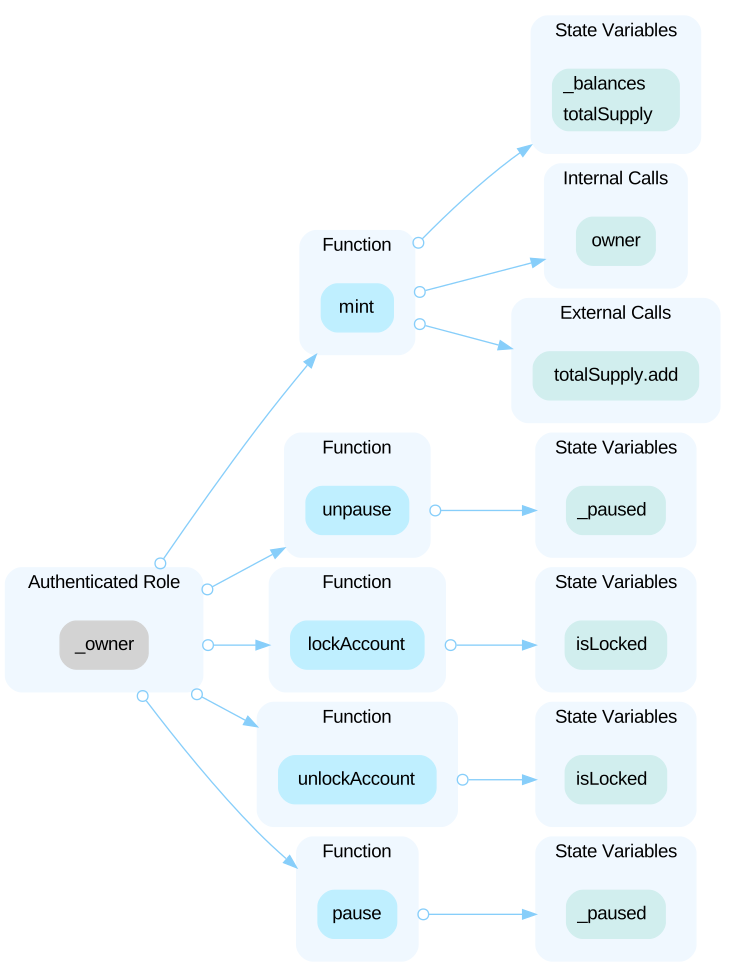 Any compromise to the private key of the `owner` may allow hackers to take advantage of this authority and allow/prevent external user access to the sensitive functionalities controlled by the whenNotPaused modifier. - function `lockAccount()`, to lock any account. Once locked the account cannot access all the functions in the contract. - function `unlockAccount()`, to unlock any account. - function `pause()`, to pause the contract by controlling the `whenNotPaused` status and die or lose the private key. All the users' funds can get stuck in the contract. - function `unpause()`, to unpause the contract. In the contract `LinearMintableToken` the role `_owner` has authority over the functions shown in the diagram below. 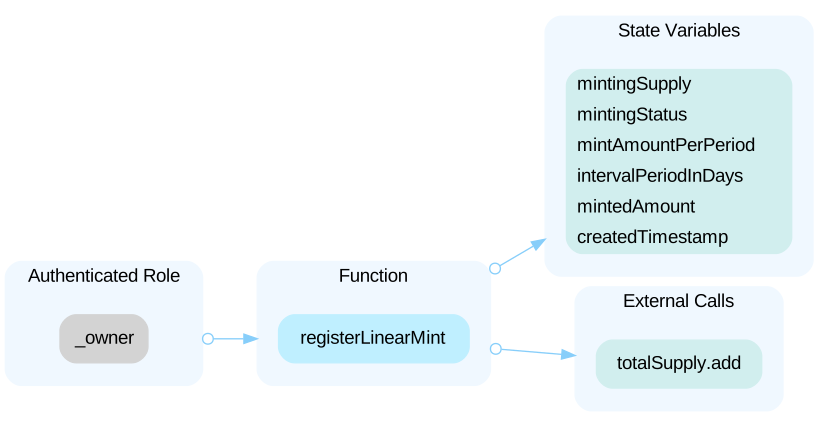 Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and modify the sensitive state variables in the `linearMint()`. In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 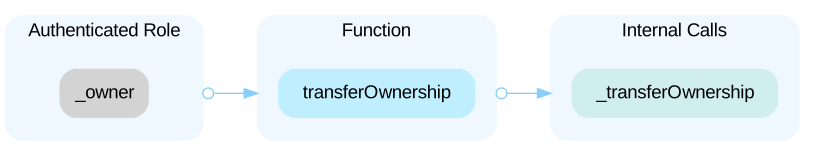 Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer control of the contract to a `newOwner`.
HighInitial Token DistributionOpen
All MOC tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute MOC tokens without the consensus of the community.
HighMinting Centralization RiskOpen
In the contract `MainToken`, the role `owner` has the authority to mint tokens to the `owner` given the `totalSupply` does not exceed the `maxSupply`. Any compromise to the `owner` account may allow a hacker to take advantage of this authority and mint a huge amount of tokens for themselves. The hacker could sell those tokens and cause the token price to drop. In the contracts `LinearMintableToken`, tokens are gradually minted into the `_owner` EOA address overtime via the `linearMint()` function. This creates a severe centralization risk and can lead to manipulation the tokenomics of the project.
LowArbitrary external callsOpen
The function `approveAndCall` will call unpredictable contracts with arbitrary parameters, which is unsafe.
LowConfusing implementation in function `calculateMiOpen
`calculateMintAmount` is used for calculating the mint amount of the token. In the function, `pastDays` is calculated as follows: `blockTimestamp.sub(createdTimestamp).div(SECONDS_IN_A_DAY);`, where `blockTimestamp` equals `block.timestamp`. block.timestamp is specified in milliseconds, not seconds, which will cause `pastDays` become inaccurate. Since `intervalPeriodInDays` and `mintAmountPerPeriod` is set by the owner, it is difficult to determine the impact of this issue.
LowMissing Emit EventsOpen
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
LowMissing Error MessagesOpen
The **require** can be used to check for conditions and throw an exception if the condition is not met. It is better to provide a string message containing details about the error that will be passed back to the caller.
LowRedundant StatementsOpen
According to the logic in the function `calculateMintAmount()`, the `mintingAmount` will never be zero. ```solidity=15 if ( mintingAmount == 0 ) return; ``` The below state variable is declared but never used. ```solidity=15 uint256 public intervalCount; ```
LowVariables That Could Be Declared as ImmutableOpen
The linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (6)
- SafeMath.sol
- Ownable.sol
- LinearMintableToken.sol
- ERC20Token.sol
- MainToken.sol
- TokenRecipient.sol
Part of Mossland’s security record
 Mossland
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us