0x1d5fd72c02cb52cec1395e5639e0c41b2174db07
As of 21 Nov 2026, Trustblock’s record holds 0x1d5fd72c02cb52cec1395e5639e0c41b2174db07 on Polygon (POS) as a contract of MetaTrace. 1 audit report on Trustblock lists this address: CertiK, 8 Nov 2023. 8 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Polygon (POS).
3 High, 5 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `MetaTraceGovernanceToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and: - pause/unpause the contract at will. - upgrade the contract code to a potentially malicious one. Note that the function `renounceOwnership()` always reverts so the ownership is prevented from being renounced. 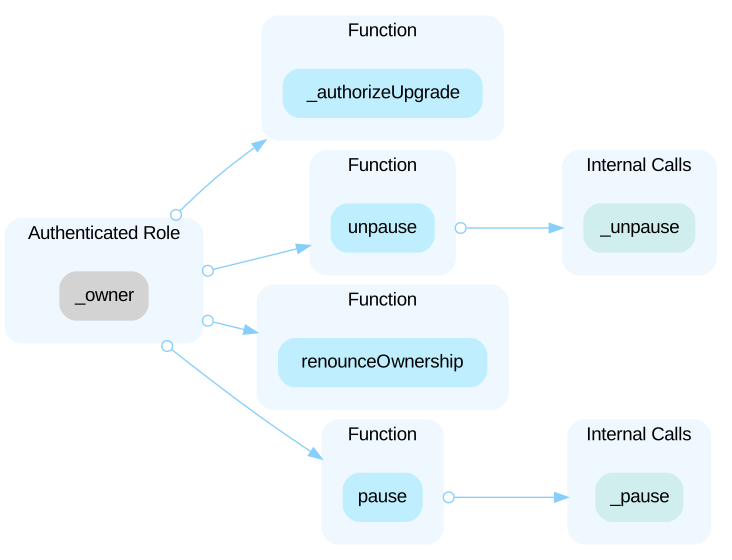 In the contract `OwnableUpgradeable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer the ownership to one of its EoA. 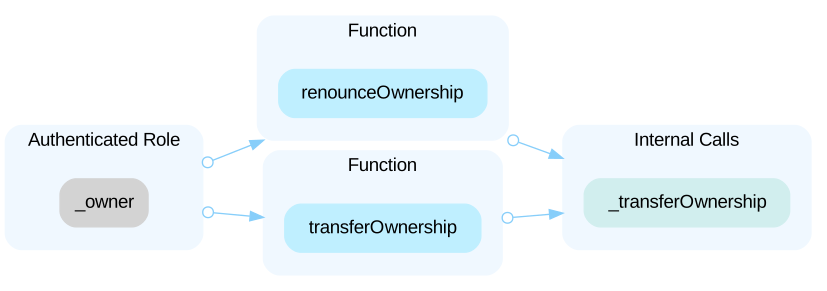
The audit on Trustblock · Open the reportIn the contract `MetaTraceGovernanceToken.sol`, the role `admin` has the authority to update the implementation contract behind the contract. Any compromise to the `admin` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
The audit on Trustblock · Open the reportAll of the `TRC` tokens are sent to the contract deployer or one or several externally-owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on Trustblock · Open the reportIt's recommended to check if `msg.sender == to` in the function `transfer()` since transferring to self makes no sense.
The audit on Trustblock · Open the reportIt is a good practice to NOT include OpenZeppelin library code directly in source code, but import the most recent and stable version of the library to be updated with the latest changes and security fixes. The contract `ERC1967Proxy` should implement the contract `ERC1967Proxy` in OpenZeppelin library. See https://github.com/OpenZeppelin/openzeppelin-contracts/blob/f715365ec40515159ac5f4a4d6f85625ab3b405d/contracts/proxy/ERC1967/ERC1967Proxy.sol. For example, on top of the other changes, the usage of `isContract` has been removed in OpenZeppelin libraries.
The audit on Trustblock · Open the reportThe change of `_owner` by function `transferOwnership()` overrides the previously set `_owner` with the new one without guaranteeing the new `_owner` can actuate transactions on-chain.
The audit on Trustblock · Open the reportLiterals with many digits are difficult to read and review.
The audit on Trustblock · Open the reportSee [this](https://docs.openzeppelin.com/contracts/4.x/upgradeable#storage_gaps) link for a description of this storage variable. While some contracts may not currently be sub-classed, adding the variable now protects against forgetting to add it in the future.
The audit on Trustblock · Open the reportThe MetaTrace security record · Every MetaTrace address · This address on the explorer