MetaTrace
CertiK reviewed MetaTrace on 8 Nov 2023: 10 findings, 0 critical; 2 marked fixed, 5 acknowledged, 3 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings10
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 5 | 2 |
HighCentralization Risks in MetaTraceGovernanceToken.Open
In the contract `MetaTraceGovernanceToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and: - pause/unpause the contract at will. - upgrade the contract code to a potentially malicious one. Note that the function `renounceOwnership()` always reverts so the ownership is prevented from being renounced. 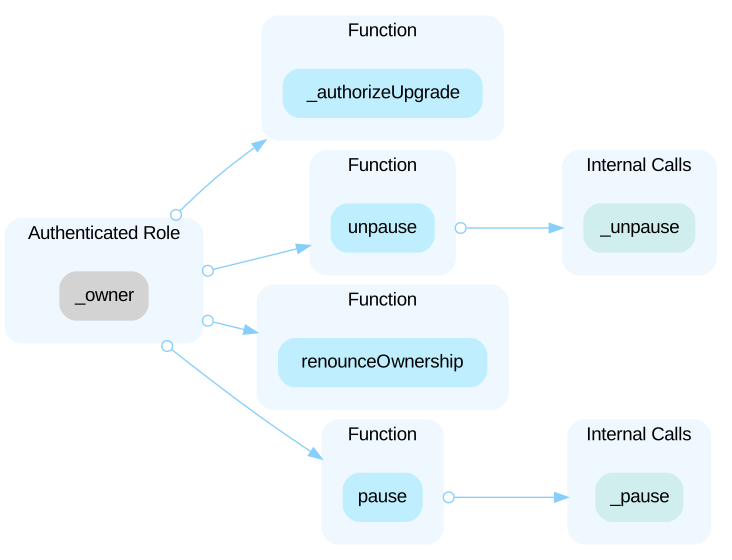 In the contract `OwnableUpgradeable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer the ownership to one of its EoA. 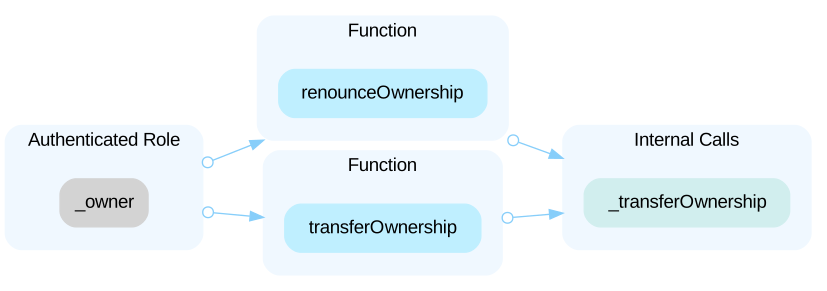
HighCentralized Control of Contract UpgradeOpen
In the contract `MetaTraceGovernanceToken.sol`, the role `admin` has the authority to update the implementation contract behind the contract. Any compromise to the `admin` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
HighInitial Token DistributionOpen
All of the `TRC` tokens are sent to the contract deployer or one or several externally-owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Contracts in scope2
| Address | Chain | Source code |
|---|---|---|
| 0x1d5fd72c02cb52cec1395e5639e0c41b2174db07 | Chain: Polygon (POS) | Source code: Verified source |
| 0x40d9fc77027a281d85de1fa660c887e645ae26c3 | Chain: Polygon (POS) | Source code: Verified source |
Part of MetaTrace’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us