0x6d295da283c4c0658eafe608e4145e8a86777b88
As of 21 Nov 2026, Trustblock’s record holds 0x6d295da283c4c0658eafe608e4145e8a86777b88 on Polygon (POS) as a contract of SolarX. 1 audit report on Trustblock lists this address: CertiK, 18 Aug 2023. 3 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Polygon (POS).
| Audit | Security firm | Date | Commit named in the report | Report |
|---|---|---|---|---|
| SolarX - Audit | CertiK | Not recorded (see the report) | Open |
3 High. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `AccessControl` the role `adminRole` has authority over the following functions: - grantRole() - revokeRole() Any compromise to the `adminRole` account may allow the hacker to take advantage of this authority and grant associated role to any account or revoke the role from any account. Note that `DEFAULT_ADMIN_ROLE` is the admin role for all roles. ----------- In the contract `AccessControl` the role `role` has authority over the following function: - renounceRole() Any compromise to the `role` account may allow the hacker to take advantage of this authority and renounce corresponding privileges to functions within other contracts. --- In the contract `SolarX` the role `MINTER_ROLE` has authority over the function shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and mint tokens. 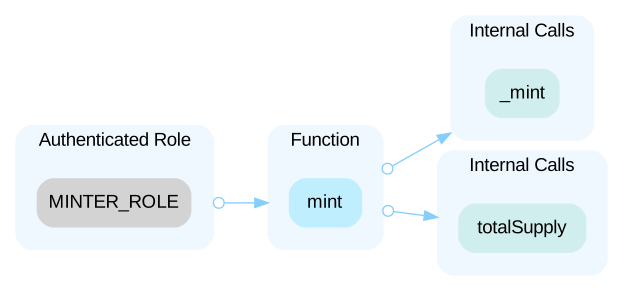 --- In the contract `SolarX` the role `UPDATER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `UPDATER_ROLE` account may allow the hacker to take advantage of this authority and update the variables `miningPoolAddress`, `commissionPercentage`, and `MAX_ALLOWED_BURN_AMOUNT`. 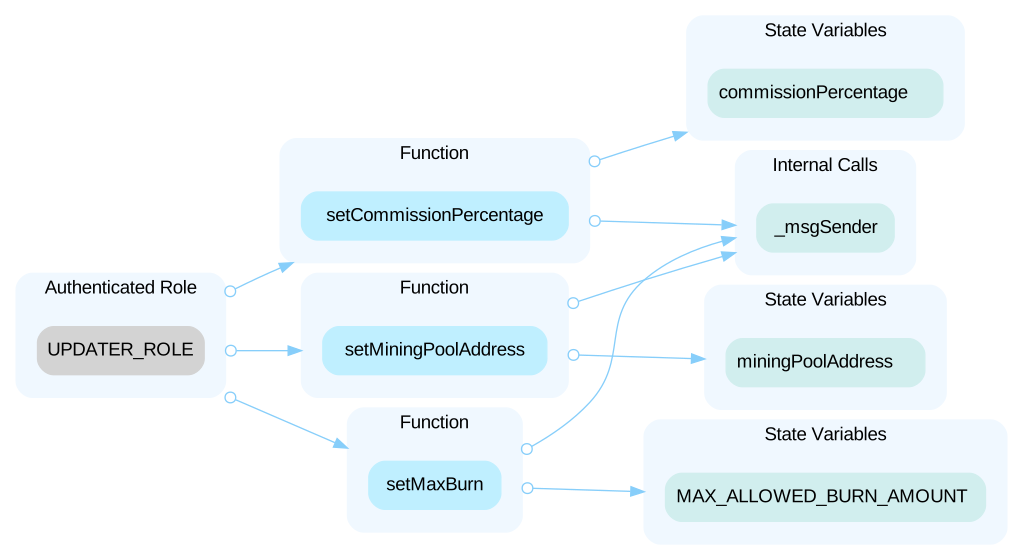 --- In the contract `SolarX` the role `advisors` has authority over the function shown in the diagram below. Any compromise to the `advisors` account may allow the hacker to take advantage of this authority and burn their tokens. 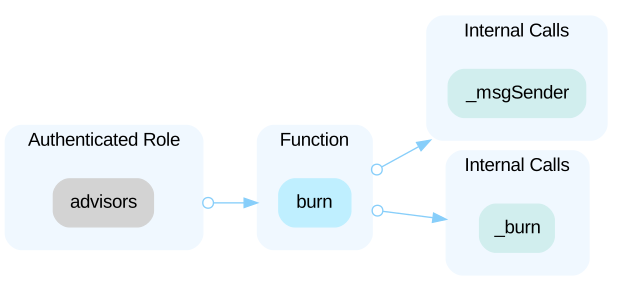
The audit on Trustblock · Open the report`initialSupply` amount of tokens are sent to the contract deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to the address may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on Trustblock · Open the reportThe role `MINTER_ROLE` has the authority to mint an arbitrary amount of tokens to an arbitrary address. Any compromise to the `MINTER_ROLE` account may allow a hacker to take advantage of this authority and mint a huge amount of tokens to themselves.
The audit on Trustblock · Open the reportThe SolarX security record · Every SolarX address · This address on the explorer