0xf3f4e51bf642625c922aad9fe7dc6c22a199990d
As of 21 Nov 2026, Trustblock’s record holds 0xf3f4e51bf642625c922aad9fe7dc6c22a199990d on Polygon (POS) as a contract of CFC Project. 1 audit report on Trustblock lists this address: CertiK, 30 Aug 2023. 5 findings in it are recorded as open or acknowledged.
Each report’s scope as stored on Trustblock names this address on Polygon (POS).
2 High, 3 Low. In the firm’s own words; statuses are the firm’s, from each report.
In the contract `CFCToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and pause/unpause the contract. 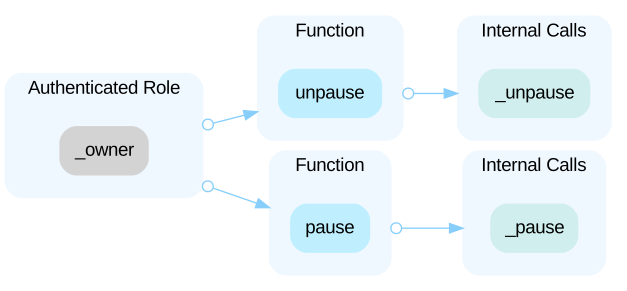 In the contract `MRC20` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and add/remove the frozen addresses and transfer tokens to any address and add a time lock to lock the tokens 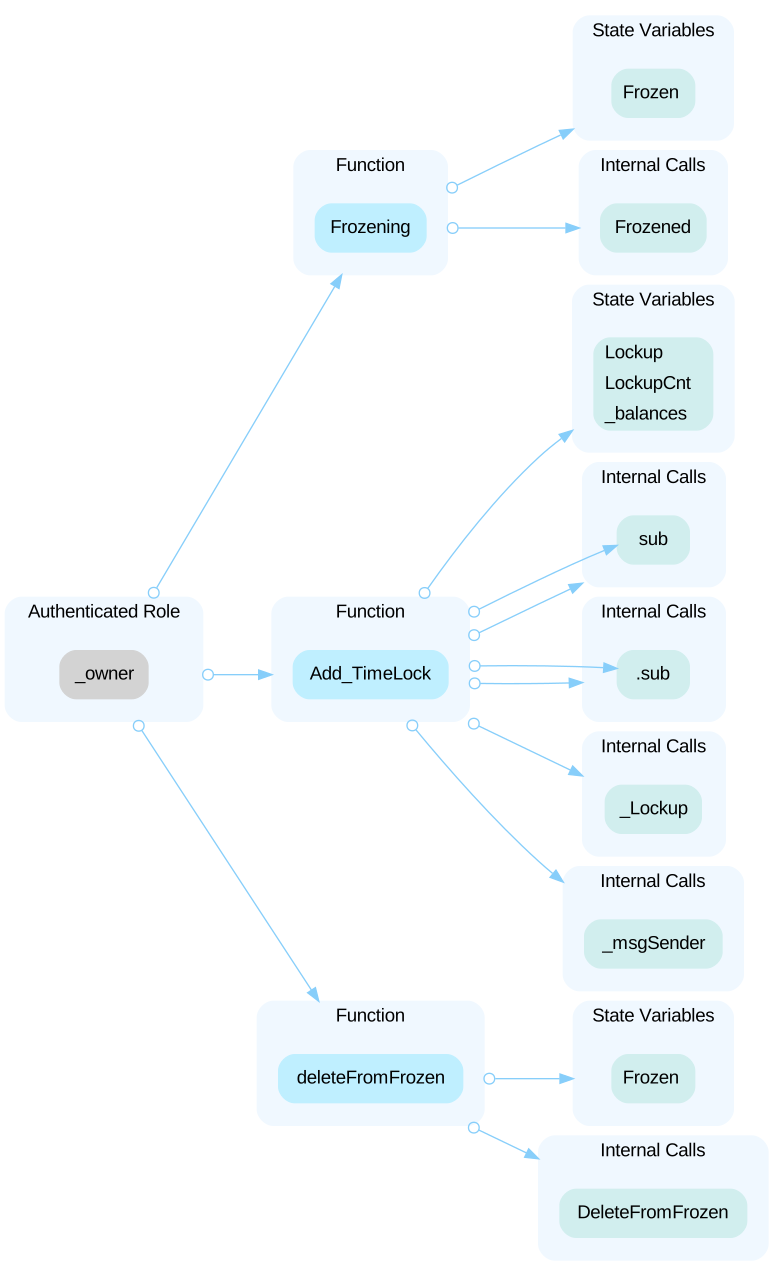 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer ownership to any address. 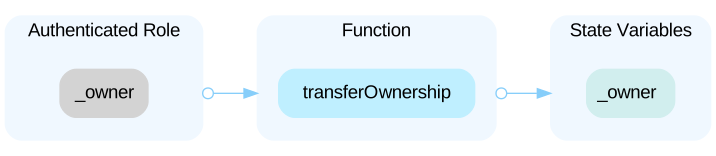
The audit on Trustblock · Open the reportAll of the `CFC` tokens are sent to the contract deployer or one or several externally-owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
The audit on Trustblock · Open the reportThe **require** can be used to check for conditions and throw an exception if the condition is not met. It is better to provide a string message containing details about the error that will be passed back to the caller.
The audit on Trustblock · Open the reportMathematical expression does not check arithmetic overflow. Such unsafe math operation may cause unexpected behavior if unusual parameters are given.
The audit on Trustblock · Open the reportIt is not recommended to use Solidity's `transfer()` and `send()` functions for transferring native tokens, since some contracts may not be able to receive the funds. Those functions forward only a fixed amount of gas (2300 specifically) and the receiving contracts may run out of gas before finishing the transfer. Also, EVM instructions' gas costs may increase in the future. Thus, some contracts that can receive now may stop working in the future due to the gas limitation. ```solidity=677 0x06806458405C55E40D75Bd0fE1732500Cd1C229c.transfer(msg.value); ``` - `CFCToken.constructor` uses `transfer()`.
The audit on Trustblock · Open the reportThe CFC Project security record · Every CFC Project address · This address on the explorer