Magiccraft - MagicMarketplace
CertiK reviewed MagicCraft (Magiccraft - MagicMarketplace) on 28 Sep 2022: 5 findings, 0 critical; all acknowledged, none fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings5
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 3 | 0 |
HighCentralization Risks in MagicMarketplace.solAcknowledged
In the contract `MagicMarketplace` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the protocol. 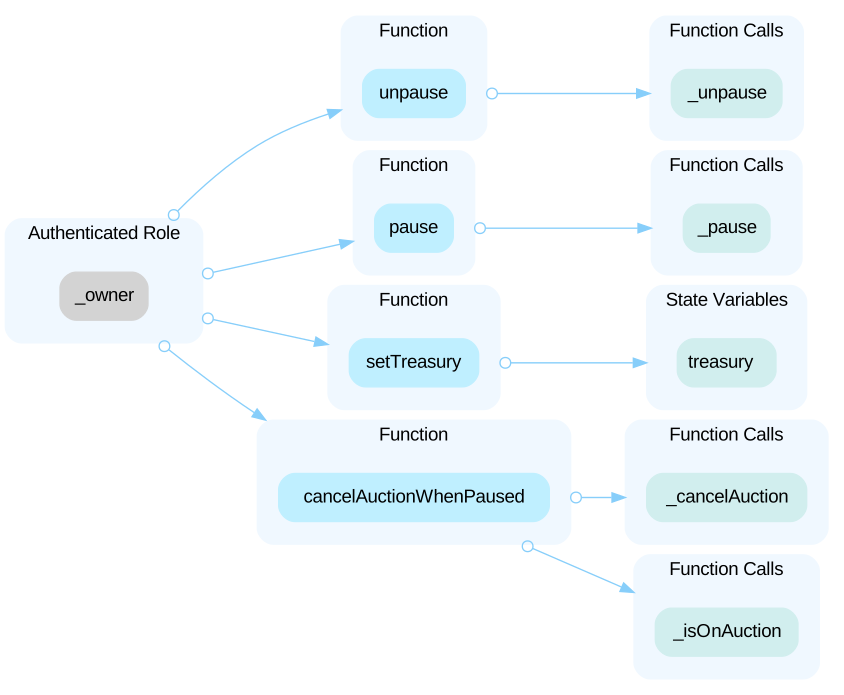
HighCentralized Control of Contract UpgradeAcknowledged
TransparentUpgradeableProxy is an upgradeable contract, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and inject malicious implementation into the implementation contract behind the proxy .
LowIncorrect AssumptionAcknowledged
In function `_escrow()` and `_transfer()`, `ftContract.transferFrom(address(this), _receiver, _tokenId);` is assumed to throw if any error. However, this is an incorrect assumption because the address of `_nftContract` cannot guarantee a NFT address nor the `transferFrom()` cannot guarantee to revert if the transfer fails. This is because that the value of `_nftAddress` is from input argument and there's no check to validate if `_nftAddress.transferFrom()` is correctly implemented.
LowInvalid NFT Implementation CheckAcknowledged
The goal of function `_getNftContract()` is designed to check if the contract in given `_nftAddress` address is a valid ERC721 deployment with correct ERC721 functionality. However current function can not validate the implementation in `_nftAddress`
LowInvalid Ownership ValidationAcknowledged
In function `createAuction()`, `_owns` is implemented to validate ownership of the token in NFT contract in `_nftAddress` address. However due to the value of `_nftAddress` being from input argument, the implementation correctness of `_nftContract.ownerOf` cannot be guaranteed.
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0x76ae87e1c364ead343251ee7dfa2415b4678615d | Chain: BNB Chain | Source code: Verified source |
Part of MagicCraft’s security record
 MagicCraft
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us