TokenFi Token Launcher
CertiK reviewed TokenFi (TokenFi Token Launcher) on 6 Feb 2024: 48 findings, 0 critical; 33 marked fixed, 2 acknowledged, 13 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings48
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 0 |
| Medium | 2 | 0 | 11 |
| Low | 11 | 0 | 22 |
HighCentralized Related RisksAcknowledged
In the contract `AccessControl`, the role `DEFAULT_ADMIN_ROLE` has authority over the functions. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and do the following: - `grantRole()`, grant any role to any account. - `revokeRole()`, revoke any role from any account. In the contract `TokenLauncherERC1155` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and do the following: - `updateTokenLauncherStore()`, set malicious token launcher store contract address. 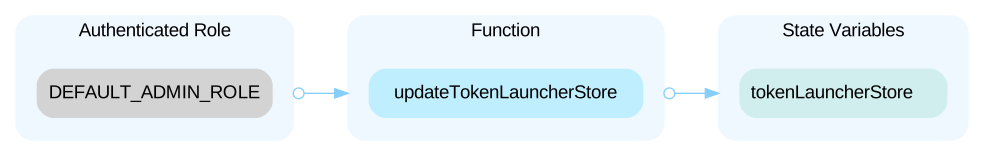 In the contract `TokenLauncherERC20` the token contract `owner` has authority over the functions shown in the diagram below. Any compromise to the token contract `owner` account may allow the hacker to take advantage of this authority and do the following: - `updateBuyBackDetails()`, update to the malicious buy back details. In the contract `TokenLauncherERC20` the `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and do the following: - `updateTokenLauncherStore()`, set malicious token launcher store contract address. - `updateBuyBackHandler()`, update buyback handler contract. In the contract `TokenLauncherERC721` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and do the following: - `updateTokenLauncherStore()`, set malicious token launcher store contract address. 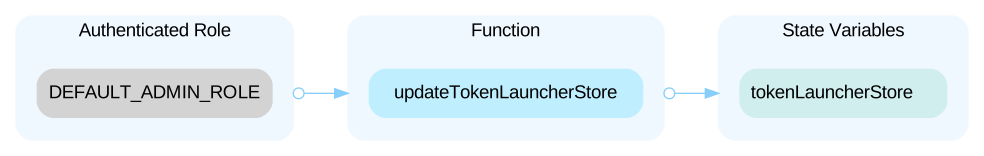 In the contract `TokenLauncherStore` the role `REGISTER_LIQUIDITY_POOL_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `REGISTER_LIQUIDITY_POOL_ROLE` account may allow the hacker to take advantage of this authority and do the following: - `registerLiquidityPool()`, register liquidity pool contract. In the contract `TokenLauncherStore` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and do the following: - `addToken()`, add invalid token contract to store. - `updatePaymentModule()`, update `TokenLauncherPaymentModuleV1` contract. - `updatePricingModule()`, update `TokenLauncherPricingModuleV1` contract. 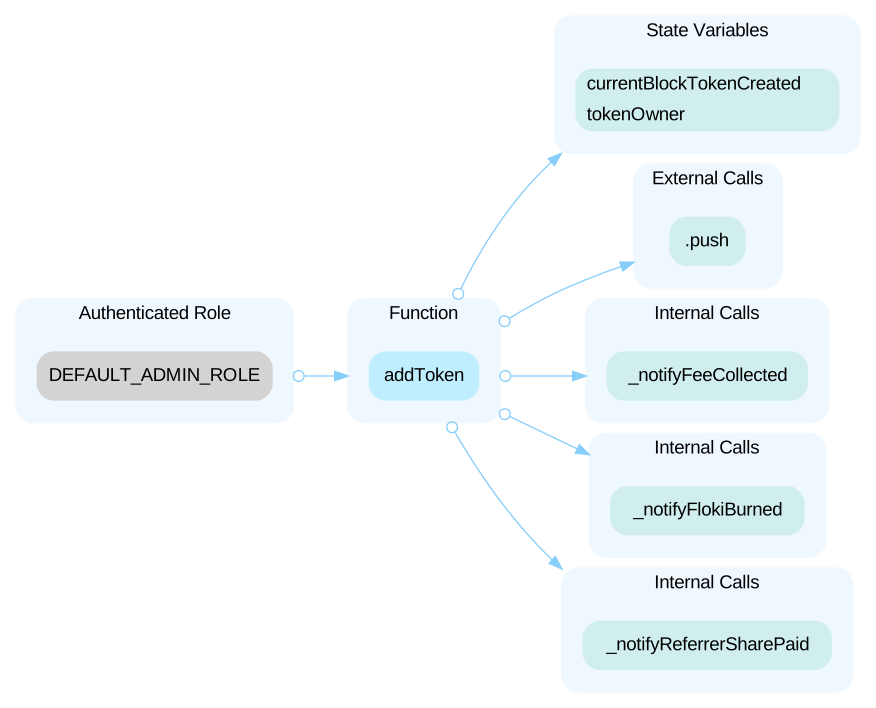 In the contract `TokenLauncherStore` the role `owner` has authority over the functions shown in the diagram below. Any compromise to the `owner` account may allow the hacker to take advantage of this authority and do the following: - `updateTokenOwner()`, maliciously update token owner. 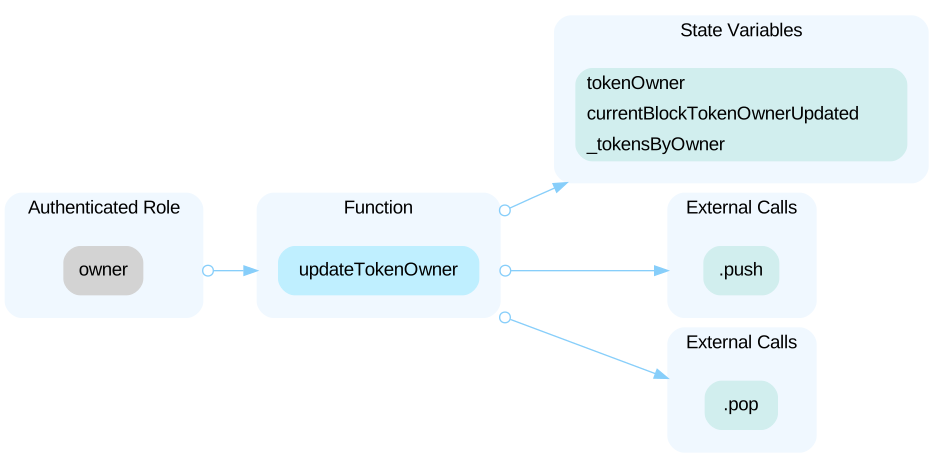 In the contract `BuyBackHandler` the role `BUYBACK_CALLER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `BUYBACK_CALLER_ROLE` account may allow the hacker to take advantage of this authority and do the following: - `buyBack()`, maliciously use assets held by `BuyBackHandler` contract to add liquidity. 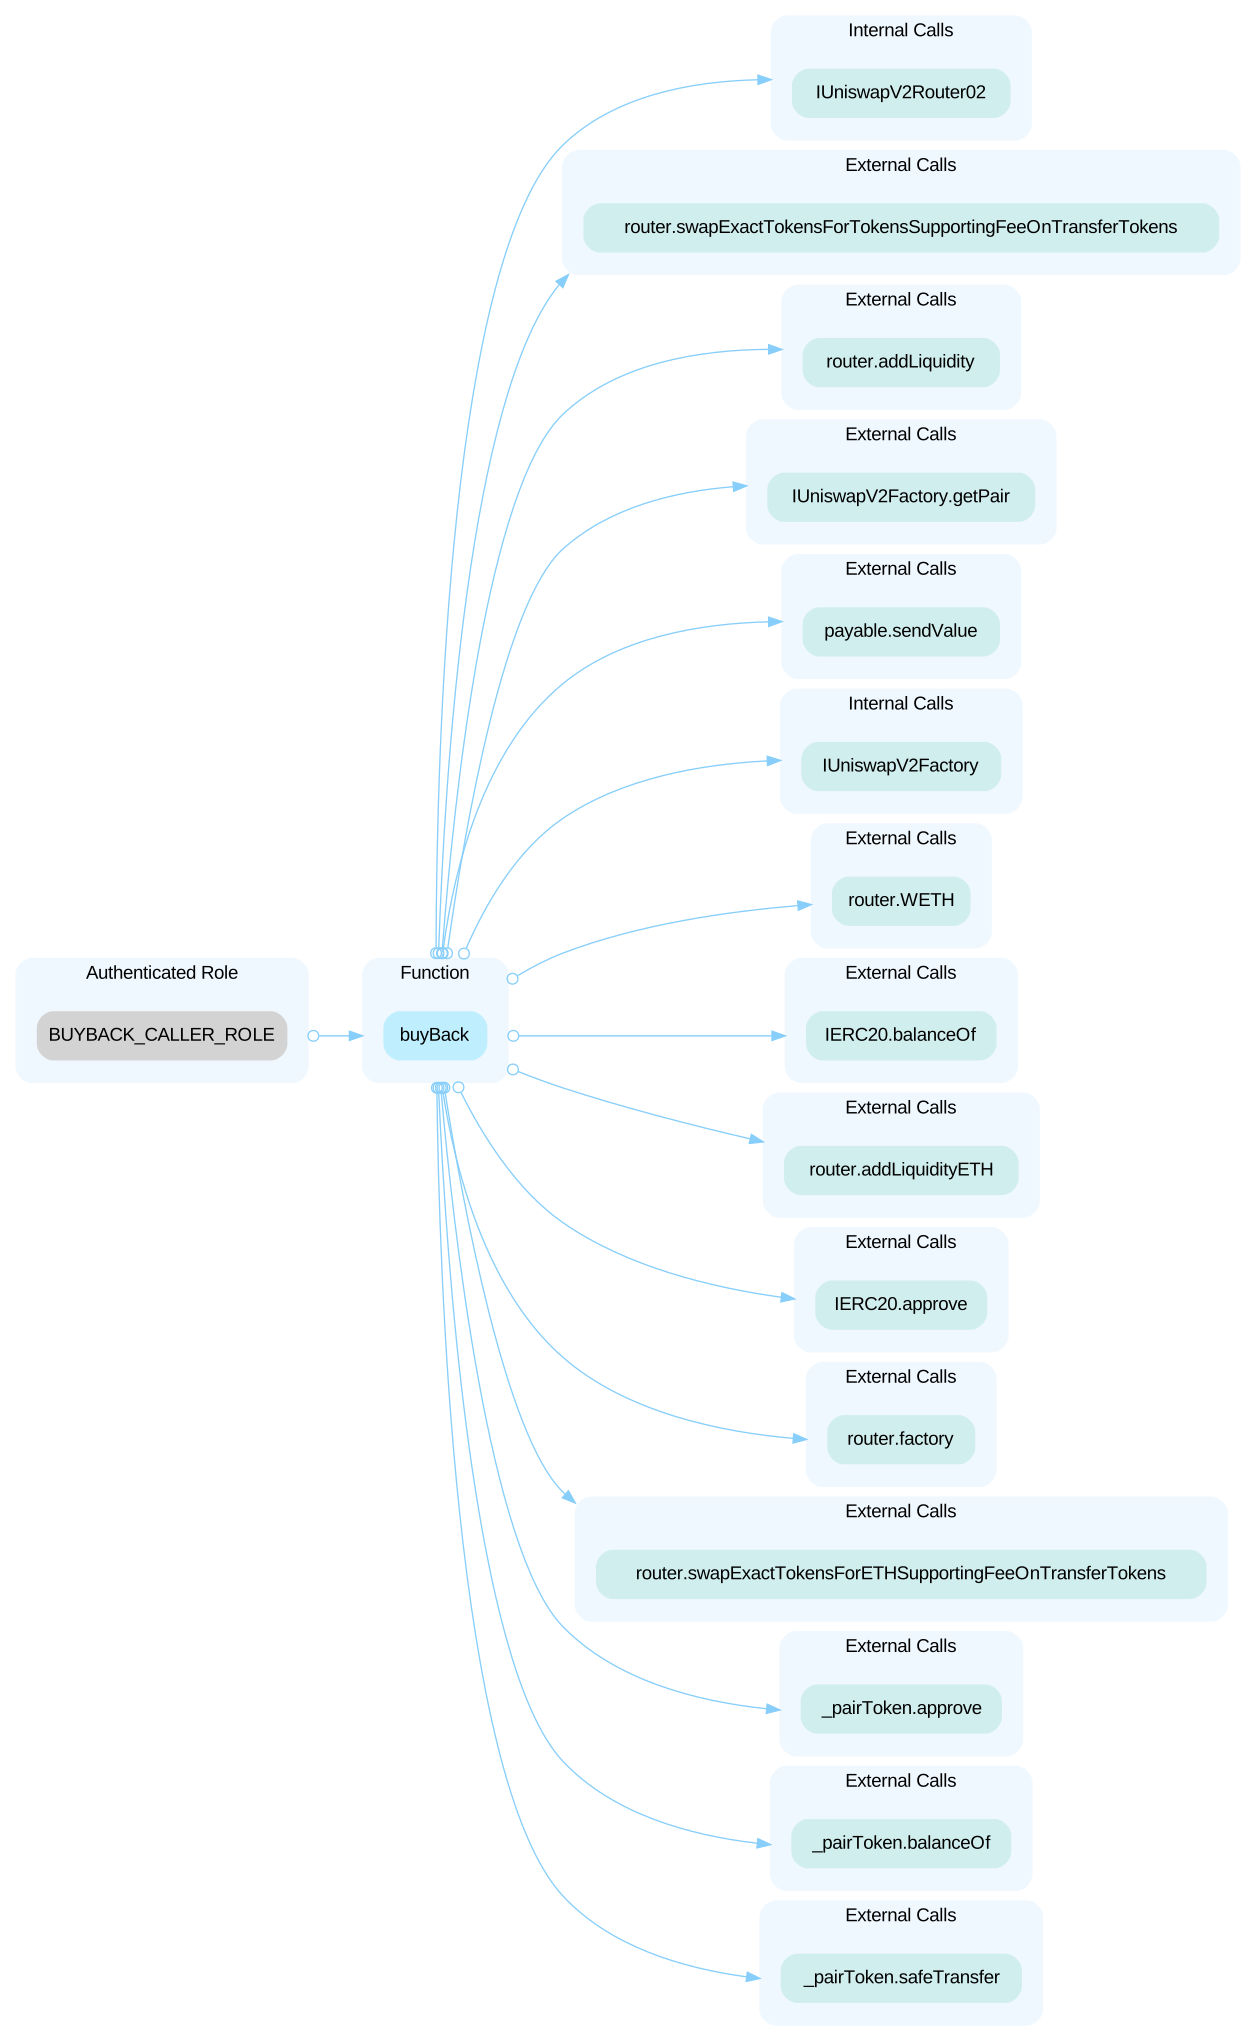 In the contract `BuyBackHandler` the `role admin` has authority over the functions shown in the diagram below. Any compromise to the `role admin` account may allow the hacker to take advantage of this authority and do the following: - `grantRole()`, grant role to specific account. In the contract `BuyBackHandler` the `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and do the following: - `withdraw()`, withdraw assets from `BuyBackHandler` contract. In the contract `TokenLauncherLiquidityPoolFactoryV1` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and do the following: - `setVaultFactory()`, set malicious vault factory contract. - `createV2Liquidity
HighInitial Token DistributionAcknowledged
All of the initial TokenFi ERC20 tokens are sent to the contract deployer or one or several externally-owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (13)
- contracts/token-launcher/templates/TokenFiERC1155.sol
- contracts/token-launcher/TokenLauncherERC1155.sol
- contracts/token-launcher/TokenLauncherERC20.sol
- contracts/token-launcher/payment/TokenLauncherPaymentModuleV1.sol
- contracts/token-launcher/TokenLauncherERC721.sol
- contracts/token-launcher/payment/TokenMintPaymentModuleV1.sol
- contracts/token-launcher/payment/TokenLauncherLiquidityPoolFactoryV1.sol
- contracts/token-launcher/payment/TokenLauncherPricingModuleV1.sol
- contracts/token-launcher/payment/TokenMintPricingModuleV1.sol
- contracts/token-launcher/templates/TokenFiERC721.sol
- contracts/token-launcher/payment/BuyBackHandler.sol
- contracts/token-launcher/TokenLauncherStore.sol
- contracts/token-launcher/templates/TokenFiERC20.sol
Part of TokenFi’s security record
 TokenFi
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us