Wemix Retainer 63 AirDrop
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 63 AirDrop) on 21 Sep 2023: 3 findings, 0 critical; 2 marked fixed, 1 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings3
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 0 | 2 |
HighCentralization Related RisksOpen
In the contract `InitializationExecuteManager` the role `_setter` has authority over the functions shown in the diagram below. Any compromise to the `_setter` account may allow the hacker to take advantage of this authority and set the role manager contract address, set the execute manager contract address and set the blacklist contract address. 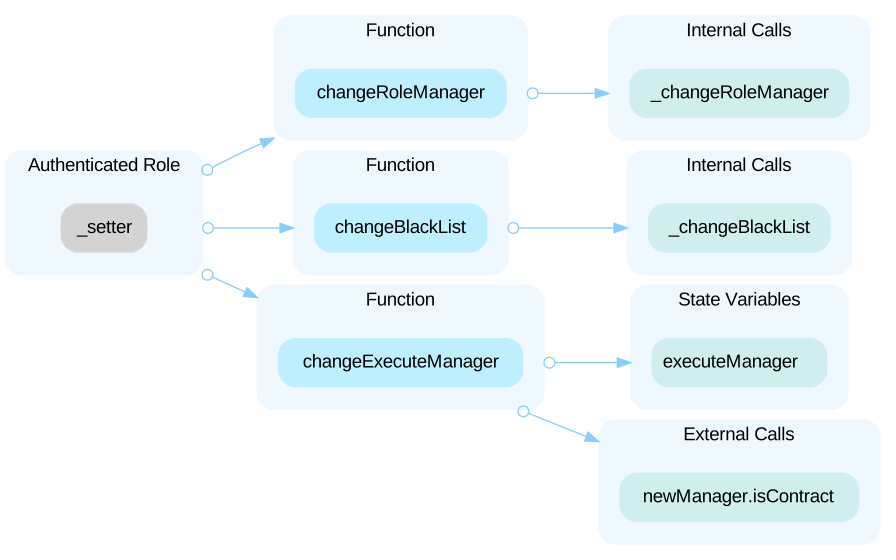 ----- In the contract `AirDrop` the role `_delegator` has authority over the functions shown in the diagram below. Any compromise to the `_delegator` account may allow the hacker to take advantage of this authority and airdrop the ERC20 token. 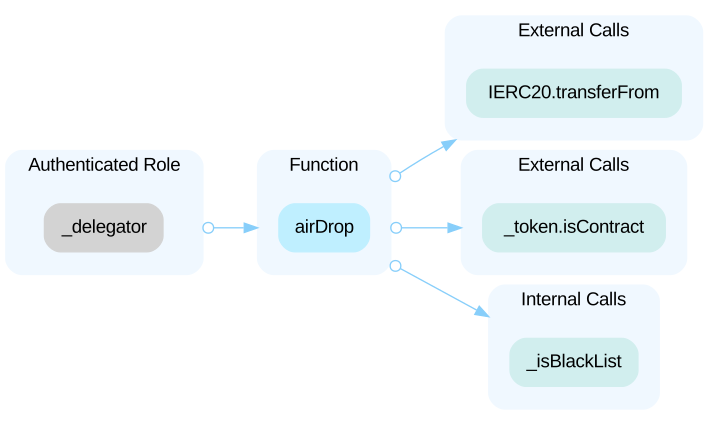 In the contract `AirDrop` the role `_setter` has authority over the functions shown in the diagram below. Any compromise to the `_setter` account may allow the hacker to take advantage of this authority and register the delegator for the treasury, deprive the delegator of the treasury, and change the `ReceiveInfo` list max size. 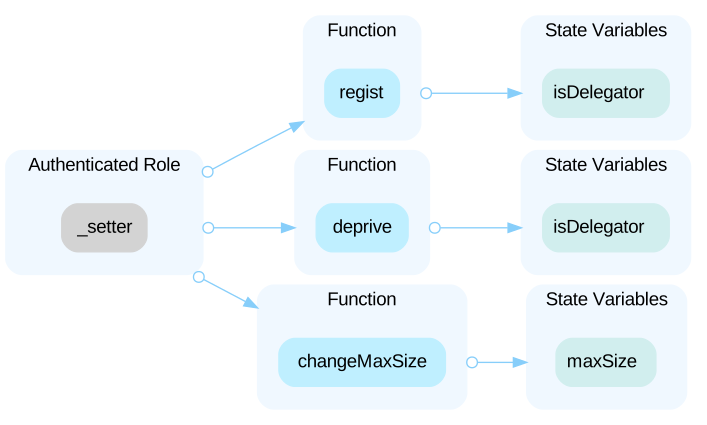 In the contract `AirDrop` the role `treasury` has authority over the functions shown in the diagram below. Any compromise to the `treasury` account may allow the hacker to take advantage of this authority and airdrop the ERC20 token. 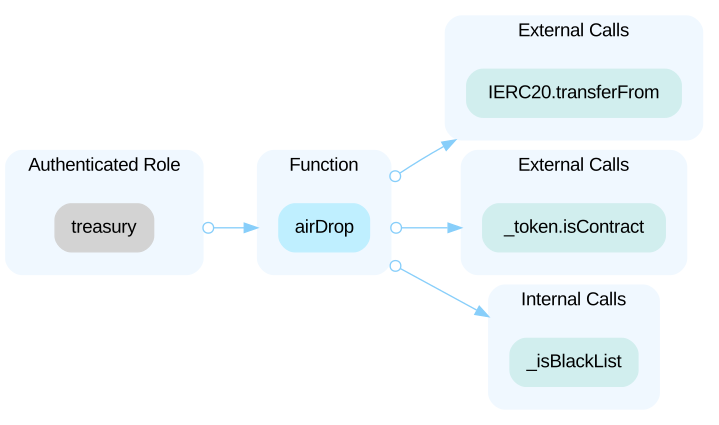
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (2)
- projects/AirDropSimplification/contracts/AirDrop.sol
- projects/AirDropSimplification/contracts/IAirDrop.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us