ALTR
CertiK reviewed ALTR on 2 Mar 2023: 18 findings, 0 critical; 12 marked fixed, 6 acknowledged.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings18
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 2 |
| Medium | 0 | 1 | 2 |
| Low | 0 | 3 | 8 |
HighCentralization RisksAcknowledged
In the contract `AltrAllowList` the role `LIST_MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `LIST_MANAGER_ROLE` account may allow the hacker to take advantage of this authority. 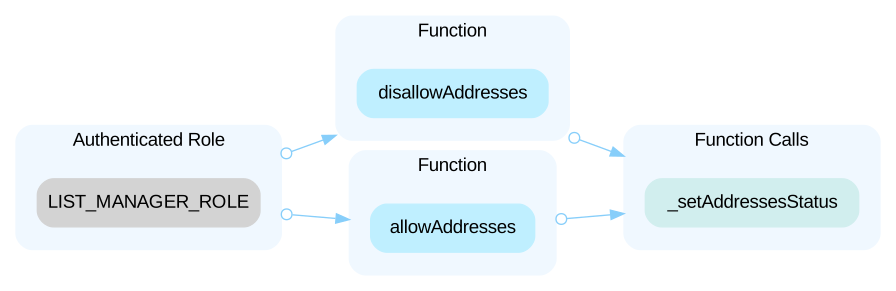 In the contract `AltrFeeManager` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 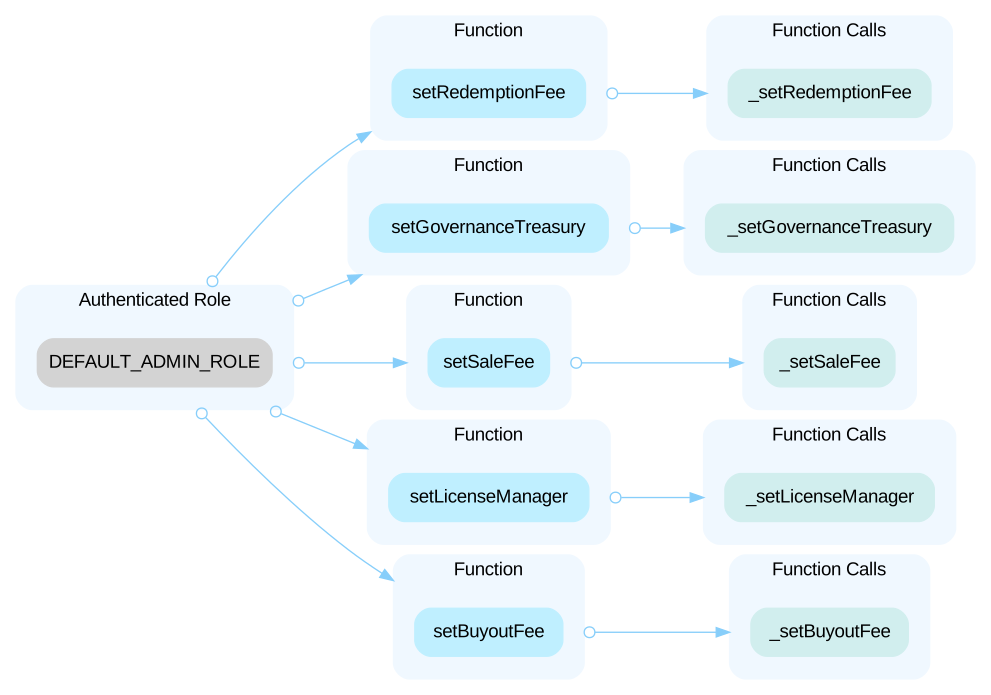 In the contract `AltrFeeManager` the role `TRADE_CHECKER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `TRADE_CHECKER_ROLE` account may allow the hacker to take advantage of this authority. 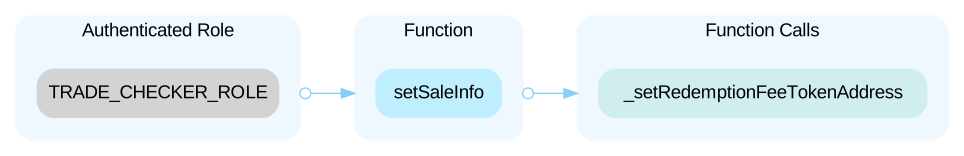 In the contract `AltrFractions` the role `BURN_MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `BURN_MANAGER_ROLE` account may allow the hacker to take advantage of this authority. 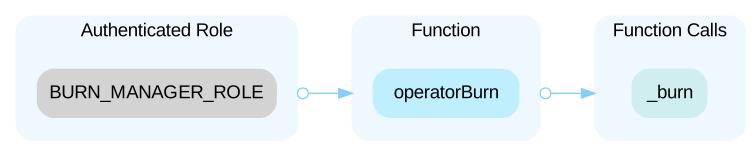 In the contract `AltrFractions` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 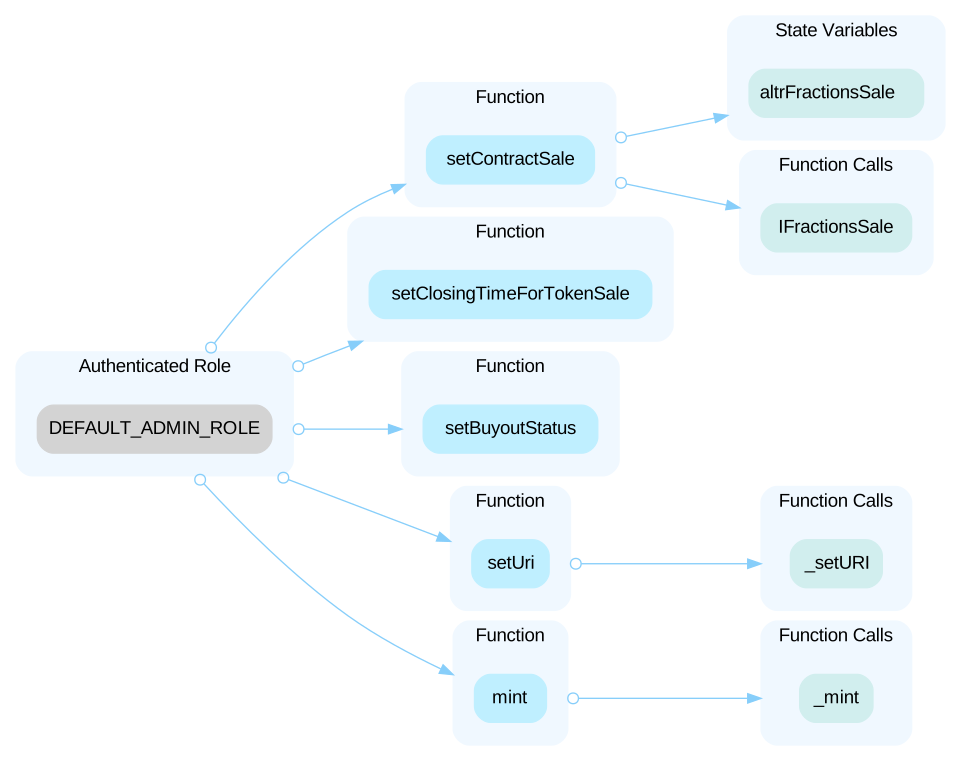 In the contract `AltrFractionsBuyout` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 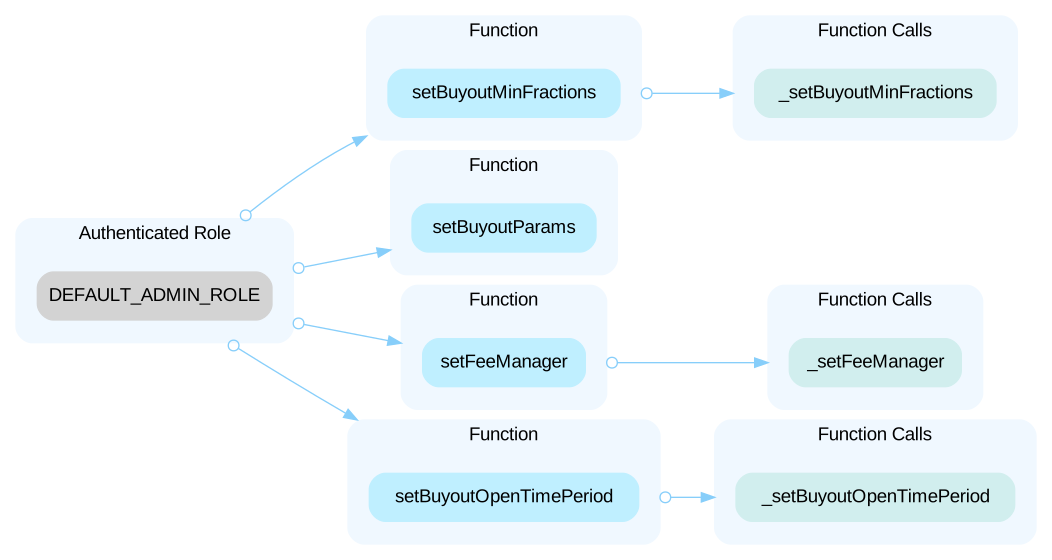 In the contract `AltrFractionsSale` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority. 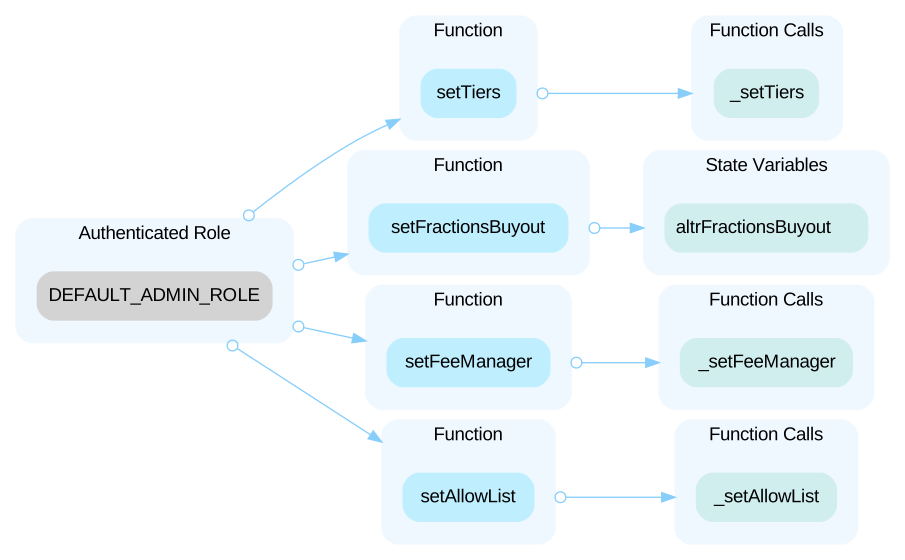 In the contract `AltrFractionsSale` the role `SALE_ISSUER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `SALE_ISSUER_ROLE` account may allow the hacker to take advantage of this authority. 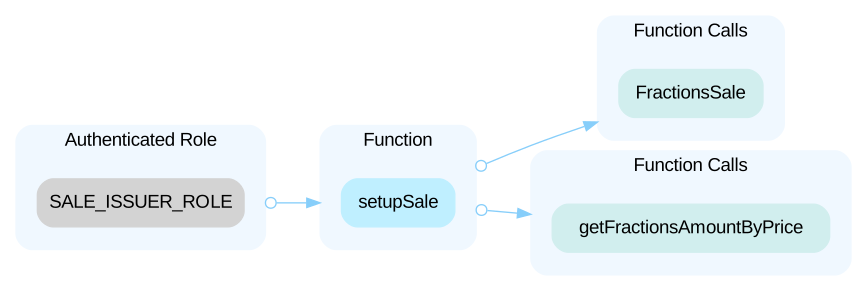 Also, since the `setupSale()` function can only be called by `SALE_ISSUER_ROLE`, and the `fractionsSale.initiator` is set to `msg.sender` in `setupSale()`, functions `withdrawFractionsKept()` and `withdrawFailedSaleNft()` are another two functions that `SALE_ISSUER_ROLE` has authority over. In the contract `AltrFractionsSale` the role `allowList.isAddressAllowed` has authority over the functions shown in the list below. Any compromise to the `allowList.isAddressAllowed` account may allow the hacker to take advantage of this authority. * `buyFractions()` In the contract `AltrLicenseManager` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 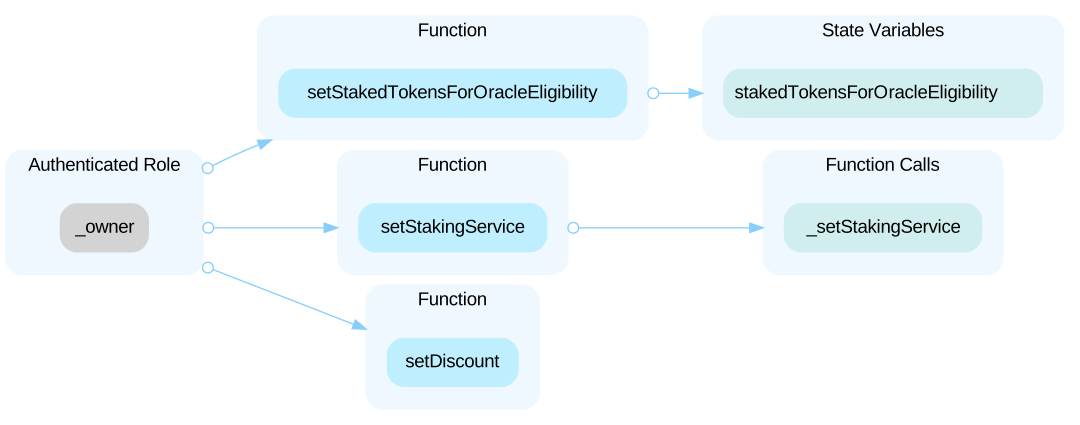 In the contract `AltrNftCollateralRetriever` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 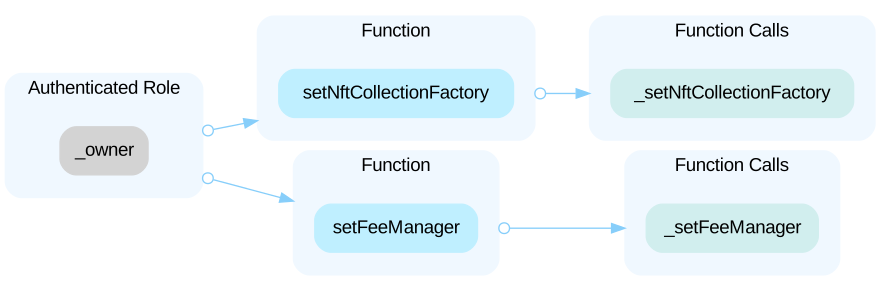 In the contract `AltrNftCollateralRetriever` the role *`MINTER_ROLE` of the input `nftContract`* has authority over the functions shown in the list below. Any compromise to the *`MINTER_ROLE` of the input `nftContract`* account may allow the hacker to take advantage of this authority. * `burnNft()` In the contract `AltrNftCollection` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. A
HighCentralized Control of Contract UpgradeAcknowledged
`AltrFeeManager`, `AltrNftCollateralRetriever` and `AltrNftCollectionFactory` are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
MediumNew Contract Instance Created in Upgradeable ContAcknowledged
When creating a new instance of a contract from upgradeable contract’s code, these creations are handled directly by Solidity and not by OpenZeppelin Upgrades, which means that these contracts will not be upgradeable.
LowIncompatibility with Deflationary TokensAcknowledged
When transferring deflationary ERC20 tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user sends 100 deflationary tokens (with a 10% transaction fee), only 90 tokens actually arrived to the contract. However, a failure to discount such fees may allow the same user to withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. Reference: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f
LowThird Party DependencyAcknowledged
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assume their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc.
LowUnit Test DocumentationAcknowledged
Code documentation can be improved by providing unit tests for the workflows. Unit tests could be used to cover and precisely test the program in its development evolution, to assert properties being held when code evolves. Documenting with unit tests allows precise expression of the expectations about the program. Examples may include expected cases, edge cases and ensure rejections of invalid data.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (13)
- altr-smart-contracts-7caa89ffc641528cf00a3ad542b37605cc1a99c8/contracts/LucidaoGovernanceNftReserve.sol
- altr-smart-contracts-7caa89ffc641528cf00a3ad542b37605cc1a99c8/contracts/AltrFeeManager.sol
- altr-smart-contracts-7caa89ffc641528cf00a3ad542b37605cc1a99c8/contracts/AltrNftCollection.sol
- altr-smart-contracts-7caa89ffc641528cf00a3ad542b37605cc1a99c8/contracts/AltrFractions.sol
- altr-smart-contracts-7caa89ffc641528cf00a3ad542b37605cc1a99c8/contracts/TimedTokenSplitter.sol
- altr-smart-contracts-7caa89ffc641528cf00a3ad542b37605cc1a99c8/contracts/AltrAllowList.sol
- altr-smart-contracts-7caa89ffc641528cf00a3ad542b37605cc1a99c8/contracts/AltrFractionsSale.sol
- altr-smart-contracts-7caa89ffc641528cf00a3ad542b37605cc1a99c8/contracts/AltrNftCollectionFactory.sol
- altr-smart-contracts-7caa89ffc641528cf00a3ad542b37605cc1a99c8/contracts/AltrLicenseManager.sol
- altr-smart-contracts-7caa89ffc641528cf00a3ad542b37605cc1a99c8/contracts/AltrTradeChecker.sol
- altr-smart-contracts-7caa89ffc641528cf00a3ad542b37605cc1a99c8/contracts/AltrFractionsBuyout.sol
- altr-smart-contracts-7caa89ffc641528cf00a3ad542b37605cc1a99c8/contracts/TokenSplitter.sol
- altr-smart-contracts-7caa89ffc641528cf00a3ad542b37605cc1a99c8/contracts/AltrNftCollateralRetriever.sol
Part of ALTR’s security record
 ALTR
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us