Trossard
CertiK reviewed Trossard on 30 Jun 2023: 13 findings, 0 critical; all acknowledged, none fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings13
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 11 | 0 |
HighCentralization Risks in TROSS.solAcknowledged
In the contract `BEP20` the role `_owner` has authority over the functions shown in the diagram below. 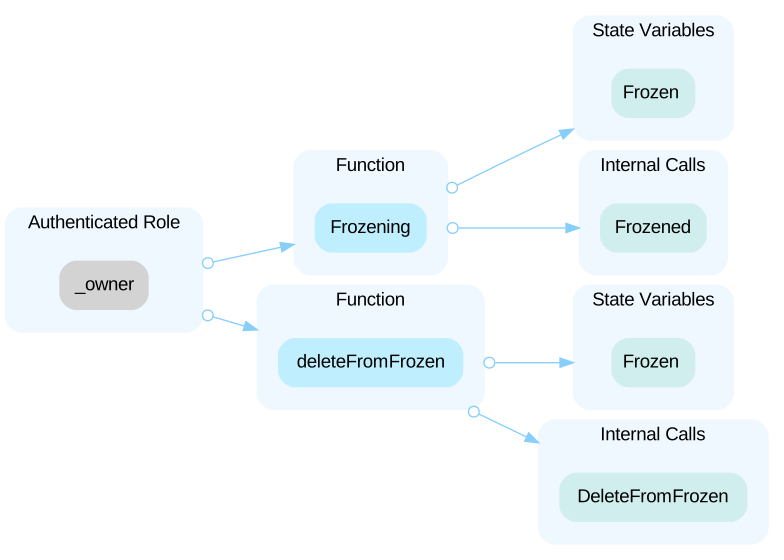 - `Frozening(address _addr)`: This function freezes the account at address `_addr`, preventing it from conducting any transactions. The privileged role that can call this function is the `owner`. - `deleteFromFrozen(address _addr)`: This function unfreezes the account at address `_addr`, allowing it to conduct transactions again. The privileged role that can call this function is the `owner`. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the projects. --- In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 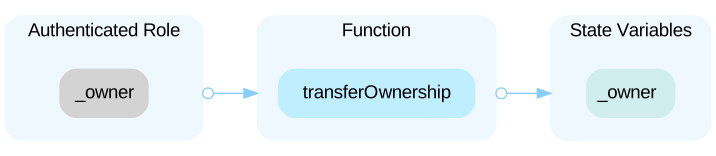 - `transferOwnership(address newOwner)`: This function allows the current owner to transfer the ownership of the contract to a new owner. The privileged role that can call this function is the current `owner`. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the projects.
HighInitial Token DistributionAcknowledged
All of the `TROSS` tokens are sent to the contract deployer or one or several externally-owned account (EOA) addresses. This is a centralization risk because the deployer or the owner(s) of the EOAs can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
LowFunction `transfer` of Contract `BEP20` Fails onAcknowledged
It is expected that invocations of the form `transfer(recipient, amount)` succeed and return `true` if * The address in `recipient` is not the zero address, * `amount` does not exceed the balance of address `msg.sender`, * transferring `amount` to the address `recipient` does not lead to an overflow of the recipient's balance, and * the supplied gas suffices to complete the call. Nevertheless, the `transfer` function of `BEP20` fails in some of those admissible cases.
LowFunction `transfer` of Contract `BEP20` Fails onAcknowledged
It is expected that invocations of the form `transfer(recipient, amount)` where the address in `recipient` equals the address in `msg.sender` (i.e. self-transfers) succeed and return `true` if * The value in `amount` does not exceed the balance of `msg.sender` and * the supplied gas suffices to complete the call. Nevertheless, the `transfer` function of `BEP20` fails in some of those admissible cases.
LowFunction `transfer` of Contract `TROSSToken` FailAcknowledged
It is expected that invocations of the form `transfer(recipient, amount)` succeed and return `true` if * The address in `recipient` is not the zero address, * `amount` does not exceed the balance of address `msg.sender`, * transferring `amount` to the address `recipient` does not lead to an overflow of the recipient's balance, and * the supplied gas suffices to complete the call. Nevertheless, the `transfer` function of `BEP20` fails in some of those admissible cases.
LowFunction `transfer` of Contract `TROSSToken` FailAcknowledged
It is expected that invocations of the form `transfer(recipient, amount)` where the address in `recipient` equals the address in `msg.sender` (i.e. self-transfers) succeed and return `true` if * The value in `amount` does not exceed the balance of `msg.sender` and * the supplied gas suffices to complete the call. Nevertheless, the `transfer` function of `BEP20` fails in some of those admissible cases.
LowFunction `transferFrom` of Contract `BEP20` FailsAcknowledged
It is expected that invocations of `transferFrom(from, dest, amount)` succeed and return `true` if * the value of `amount` does not exceed the balance of address `from`, * the value of `amount` does not exceed the allowance of `msg.sender` for address `from`, * transferring a value of `amount` to the address in `dest` does not lead to an overflow of the recipient's balance, and * the supplied gas suffices to complete the call. Nevertheless, the `transferFrom` function of `BEP20` fails in some of those admissible cases.
LowFunction `transferFrom` of Contract `BEP20` FailsAcknowledged
It is expected that invocations of `transferFrom(from, dest, amount)` where the address in `dest` equals the address in `from` (i.e. self-transfers) succeed and return `true` if: * The value of `amount` does not exceed the balance of address `from`, * the value of `amount` does not exceed the allowance of `msg.sender` for address `from`, and * the supplied gas suffices to complete the call. Nevertheless, the `transferFrom` function of `BEP20` fails for some self-transfers in these admissible cases.
LowFunction `transferFrom` of Contract `TROSSToken`Acknowledged
It is expected that invocations of `transferFrom(from, dest, amount)` succeed and return `true` if * the value of `amount` does not exceed the balance of address `from`, * the value of `amount` does not exceed the allowance of `msg.sender` for address `from`, * transferring a value of `amount` to the address in `dest` does not lead to an overflow of the recipient's balance, and * the supplied gas suffices to complete the call. Nevertheless, the `transferFrom` function of `BEP20` fails in some of those admissible cases.
LowFunction `transferFrom` of Contract `TROSSToken`Acknowledged
It is expected that invocations of `transferFrom(from, dest, amount)` where the address in `dest` equals the address in `from` (i.e. self-transfers) succeed and return `true` if: * The value of `amount` does not exceed the balance of address `from`, * the value of `amount` does not exceed the allowance of `msg.sender` for address `from`, and * the supplied gas suffices to complete the call. Nevertheless, the `transferFrom` function of `BEP20` fails for some self-transfers in these admissible cases.
Show 3 more
LowRedundant Code ComponentsAcknowledged
The linked statements do not affect the functionality of the codebase and appear to be either leftovers from test code or older functionality.
LowUnchecked `sender` and `recipient` Equality in `_Acknowledged
The `_transfer` function of the provided contract does not check whether the `sender` and `recipient` are the same address. This oversight may lead to unnecessary contract calls and event emissions, wasting gas and potentially causing confusion.
LowUsage of `transfer`/`send` for Sending Native TokAcknowledged
It is not recommended to use Solidity's `transfer()` and `send()` functions for transferring native tokens, since some contracts may not be able to receive the funds. Those functions forward only a fixed amount of gas (2300 specifically) and the receiving contracts may run out of gas before finishing the transfer. Also, EVM instructions' gas costs may increase in the future. Thus, some contracts that can receive now may stop working in the future due to the gas limitation. ```solidity=555 0x06806458405C55E40D75Bd0fE1732500Cd1C229c.transfer(msg.value); ``` - `TROSSToken.constructor` uses `transfer()`.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- TROSS.sol
Part of Trossard’s security record
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us