ApeIron - Audit 3
CertiK reviewed Apeiron (ApeIron - Audit 3) on 11 Oct 2022: 14 findings, 0 critical; 11 marked fixed, 2 acknowledged, 1 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings14
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 0 |
| Medium | 0 | 0 | 2 |
| Low | 1 | 0 | 9 |
HighCentralization Risks in `MarketPlace1155.sol`, `MAcknowledged
In the contract `MarketPlace.sol` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and: * Upgrade the current contract's implementation to any new implementation set by the `_owner`, with function `_authorizeUpgrade()`. * Set the `tokenReceiptHandler` address to any contract address, with function `setupTokenReceiptContracts()`. The `tokenReceiptHandler` contract is in charge of creating and burning receipts when an ERC721 token ID is listed, purchased or cancelled. * Set the `blacklist` address to any contract address, with function `setupBlacklistContracts()`. The `blacklist` contract is in charge of blacklisting specific users and their tokens from being listed in the `MarketPlace.sol` contract. * Set the `platformFeePercent` to any value, with function `setPlatformFeePercent()`. The `platformFeePercent` is the percent fee taken from the seller after their listing was purchased, and this fee is sent to the `payoutWalletAddress`. * Set the `payoutWalletAddress` to any address, with function `setPlatformFeePayoutWalletAddress()`. The `payoutWalletAddress` receives selling fees according to the percent set by `platformFeePercent`. * Set the allowed ERC20 tokens to be used to purchase the listed ERC721 token IDs, with function `setApprovedPurchaseTokenAddresses()`. 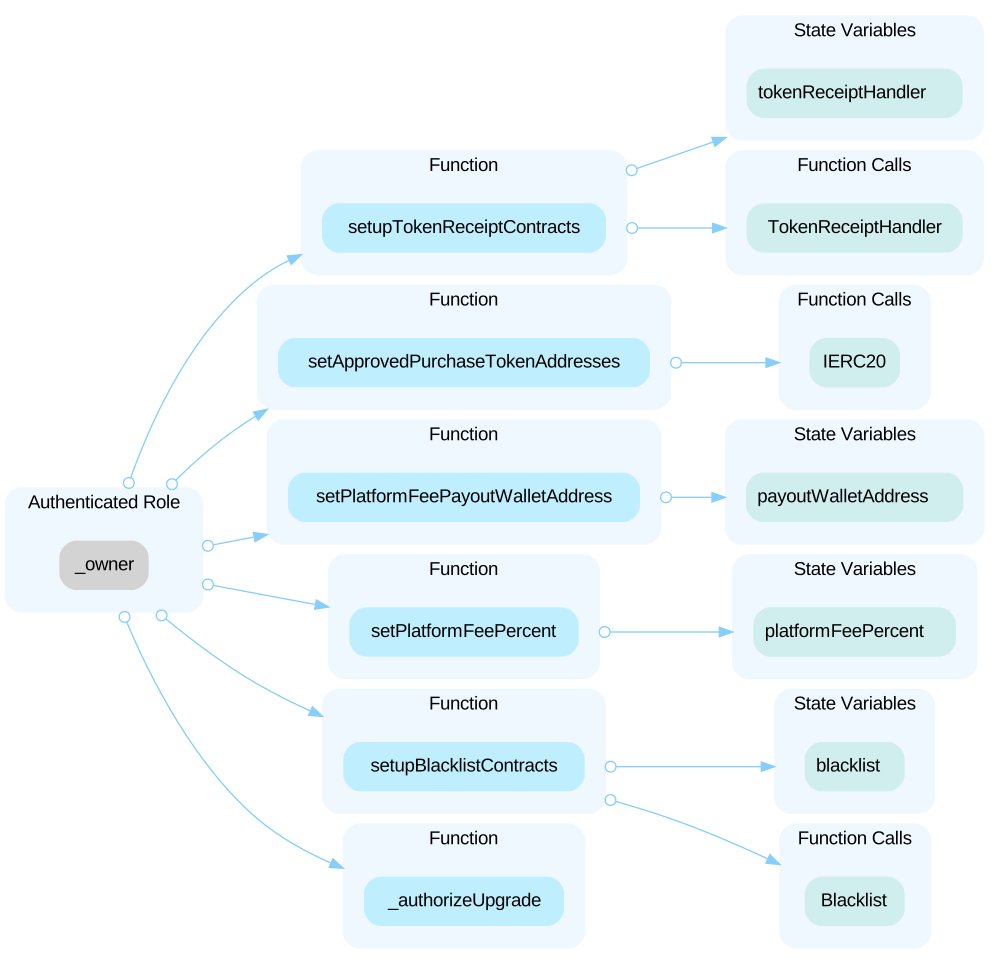 --- In the contract `MarketPlace1155.sol` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and: * Upgrade the current contract's implementation to any new implementation set by the `_owner`, with function `_authorizeUpgrade()`. * Set the `tokenReceiptHandler` address to any contract address, with function `setupTokenReceiptContracts()`. The `tokenReceiptHandler` contract is in charge of creating and burning receipts when an ERC1155 token ID is listed, purchased or cancelled. * Set the `blacklist` address to any contract address, with function `setupBlacklistContracts()`. The `blacklist` contract is in charge of blacklisting specific users and their tokens from being listed in the `MarketPlace1155.sol` contract. * Set the `platformFeePercent` to any value, with function `setPlatformFeePercent()`. The `platformFeePercent` is the percent fee taken from the seller after their listing was purchased, and this fee is sent to the `payoutWalletAddress`. * Set the `payoutWalletAddress` to any address, with function `setPlatformFeePayoutWalletAddress()`. The `payoutWalletAddress` receives selling fees according to the percent set by `platformFeePercent`. * Set the allowed ERC20 tokens to be used to purchase the listed ERC1155 token IDs, with function `setApprovedPurchaseTokenAddresses()`. 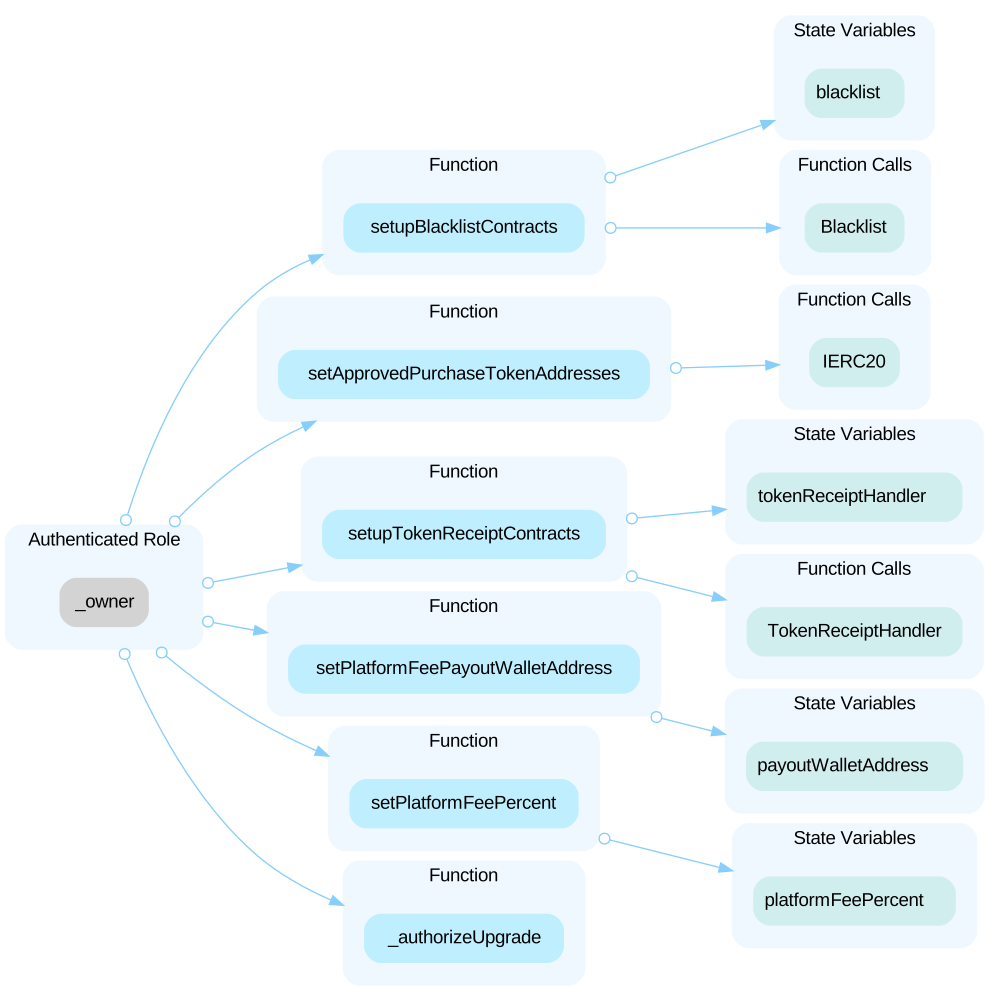 --- In the contract `Blacklist.sol` the role `_owner` has authority over the functions: * `setAdmin()` * `_authorizeUpgrade()` Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and: * Upgrade the current contract's implementation to any new implementation set by the `_owner`, with function `_authorizeUpgrade()`. * Add/Remove any address from the `admin` role, with function `setAdmin()`. The `admin` role has privildeged access to the functions described below. --- In the contract `Blacklist.sol` the role `admin` has authority over the functions: * `blacklistNFTs()` * `setDisabled()` Any compromise to the `admin` account may allow the hacker to take advantage of this authority and: * Blacklist the following from being listed on `MarketPlace.sol` or `MarketPlace1155.sol`, with function `blacklistNFTs()`: * A specific users NFT/ERC1155 token IDs. * All of the users tokens for a specific NFT/ERC1155. * All of the users tokens from all NFT/ERC1155. * Enable/Disable the contract's functionality of preventing users and their tokens from being listed on `MarketPlace.sol` or `MarketPlace1155.sol`, with function `setDisabled()`.
HighCentralized Control of Contract UpgradeAcknowledged
The linked contracts are upgradeable contracts, and the owner can upgrade the contract without the community's consent. If an attacker compromises the account, they can change the implementation of the contract and drain tokens from the contract.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (3)
- contracts/Blacklist.sol
- contracts/marketplace/MarketPlace.sol
- contracts/marketplace/MarketPlace1155.sol
Part of Apeiron’s security record
Security firm
 CertiK
1,044 projects reviewed · 1,393 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us