Iskra - Launchpad
CertiK reviewed Iskra (Iskra - Launchpad) on 12 Jun 2023: 23 findings, 0 critical; 16 marked fixed, 7 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings23
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 5 | 0 | 0 |
| Medium | 0 | 0 | 2 |
| Low | 2 | 0 | 14 |
HighCentralization Risks in IGOVesting.solOpen
In the contract `IGOVesting` the role `_operator` has authority over the functions shown in the diagram below. Any compromise to an `_operator` account may allow the hacker to take advantage of this authority and register or add new vesting for an account. 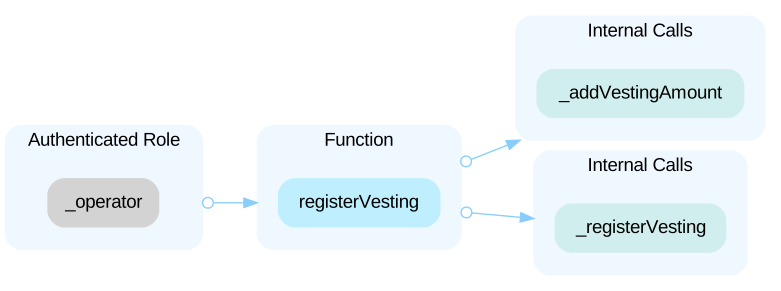 ----- In the contract `IGOVesting` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and: - transfer ownership to an address they control; - add or remove any address as an operator. 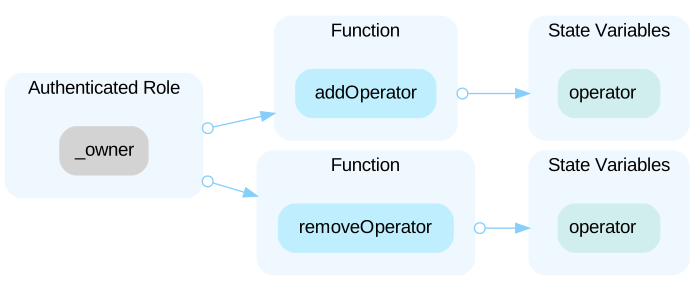
HighCentralization Risks in InitialGameOffering.solOpen
In the contract `InitialGameOffering` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and : - transfer ownership to an address they control; - modify the time intervals of each status, if the contract state is `READY`; - modify the sale amounts, if the contract state is `READY`; - revoke the contract if the sale has not started yet, this allows the `owner` address to drain tokens from the contract; - set any address they control as the operator. 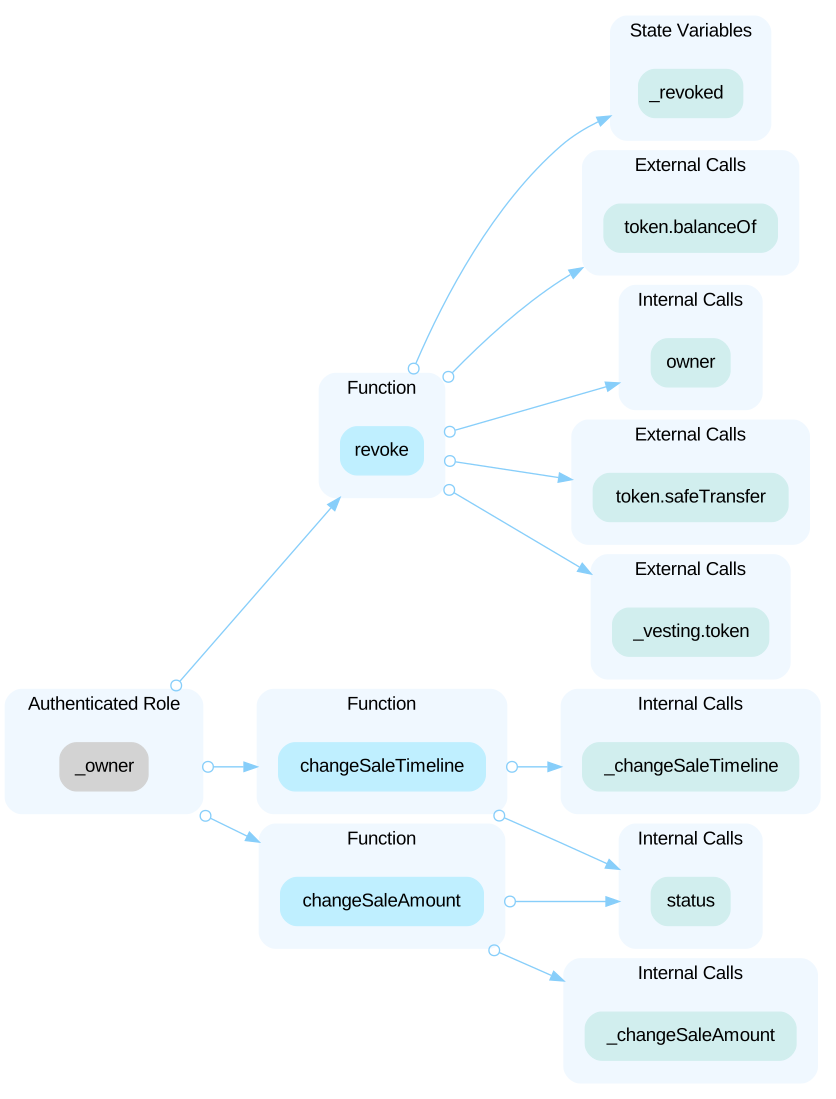 ------ In the contract `InitialGameOffering` the role `operator` has authority over the functions shown in the diagram below. Any compromise to the `operator` account may allow the hacker to take advantage of this authority and: - set any address they control as the new operator. - reclaim tokens when the contract state is `SALE_FINISHED`. 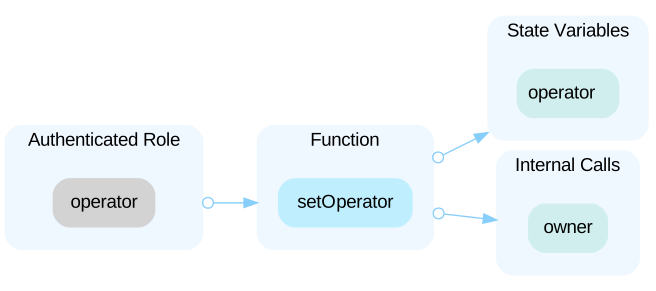
HighCentralization Risks in Launchpad.solOpen
In the contract `Launchpad` the role `_operator` has authority over the functions shown in the diagram below. Any compromise to the `_operator` account may allow the hacker to take advantage of this authority and, set any address they control as the operator, interfere with the `IGO` contract by modifying important state variables. This contract has a lot of control over `InitialGameOffering` contracts. The hacker could also: - set an address they control as the fee recipient and set the fees to the maximum in order to divert tokens; - deploy malicious `InitialGameOffering` and `IGOVesting` contracts and make them appear legitimate since they will be deployed from the launchpad. 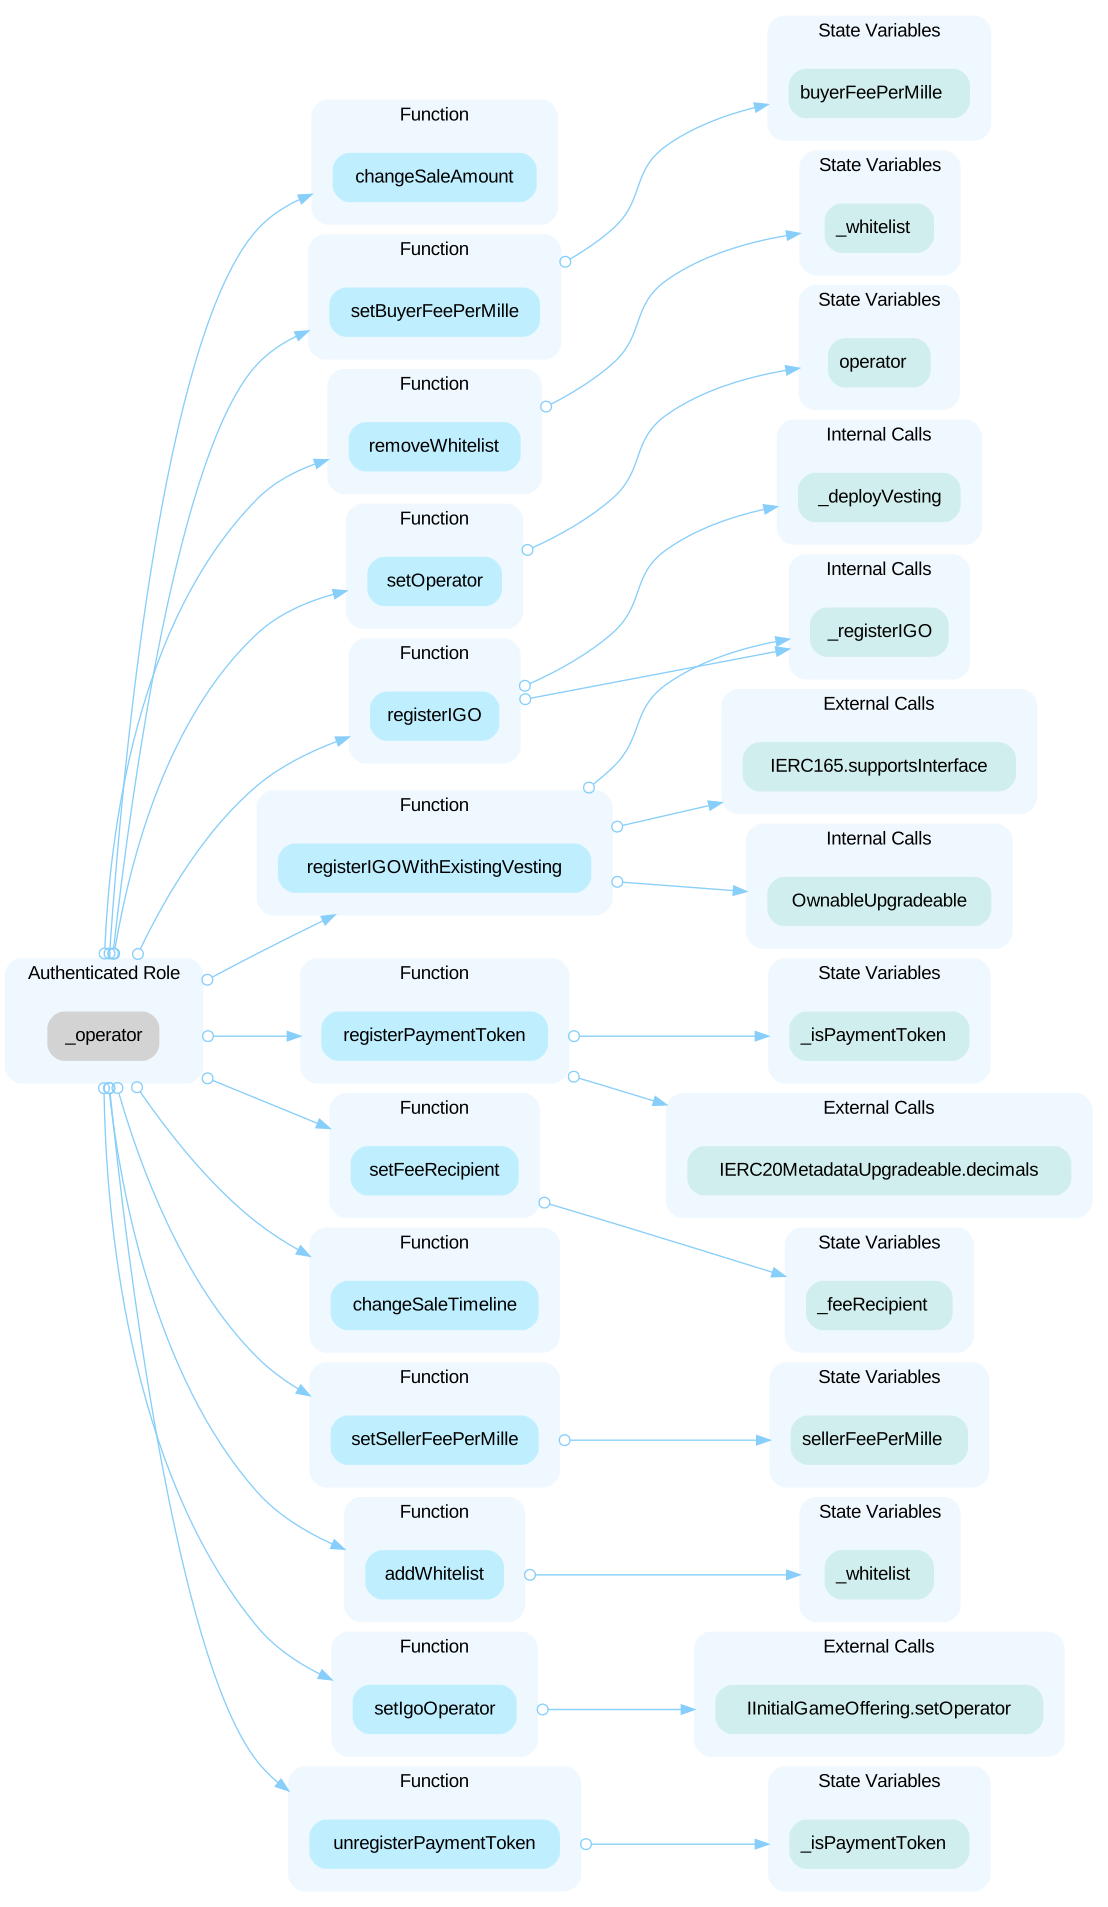 ---- In the contract `Launchpad` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and : - transfer ownership to an address they control; - change the `qualificationChecker` to an address of a malicious contract, this would allow to interfere with the signature mechanism; - change the oracle address, which is critical for the safety and reliability of `InitialGameOffering` contracts. 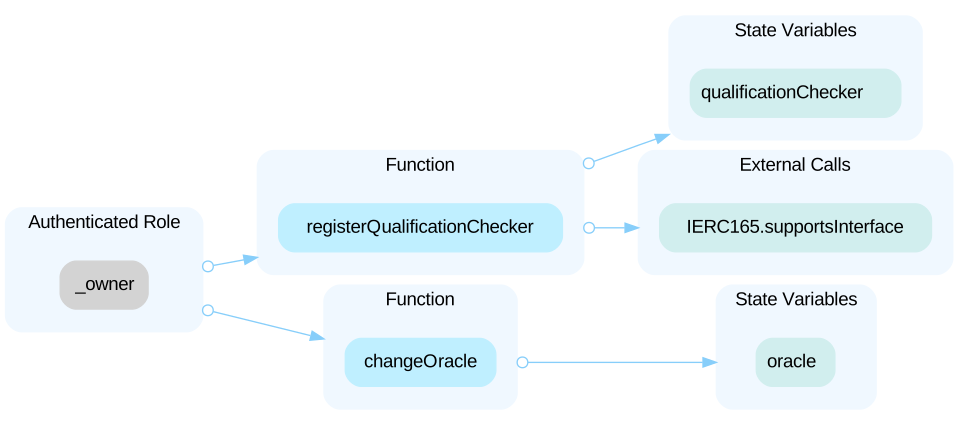
HighCentralization Risks in StructuredSignVerifier.soOpen
In the contract `StructuredSignVerifier` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and : - transfer ownership to an address they control; - modify the `signLifespan`, which is used as a security parameter when verifying a signature. - set any address as the new `signer` which is a crucial parameter to ensure the signature mechanism works fine. 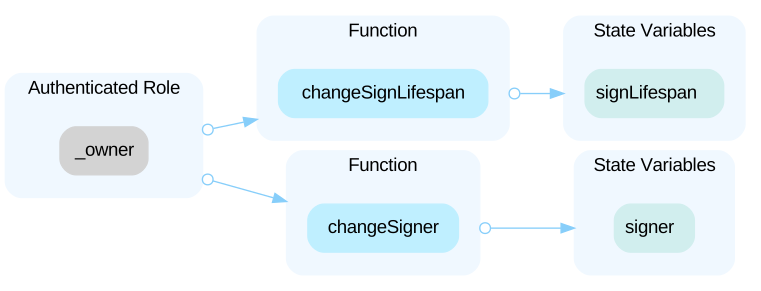
HighCentralized Control of Contract UpgradeOpen
`IGOVesting`, `InitialGameOffering`, and `LaunchpadBase` are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
LowMissing Emit EventsOpen
Events should be emitted in sensitive functions controlled by centralization roles.
LowThird Party DependencyOpen
The contract is serving as the underlying entity to interact with one or more third-party protocols. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. --- ```solidity=19 IExpTokenRule private _expTokenRule; ``` - The contract `IGOVesting` interacts with a third-party contract with `IExpTokenRule` interface via `_expTokenRule`. --- ```solidity=61 address[] private _paymentTokens; ``` - The contract `InitialGameOffering` interacts with a third-party contract with `IERC20Upgradeable` interface via `_paymentTokens`. --- ```solidity=242 address paymentToken, ``` - The function `InitialGameOffering._participate` interacts with a third-party contract with `IERC20Upgradeable` interface via `paymentToken`. ---- ```solidity=364 require(_launchpadRule.isOracle(msg.sender), "invalid msg.sender."); ``` The function `InitialGameOffering.submitLotteryResult` interacts with an address `oracle` declared in `LaunchpadBase`, through the interface `_launchpadRule` and the function `Launchpad.isOracle()`. \ The safety of `InitialGameOffering` lottery depends heavily on the reliability of this `oracle` address. ----- The contract `Launchpad.sol` is using functions from `BeaconProxyFactory.sol` which is outside the scope of this audit. The scope of the audit treats this contract as a black box and assumes its functional correctness.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (8)
- contracts/launchpad/InitialGameOffering.sol
- contracts/upgradable/UpgradableBase.sol
- contracts/verifier/StructuredSignVerifier.sol
- contracts/launchpad/LaunchpadBase.sol
- contracts/launchpad/Launchpad.sol
- contracts/launchpad/LaunchpadInitializer.sol
- contracts/launchpad/LaunchpadQualificationChecker.sol
- contracts/launchpad/IGOVesting.sol
Part of Iskra’s security record
 Iskra
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us