The Unfettered
CertiK reviewed The UNFETTERED on 22 May 2023: 29 findings, 0 critical; 17 marked fixed, 2 acknowledged, 10 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings29
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 10 | 0 | 17 |
HighCentralization Related RisksAcknowledged
In the contract `Crowdfunding`, the role `Manager` has authority over the functions below: - function `addRewards`: to add rewards vestings to designated addresses if 3 out of 5 managers approved. - function `deactivateInvestorVesting`: to make some `_vestingIndexes` of a `_rewardOwner` inactive if 3 out of 5 managers approved. - function `activateInvestorVesting`: to make some `_vestingIndexes` of a `_rewardOwner` active if 3 out of 5 managers approved. - function `addToBlacklist`: to make a `_rewardOwner` cannot claim the subsequent vesting rewards if 3 out of 5 managers approved. - function `removeFromBlacklist`: to make a `_rewardOwner` able to claim the subsequent vesting rewards again if 3 out of 5 managers approved. Any compromise to the `Manager` account may allow the hacker to take advantage of this authority. In the contract `SoulsToken`, the role `Manager` has authority over the functions below: - function `disableBotPrevention`: to disable the bot prevention mechanism if 3 out of 5 managers approved. - function `enableBotPrevention`: to enable the bot prevention mechanism if 3 out of 5 managers approved. Any compromise to the `Manager` account may allow the hacker to take advantage of this authority. In the contract `Vault`, the role `Manager` has authority over the functions below: - function `withdrawTokens`: to withdraw tokens to addresses in regards to the vesting if 3 out of 5 managers approved. Any compromise to the `Manager` account may allow the hacker to take advantage of this authority. In the contract `LiquidityVault`, the role `Manager` has authority over the functions below: - function `addLiquidityOnDEX`: to add liquidities to the `mainVaultAddress` if 3 out of 5 managers approved. - function `withdrawMarketMakerShare`: to withdraw the `MarketMakerShare` part if 3 out of 5 managers approved. - function `withdrawRemainingTokens`: to withdraw tokens from liquidity vault after unlock time if 3 out of 5 managers approved. Any compromise to the `Manager` account may allow the hacker to take advantage of this authority. In the contract `BotPrevention` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set `botPreventionParams`, `tokenAddress`, `managers`, `tradingEnabled`, and `dexPairAddress`. 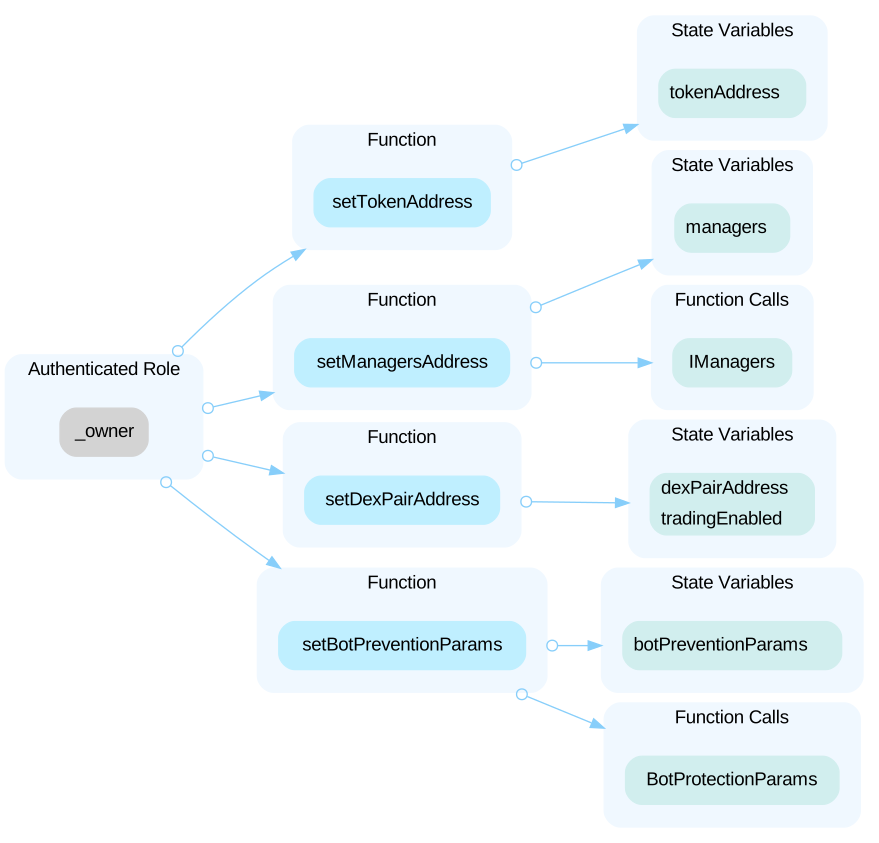 In the contract `BotPrevention`, the role `Manager` has authority over the functions below: - function `disableTrading`: to disable all the tradings if 3 out of 5 managers approved. - function `enableTrading`: to enable all the tradings if 3 out of 5 managers approved. Any compromise to the `Manager` account may allow the hacker to take advantage of this authority. In the contract `MainVault` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority, configure the `CrowdfundingVault`, `Vault`, and `LiquidityVault`, add corresponding share and vesting, and transfer `soulsToken` to any address. 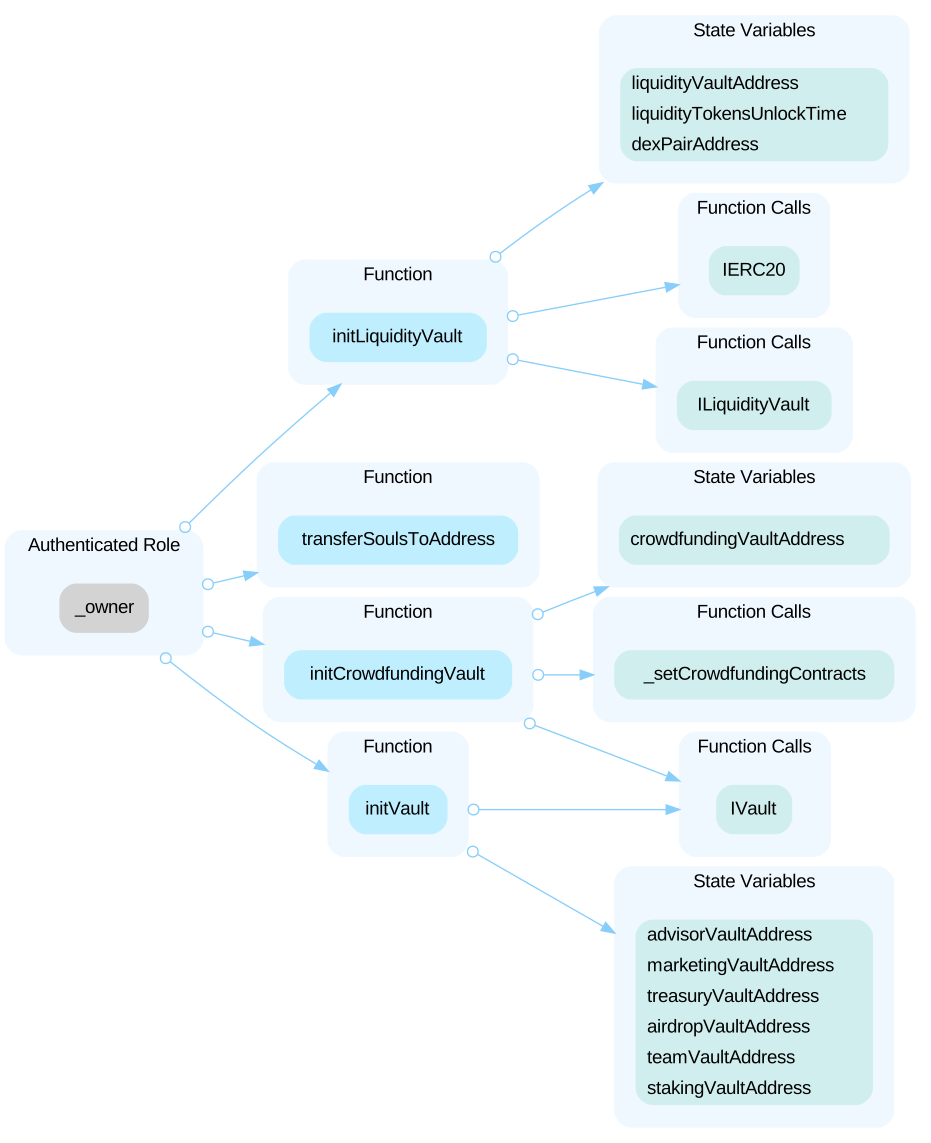 In the contract `MainVault`, the role `Manager` has authority over the functions below: - function `initStakingVault`: to configure the StakingVault and add the corresponding share and vesting if 3 out of 5 managers approved. - function `initPlayToEarnVault`: to configure the PlayToEarnVault and add the corresponding share and vesting if 3 out of 5 managers approved. - function `withdrawLPTokens`: to withdraw all the LP tokens in the contract if 3 out of 5 managers approved and `liquidityTokensUnlockTime` is reached. - function `addAddressToTrustedSources`: to add a new address as `TrustedSources` if 3 out of 5 managers approved, and this address could be used to invoke the `approveTopic`. - function `testApproveTopicFunction`: to set a new `_testAddress` if 3 out of 5 managers approved. Any compromise to the `Manager` account may allow the hacker to take advantage of this authority. In the contract `Managers` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and add any addresses as the `TrustedSources`. 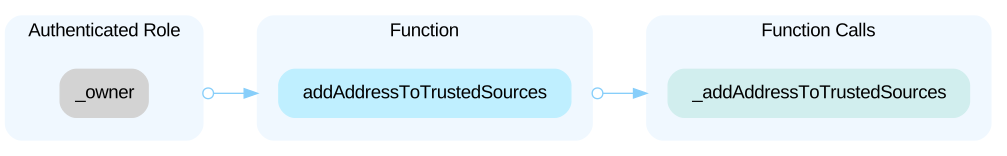 In the contract `Managers`, the role `Manager` has authority over the functions below: - function `approveTopic`: to approve a topic by a manager (as `tx.origin`) and execute the topic if 3 out of 5 managers approved, besides, the `msg.sender` should be `TrustedSources`. - function `cancelTopi
HighCentralized risk in `addLiquidity`Acknowledged
```solidity= // add the liquidity _router.addLiquidity( soulsTokenAddress, stableTokenAddress, _tokenAmountToAdd, _stableAmountToAdd, 0, 0, mainVaultAddress, block.timestamp + 1 hours ); ``` The `addLiquidity` function calls the `IPancakeRouter02.addLiquidityETH` function with the `to` address specified as `mainVaultAddress` for acquiring the generated LP tokens from the `SOUL-StableCoin` pool. As a result, over time the `mainVaultAddress` address will accumulate a significant portion of LP tokens. If the `mainVaultAddress` is an EOA (Externally Owned Account), the mishandling of its private key can have devastating consequences for the project as a whole.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (14)
- contracts/Vaults/LiquidityVault.sol
- contracts/Claimables/WithdrawClaim.sol
- contracts/Claimables/Crowdfunding.sol
- contracts/BotPrevention.sol
- contracts/Claimables/Airdrop.sol
- contracts/Vaults/AirdropVault.sol
- contracts/Vaults/PlayToEarnVault.sol
- contracts/Claimables/Staking.sol
- contracts/Vaults/StakingVault.sol
- contracts/Managers.sol
- contracts/Vaults/Vault.sol
- contracts/MainVault.sol
- contracts/SoulsToken.sol
- contracts/Vaults/CrowdfundingVault.sol
Part of The UNFETTERED’s security record
 The UNFETTERED
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us