Olympus Protocol
CertiK reviewed Olympus (Olympus Protocol) on 11 Sep 2022: 12 findings, 0 critical; 6 marked fixed, 6 open.
The original report was removed from its address (seen 14 Oct 2026).
Trustblock does not review code.
Findings12
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 4 | 0 | 6 |
HighCentralization Risks in OLY.solOpen
In the contract `OLY` the roles `_actionContract` and `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_actionContract` account may allow the hacker to take advantage of this authority and: * Mint any amount of `OLY` tokens to any receiving address, with function `mintAction()`. * Increase the `teamIDO` amount for a user's team user by any amount, with function `setPerformanceIDO()`. * Increase the `teamShare` amount for a user's team user by any amount, with function `setPerformanceShare()`. 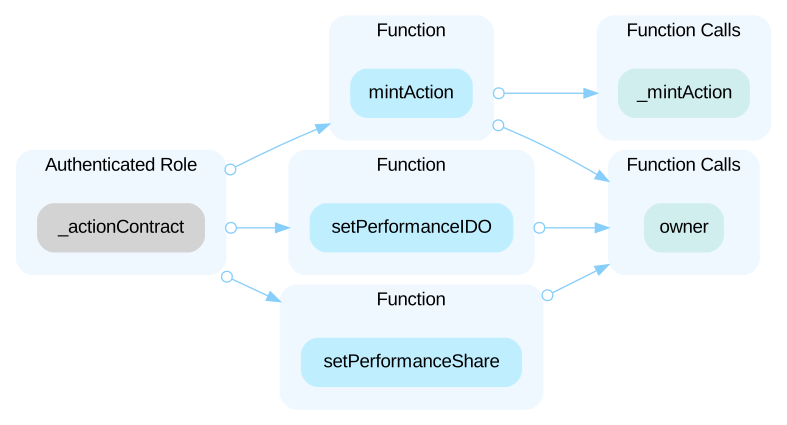 --- In the contract `OLY` the roles `_allowMint` and `_owner` has authority over the function shown in the diagram below. Any compromise to the `_allowMint` account may allow the hacker to take advantage of this authority and: * Mint any amount of `OLY` tokens to any receiving address, with function `mint()`. This minting process distributes the newly minted tokens as follows: * 40% to the receiving address * 20% to the `_dividend` address * 40% to the last 10 referral address down the line from the receiving address. * Any remaining tokens will be sent to the `_pools` address. 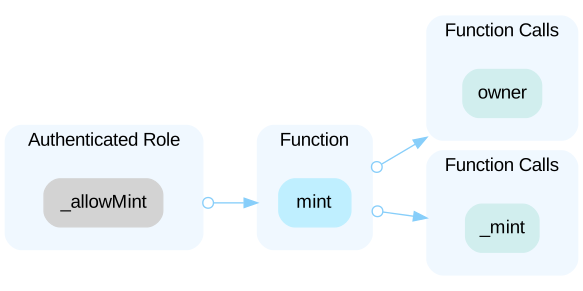 --- In the contract `OLY` the role `_owner` has authority over the functions shown in the diagrams below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and: * Transfer any `ERC20` token from the contract to any address, with function `transfer()`. * Set the team user `tid` address to the users address, with function `setTeamUser()`. * Add a new address to the `_cakeLPs` list, with function `setCakeLP()`. Tokens transferring to/from these addresses are assumed to be liquidity pool selling/buying transactions, and are subject to a different fee structure than regular token transfers. * Exclude any address, with function `setExcluded()`. Excluded addresses can still purchase `OLY` tokens from the `_cakeLPs` addresses even if the swap is not yet open. * Set the `_swapTime` to any time, with function `setSwapTime()`. The `_swapTime` dictates when users can purchase `OLY` tokens from the `_cakeLPs` addresses. Excluded addresses set by `setExcluded()` *do not* have this restriction. * Set the `_dividend`, `_pools`, and `_funds` addresses to any address, with functions `setDividend()`, `setPools()` and `setFunds()`. These addresses receive a portion of the fees during token transfers and token minting. * Set the `_actionContract` and `allowMint` addresses to any address, with functions `setAllowMint()` and `setActionContract()`. The `_actionContract` and `allowMint` address has authority over the functions described in this finding above. * Set the fee structure for buying, selling and transferring tokens to any percent, with function `setParams()`. * Renounce ownership of the `_owner` role such that the functions described above can no longer be called. * Transfer ownership of the `_owner` role to any address. The new address will have the authority to call any of the functions described above. 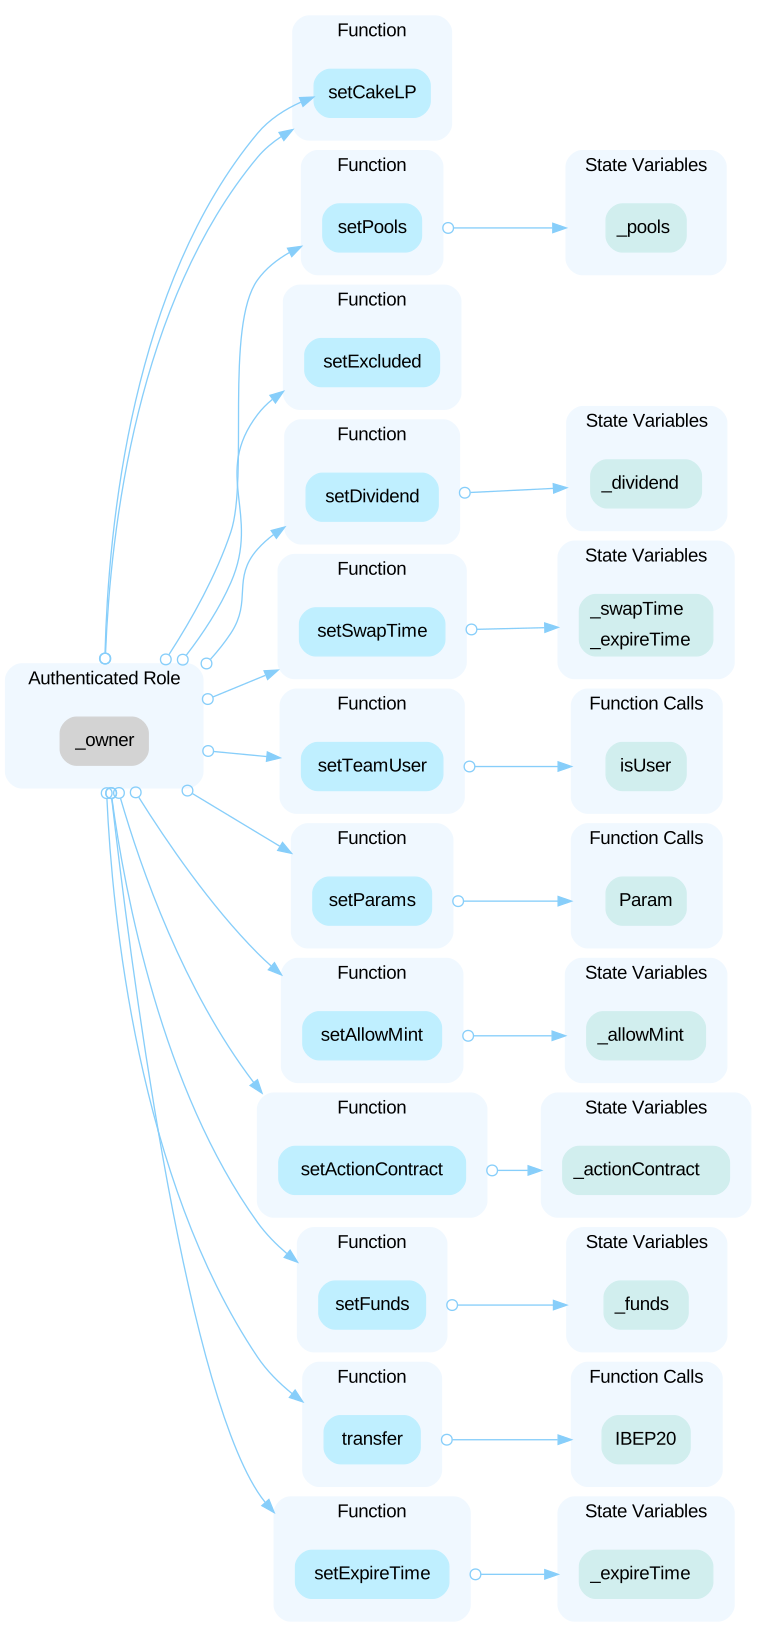 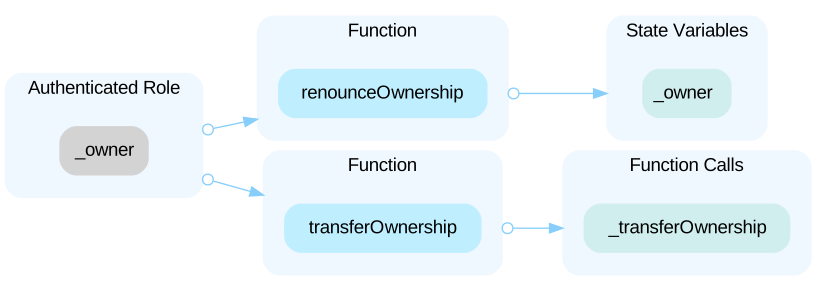
HighInitial Token DistributionOpen
All of the `OLY` tokens are sent to the EOA [0xE753D7ba0ac5E88B68FAECa98abd2964C813b060](https://bscscan.com/address/0xE753D7ba0ac5E88B68FAECa98abd2964C813b060) when deploying the contract. This could be a centralization risk as the deployer can distribute `OLY` tokens without obtaining the consensus of the community.
LowMissing Emit EventsOpen
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
LowNo Fee Applied if Token Sender is a ContractOpen
During token transfers in function `_transfer()`, the else statement on line 658 covers the normal token transfers (Not buying/selling tokens from/to a liquidity pool). A fee is taken on normal token transfers, using function `_transferFee()`. However line 662 checks if the sender is a contract and if so, no fee is applied to the token transfer by calling `_transferFree()` instead. ```solidity=662 if (isContract(sender)) { //If the sender is a contract _transferFree(sender, receipt, amount); //Tax free token transfer } else { //If the sender is an EOA _transferFee( //Tax applied on token transfer sender, receipt, amount, false, _params["transfer"] ); } ``` If the sender is an EOA, a fee is applied. If the sender is a contract, no fee is applied.
LowUninitialized Local VariableOpen
The linked locations contain local variables that are not initialized.
LowUser-Defined GettersOpen
The linked functions are equivalent to the compiler-generated getter functions for the respective variables.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- contracts/OLY.sol
Part of Olympus’s security record
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us