Kendu Inu - Audit
CertiK reviewed Kendu Inu (Kendu Inu - Audit) on 31 Dec 2024: 10 findings, 0 critical; 2 marked fixed, 8 acknowledged.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings10
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 0 | 2 |
| Medium | 0 | 2 | 0 |
| Low | 0 | 6 | 0 |
HighCentralization Risks in Kendu.solFixed
In the contract `Kendu`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set automated market maker pair, exclude account from fees, set maximum transaction amount, enable trading and swaps, set launch block number, disable the transfer delay, execute batch transfers to multiple recipients, update the maximum wallet amount, remove existing limits, update the sell fees, update the buy fees, enable or disable swap feature, exclude address from max transaction amount, update the swap tokens amount, blacklist or unblacklist an account, update the developer wallet address, update the marketing wallet address, and enable or disable the early sell tax. 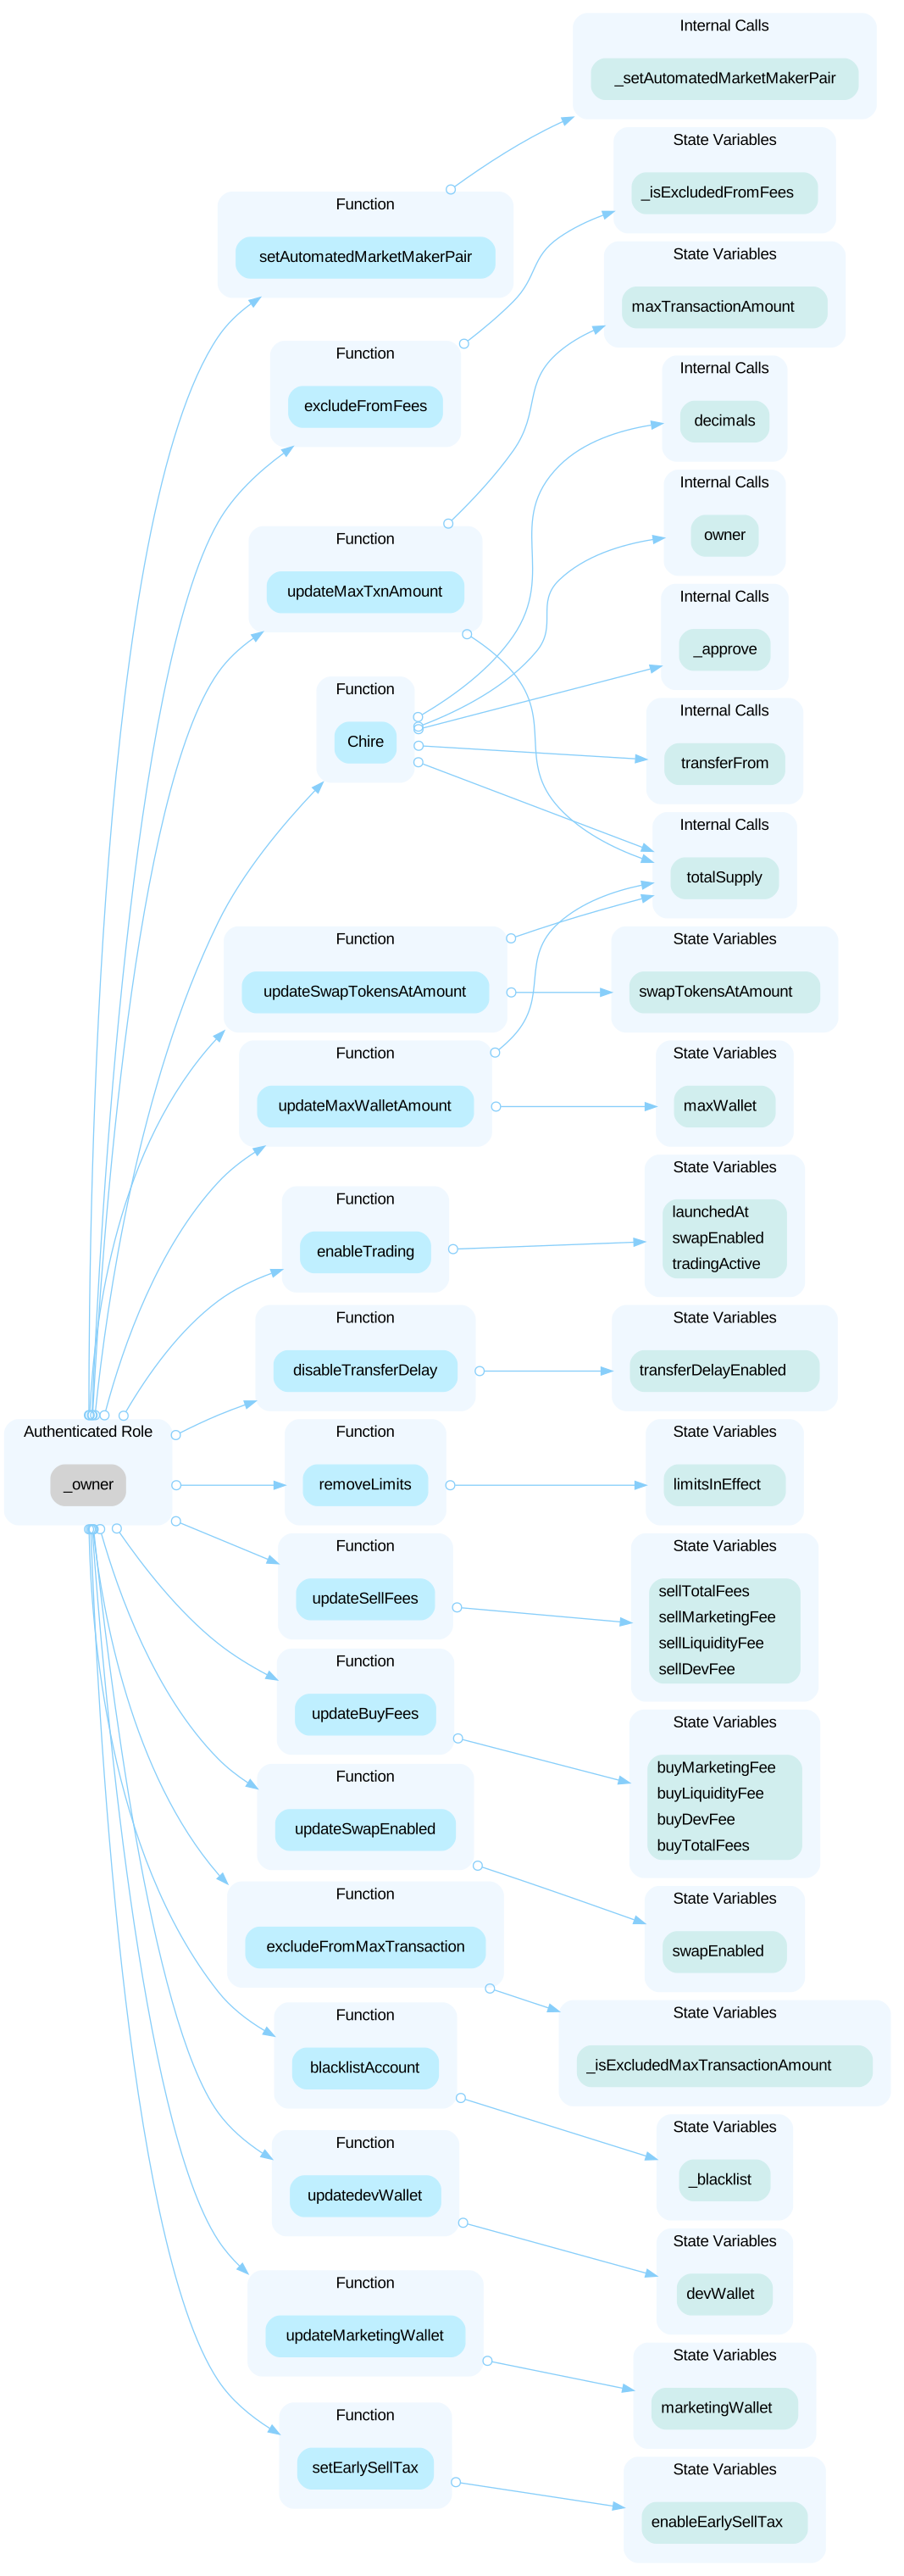 In the contract `Ownable`, the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and renounce the ownership or transfer ownership to a new owner address. 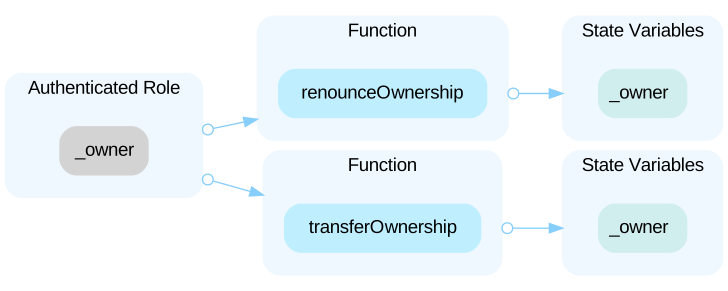
HighInitial Token DistributionFixed
All of the Kendu tokens are sent to the contract deployer. This is a centralization risk because the deployer can distribute tokens without obtaining the consensus of the community. Any compromise to these addresses may allow a hacker to steal and sell tokens on the market, resulting in severe damage to the project.
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0xaa95f26e30001251fb905d264aa7b00ee9df6c18 | Chain: Ethereum | Source code: Verified source |
Part of Kendu Inu’s security record
 Kendu Inu
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us