Derify Protocol v2
CertiK reviewed Derify protocol (Derify Protocol v2) on 7 Dec 2023: 18 findings, 0 critical; 3 marked fixed, 6 acknowledged, 9 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings18
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 3 | 1 |
| Medium | 0 | 3 | 2 |
| Low | 9 | 0 | 0 |
HighCentralization Related RisksAcknowledged
In the contract `DerifyClearing`/ `DerifyClearingModule` the role `EXECUTOR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `EXECUTOR_ROLE` account may allow the hacker to take advantage of this authority: - withdraw executor's reward - transfer limit order to market - stop the position for profit or loss - liquidate or partial liquidate the user 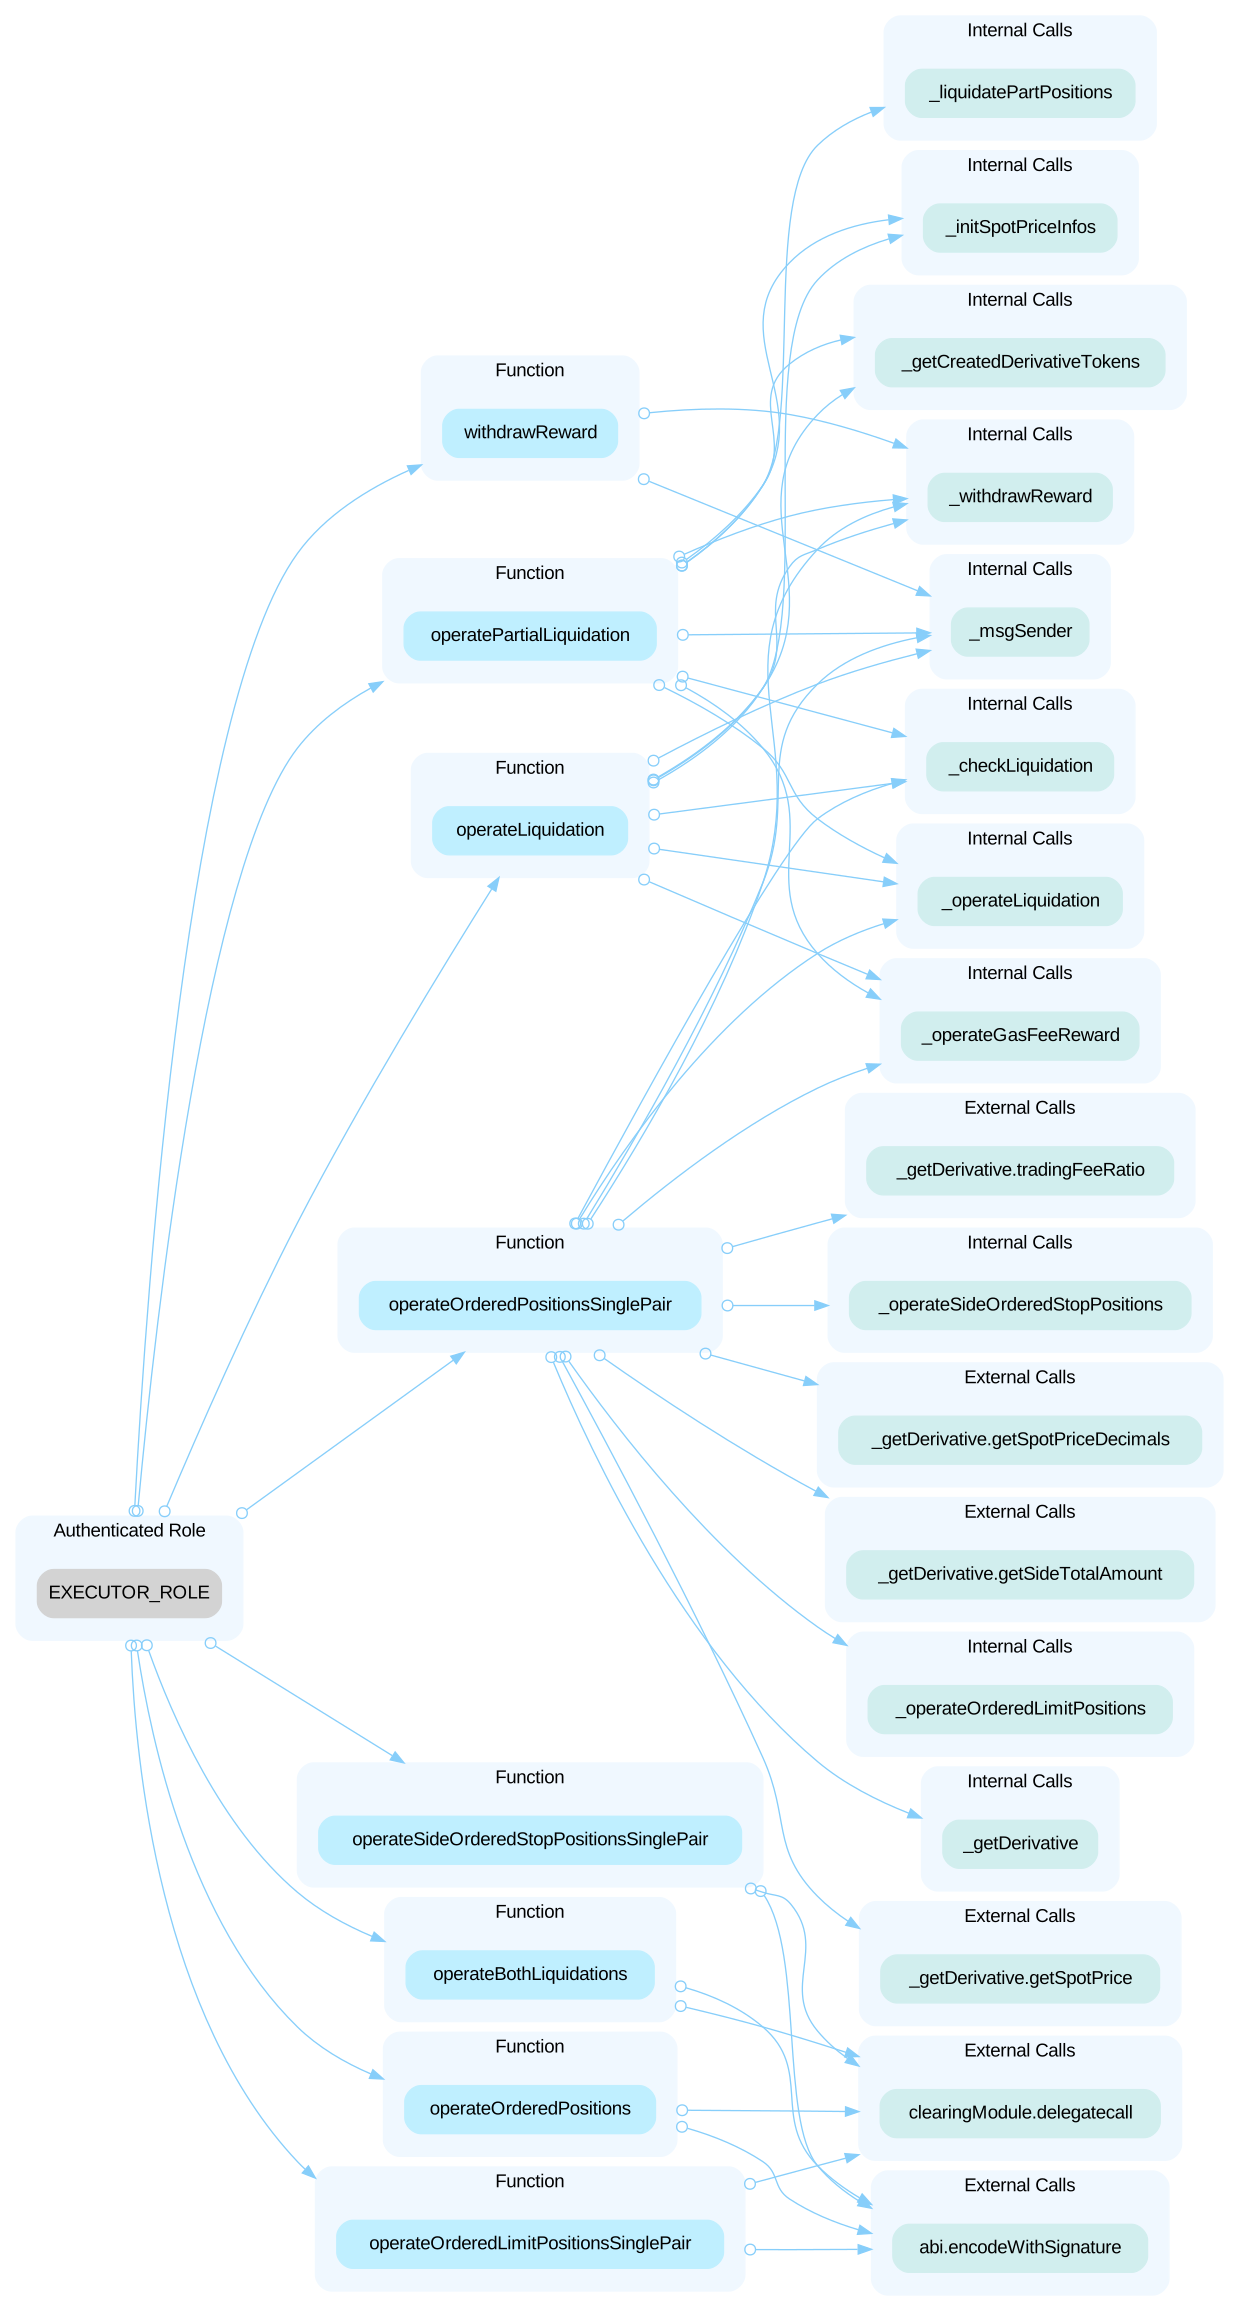 In the contract `DerifyClearing` / `DerifyClearingModule` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority: - pause and unpause the contract 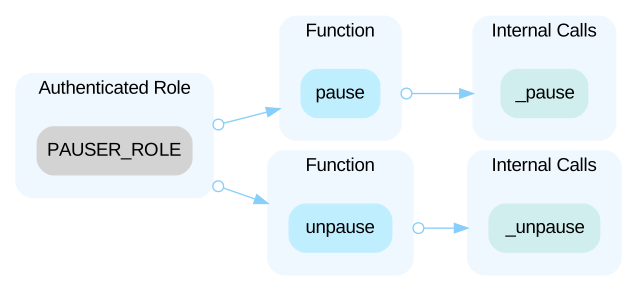 In the contract `DerifyClearing` / `DerifyClearingModule` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority: - update contract‘s ratio 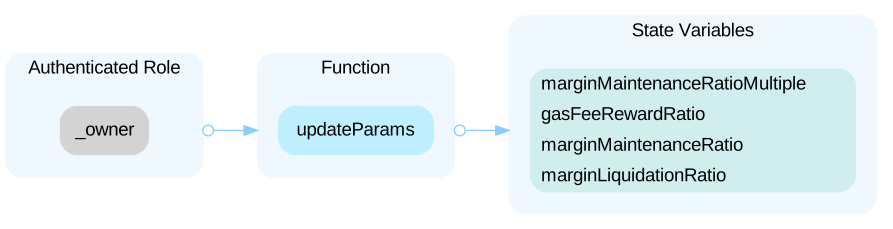 In the contract `DerifyExchange` the role `BUYBACK_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `BUYBACK_ROLE` account may allow the hacker to take advantage of this authority: - buyBack Drf tokens 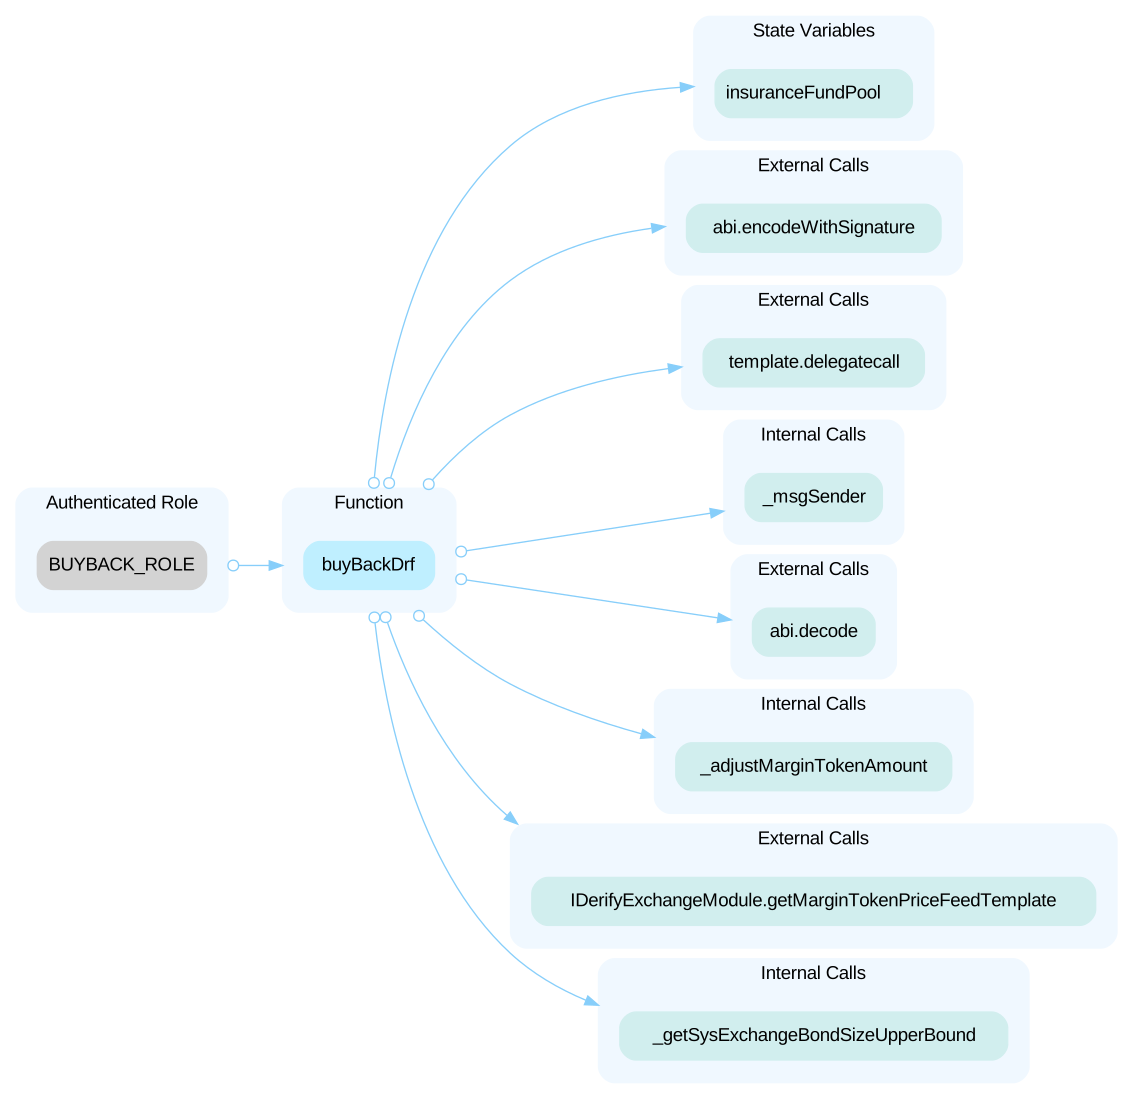 In the contract `DerifyExchange` the role `CLEARING_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `CLEARING_ROLE` account may allow the hacker to take advantage of this authority: - transfer one's tokens to others - remove the trader 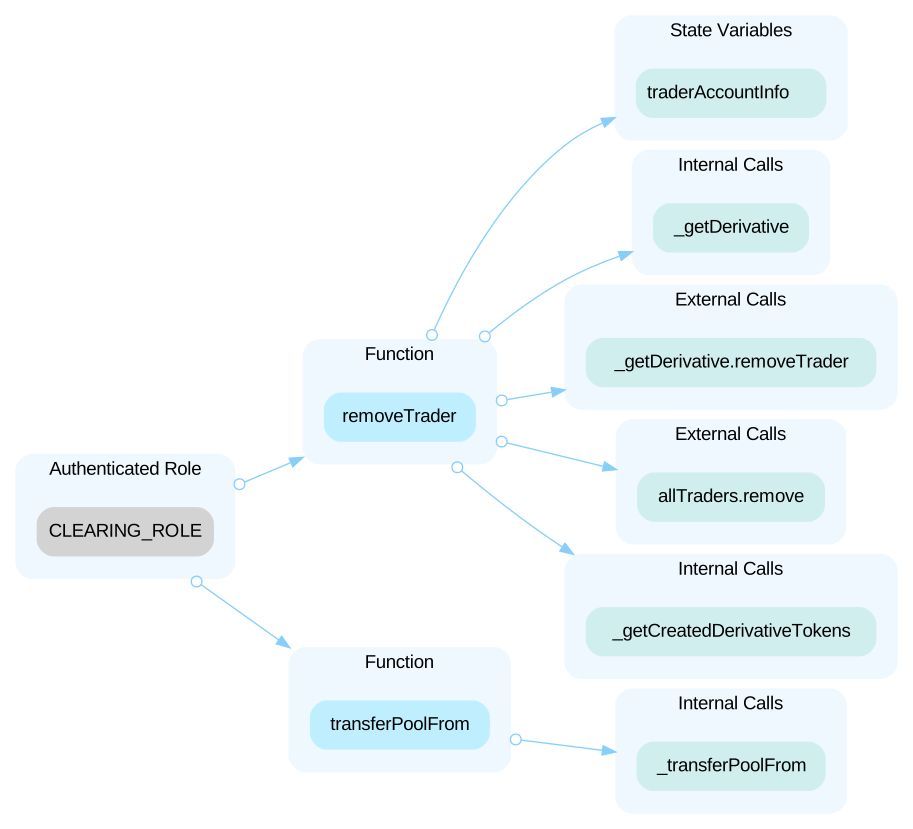 In the contract `DerifyExchange` the role `FEE_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `FEE_ROLE` account may allow the hacker to take advantage of this authority: - update the trader's balance - charge the trading fee 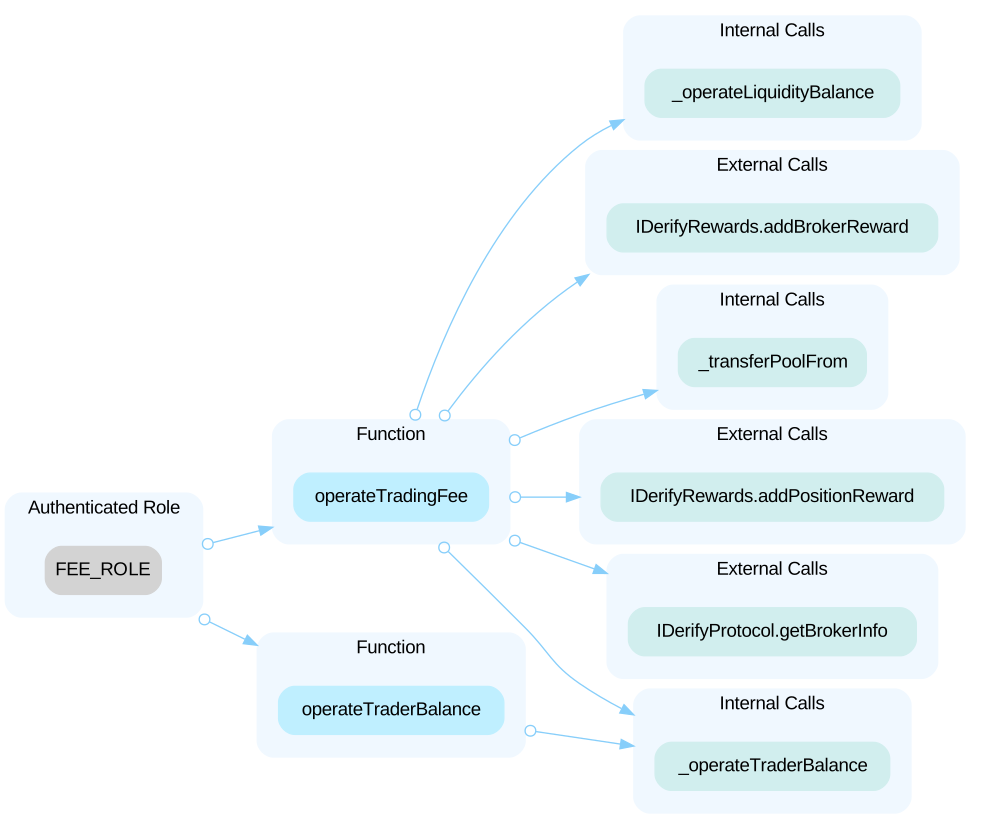 In the contract `DerifyExchange` the role `PAUSER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PAUSER_ROLE` account may allow the hacker to take advantage of this authority: - pause and unpause the contract 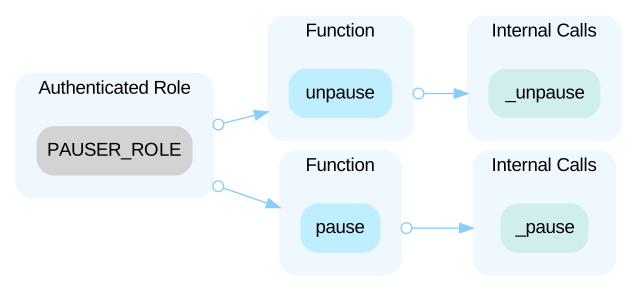 In the contract `DerifyExchange` the role `REWARD_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `REWARD_ROLE` account may allow the hacker to take advantage of this authority: - transfer marginToken to trader 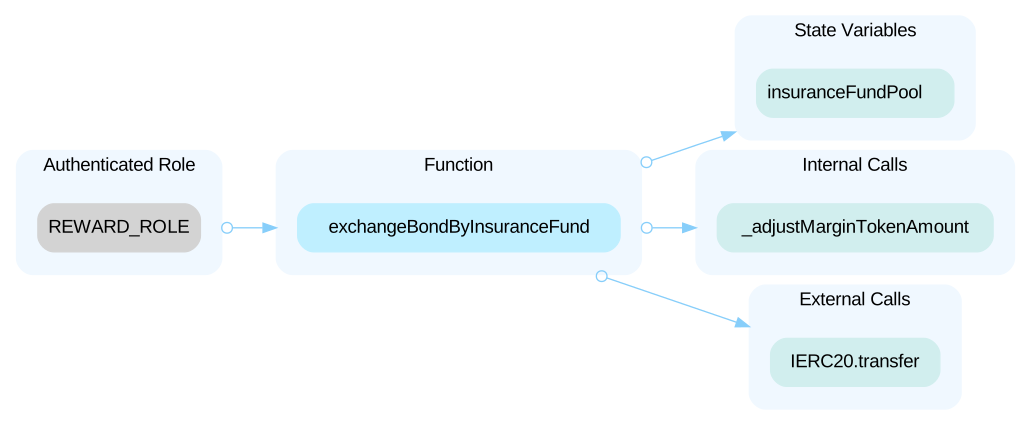 In the contract `DerifyExchange` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority: - initialize the contract - update the variable `thetaRatio`, `buyBackFundRatio` and `minOpenAmount` 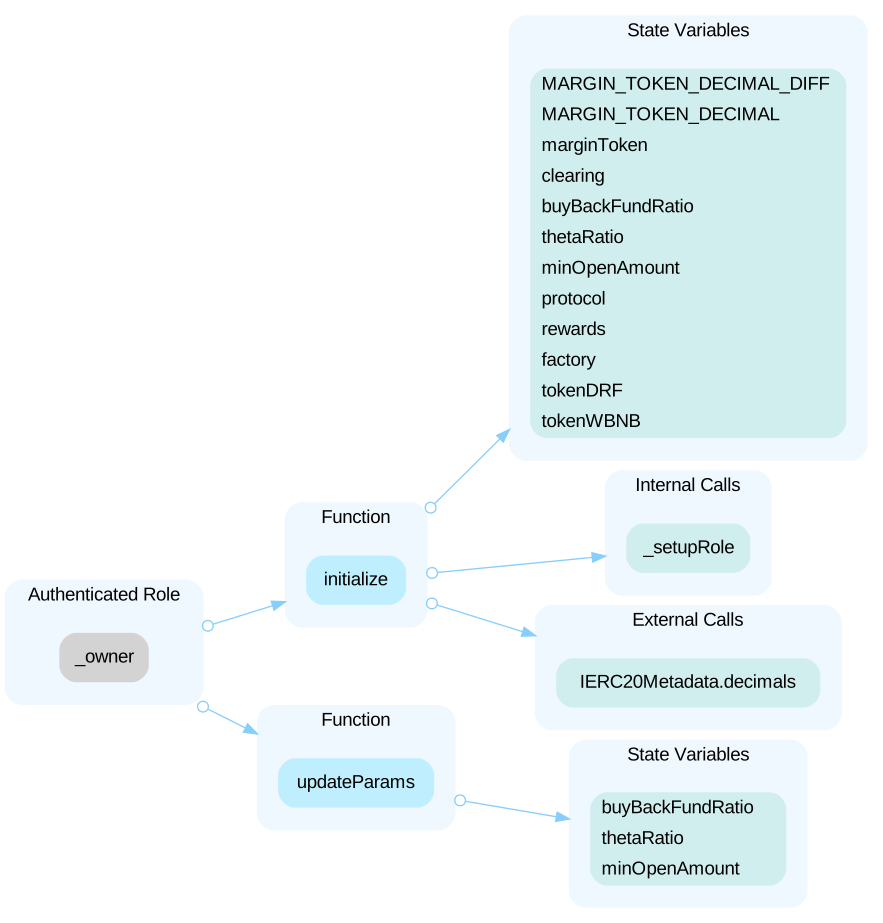 In the contract `DerifyDerivative` / `DerifyDerivativeModule` the role `CALLER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `CALLER_ROLE` account may allow the hacker to take advantage of this authority: - open market price position - create and cancel the limit price order - close the Position - remove the trader 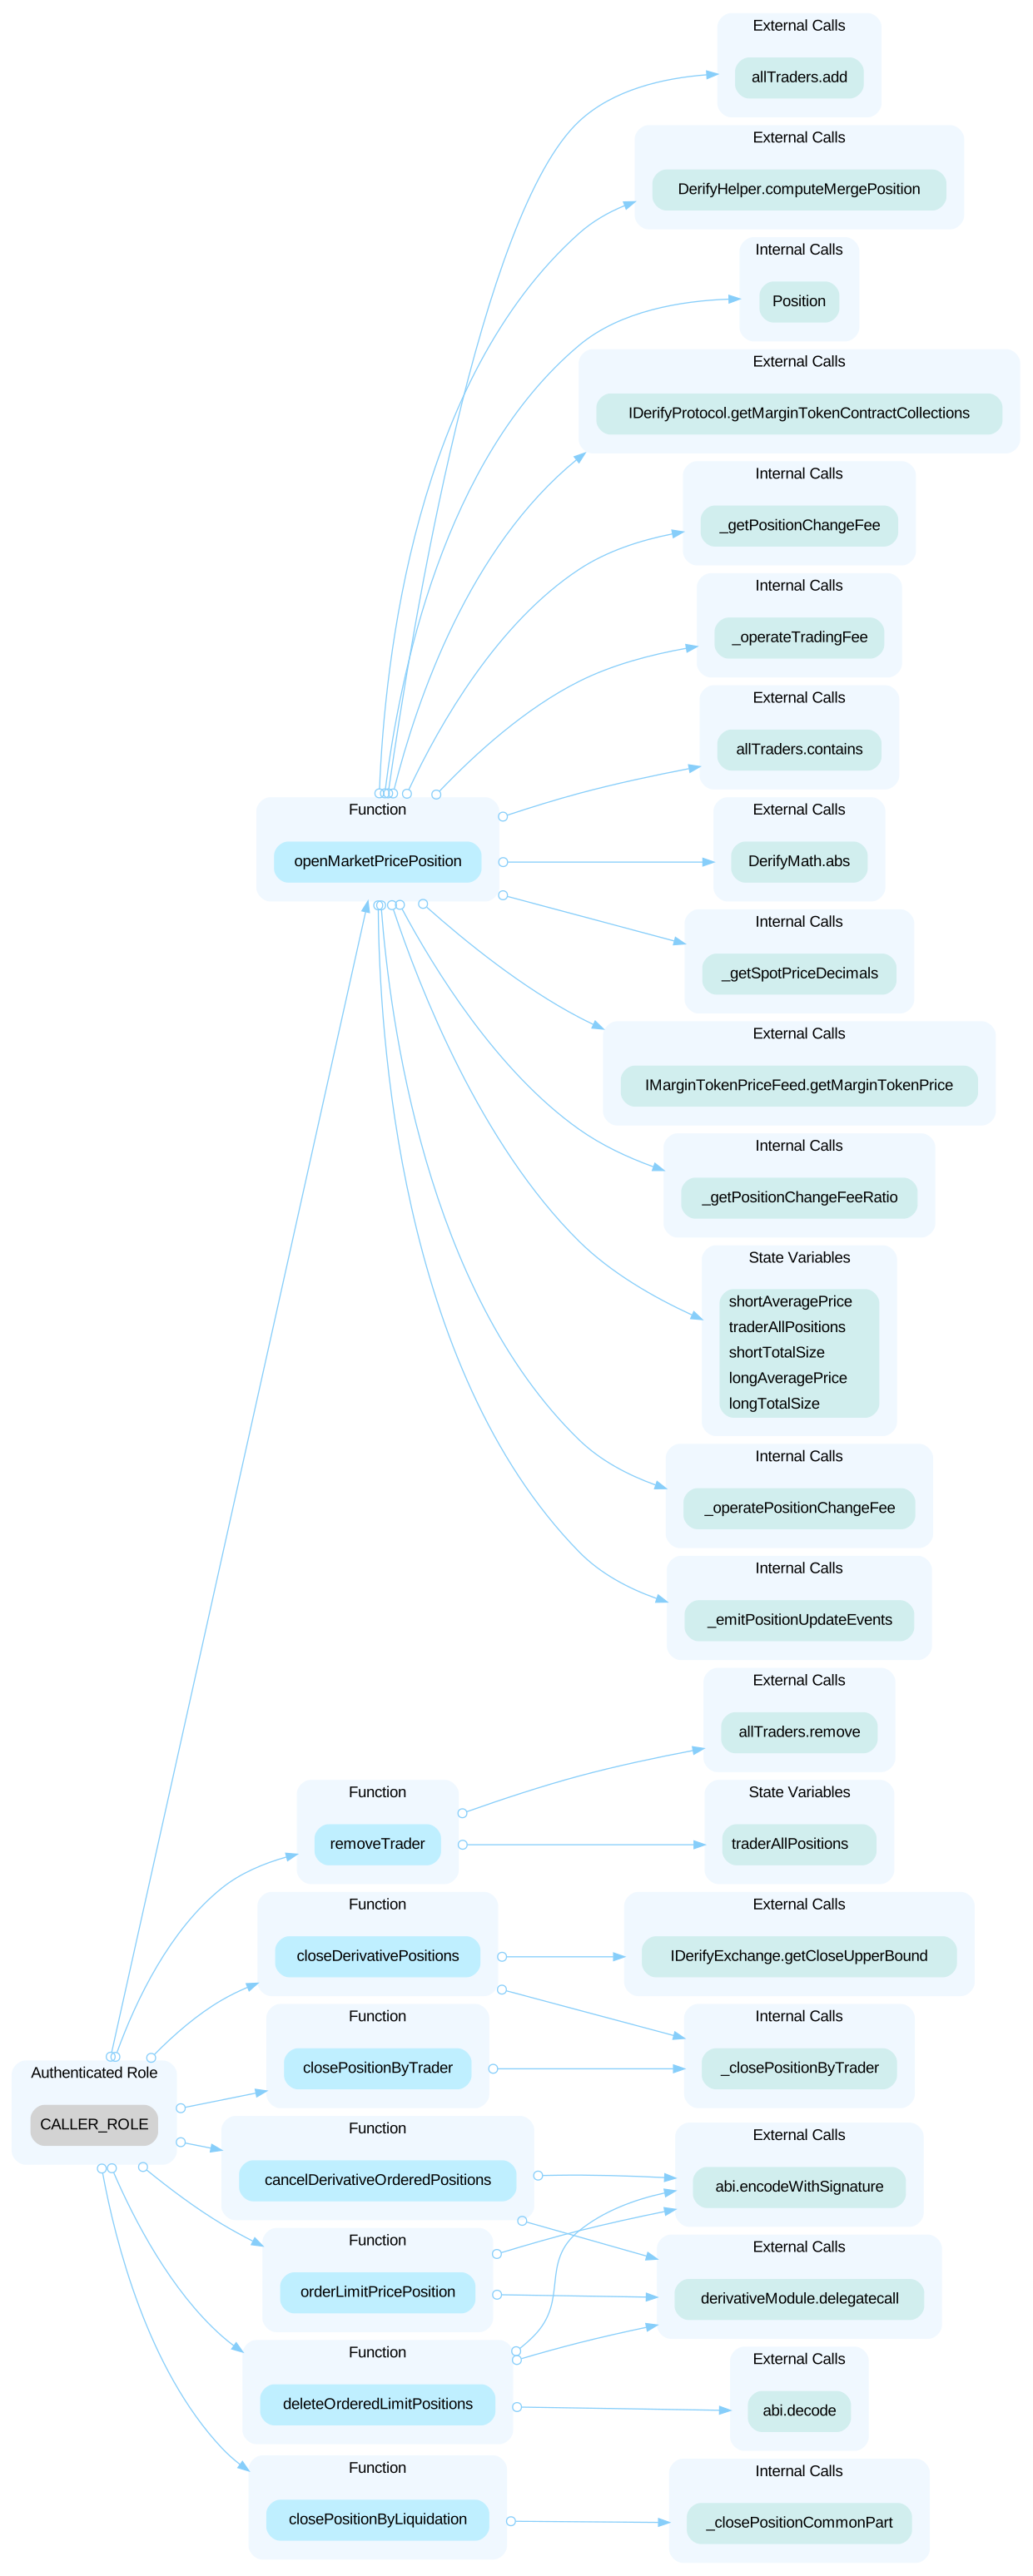 In the contract `DerifyDerivative`/ `DerifyDerivativeModule` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority: - initialize the contract - update the variable : - function lockDerivative(), to lock the price of the derivative. Any compromise to the `owner` account may allow the hacker to take advantage of this authority.
HighInsufficient Validation of Oracle DataAcknowledged
The `DerifyDerivative` contract does not check whether the price oracle returns non-zero value, nor the staleness of the data. Stale Oracle price can be caused by any issues with the Oracle provider. Thus, in the case that the Oracle returns an old price (which is incorrect at the moment of the request) this `price` will be valid and will lead to unexpected behavior. `latestRoundData` may return stale data, and there aren't any checks to ensure that this doesn't happen. This can be caused by any issues with Chainlink, such as oracle consensus problems or chain congestion, which may result in this contract relying on outdated data. **Notice**: The return data `answeredInRound`, which was previously used when answers could take multiple rounds to be computed, is deprecated. Its value is always equal to `roundId`. You can verify within the `OffchainAggregator.sol` contract specifically at L810 where the `latestRoundData()` function is defined.
MediumLack of reasonable lower and Upper LimitAcknowledged
There are no lower/upper boundaries when changing all the ratio in the function `updateParams()`.
MediumPotential Front-running Order Cancellation to AvoAcknowledged
Users are able to place multiple limit orders with gradually decreasing prices to open long positions. In the event of a significant and rapid market downturn, these users, by monitoring the mempool for any order operation transactions, may swiftly cancel the higher-priced orders that have become unfavorable compared to the current market price. This activity could disrupt the intended order execution flow . File: DerifyClearing.sol ```solidity=442 _getDerivative(token).openMarketPricePosition( IDerifyDerivative.TradeType.LimitPriceOpen, trader, theBroker, IDerifyDerivative.Side.LONG, executeSize, loops[k].price, loops[k].leverage ); operatedSize += executeSize; _getDerivative(token).deleteOrderedLimitPositions( trader, IDerifyDerivative.Side.LONG, k, executeSize, loops[k].price, loops[k].leverage, loops[k].timestamp ); ``` Front-running could happen as a result of: a) Oracle related issues: for instance, if oracle is missing an update for whatever reason or faces increased latency there is a risk of an arbitrager front-running the price feed and exploiting any differences with stale oracle price. b) MEV: even if oracle is functioning as designed, on Ethereum mainnet arbitragers could read mempool data and attempt to sandwich the price feed update by paying extra gas cost. Reference: https://chain.link/education-hub/maximal-extractable-value-mev
MediumThe oracle price feed will continue to report theAcknowledged
Chainlink aggregators have a built in circuit breaker if the price of an asset goes outside of a predetermined price band. The result is that if an asset experiences a huge drop in value (i.e. LUNA crash) the price of the oracle will continue to return the minPrice instead of the actual price of the asset. This would allow users to continue borrowing with the asset but at the wrong price. This is exactly what happened to [Venus on BSC when LUNA imploded](https://rekt.news/venus-blizz-rekt/). ChainlinkFeedRegistry#latestRoundData pulls the associated aggregator and requests round data from it. ChainlinkAggregators have minPrice and maxPrice circuit breakers built into them. This means that if the price of the asset drops below the minPrice, the protocol will continue to value the token at minPrice instead of it's actual value. This will allow users to take out huge amounts of bad debt and bankrupt the protocol.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (17)
- contracts/DerifyPmr.sol
- contracts/DerifyRewards.sol
- contracts/DerifyDerivative.sol
- contracts/DerifyClearing.sol
- contracts/DerifyRank.sol
- contracts/DeployDerifyFactory.sol
- contracts/DeployDerifyDerivative.sol
- contracts/DerifyDerivativeModule.sol
- contracts/DeployDerifyClearing.sol
- contracts/DeployDerifyExchange.sol
- contracts/DeployDerifyRewards.sol
- contracts/DerifyExchange.sol
- contracts/DerifyFactory.sol
- contracts/DerifyProtocol.sol
- contracts/DeployBMarginToken.sol
- contracts/DerifyExchangeModule.sol
- contracts/DerifyClearingModule.sol
Part of Derify protocol’s security record
 Derify protocol
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us