WaifuTv
CertiK reviewed WaifuTv on 31 Aug 2022: 33 findings, 0 critical; 10 marked fixed, 23 open.
The original report was removed from its address (seen 15 Oct 2026).
Trustblock does not review code.
Findings33
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 14 | 0 | 1 |
| Medium | 2 | 0 | 1 |
| Low | 7 | 0 | 8 |
HighCentralization Related Risks in `EarlyWaifuHolderOpen
In the contract `EarlyWaifuHolders`, the role `DEFAULT_ADMIN_ROLE` could reset the following privileged roles, any compromise to the `DEFAULT_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and grant the privileged roles. In the contract `EarlyWaifuHolders`, the role `MINTER_ROLE` has authority over the following functions: - function safeMintNext() - function safeMintNextBatch() Any compromise to the `MINTER_ROLE` account may allow a hacker to take advantage of this authority and mint tokens. In the contract `EarlyWaifuHolders`, the role `URI_SETTER_ROLE` has authority over the following functions: - function setRevealedURI() - function setUnrevealedURI() - function setIsRevealed() Any compromise to the `MINTER_ROLE` account may allow a hacker to take advantage of this authority and reveal the URI. In the contract `EarlyWaifuHolders`, the role `LIMITS_ADMIN_ROLE` has authority over the following functions: - function setTransfersEnabled() - function setAccountTransfersEnabled() Any compromise to the `LIMITS_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and enable the transfers. In the contract `EarlyWaifuHolders`, the role `ROYALTY_SETTER_ROLE` has authority over the following functions: - function setDefaultRoyalty Any compromise to the `ROYALTY_SETTER_ROLE` account may allow a hacker to take advantage of this authority and set the royalty. In the contract `EarlyWaifuHolders`, the role `PAUSER_ROLE` has authority over the following functions: - function pause() - function unpause() Any compromise to the `PAUSER_ROLE` account may allow a hacker to take advantage of this authority and pause the token transfer. In the contract `EarlyWaifuHolders`, the role `UPGRADER_ROLE` has authority over the following functions: - function _authorizeUpgrade() Any compromise to the `UPGRADER_ROLE` account may allow a hacker to take advantage of this authority and upgrade the contract implementation. In the contract `EarlyWaifuHolders`, the privileged role `TRANSFERER_ROLE` is authorized to transfer ERC721 Tokens. As the override of `_isApprovedOrOwner` in this contract, the spender has `TRANSFERER_ROLE` but not actually own the tokenId could also get `true` from `_isApprovedOrOwner`. Any compromise to the `UPGRADER_ROLE` account may allow a hacker to take advantage of this authority and transfer tokens belongs to the others.
HighCentralization Related Risks in `PreLaunchToken.sOpen
In the contract `WaifuToken`, the role `DEFAULT_ADMIN_ROLE` could reset the following privileged roles, any compromise to the `DEFAULT_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and grant the privileged roles. In the contract `PreLaunchToken`, the role `PRESALE_HELPER_ROLE` and `MINTER_ROLE` has authority over the following functions: - function mint() Any compromise to the `PRESALE_HELPER_ROLE` and `MINTER_ROLE` accounts may allow a hacker to take advantage of this authority and mint tokens. In the contract `PreLaunchToken`, the role `CASHIER_ROLE` has authority over the following functions: - function mint() Any compromise to the `CASHIER_ROLE` accounts may allow a hacker to take advantage of this authority and withdraw for waifuToken from the other's balance. In the contract `PreLaunchToken`, the role `TOKEN_SETTER_ROLE` has authority over the following functions: - function setMainToken() Any compromise to the `PRESALE_HELPER_ROLE` and `MINTER_ROLE` accounts may allow a hacker to take advantage of this authority and set the main token address. In the contract `PreLaunchToken`, the role `UPGRADER_ROLE` has authority over the following functions: - function _authorizeUpgrade() Any compromise to the `UPGRADER_ROLE` accounts may allow a hacker to take advantage of this authority and upgrade contract implementations.
HighCentralization Related Risks in `PresaleHelper.soOpen
In the contract `WaifuManager`, the role `DEFAULT_ADMIN_ROLE` could reset the following privileged roles, any compromise to the `DEFAULT_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and grant the privileged roles. In the contract `WaifuManager`, the role `LIMITS_ADMIN_ROLE` has authority over the following functions: - function setPurchaseAllowed() - function setPurchaseAllowedBatch() Any compromise to the `LIMITS_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and set the node tiers. In the contract `WaifuManager`, the role `UPGRADER_ROLE` has authority over the following functions: - function _authorizeUpgrade() Any compromise to the `UPGRADER_ROLE` account may allow a hacker to take advantage of this authority and upgrade the contract implementation.
HighCentralization Related Risks in `RevenuePaymentSpOpen
In the contract `EarlyWaifuHolders`, the role `UPGRADER_ROLE` has authority over the following functions: - function _authorizeUpgrade() Any compromise to the `UPGRADER_ROLE` account may allow a hacker to take advantage of this authority and upgrade the contract implementation.
HighCentralization Related Risks in `WaifuCashier.solOpen
In the contract `WaifuCashier`, the role `DEFAULT_ADMIN_ROLE` could reset the following privileged roles, and the following functions: - function setFees() Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow a hacker to take advantage of this authority, grant the privileged roles, and set fees. In the contract `WaifuCashier`, the role `PAYMENT_MANAGER_ROLE` could reset the following privileged roles, and the following functions: - function getPaymentFrom() - function makePaymentTo() - function grantRewardsFor() Any compromise to the `PAYMENT_MANAGER_ROLE` account may allow a hacker to take advantage of this authorization and manage the payments. In the contract `WaifuCashier`, the role `FEES_ADMIN_ROLE` has authority over the following functions: - function setRevenuePool() - function function setTreasury() - function setCompanyWallet() - function setEscrowWallet() - function setRouter() Any compromise to the `FEES_ADMIN_ROLE` account may allow a hacker to take advantage of this authority, set the revenue pool, set the router, and set the wallet addresses. In the contract `WaifuCashier`, the role `PAUSER_ROLE` has authority over the following functions: - function pause() - function unpause() Any compromise to the `PAUSER_ROLE` account may allow a hacker to take advantage of this authority and pause the transfer. In the contract `WaifuCashier`, the role `UPGRADER_ROLE` has authority over the following functions: - function _authorizeUpgrade() Any compromise to the `UPGRADER_ROLE` account may allow a hacker to take advantage of this authority and upgrade the contract implementation.
HighCentralization Related Risks in `WaifuManager.solOpen
In the contract `WaifuManager`, the role `DEFAULT_ADMIN_ROLE` could reset the following privileged roles, any compromise to the `DEFAULT_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and grant the privileged roles. In the contract `WaifuManager`, the role `NODES_ADMIN_ROLE` has authority over the following functions: - function addNewCapacityTier() - function addNewNodeTier() Any compromise to the `NODES_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and set the node tiers. In the contract `WaifuManager`, the role `FINANCE_ADMIN_ROLE` has authority over the following functions: - function setNodePrices() - function addNewEpoch() Any compromise to the `FINANCE_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and set the price & epoch. In the contract `WaifuManager`, the role `PAUSER_ROLE` has authority over the following functions: - function pause() - function unpause() Any compromise to the `PAUSER_ROLE` account may allow a hacker to take advantage of this authority and pause the transfer. In the contract `WaifuManager`, the role `UPGRADER_ROLE` has authority over the following functions: - function _authorizeUpgrade() Any compromise to the `UPGRADER_ROLE` account may allow a hacker to take advantage of this authority and upgrade the contract implementation.
HighCentralization Related Risks in `WaifuNodes.sol`Open
In the contract `WaifuNodes`, the role `DEFAULT_ADMIN_ROLE` could reset the following privileged roles, any compromise to the `DEFAULT_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and grant the privileged roles. In the contract `WaifuNodes`, the role `MANAGER_ROLE` has authority over the following functions: - function mint() - function mingBatch() - function upgradeNodesFor() - function upgradeNodesBatchFor() - function clearHistoryFor() Any compromise to the `LIMITS_ADMIN_ROLE` account may allow a hacker to take advantage of this authority, mint tokens, and upgrade node tiers. In the contract `WaifuNodes`, the role `LIMITS_ADMIN_ROLE` has authority over the following functions: - function setWalletLimit() - function setTransfersEnabled() Any compromise to the `LIMITS_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and set the transfer restrictions. In the contract `WaifuNodes`, the role `URI_SETTER_ROLE` has authority over the following functions: - function setURI() Any compromise to the `URI_SETTER_ROLE` account may allow a hacker to take advantage of this authority and set the token URI. In the contract `WaifuNodes`, the role `PAUSER_ROLE` has authority over the following functions: - function pause() - function unpause() Any compromise to the `PAUSER_ROLE` account may allow a hacker to take advantage of this authority and pause the transfer. In the contract `WaifuNodes`, the role `UPGRADER_ROLE` has authority over the following functions: - function _authorizeUpgrade Any compromise to the `UPGRADER_ROLE` account may allow a hacker to take advantage of this authority and upgrade the contract implementation.
HighCentralization Related Risks in `WaifuPerks.sol`Open
In the contract `WaifuPerks`, the role `DEFAULT_ADMIN_ROLE` could reset the following privileged roles, any compromise to the `DEFAULT_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and grant the privileged roles. In the contract `WaifuPerks`, the role `URI_SETTER_ROLE` has authority over the following functions: - function setURI() Any compromise to the `URI_SETTER_ROLE` account may allow a hacker to take advantage of this authority and set the token URI. MINTER_ROLE In the contract `WaifuPerks`, the role `MINTER_ROLE` has authority over the following functions: - function mint() - function mintBatch() Any compromise to the `MINTER_ROLE` account may allow a hacker to take advantage of this authority and mint the token. In the contract `WaifuPerks`, the role `BURNER_ROLE` has authority over the following functions: - function burn() - function burnBatch() Any compromise to the `BURNER_ROLE` account may allow a hacker to take advantage of this authority and burn the other's token.
HighCentralization Related Risks in `WaifuToken.sol`Open
In the contract `WaifuToken`, the role `DEFAULT_ADMIN_ROLE` could reset the following privileged roles, any compromise to the `DEFAULT_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and grant the privileged roles. In the contract `WaifuToken`, the role `MINTER_ROLE` has authority over the following functions: - function mint() Any compromise to the `MINTER_ROLE` account may allow a hacker to take advantage of this authority and mint the token. In the contract `WaifuToken`, the role `BURNER_ROLE` has authority over the following functions: - function burnFrom() Any compromise to the `BURNER_ROLE` account may allow a hacker to take advantage of this authority and burn tokens from others. In the contract `WaifuToken`, the role `LIMITS_ADMIN_ROLE` has authority over the following functions: - function setTotalWalletLimit() - function setWalletTransferLimitDuration() - function setWalletTransferLimitPercentage() - function setWalletLimitDisabled() Any compromise to the `LIMITS_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and set the wallet limitations. In the contract `WaifuToken`, the role `UPGRADER_ROLE` has authority over the following functions: - function _authorizeUpgrade() Any compromise to the `UPGRADER_ROLE` account may allow a hacker to take advantage of this authority and upgrade the contract implementations.
HighCentralization Risks in PancakeFactory.solOpen
In the contract `PancakeFactory` the role `feeToSetter` has authority over the functions shown in the diagram below. Any compromise to the `feeToSetter` account may allow the hacker to take advantage of this authority and set the feeto address. 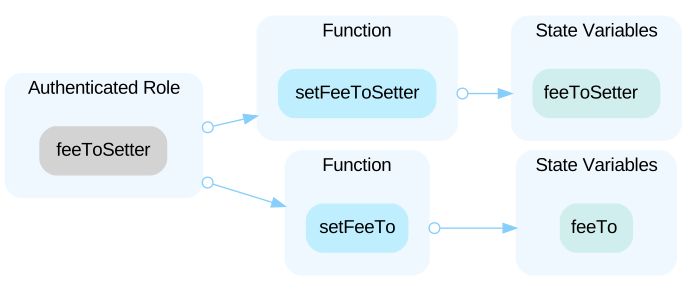
Show 10 more
HighCentralization Risks in PerkSaleHelper.solOpen
In the contract `PerkSaleHelper` the role `PRICE_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `PRICE_ADMIN_ROLE` account may allow the hacker to take advantage of this authority, set the sale/presale price, and end the presale. - `function finishPresale()` - `function setTypePrice()` - `function setTypePresalePrice()` In the contract `PerkSaleHelper` the role `UPGRADER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `UPGRADER_ROLE` account may allow the hacker to take advantage of this authority and upgrade the implementation. - `function _authorizeUpgrade()`
HighCentralized Control of Contract UpgradeOpen
Waifulab contracts are upgradeable contracts, the owner can upgrade the contract without the community's consensus. If an attacker compromises the account, the attacker can change the implementations of the contracts and drain tokens from the contracts.
HighCentralized Risk in `addLiquidity()`Open
```solidity=374 router.addLiquidity( address(wbnb), address(waifuToken), waifuBalance, wbnbBalance, 0, 0, treasury, block.timestamp ); ``` The `_addLiquidity` function calls the `addLiquidity` function of pancakeswapRouter with the `to` address specified as `treasury` for acquiring the generated LP tokens from the `WaifuToken-WBNB` pool. As a result, over time the `treasury` address will accumulate a significant portion of LP tokens. If the `treasury` is an EOA (Externally Owned Account), mishandling of its private key can have devastating consequences to the project as a whole.
HighFee DistributionOpen
There are 3 kinds of fee in contract WaifuCashier. - treasuryFee - companyFee - escrowFee The `_liquidate` function will liquidify to the corresponding `PancakePair` with the Waifu and WBNB balances, while the owner can transfer the balance of WBNB, which swapped from Waifu to `treasury`, `companyWallet`, and `escrowWallet`.
MediumMissing Token ID Checks When Adding SharesOpen
In the `initialize` function of contract `RevenuePaymentSplitter`, a payee will be created for each token ID with shares. But the contract did not check if the NFT token ID existed. The initialized share by the burned token will take the release as well.
MediumPotential Sandwich AttacksOpen
A sandwich attack might happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by front-running (before the transaction being attacked) a transaction to purchase one of the assets and make profits by back running (after the transaction being attacked) a transaction to sell the asset. The following functions are called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large: - `PancakeRouter.addLiquidity()` - `PancakeRouter.swapExactTokensForTokens()`
LowDirectly Delete From Array By IndexOpen
In Solidity, deleting an element by index from an array would cause a gap in the array storage, and the array length would not change.
LowInconsistent `DEFAULT_ADMIN_ROLE` AssignmentOpen
In the contract `PreLaunchToken`, the `DEFAULT_ADMIN_ROLE` will be re-assigned to the caller of function `initialize()`. The other contracts do not have implementations like this. ```solidity=63 if (admin != _msgSender()) { _grantRole(DEFAULT_ADMIN_ROLE, _msgSender()); } ``` It's not reasonable to overwrite the input admin address because it would mislead the contract deployer to get an unexpected deployment.
LowMissing Input ValidationOpen
The linked variables in the "Locations" section are missing input validation, which means the essential variables can be `address(0)`, `0`, or some other invalid values.
LowNot Recommended MetadataURI ProtocolOpen
HTTP/HTTPS should not be used for token metadata because the domain and web server owner can change token metadata at will to dramatically affect token value.
Show 3 more
LowStorage Manipulation In `view` FunctionsOpen
Storage Manipulation In `view` Functions There should not be any storage variable manipulation in the `view` function.
LowThird Party DependenciesOpen
The contract is serving as the underlying entity to interact with third party Pancakeswap protocols. The scope of the audit treats 3rd party entities as black boxes and assume their functional correctness. However, in the real world, 3rd parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of 3rd parties can possibly create severe impacts, such as increasing fees of 3rd parties, migrating to new LP pools, etc.
LowUnused `_snapshot()` FunctionOpen
The function `_snapshot()` in contract `ERC1155TempBalanceHistoryUpgradeable` has `internal` visibility, and it is never used.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (13)
- PresaleHelper.sol
- WaifuToken.sol
- LiquidityManager.sol
- extensions/ERC1155TempBalanceHistoryUpgradeable.sol
- WaifuPerks.sol
- extensions/ERC1155AggregateSupplyUpgradeable.sol
- WaifuCashier.sol
- WaifuManager.sol
- RevenuePaymentSplitter.sol
- PreLaunchToken.sol
- EarlyWaifuHolders.sol
- WaifuNodes.sol
- PerkSaleHelper.sol
Part of WaifuTv’s security record
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us