Satoshiscloset Wallet
CertiK reviewed Satoshi's Closet (Satoshiscloset Wallet) on 21 Nov 2022: 10 findings, 0 critical; 5 marked fixed, 5 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings10
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 5 | 0 | 5 |
LowApplication uses v1 signature scheme (Janus AttacFixed
The application is signed with v1 signature scheme, making it vulnerable to Janus vulnerability on Android <7.0 The Janus vulnerability stems from the possibility to add extra bytes to APK files and to DEX files. On the one hand, an APK file is a zip archive, which can contain arbitrary bytes at the start, before its zip entries (actually more generally, between its zip entries). The JAR signature scheme only takes into account the zip entries. It ignores any extra bytes when computing or verifying the application’s signature. On the other hand, a DEX file can contain arbitrary bytes at the end, after the regular sections of strings, classes, method definitions, etc. A file can, therefore, be a valid APK file and a valid DEX file at the same time. References: - https://www.xda-developers.com/janus-vulnerability-android-apps/ - https://medium.com/mobis3c/exploiting-apps-vulnerable-to-janus-cve-2017-13156-8d52c983b4e0
LowCustom Keyboards Allowed for Sensitive InputsFixed
The WLT mobile application does not disable custom keyboards when entering wallet mnemonics. Since a long time ago, users have been able to install custom keyboards that can be used in any app, replacing the system's default keyboard. Custom keyboards can, and very frequently do, log and exfiltrate the data users enter. The following screenshot shows the input of the mnemonic using the third party keyboard SwiftKey. 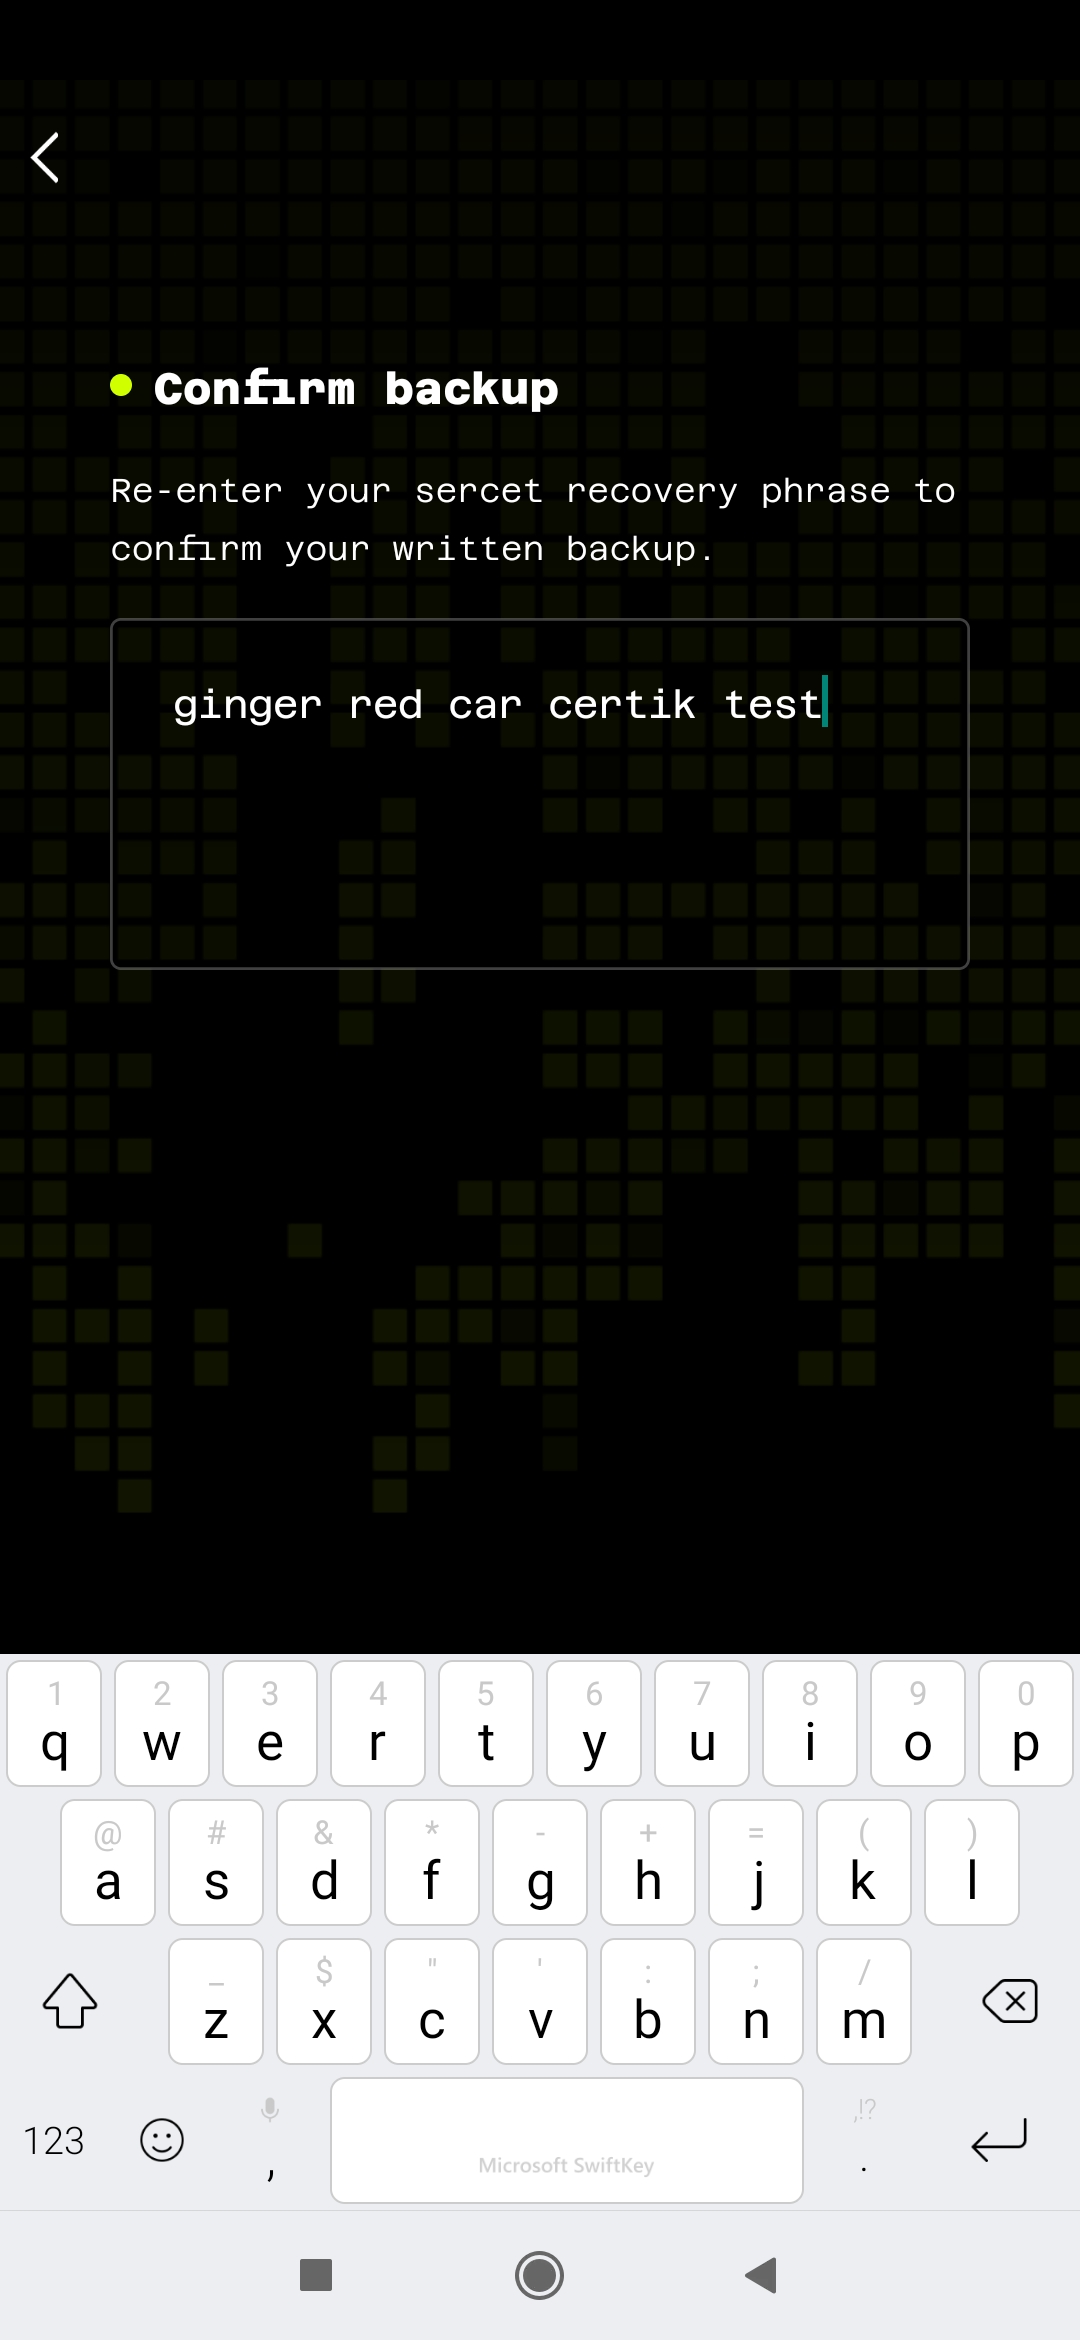
LowMnemonic Display Allow ScreenshotsFixed
The mnemonic phrase is a list of words that can be used to recover a wallet account. The application does not have a mechanism in place to stop a user from taking a screenshot of the displayed wallet secrets. This finding has been rated as low risk because the applications displays a warning to remind the user of the risk of taking a screenshot. 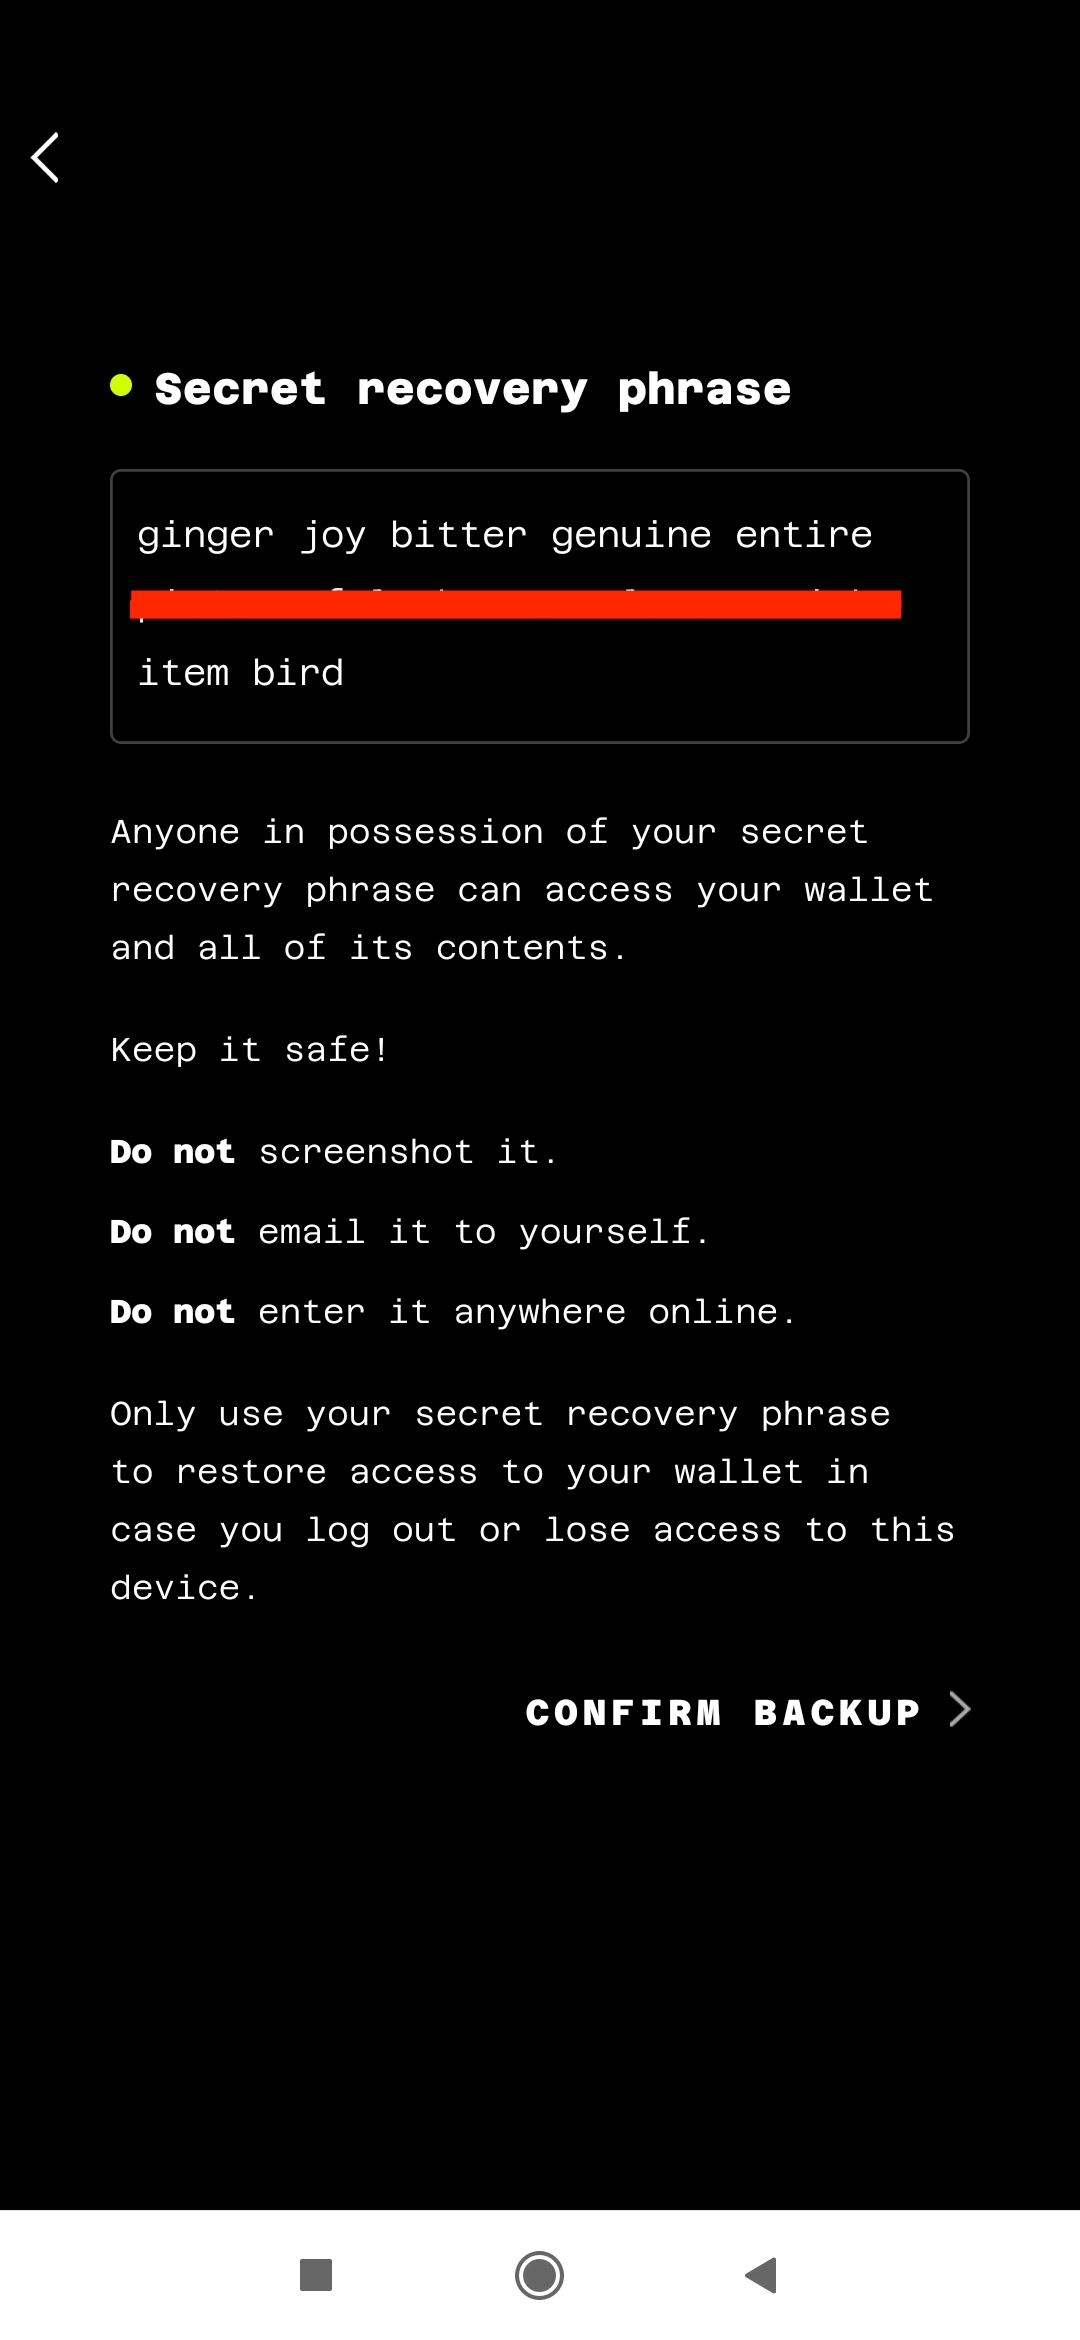
LowNo Root or Jailbreak DetectionFixed
No root or jailbreak detection is implemented in the application.
LowScreenshot BackgroundingFixed
On mobile devices, a screenshot of the current activity is taken when an application goes into the background and displayed for aesthetic purposes when the app returns to the foreground. This feature may pose a security risk. Sensitive data may be exposed if the user background the application while sensitive data is displayed. A malicious application that is running on the device and able to continuously capture the screen may also expose data. 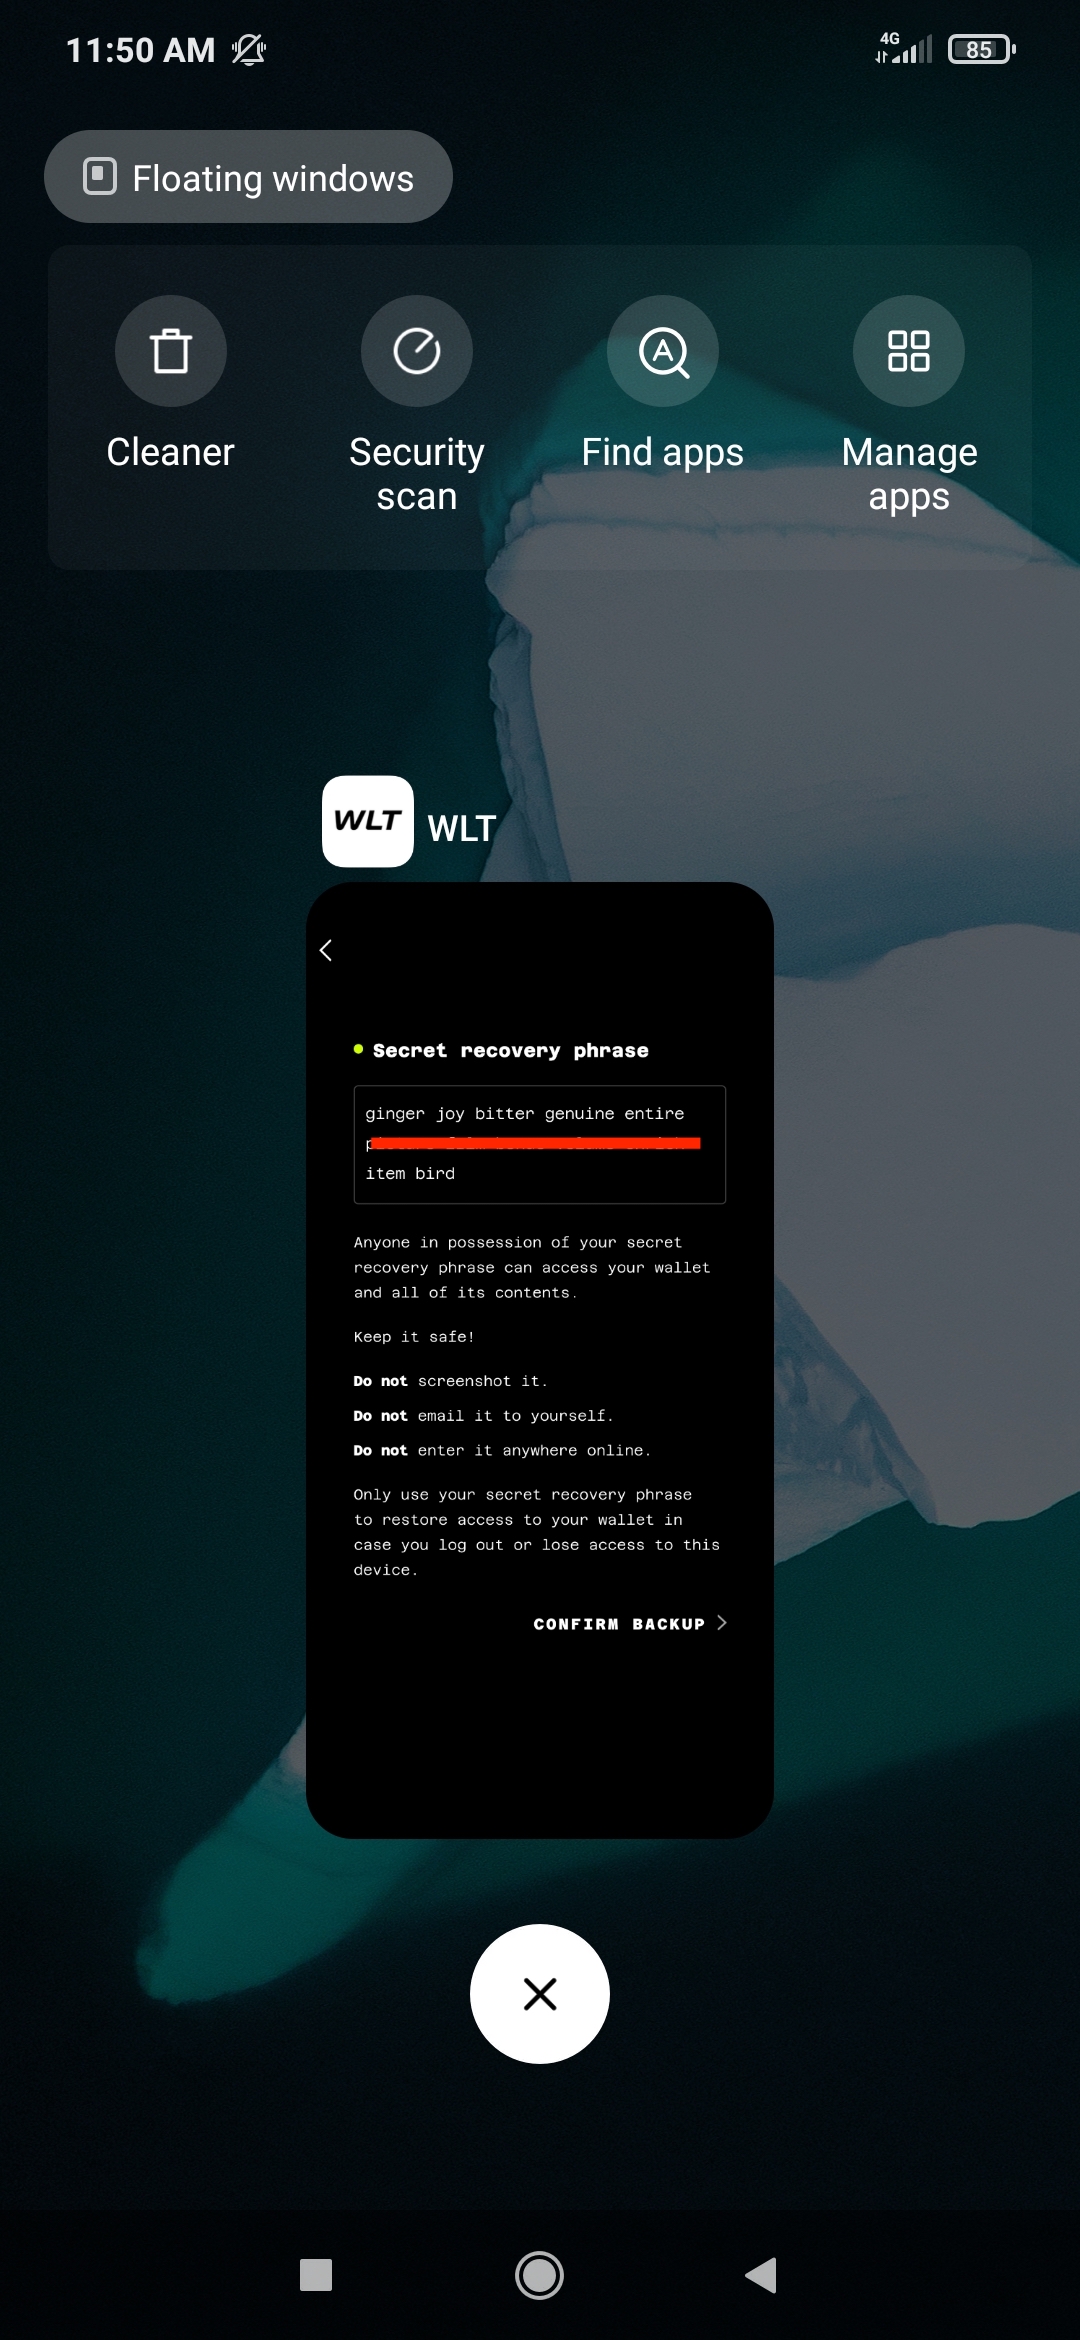
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Part of Satoshi's Closet’s security record
 Satoshi's Closet
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us