Wemix Retainer 28 (NILE NFT-Fi)
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 28 (NILE NFT-Fi)) on 19 Jun 2023: 19 findings, 0 critical; 12 marked fixed, 7 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings19
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 5 | 0 | 12 |
HighCentralization Related RisksOpen
In the contract `ERC20WhiteList` the role `_admin` has authority over the functions shown in the diagram below. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and add/remove whitelisted ERC20 tokens and update `addressManager`. 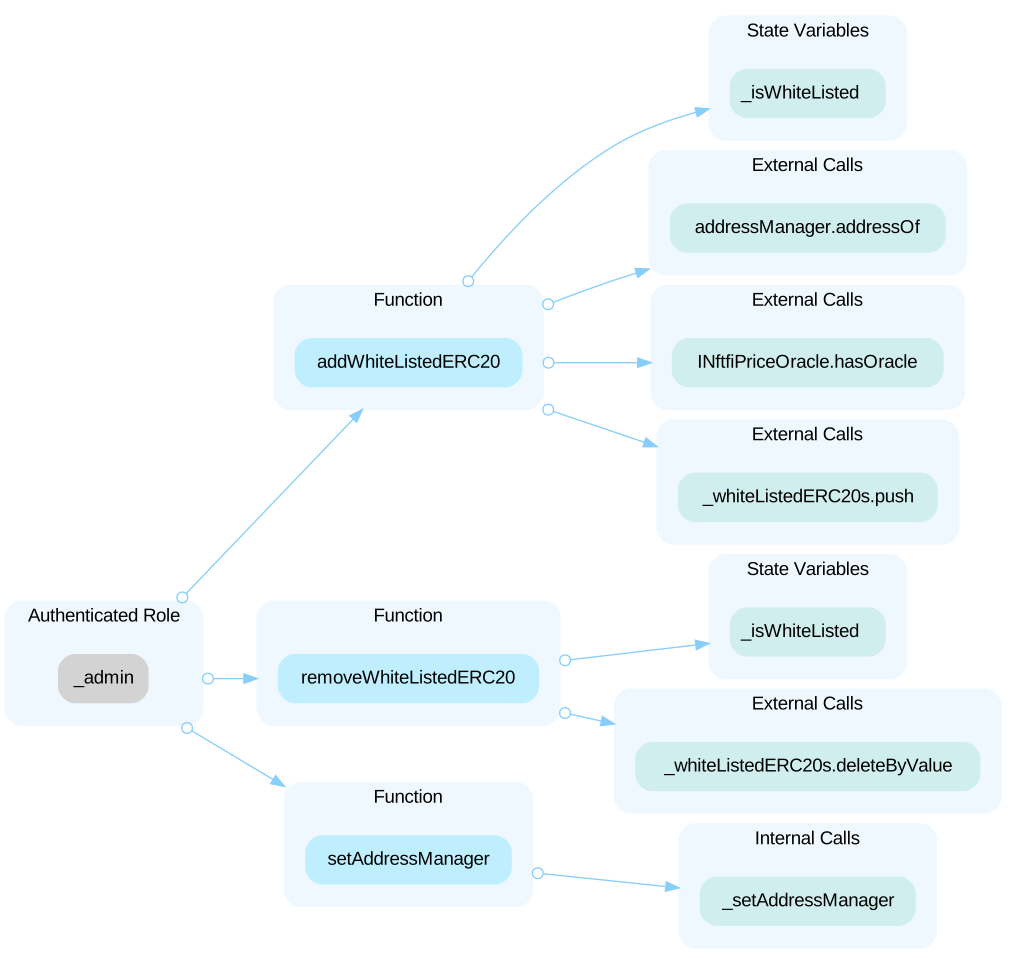 In the contract `LoanAuctionBase` the role `_admin` has authority over the following functions: - addAllowedAuctionDuration() - removeAllowedAuctionDuration() - pause() - unpause() - setExtendDurationFromLastBidding() - setDefaultLoanDuration() - setTimeToBorrowerFeeDenominator() - setLenderFeeRateMantissa() - setFeeToken() - setFeeWallet() Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and modify important variables, pause/unpause transactions, and set critical variables. In the contract `NFTWhiteList` the role `_admin` has authority over the functions shown in the diagram below. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and add/remove whitelisted NFTs. 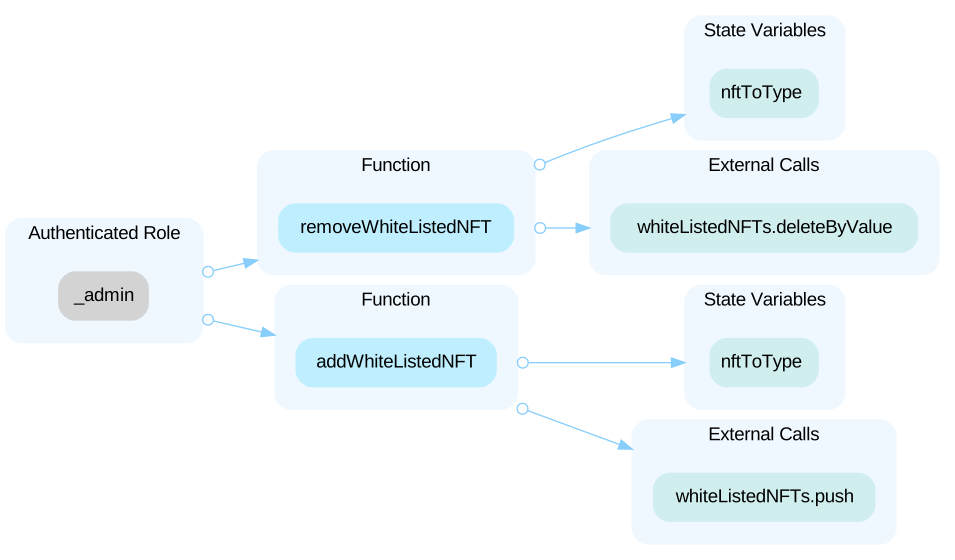 In the contract `NftfiPriceOracle` the role `_admin` has authority over the functions shown in the diagram below. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and add/remove price oracles. 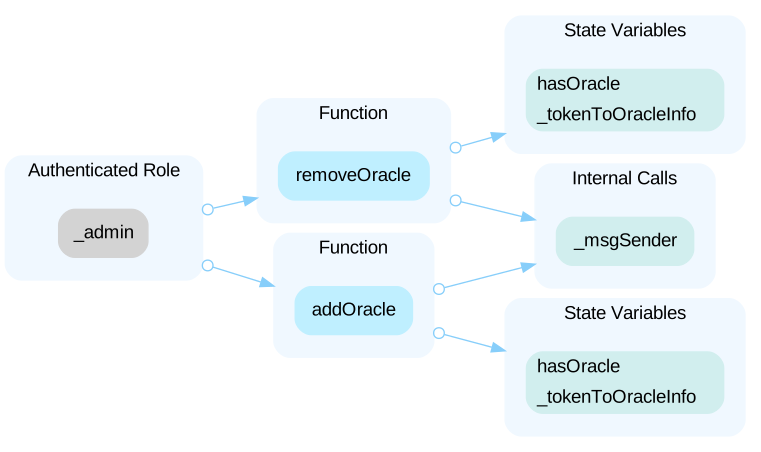 In the contract `AddressManager` the role `_admin` has authority over the following functions: - setAddressOf() - setAllAddressOf() - removeAddressOf() Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and set critical variables. In the contract `Admin` the role `_admin` has authority over the function shown in the diagram below. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority and transfer the admin role. 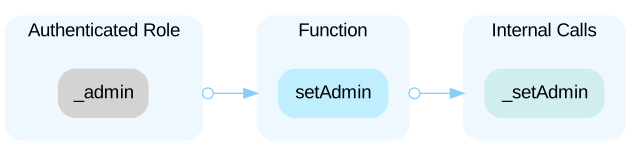 In the contract `FixedSwapPath` the role `_owner` has authority over the function shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set the role `setterManager`. 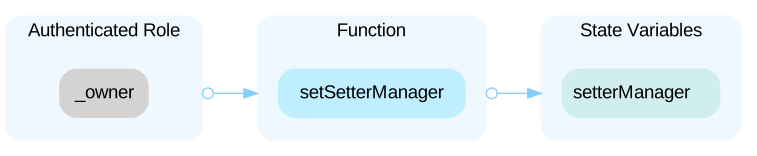 In the contract `FixedSwapPath` the role `setterManager` has authority over the function shown in the diagram below. Any compromise to the `setterManager` account may allow the hacker to take advantage of this authority and set the role `swapInfoSetter`. 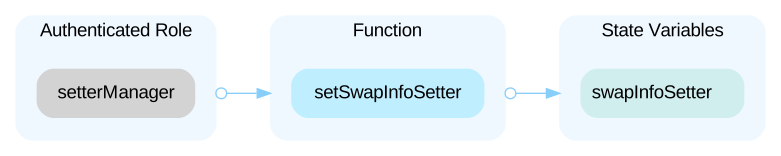 In the contract `FixedSwapPath` the role `swapInfoSetter` has authority over the functions shown in the diagram below. Any compromise to the `swapInfoSetter` account may allow the hacker to take advantage of this authority and modify the `swapInfos` mapping. 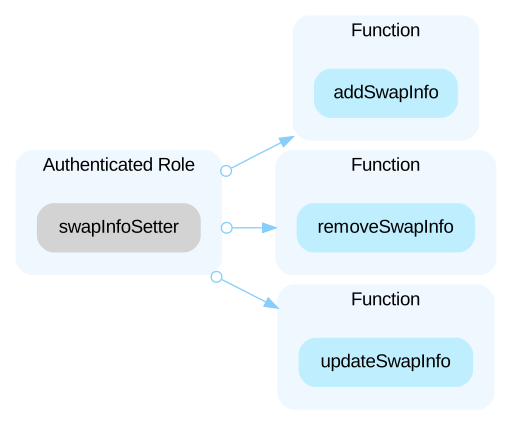 In the contract `OwnableUpgradeable` the role `_owner` has authority over the following functions: - transferOwnership() - renounceOwnership() Any compromise to the `setterManager` account may allow the hacker to take advantage of this authority and transfer or renounce the ownership.
HighCentralized Control of Contract UpgradeOpen
The following contracts are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can modify the implementation in a manner detrimental to the tokenomics. For instance, he could drain tokens from the contracts. - NfiFiHelper - WeswapV2Router - ERC20WhiteList - LoanAuctionFixedInterest - NFTWhiteList - NftfiPriceOracle - AddressManager
LowIncompatibility With Deflationary TokensOpen
When transferring standard ERC20 deflationary tokens, the input amount may not be equal to the received amount due to the charged transaction fee.
LowInconsistency Between Comments and CodeOpen
In the function `LoanAuctionBase._checkListTerms()`, the provided comments suggest that the annual percentage rate (APR) should be set at no less than 20% of the borrowed amount. This implies that `listTerms.maxRepayAmount >= 1.2 * listTerms.principalAmount`. However, this is not the condition currently checked in the code. Instead, it only requires `listTerms.maxRepayAmount >= listTerms.principalAmount`, potentially allowing APR to be set lower than 20%. Additionally, comments in the `ListTerms` struct indicate that setting `loanDuration` as 0 should utilize the default loan duration stored in the contract. However, this condition is not implemented in the `LoanAuctionBase.listLoan()` function, as `ListTerms.loanDuration` attribute is not used. Lastly, the comments in the function `LoanAuctionBase.repayLoan()` suggest that only the borrower should be able to repay the loan. However, the code itself does not enforce this restriction, potentially allowing anyone to repay the loan.
LowPossible Out-of-scope DependenciesOpen
The following contracts are not in the audit scope: - pair - factory The audit treats them as black boxes and assumes their functional correctness. However, in the real world, they can be compromised and this may lead to lost or stolen assets. Addtionally, in the current code, the init code of the pair contract does not match it in the latest [WeswapLibrary.sol](https://github.com/wemixarchive/weswap-periphery/blob/13b27ea93db764952934e1270c0fc1482ff01d02/contracts/libraries/WeswapLibrary.sol) file or the audited version. As such, we would like the client to confirm whether the current state of the code is indeed correct.
LowThird-Party DependenciesOpen
The contract is serving as the underlying entity to interact with third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. The third parties include: - price oracles - ERC20 tokens - ERC721 tokens - ERC1155 tokens
LowUnreasonable or Missing Upper Limit in `setTimeToOpen
There is no upper boundary for `setLenderFeeRateMantissa()` which is used to set fee rates. It is possible to set the lender fee rate up to any arbitrary amount. The `setTimeToBorrowerFeeDenominator()` function may not have a reasonable upper limit and can be used to set the borrower fee up to 100%.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (36)
- IERC20WhiteList.sol
- swap-helper-main/contracts/path/FixedSwapPath.sol
- swap-helper-main/contracts/interfaces/INFTWhiteList.sol
- IFixedSwapPath.sol
- swap-helper-main/contracts/helpers/SwapHelper.sol
- swap-helper-main/contracts/interfaces/IAddressManager.sol
- swap-helper-main/contracts/interfaces/IWeswapPair.sol
- swap-helper-main/contracts/helpers/NFTReceiverUpgradeable.sol
- IWeswapRouter.sol
- NftfiPriceOracle.sol
- swap-helper-main/contracts/libraries/WeswapLibrary.sol
- IDataCollector.sol
- swap-helper-main/contracts/interfaces/IFixedSwapPath.sol
- NFTReceiver.sol
- Strings.sol
- ERC20WhiteList.sol
- LoanAuctionFixedInterest.sol
- swap-helper-main/contracts/interfaces/ILoanAuctionFixedInterest.sol
- swap-helper-main/contracts/routers/WeswapV2Router.sol
- swap-helper-main/contracts/interfaces/LoanStruct.sol
- INFTWhiteList.sol
- ILoanAuctionBase.sol
- LoanAuctionBase.sol
- swap-helper-main/contracts/libraries/TransferHelper.sol
- NFTWhiteList.sol
- IAddressManager.sol
- LoanStruct.sol
- Array.sol
- swap-helper-main/contracts/interfaces/ISwapRouter.sol
- ISwapRouter.sol
- swap-helper-main/contracts/interfaces/IWWEMIX.sol
- INftfiPriceOracle.sol
- swap-helper-main/contracts/helpers/NfiFiHelper.sol
- Admin.sol
- swap-helper-main/contracts/interfaces/IWeswapRouter.sol
- AddressManager.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us