The Karma Pad - Audit
CertiK reviewed Karma (The Karma Pad - Audit) on 18 Oct 2023: 16 findings, 0 critical; 11 marked fixed, 5 acknowledged.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings16
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 3 | 2 |
| Medium | 0 | 0 | 6 |
| Low | 0 | 2 | 3 |
HighCentralization Related RisksAcknowledged
In the contract `ReflectionToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 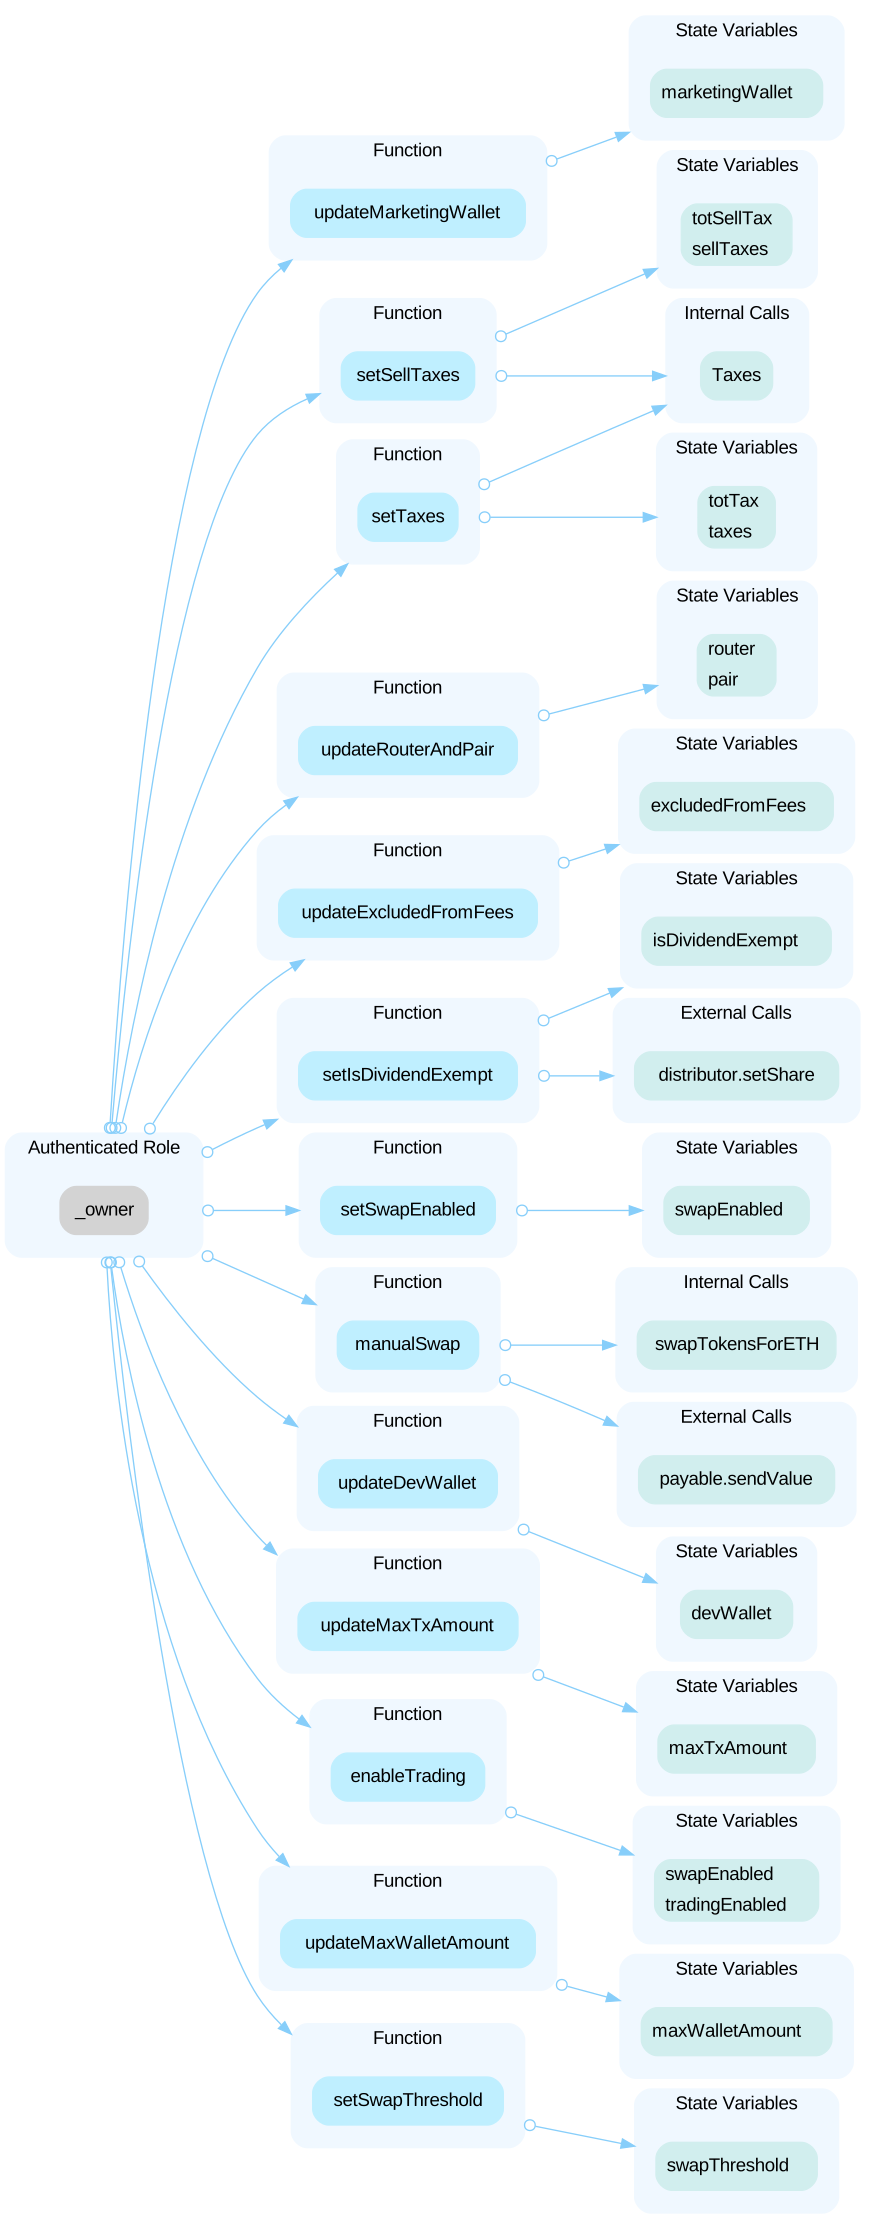 In the contract `ReflectionToken` the role `karmaDeployer` has authority over the functions shown in the diagram below. Any compromise to the `karmaDeployer` account may allow the hacker to take advantage of this authority. 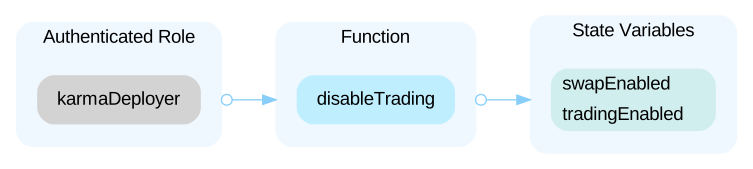 In the contract `BaseToken` the role `deployer` has authority over the functions shown in the diagram below. Any compromise to the `deployer` account may allow the hacker to take advantage of this authority. 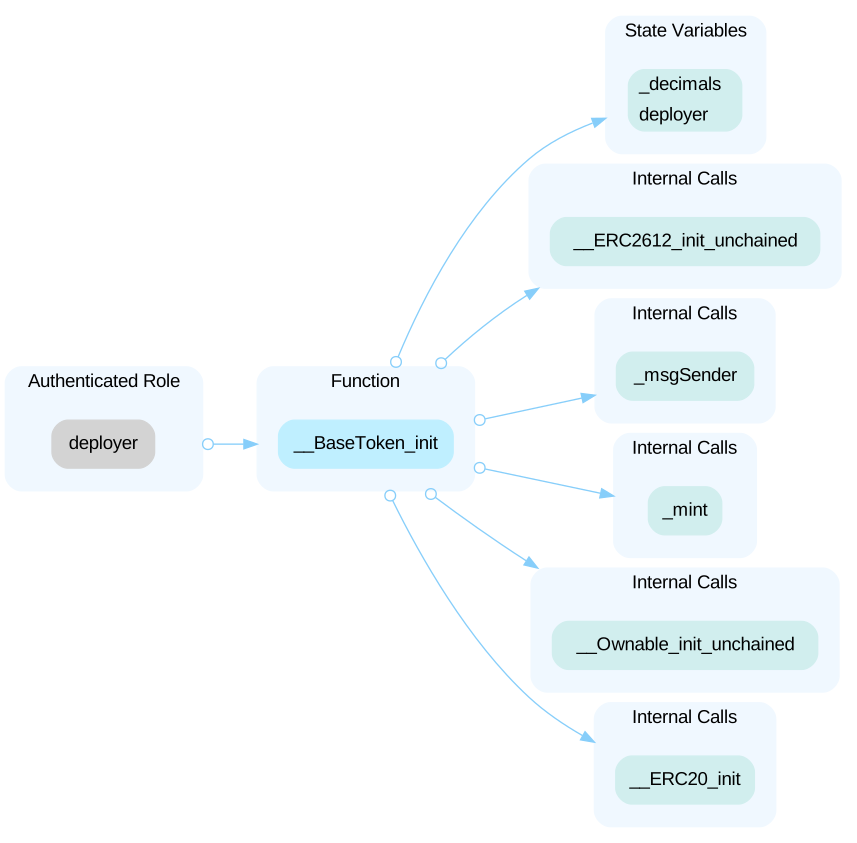 In the contract `StandardToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 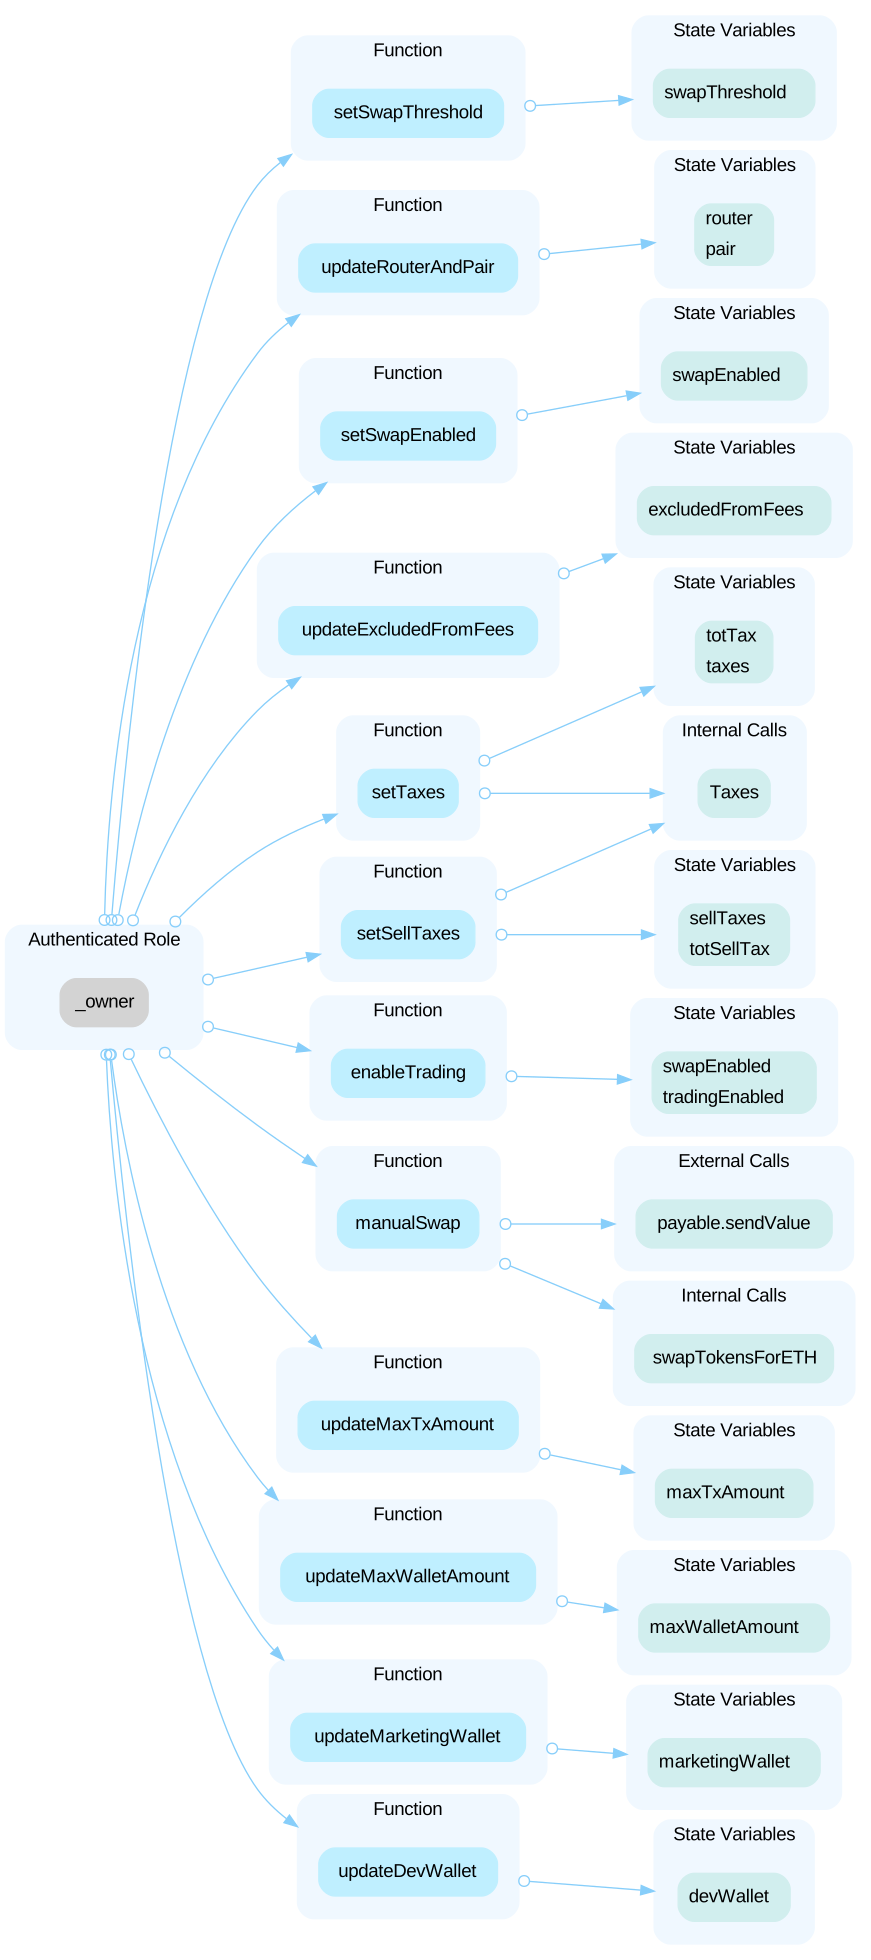 In the contract `StandardToken` the role `karmaDeployer` has authority over the functions shown in the diagram below. Any compromise to the `karmaDeployer` account may allow the hacker to take advantage of this authority. 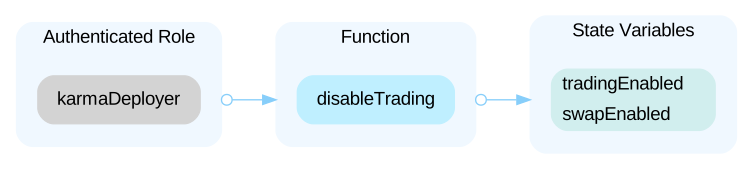 In the contract `Token` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 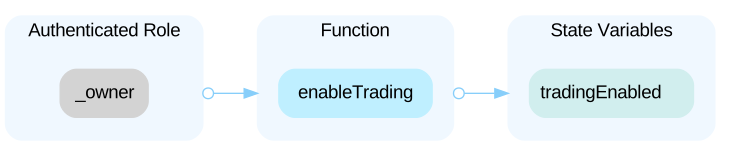 In the contract `Token` the role `karmaDeployer` has authority over the functions shown in the diagram below. Any compromise to the `karmaDeployer` account may allow the hacker to take advantage of this authority. 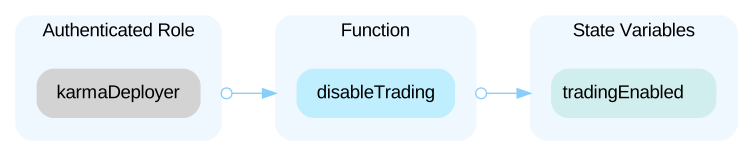 In the contract `DividendDistributor` the role `_token` has authority over the functions shown in the diagram below. Any compromise to the `_token` account may allow the hacker to take advantage of this authority. 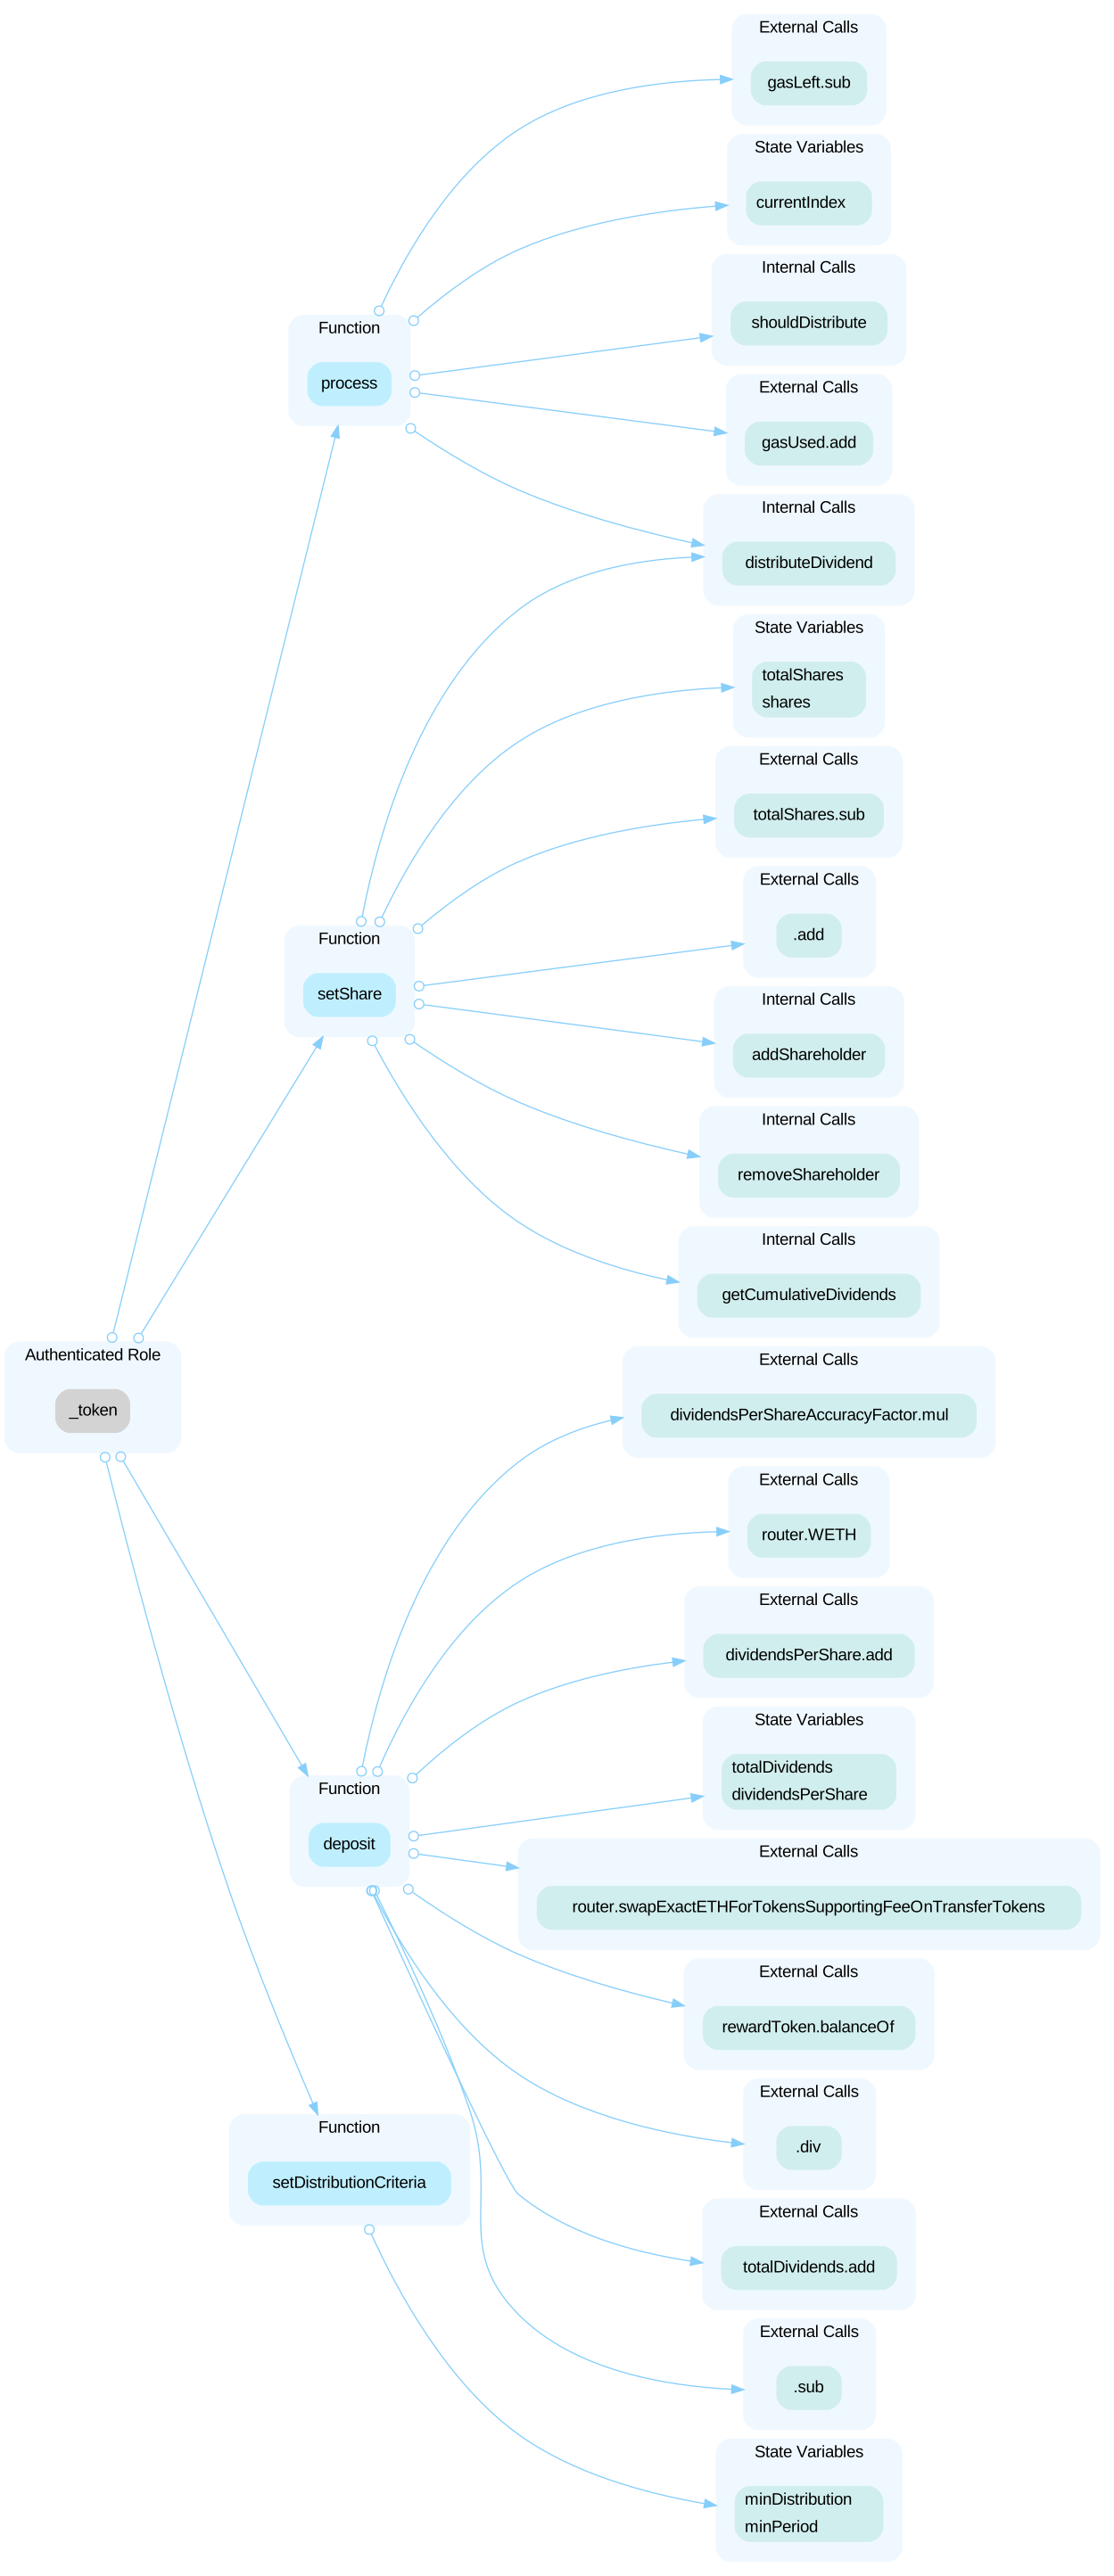 In the contract `ERC20Mintable` the role `_minter` has authority over the functions shown in the diagram below. Any compromise to the `_minter` account may allow the hacker to take advantage of this authority. 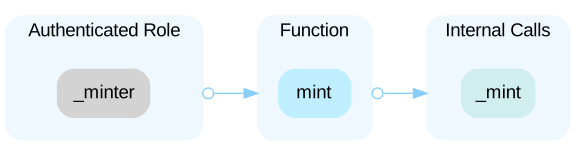 In the contract `ERC20Mintable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 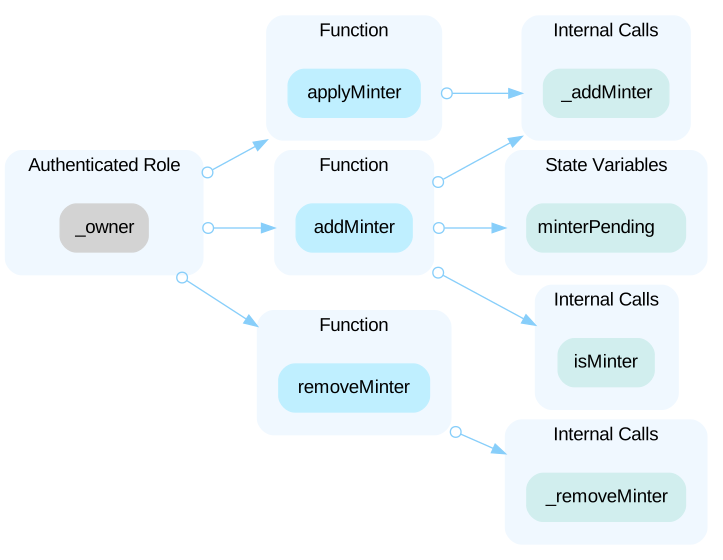 In the contract `ERC20TokenRecover` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 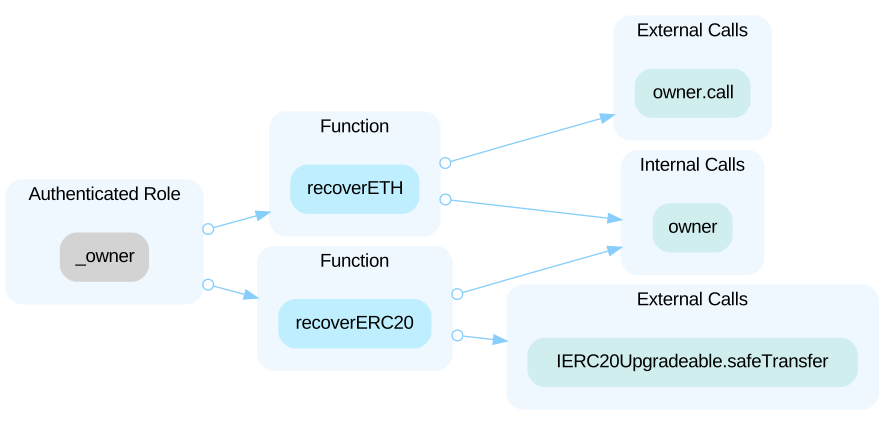
HighCentralized Control of Contract UpgradeAcknowledged
In the contract Reflecttoken and Standardtoken, the role `admin` has the authority to update the implementation contract behind the proxy contract. Any compromise to the `admin` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
HighInitial Token DistributionAcknowledged
All tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute tokens without the consensus of the community.
LowPotential Sandwich AttackAcknowledged
A sandwich attack may happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (executing before the target) a transaction to purchase one of the assets and make profits by backrunning (executing after the target) a transaction to sell the asset. ```solidity=100 router.swapExactETHForTokensSupportingFeeOnTransferTokens{ value: msg.value }(0, path, address(this), block.timestamp); ``` Function `DividendDistributor.deposit` invokes `IUniswapV2Router02.swapExactETHForTokensSupportingFeeOnTransferTokens` without setting restrictions on slippage or minimum output amount. Transactions triggering these functions are vulnerable to sandwich attacks.
LowThird-Party Dependency UsageAcknowledged
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. --- ```solidity=22 IUniswapV2Router02 public router; ``` - The contract `DividendDistributor` interacts with third party contract with `IUniswapV2Router02` interface via `router`. --- ```solidity= antibot.onPreTransferCheck(sender, recipient, amount); ``` - The contract `StandardToken` interacts with third party contract with `IKARMAAntiBot` interface via `antibot`.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (16)
- buyback/IDividendDistributor.sol
- extensions/ERC20Capped.sol
- ERC2612/IERC2612.sol
- extensions/ERC20Mintable.sol
- ReflectionToken.sol
- ERC1363/IERC1363Spender.sol
- buyback/DividendDistributor.sol
- ERC2612/ERC2612.sol
- extensions/ERC20Burnable.sol
- ERC1363/IERC1363.sol
- extensions/ERC20TokenRecover.sol
- BaseToken.sol
- extensions/IERC20Mintable.sol
- ERC1363/ERC1363.sol
- ERC1363/IERC1363Receiver.sol
- StandardToken.sol
Part of Karma’s security record
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us