Wemix Retainer 111 Wonder Staking
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 111 Wonder Staking) on 15 Apr 2024: 21 findings, 0 critical; 12 marked fixed, 9 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings21
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 2 | 0 | 3 |
| Low | 5 | 0 | 9 |
HighCentralization Related RisksOpen
In the contract `NCPStaking` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - set withdrawalNFT contract address - set `multiplierPointBasis` - set duration of fee ratio change - set platform fee ratio - set registry contract address - add a new LP to the pool - remove the LP from the pool - set the unbound time of the pool 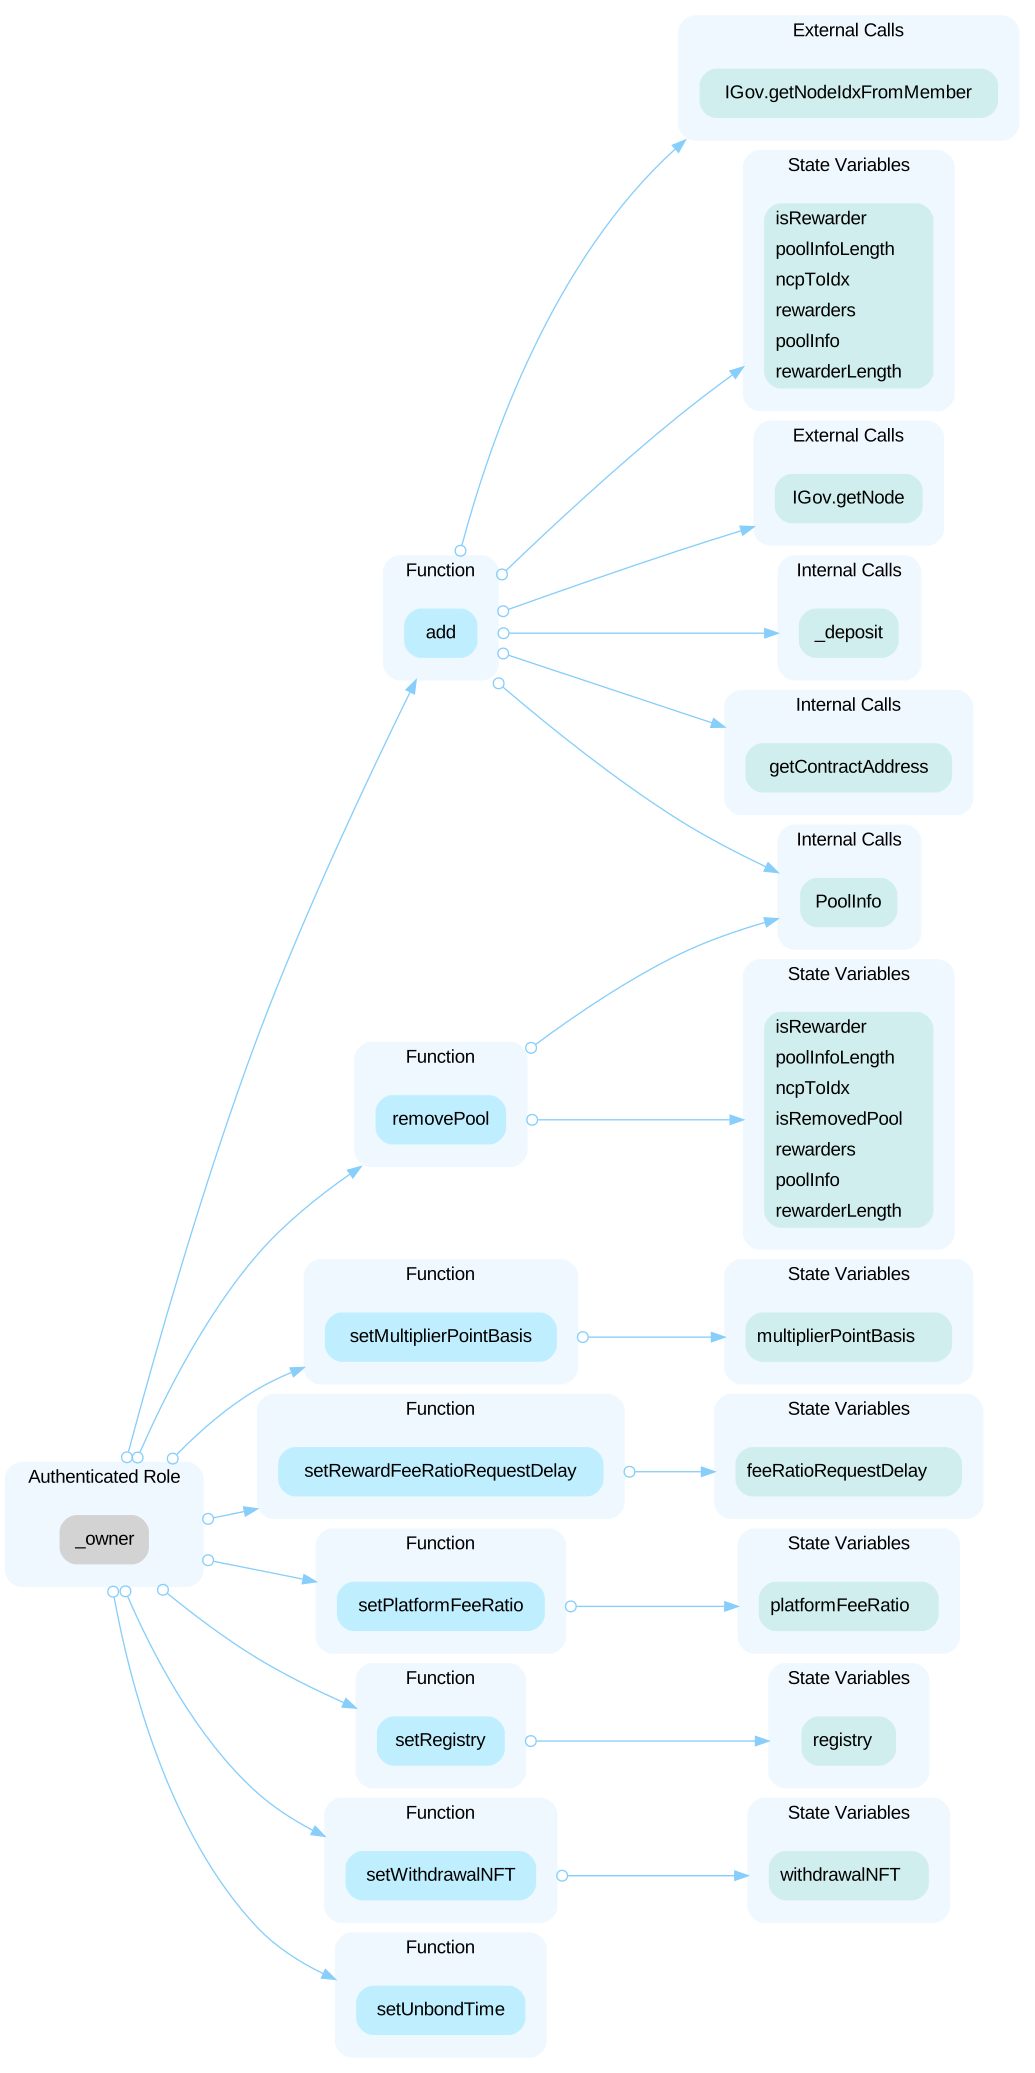 In the contract `NCPStaking` the role `_rewarderowner` has authority over the functions shown in the diagram below. Any compromise to the `_rewarderowner` account may allow the hacker to take advantage of this authority and update the given pool's reward point, update the given pool's reward fee ratio, and update the given pool's reward fee ratio request. 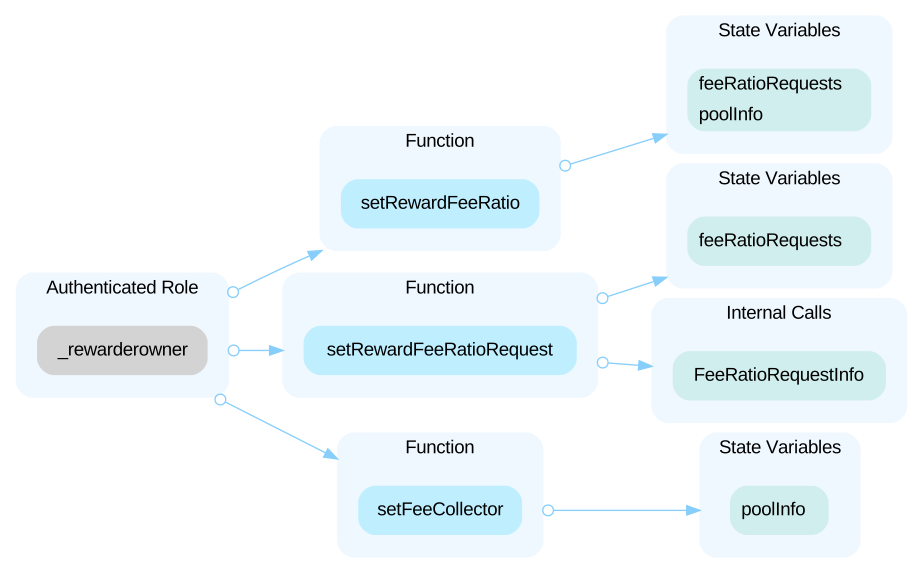 ----- In the contract `Rewarder` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and add/remove the rewarder and set the NCP address. 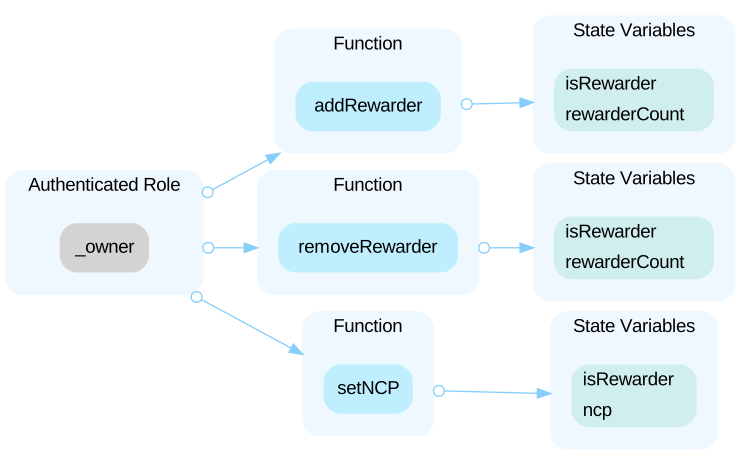 ----- In the contract `WithdrawalNFT` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and emergency transfer and change claimable time. 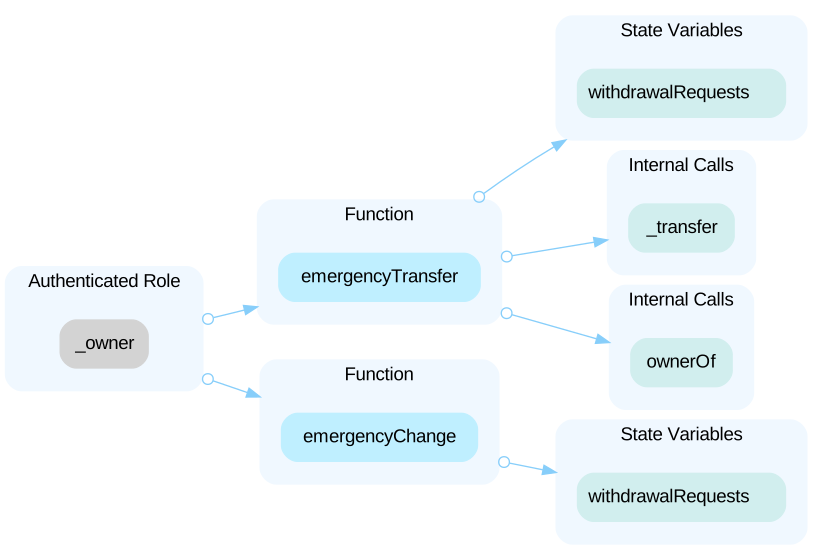 In the contract `WithdrawalNFT` the role `minter` has authority over the functions shown in the diagram below. Any compromise to the `minter` account may allow the hacker to take advantage of this authority and mint NFT to any address and burn NFT from any address. 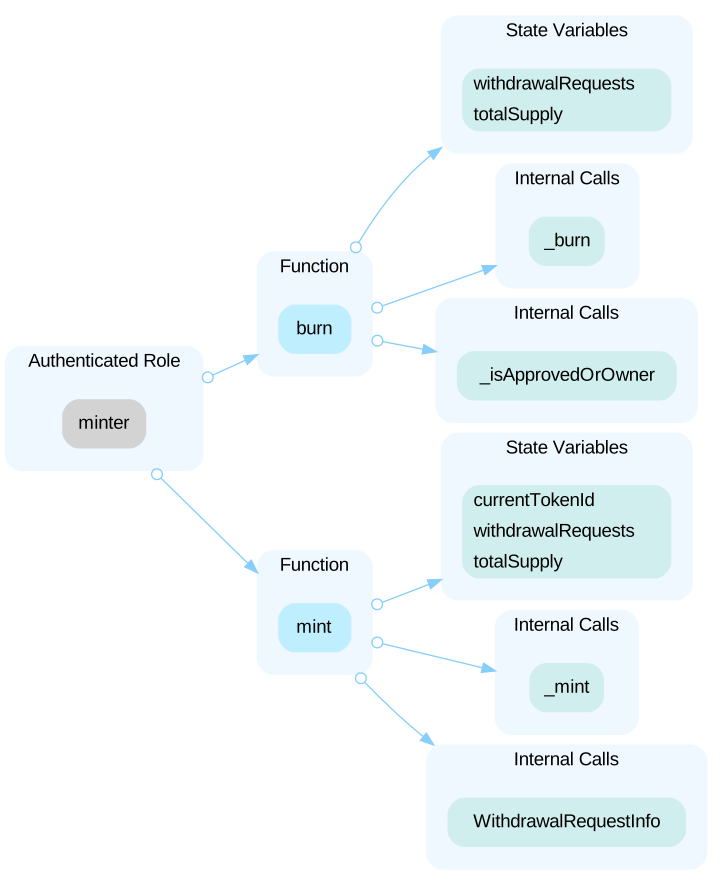
HighCentralized Control of Contract UpgradeOpen
In the contracts `NCPStaking`,`WithdrawalNFT` and `Rewarder`, the role `admin` has the authority to update the implementation contract behind the proxy contract. Any compromise to the `admin` account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
Medium`setMultiplierPointBasis()` Does Not Settle RewarOpen
The function `setMultiplierPointBasis()` in the linked contracts does not settle the current rewards with the old rate. All the staking users will be forced to use the new reward rate. This may be unfair to the user if the new rate is lower.
MediumNo Upper Limit for FeeOpen
There are no upper boundaries for the functions `setPlatformFeeRatio()` and `setRewardFeeRatio` which are used to set the platform fee ratio and reward fee ratio. It is possible to set the total fee up to any arbitrary amount.
LowLacking the condition that the staking amount isOpen
In the function `_deposit()`, if the user is the first to stake, the `totalDepositors` of the pool will be increased by 1. However, the condition that the staking amount is greater than 0 is missing, causing the `totalDepositors` to be greater than the actual count due to no amount being deposited. ```solidity=998 if (user.amount == 0) { pool.totalDepositors++; } ```
LowRedundant ComparisonsOpen
Comparisons that are always true or always false may be incorrect or unnecessary. ```solidity=419 require( feeRatioRequests[pid].ratio >= 0 && feeRatioRequests[pid].ratio <= 10000, "fee Ratio is invalid" ); ```
LowThird-Party Dependency UsageOpen
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=1639 address public registry; ``` - The contract `NCPStaking` interacts with third party contract with `IRegistry` interface via `registry`.
LowUnused modifier `whenNotLock`Open
The functions `setFeeCollector()`, `setUnbondTime()`, `ncpDeposit()` and `ncpWithdraw()` do not use the modifier `whenNotLock`, which requires that the pool not to be locked.
LowUnused State VariableOpen
Some state variables are not used in the codebase. This can lead to incomplete functionality or potential vulnerabilities if these variables are expected to be utilized. ```solidity=66 address public governance; ``` --- ```solidity=72 address public governanceStaking; ``` --- ```solidity=18 uint256 public accRewardPerShare; ```
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (3)
- contracts/NCPStaking.sol
- contracts/Rewarder.sol
- contracts/withdrawalToken/WithdrawalNFT.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us