LUCRO
CertiK reviewed EverGrow EGC (LUCRO) on 4 Sep 2024: 6 findings, 0 critical; 4 marked fixed, 2 acknowledged.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings6
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 2 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 1 | 2 |
HighCentralization Related RisksAcknowledged
In the contract `LucroStaking` the role `_admin` has authority over the functions shown in the list below. - function `addPackage()`, to create a package, transfer the rewards token to the contract, and set the number per second of token distribution. Users can stake the token in the contract to get the rewards from the package. - function `alterPackage()`, to update the package attributes, such as updating the total distribution reward tokens, and updating the number per second of the token distribution. - function `endPackage()`, to end the package. - function `claimAllRewardsForUser()`, to claim all rewards for the user. - function `claimAllRewardsForUsers()`, to claim all rewards for the users. Any compromise to the `_admin` account may allow the hacker to take advantage of this authority, allowing them to set the package, withdraw all staking and reward tokens from the contract, claim all user rewards, update the total distribution reward tokens, and update the number per second of the token distribution. In the contract `LucroStaking` the role `_owner` has authority over the functions shown in the list below. - function `changeOwner()`, to change the owner. - function `addAdmin()`, to add an admin. The admin possesses the privilege to add or alter packages. - function `removeAdmin()`, to remove an admin. The admin possesses the privilege to add or alter packages. - function `setMaxStakingPerBatch()`, the owner of the contract possessed the privilege to set the max staking amount per batch. - function `setSafeMode()`, to change the safe mode, specifically for protecting users from accidents. - function `setSmallFeeToBoostTotalExcluded()`, the owner of the contract possessed the privilege to set the small fee amount of distribution. - function `setSlippage()`, the owner of the contract possessed the privilege to set the slippage tolerance of swapping tokens when compounding rewards. - function `setExitFee()`, to set the exit fee percentage. - function `setEntryFee()`, to set the entry fee percentage. - function `setFeeRecipient()`, to set the fee recipient address. - function `setDEX()`, to set the DEX address. - function `setSwapPath()`, to set swap paths. - function `setStartIndex()`, to set the start index for package looping. - function `setPause()`, to pause the contact, staking, unstaking, claiming rewards, and compounding rewards. Any compromise to the `_owner` account could potentially enable a hacker to exploit this authority, In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 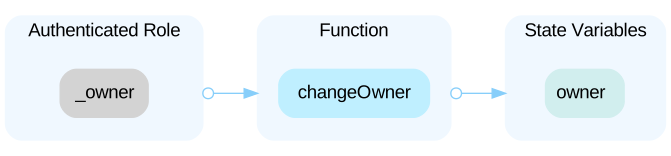 Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer the ownership. **The `alterPackage` function is exclusively controlled by the `admin` role, which is responsible for updating crucial state variables like `totalToDistribute`, and `timePeriod`. These variables are pivotal to the project's integrity and impact the number per second of the token distribution and the total distribution of reward tokens. Unauthorized modifications could severely impact certain functionalities, potentially eroding user trust.**
LowEnable Users to Stake Even When all Packages HaveAcknowledged
The lack of restrictions on the `stake` function permits users to stake their tokens even after all packages have concluded. As a result, users may face losses since there are no rewards to distribute, and entry and exit fees will be charged when staking or unstaking their tokens. We would like to confirm with the team whether this is aligned with original design.
Contracts in scope2
| Address | Chain | Source code |
|---|---|---|
| 0xae57fc660ce2dc2e713099b832f3550b89afcaf5 | Chain: BNB Chain | Source code: Verified source |
| 0x7a14676e237de4455da09a5236e54cdf4aa6fe9c | Chain: BNB Chain | Source code: Verified source |
Part of EverGrow EGC’s security record
 EverGrow EGC
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us