DigiVerse Staking - Audit
CertiK reviewed Digiverse (DigiVerse Staking - Audit) on 5 Jan 2024: 13 findings, 2 critical; 10 marked fixed, 3 acknowledged.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings13
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 1 | 1 |
| High | 0 | 2 | 4 |
| Medium | 0 | 0 | 1 |
| Low | 0 | 0 | 4 |
CriticalFinancial modelAcknowledged
The staking contract employs a hierarchical referral system, where participants earn commissions or rewards for recruiting new members. The reward seems to be distributed to the contract by the project team. However, if the token is not filled to the contract company, either the user cannot withdraw his deposits, or user's deposit can be withdrawn by other people.
HighCentralization Risks in digistake.solAcknowledged
In the contract `DigiStake` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change important parameters about the staking contract and transfer ERC 20 token other than staking token out of the contract. 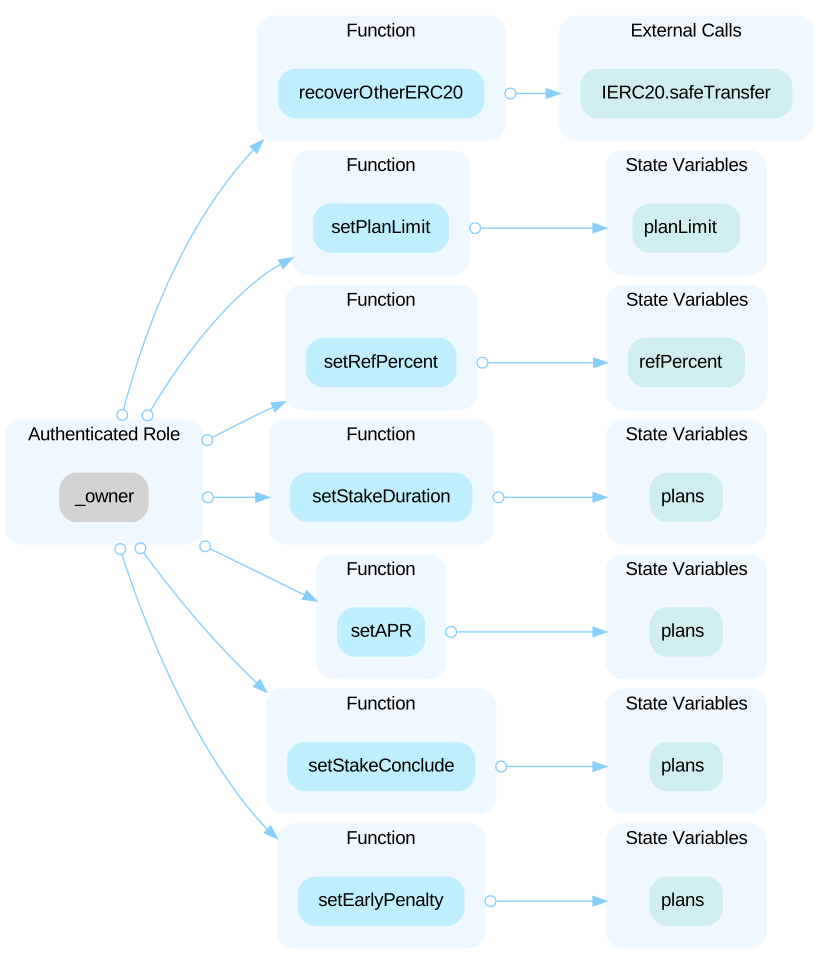
HighLack of TestsAcknowledged
There is no unit tests for the provided codebase. Testing programs are a very important aspect of proving program correctness, preventing regressions, and release engineering. Without tests, there is no way to know if the program works as expected. The fact that the code was submitted for review with such a significant flaw is regarded as an indicator of issues within the release engineering procedures. This could potentially result in unintended changes being deployed to the production environment.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- digistake.sol
Part of Digiverse’s security record
 Digiverse
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us