Trust-Ai
CertiK reviewed Trust AI (Trust-Ai) on 6 Dec 2023: 19 findings, 0 critical; 4 marked fixed, 2 acknowledged, 13 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings19
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 2 |
| Medium | 0 | 1 | 1 |
| Low | 13 | 0 | 1 |
HighAddresses Excluded From Fees Can Transfer When TrFixed
The contract `TRUSTAI` contains a conditional check that is intended to restrict trading when `tradingActive` is set to false. However, the current implementation has a flaw where wallets that are marked as `_isExcludedFromFees` can still initiate trades regardless of the `tradingActive` status. This creates a scenario where certain privileged wallets can trade while the feature is ostensibly disabled for the rest of the users.
HighCentralization Risks in TRUSTAI.solFixed
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 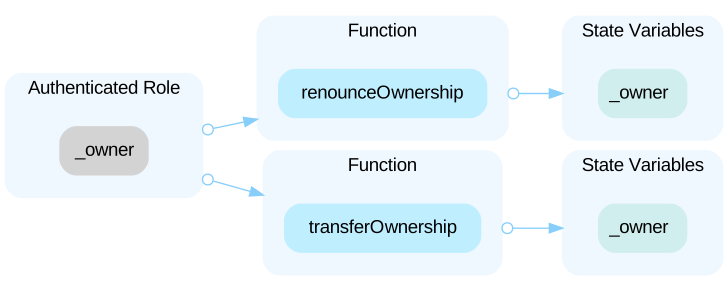 - `renounceOwnership()`: Transfers ownership of the contract to a zero address, effectively renouncing the ownership. Can be accessed by the `owner` role only. - `transferOwnership(address newOwner)`: Transfers ownership of the contract to a new account (`newOwner`). Can be accessed by the `owner` role only. In the contract `TRUSTAI` the role `_owner` has authority over the functions shown in the diagram below. 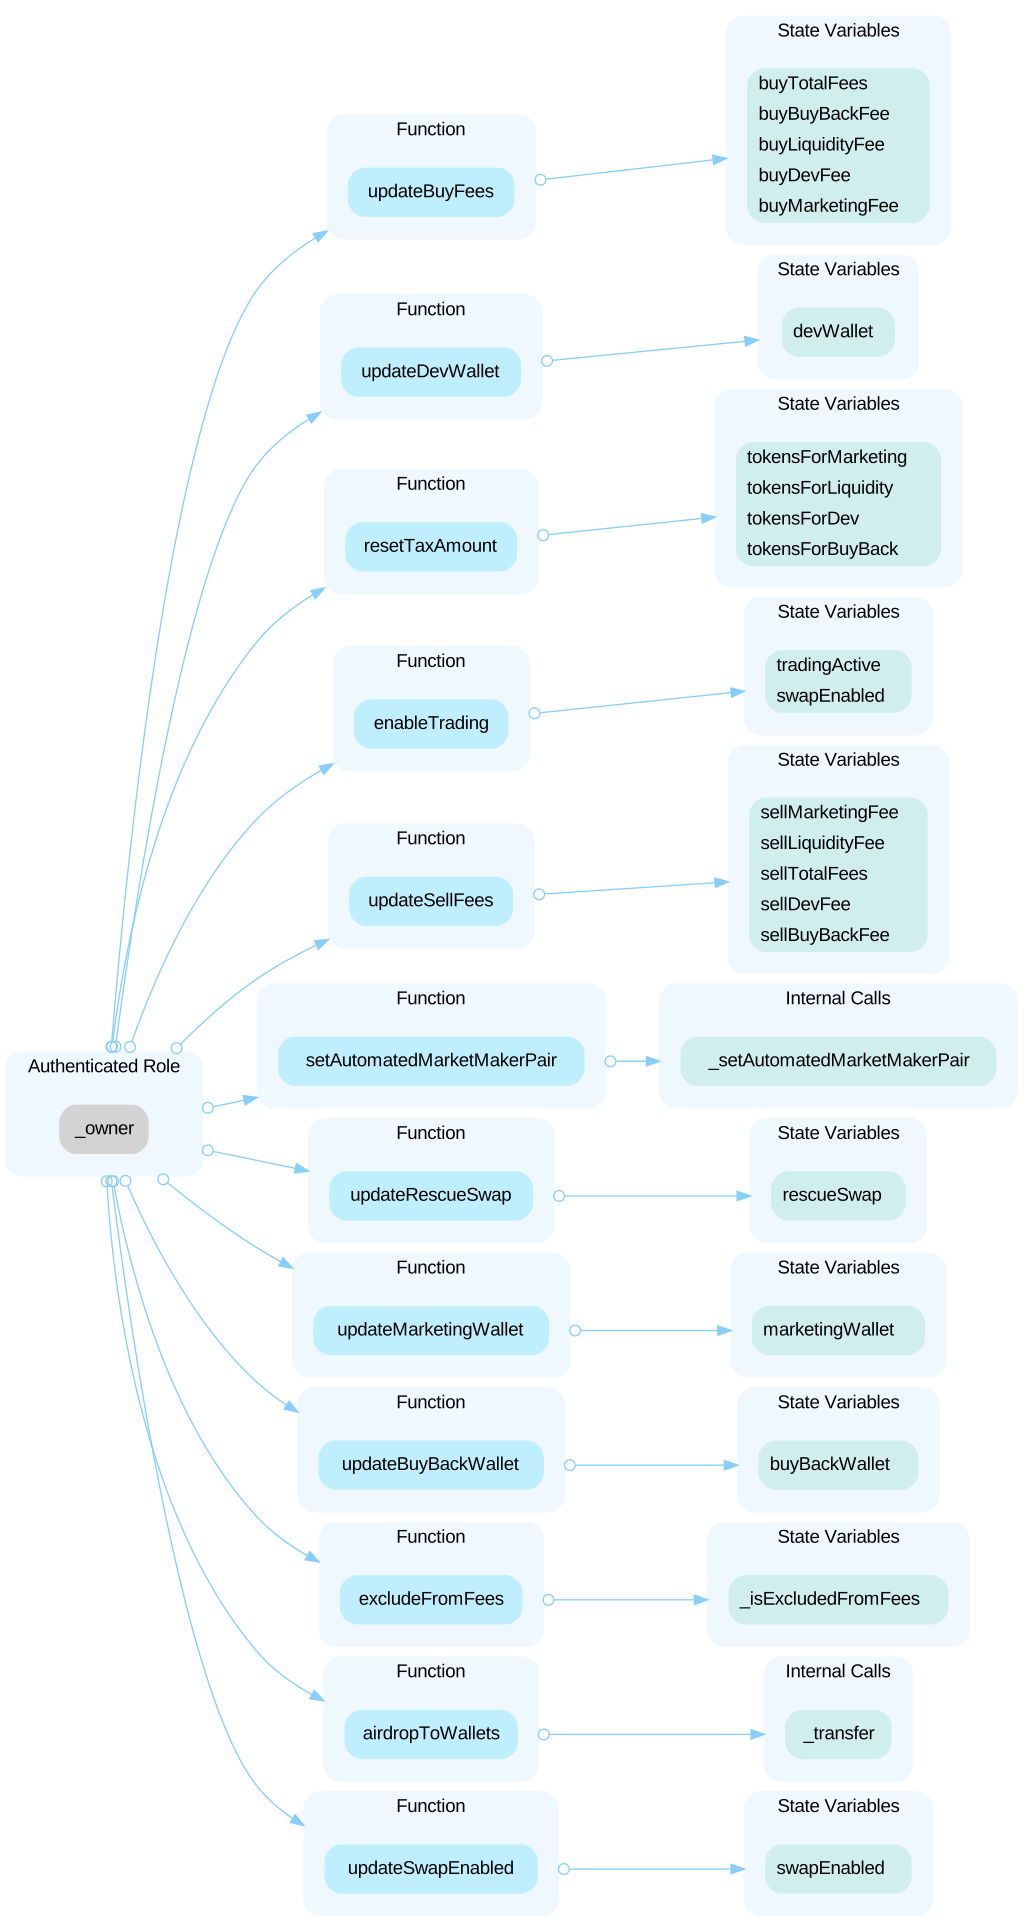 - `enableTrading()`: Activates trading and enables swapping and cannot be disabled after. Can be accessed by the `owner` role only - `airdropToWallets(address[] memory airdropWallets, uint256[] memory amounts)`: Allows the owner to airdrop tokens to a list of wallets before trading is enabled. Can be accessed by the `owner` role only. - `updateSwapEnabled(bool enabled)`: Enables or disables contract sales (emergency use). Can be accessed by the `owner` role only. - `updateBuyFees(uint256 _marketingFee, uint256 _liquidityFee, uint256 _devFee, uint256 _buyBackFee)`: Updates the fee structure for buy transactions. Can be accessed by the `owner` role only. - `updateSellFees(uint256 _marketingFee, uint256 _liquidityFee, uint256 _devFee, uint256 _buyBackFee)`: Updates the fee structure for sell transactions. Can be accessed by the `owner` role only. - `excludeFromFees(address account, bool excluded)`: Excludes or includes an account from fees. Can be accessed by the `owner` role only. - `setAutomatedMarketMakerPair(address pair, bool value)`: Sets a pair as an automated market maker pair. Can be accessed by the `owner` role only. - `updateMarketingWallet(address newMarketingWallet)`: Updates the marketing wallet address. Can be accessed by the `owner` role only. - `updateDevWallet(address newWallet)`: Updates the development wallet address. Can be accessed by the `owner` role only. - `updateBuyBackWallet(address newWallet)`: Updates the buyback wallet address. Can be accessed by the `owner` role only. - `resetTaxAmount()`: Resets the accumulated tax amounts for liquidity, marketing, development, and buyback to zero. Can be accessed by the `owner` role only. - `updateRescueSwap(bool enabled)`: Enables or disables the rescue swap feature. Can be accessed by the `owner` role only. When `swapEnabled` is set to true by owner calling `updateRescueSwap()` function, every internal call of `swapBack()` will transfer the entire token balance of the contract to the `marketingWallet` address, which is hardcoded as `0xE45C96e58b6B4001F85Fc206735fDc219AbbCA6A` initially and could be updated by calling `updateMarketingWallet` by `owner` ```solidity=1199 uint256 contractBalance = balanceOf(address(this)); if (rescueSwap){ if (contractBalance > 0){ super._transfer(address(this), marketingWallet, contractBalance); } return; } ``` Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project.
MediumInsecure `takeFee` ConditionFixed
If a reentrancy attack happened in the function `_transfer`, the `swapping` could be `true` in L1108, then the `takeFee` would always be `false` due to the condition at L1115. Therefore, any transfer performed in a reentrancy attack would avoid fees for the attacker even if the attacker address is not excluded from fees.
LowPull-Over-Push PatternFixed
The change of `owner` by function `transferOwnership()` overrides the previously set `owner` with the new one without guaranteeing the new `owner` has the ability to actuate transactions on-chain.
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0x50c7584be73d20760f1947ffcbf7942822c968c8 | Chain: BNB Chain | Source code: Verified source |
Part of Trust AI’s security record
 Trust AI
Security firm
 CertiK
1,044 projects reviewed · 1,393 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us