IceCreamSwap
CertiK reviewed IceCreamSwap on 6 Jul 2023: 6 findings, 0 critical; 3 marked fixed, 1 acknowledged, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings6
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 0 | 0 |
| Medium | 0 | 1 | 3 |
| Low | 2 | 0 | 0 |
MediumCentralization Related RisksAcknowledged
In the contract `IceCreamFarm` the role `_owner` has authority over the functions shown in the diagram below. 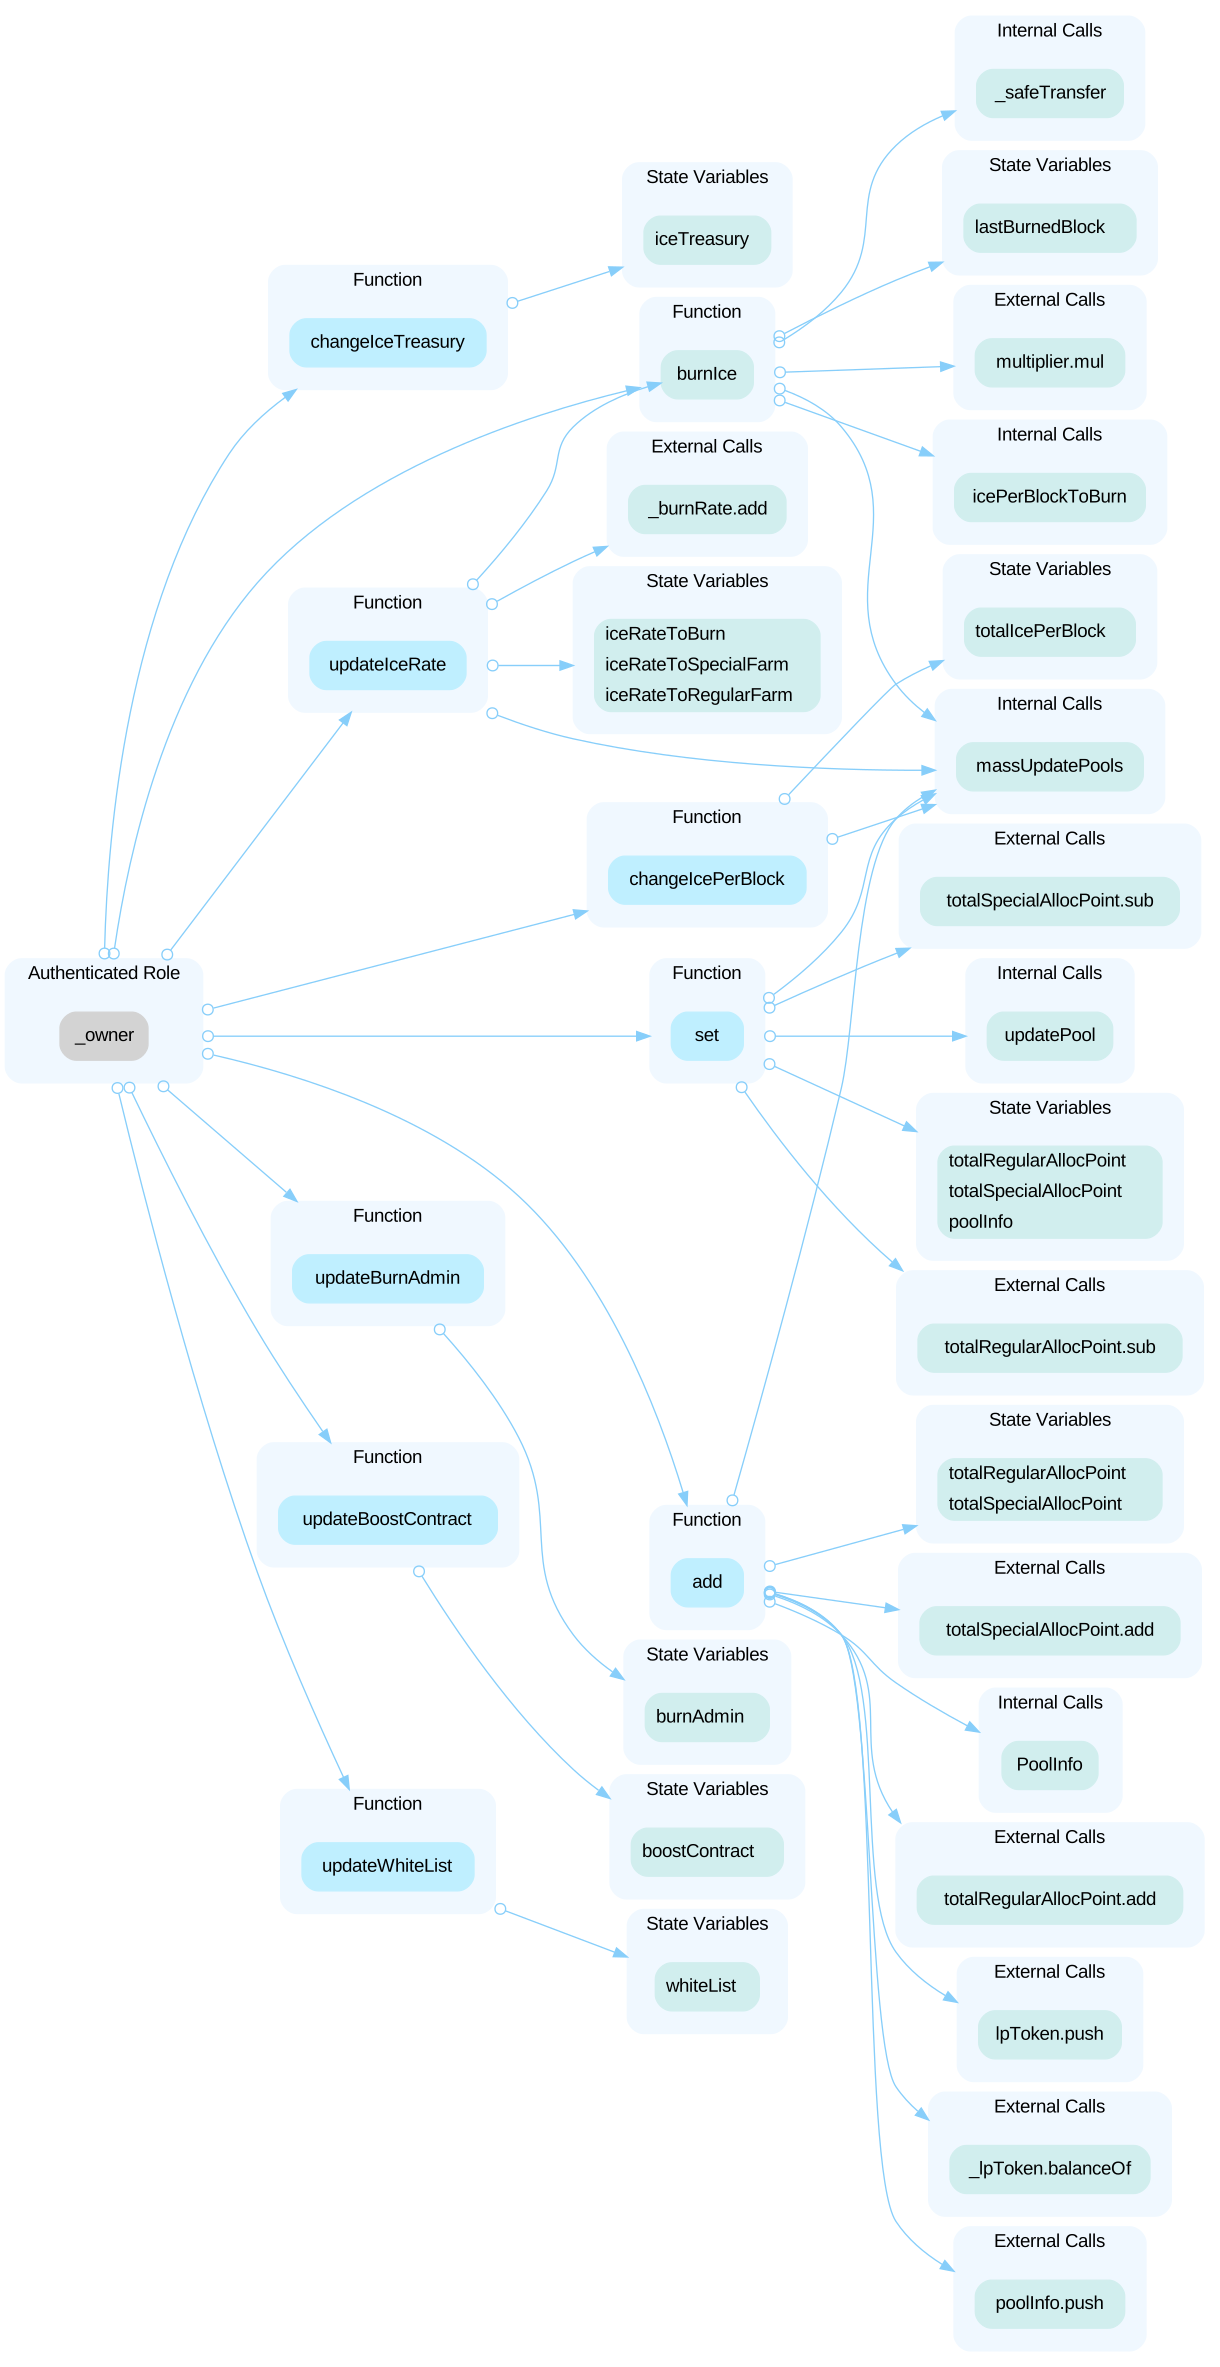 - `add(uint256 _allocPoint, IERC20 _lpToken, bool _isRegular, bool _withUpdate)`: Adds a new liquidity pool with the specified allocation point and LP token, specifies whether it's a regular pool, and optionally updates all pools. The function can only be called by the contract owner. - `set(uint256 _pid, uint256 _allocPoint, bool _withUpdate)`: Updates the allocation point of a specified pool and optionally updates all pools. The function can only be called by the contract owner. - `burnIce(bool _withUpdate)`: Burns the ICE token and optionally updates all pools. The function can only be called by the contract owner. - `updateIceRate(uint256 _burnRate, uint256 _regularFarmRate, uint256 _specialFarmRate, bool _withUpdate)`: Updates the rate of ICE tokens for burning, regular farming, and special farming, and optionally updates all pools. The function can only be called by the contract owner. - `updateBurnAdmin(address _newBurnAdmin)`: Updates the address of the burn admin. The function can only be called by the contract owner. - `updateWhiteList(address _user, bool _isValid)`: Updates the whitelist status of a user for special pools. The function can only be called by the contract owner. - `changeIceTreasury(address _iceTreasury)`: Changes the address of the ICE treasury. The function can only be called by the contract owner. - `changeIcePerBlock(uint256 _totalIcePerBlock, bool _withUpdate)`: Changes the amount of ICE being distributed per block and optionally updates all pools. The function can only be called by the contract owner. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settigns or execute sensitive functions of the contract In the contract `IceCreamFarm` the role `boostContract` has authority over the functions shown in the diagram below. 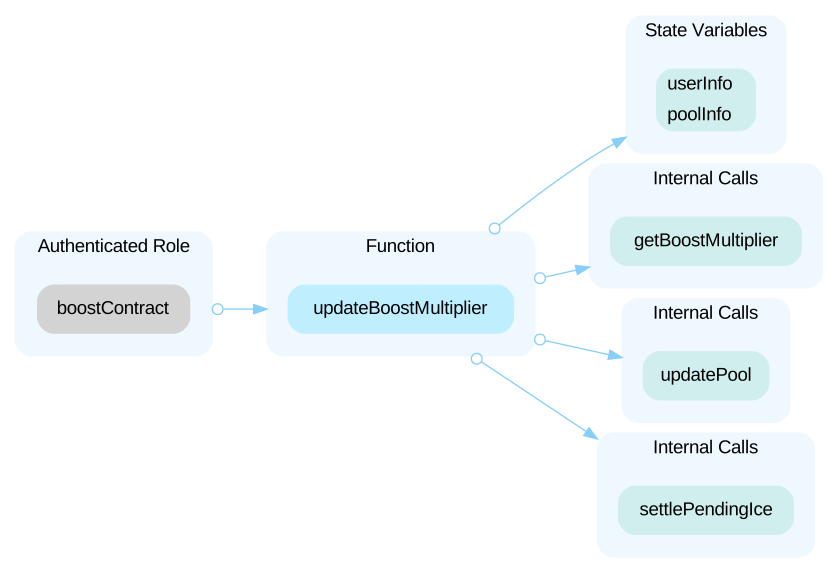 - `updateBoostContract(address _newBoostContract)`: Updates the address of the contract responsible for share boosts. The function can only be called by the account who was granted with boostContract role. Any compromise to the `boostContract` account may allow the hacker to take advantage of this authority and update the sensitive settigns or execute sensitive functions of the contract --- In the contract `PancakeFactory` the role `feeToSetter` has authority over the functions shown in the diagram below. 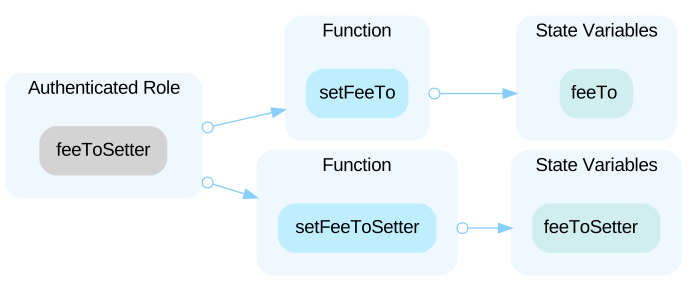 - `setFeeTo(address _feeTo)`: This function is used to set the address where fees are sent (`feeTo`). The function can only be called by the current `feeToSetter`. - `setFeeToSetter(address _feeToSetter)`: This function is used to change the address that has the privilege to set the `feeTo` address. The function can only be called by the current `feeToSetter`. Any compromise to the `feeToSetter` account may allow the hacker to take advantage of this authority and update the sensitive settigns or execute sensitive functions of the contract --- In the contract `PancakePair` the role `factory` has authority over the functions shown in the diagram below. 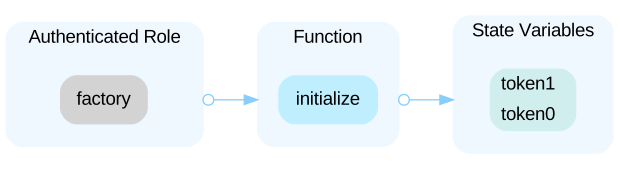 - `initialize(address _token0, address _token1)`: This function initializes the token0 and token1 state variables in the contract. It can only be called once by the factory contract during deployment. The function can only be called by the factory contract or account. Any compromise to the `factory` account may allow the hacker to take advantage of this authority and update the sensitive settigns or execute sensitive functions of the contract --- In the contract `SmartChefFactory` the role `_owner` has authority over the functions shown in the diagram below. 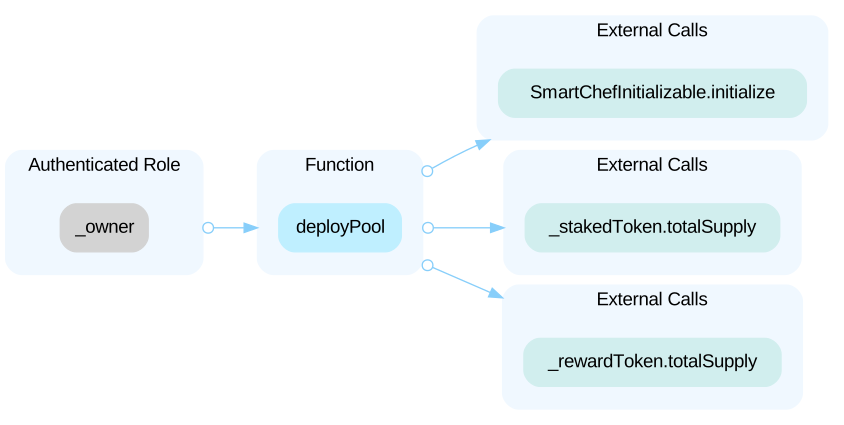 - `deployPool(IERC20Metadata _stakedToken, IERC20Metadata _rewardToken, uint256 _rewardPerBlock, uint256 _startBlock, uint256 _bonusEndBlock, uint256 _poolLimitPerUser, uint256 _numberBlocksForUserLimit, address _admin)`: This function deploys a new SmartChefInitializable contract. It verifies that the staking and reward tokens are valid by checking their total supply, and then deploys a new SmartChefInitializable contract with the given parameters. After deployment, it emits a `NewSmartChefContract
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (7)
- projects/staking/contracts/SmartChefFactory.sol
- projects/dex/contracts/PancakeRouter.sol
- projects/dex/contracts/PancakePair.sol
- projects/dex/contracts/PancakeFactory.sol
- projects/liquidity-farms/contracts/MasterChefV2.sol
- projects/staking/contracts/SmartChefInitializable.sol
- projects/dex/contracts/PancakeERC20.sol
Part of IceCreamSwap’s security record
 IceCreamSwap
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us