TenGuDaruma NFT
CertiK reviewed TenGuDaruma (TenGuDaruma NFT) on 2 Sep 2022: 12 findings, 0 critical; none marked fixed.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings12
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 10 | 0 | 0 |
HighCentralization Risks in `FarmStaking` and `WishPoOpen
In the contract `FarmStaking` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 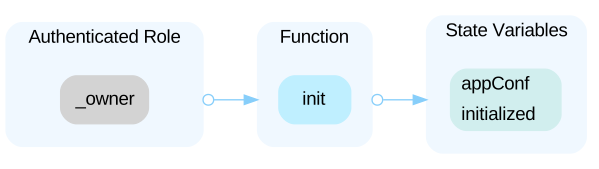 In the contract `FarmStaking` the role `_owner` also has authority over the functions in commit'f677e3b53fa79d062cce3dd6a3c8f4b871192193'. - function `pause()`: to pause the transactions. - function `unpause()`: to unpause the transactions. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. In the contract `WishPool` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 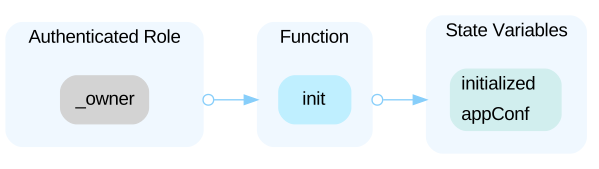 In the contract `WishPool` the role `_owner` also has authority over the functions in commit'f1b5f8bc84f224cfc434705c7d15f50ed60fb970'. - function `pause()`: to pause the transactions. - function `unpause()`: to unpause the transactions. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority.
HighCentralization Risks in the `FarmReward`Open
In the contract `FarmReward` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 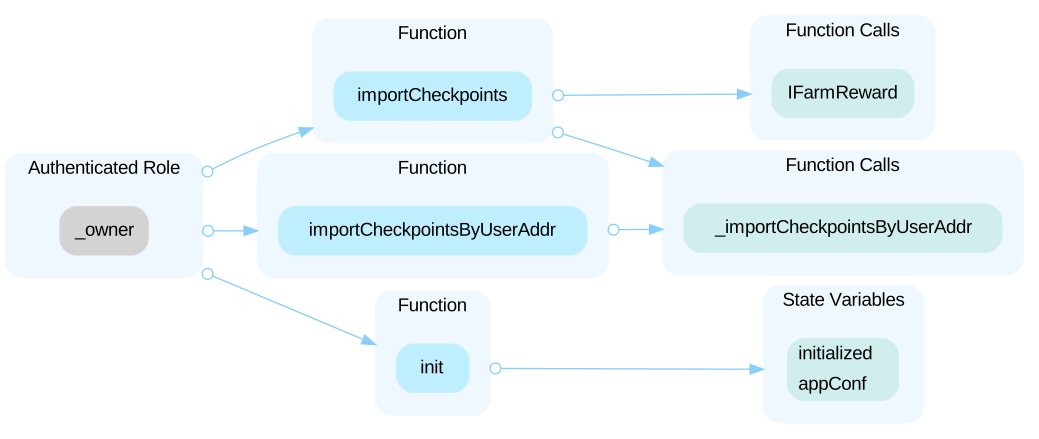 In the contract `FarmReward` the role `_owner` also has authority over the functions in commit'ca81e9d775e7631c854c8fd6c6a9069925e208c4'. - function `pause()`: to pause the transactions. - function `unpause()`: to unpause the transactions. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority.
LowDeclaration Naming ConventionOpen
One or more declarations do not conform to the [Solidity style guide](https://solidity.readthedocs.io/en/v0.7.3/style-guide.html#naming-conventions) with regards to its naming convention. Particularly: - `camelCase`: Should be applied to function names, argument names, local and state variable names, modifiers - `UPPER_CASE`: Should be applied to `constant` variables - `CapWords`: Should be applied to contract names, struct names, event names, and enums.
LowDependency contractsOpen
The contract is serving as the underlying entity to interact with one or more implementations that are out of the scope of this audit, such as `appConf.getRewardAmount()`,`nftFactory.tokenDetail()`, `IFactory(appConf.getNftFactoryAddr()).mintDamo()`, `IERC20Ex(redeemToken).safeTransferFrom()`, etc. The scope of the audit treats these codes as black boxes and assumes their functional correctness. The detailed dependencies are listed below: ```solidity contract AppConf contract damoFactory contract daMoContract contract wishDaMo interface IERC20Ex ```
LowDivide Before MultiplyOpen
Performing integer division before multiplication truncates the low bits, losing the precision of calculation. ```solidity=175 uint256 multiple = elapsedTime / appConf.getRewardPeriod(stakingRecord.gen); ``` ```solidity=176 rewardAmount = nftCount * (multiple * appConf.getRewardAmount(stakingRecord.gen)); ```
LowExternal Call Inside LoopOpen
External calls are made inside a *for* loop. This might lead to a denial-of-service attack. If any of the calls fail, it will cause the entire loop to revert.
LowGas Limit and LoopsOpen
The logic of functions `_claimAll()`, `_claim()`, `unstakeAll()` and `_unstake()` are too complex and contain many loops. Loops that do not have a fixed number of iterations, for example, loops that depend on storage values, have to be used carefully. Due to the block gas limit, transactions can only consume a certain amount of gas. Either explicitly or just due to normal operation, the number of iterations in a loop can grow beyond the block gas limit which can cause the complete contract to be stalled at a certain point. This may not apply to view functions that are only executed to read data from the blockchain. Still, such functions may be called by other contracts as part of on-chain operations and stall those. Please be explicit about such cases in the documentation of your contracts.
LowLogical issue of `stakingStatusMap`Open
The `tokenIds` may be duplicated among different types of NFTs, hence the `stakingStatusMap` should not only record the `tokenIds`, but also the NFT type.
LowMissing Emit EventsOpen
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
LowThe calculation of the rewardOpen
When the `rewardType` is not `Model.REWARD_TYPE_FIXED`, investors may get less reward because of solidity's division truncation feature. e.g. If the `nftCount == 1`, `appConf.getRewardAmount(stakingRecord.gen) == 1`, `appConf.getRewardPeriod(stakingRecord.gen) == 7 day`, `elapsedTime == 13 day`, the `rewardAmount` would be 1, which means the 6 of 13 days for staking are nullified.
Show 2 more
LowThe use of `WishPool`Open
Except for the function `getWishs()`, the contract `WishPool` has two external functions, the `wish()` and `redeem()`. The function `wish()` is used to add a new wish content to the `wishMap`, and the function `redeem()` is used to burn an NFT and get another type of NFT, and the redeem tokens or ETHs may also be transferred to the donate address and incense address. We would like the client to provide us with more detailed information about the design of the `wishMap`, the function `redeem()`, and the difference among various NFTs.
LowUnlocked Compiler VersionOpen
The contract has an unlocked compiler version. An unlocked compiler version in the source code of the contract permits the user to compile it at or above a particular version. This, in turn, leads to differences in the generated bytecode between compilations due to differing compiler version numbers. This can lead to ambiguity when debugging as compiler-specific bugs may occur in the codebase that would be hard to identify over a span of multiple compiler versions rather than a specific one.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (3)
- wish/WishPool.sol
- farm/FarmReward.sol
- farm/FarmStaking.sol
Part of TenGuDaruma’s security record
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us