LGT
CertiK reviewed LGT-NFT (LGT) on 26 Sep 2022: 24 findings, 0 critical; 1 marked fixed, 4 acknowledged, 19 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings24
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 3 | 1 |
| Medium | 0 | 1 | 0 |
| Low | 19 | 0 | 0 |
HighCentralization Risks in LGToken.solAcknowledged
In the contract `LGToken` the role `_owner` has authority over the functions shown in the diagram below. 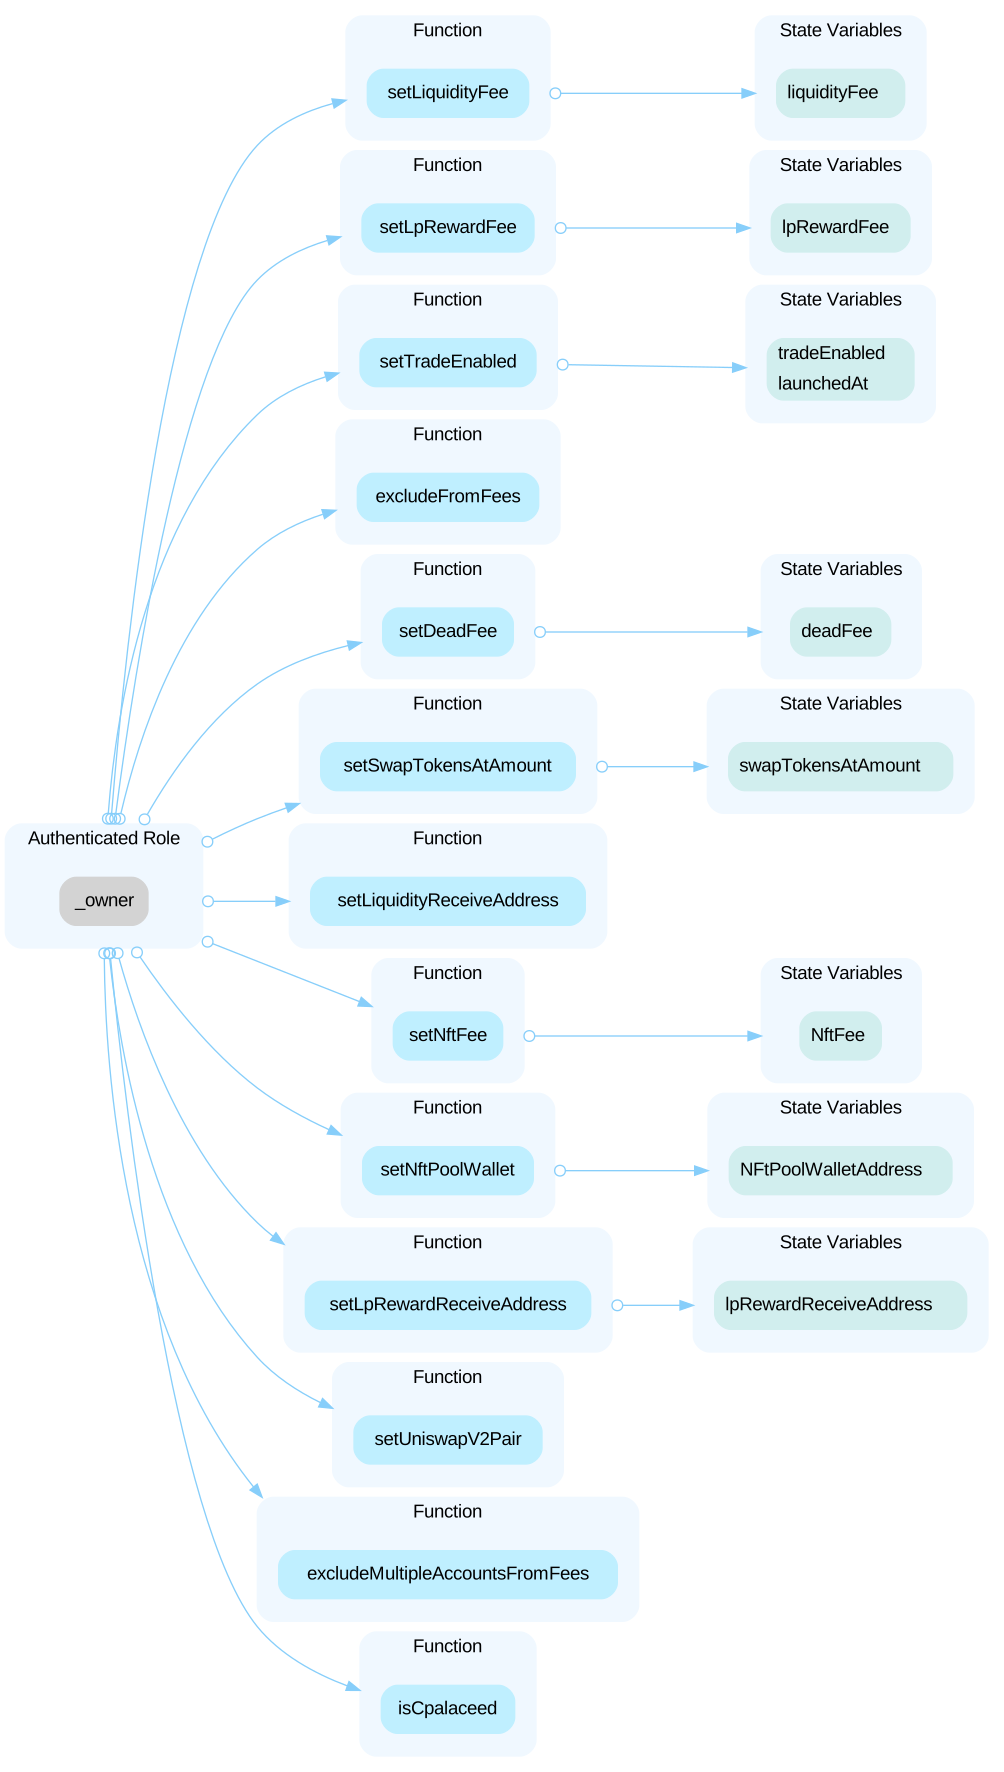 In the contract `LiquidityBackHelper` the role `_owner` has authority over the functions shown in the diagram below. 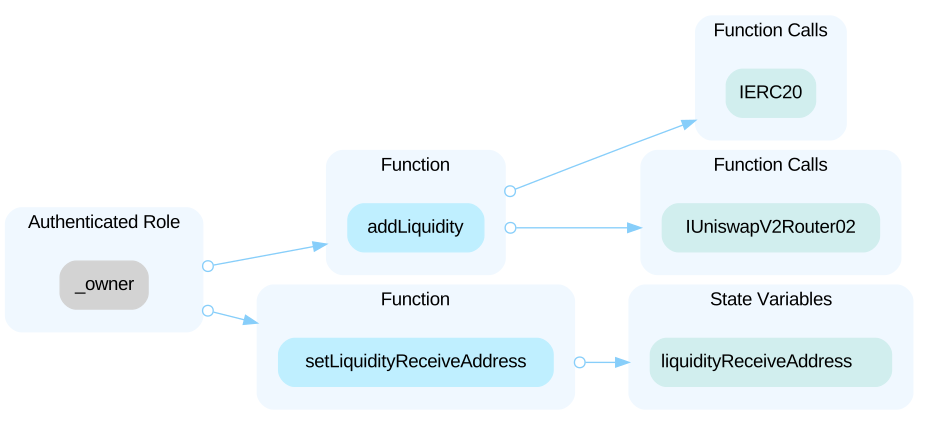 In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. 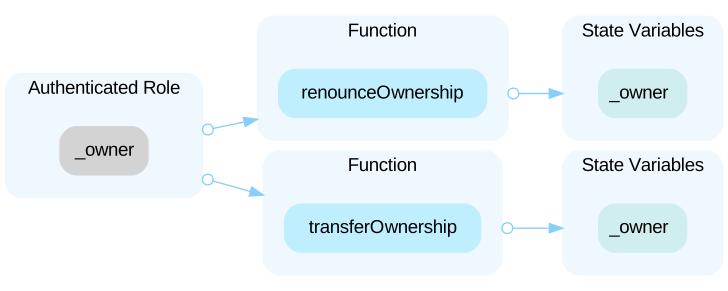 Any compromise to the privileged accounts may allow the hacker to take advantage of this authority.
HighCentralized Risk in `addLiquidity`Acknowledged
```solidity=603 function addLiquidity(uint256 tokenAmount, uint256 usdtAmount) external onlyOwner { IERC20(token).approve(address(router), tokenAmount); IERC20(usdt).approve(address(router), usdtAmount); IUniswapV2Router02(router).addLiquidity( token, usdt, tokenAmount, usdtAmount, 0, 0, liquidityReceiveAddress, block.timestamp ); } ``` The `addLiquidity()` function calls the `uniswapV2Router.addLiquidity` function with the `to` address specified as `liquidityReceiveAddress` for acquiring the generated LP tokens from the `LGT-USDT` pool. As a result, over time the `liquidityReceiveAddress` address will accumulate a significant portion of LP tokens. If the `liquidityReceiveAddress` is an EOA (Externally Owned Account), mishandling of its private key can have devastating consequences to the project as a whole.
HighInitial Token DistributionAcknowledged
All of the `LGT` tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute `LGT` tokens without obtaining the consensus of the community.
MediumContract Gains Non-withdrawable BUSD Via the `swaAcknowledged
The `swapAndLiquify()` function converts half of the `AmountLiquidityFee` `LGT` tokens to `BUSD`. The other half of `LGT` tokens and part of the converted `BUSD` are deposited into the `LGT-BUSD` pool on pancakeswap as liquidity. For every `swapAndLiquify()` function call, a small amount of `BUSD` leftover in the `liquidityBackHelper` contract. This is because the price of `LGT` drops after swapping the first half of `LGT` tokens into `BUSD`, and the other half of `LGT` tokens require less than the converted `BUSD` to be paired with it when adding liquidity. The `liquidityBackHelper` contract doesn't appear to provide a way to withdraw those `BUSD`, and they will be locked in the contract forever.
Contracts in scope1
| Address | Chain | Source code |
|---|---|---|
| 0x16243911e0c7eb0b6a7b089c79ac74572232eb68 | Chain: BNB Chain | Source code: Verified source |
Part of LGT-NFT’s security record
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us