YieldFlow - Audit 2
CertiK reviewed YieldFlow (YieldFlow - Audit 2) on 12 Apr 2024: 63 findings, 3 critical; 61 marked fixed, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings63
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 3 |
| High | 1 | 0 | 3 |
| Medium | 0 | 0 | 10 |
| Low | 1 | 0 | 45 |
HighCentralization Related RisksOpen
### Fee Distributor In the contract `FeeDistributor` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do the following: - Register/deregister tokens to allow/disallow their use. - Allow or disallow a contract to receive fees why adding or removing it from the whitelist. - Transfer ownership to another address they control. 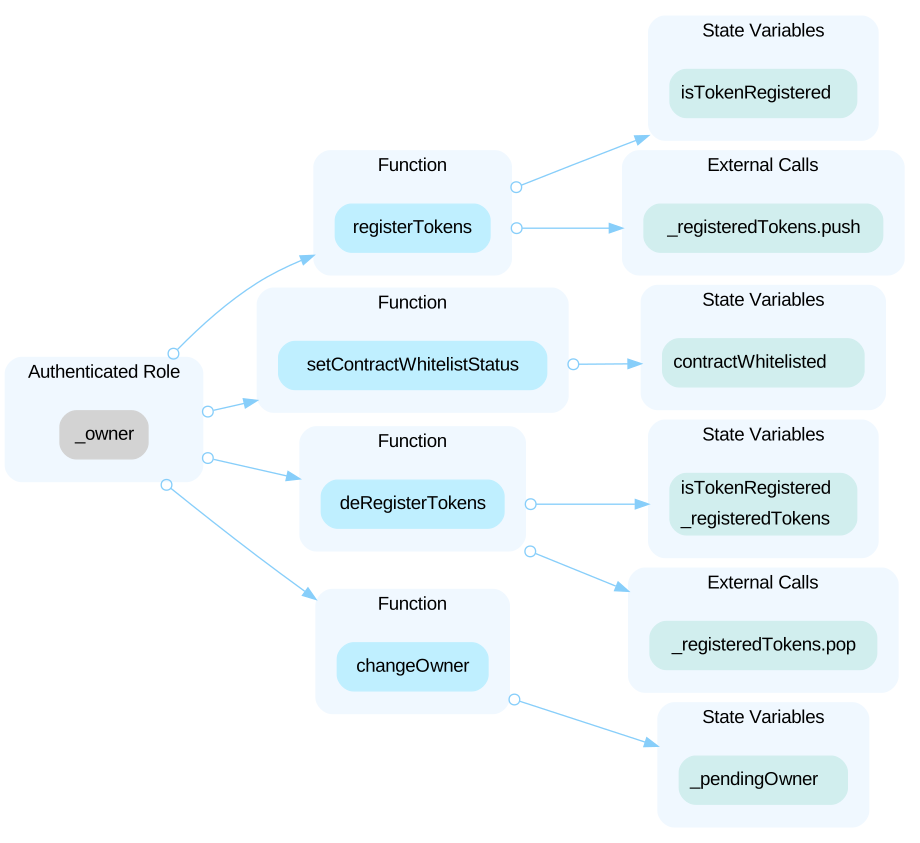 --- ### RangeMaster In the contract `RangeMaster` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do the following: - Recover any ETH or ERC20 token in the contract for themselves. - Change the YieldManager to a malicious contract to collect fees for themselves. - Change the `rangePositionManagers` to malicious contracts that will steal users liquidity. - Change the owner to an address they have the sole control over. - Lock/unlock the ability for users to add liquidity. 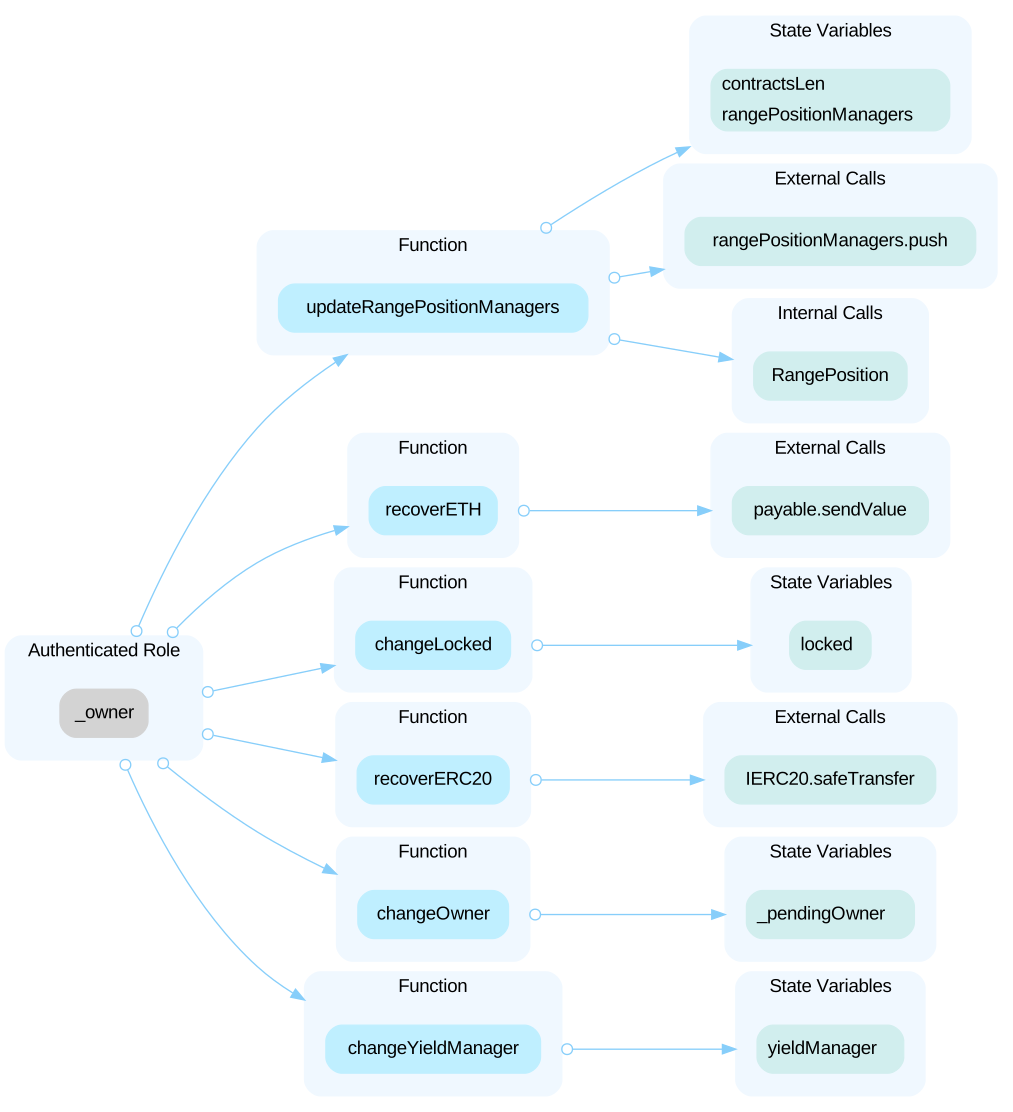 --- ### RangePositionManager In the contract `RangePositionManager` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do the following: - Change the `rangeMaster` contract to a malicious contract to increase/decrease/collect on behalf of users. - Disable the use of the Masterchef contract to stop receiving farming rewards. - Mint the initial liquidity before the protocol is ready. - Change the owner to an account they have the sole control over. - Lock/Unlock the ability for users to add liquidity to the protocol. - Withdraw any excess ERC20 tokens or ether not allocated to users for themselves. - Disable/Enable the move range checks so that the range can always be moved or can only be moved if outside of a specified range. - Give/Revoke accounts the operator privilege, which has the ability to call `moveRange()` or `increaseLiquidityAuto()`. - Set the fee distributor or swapper contract to malicious contracts to steal funds from the protocol. 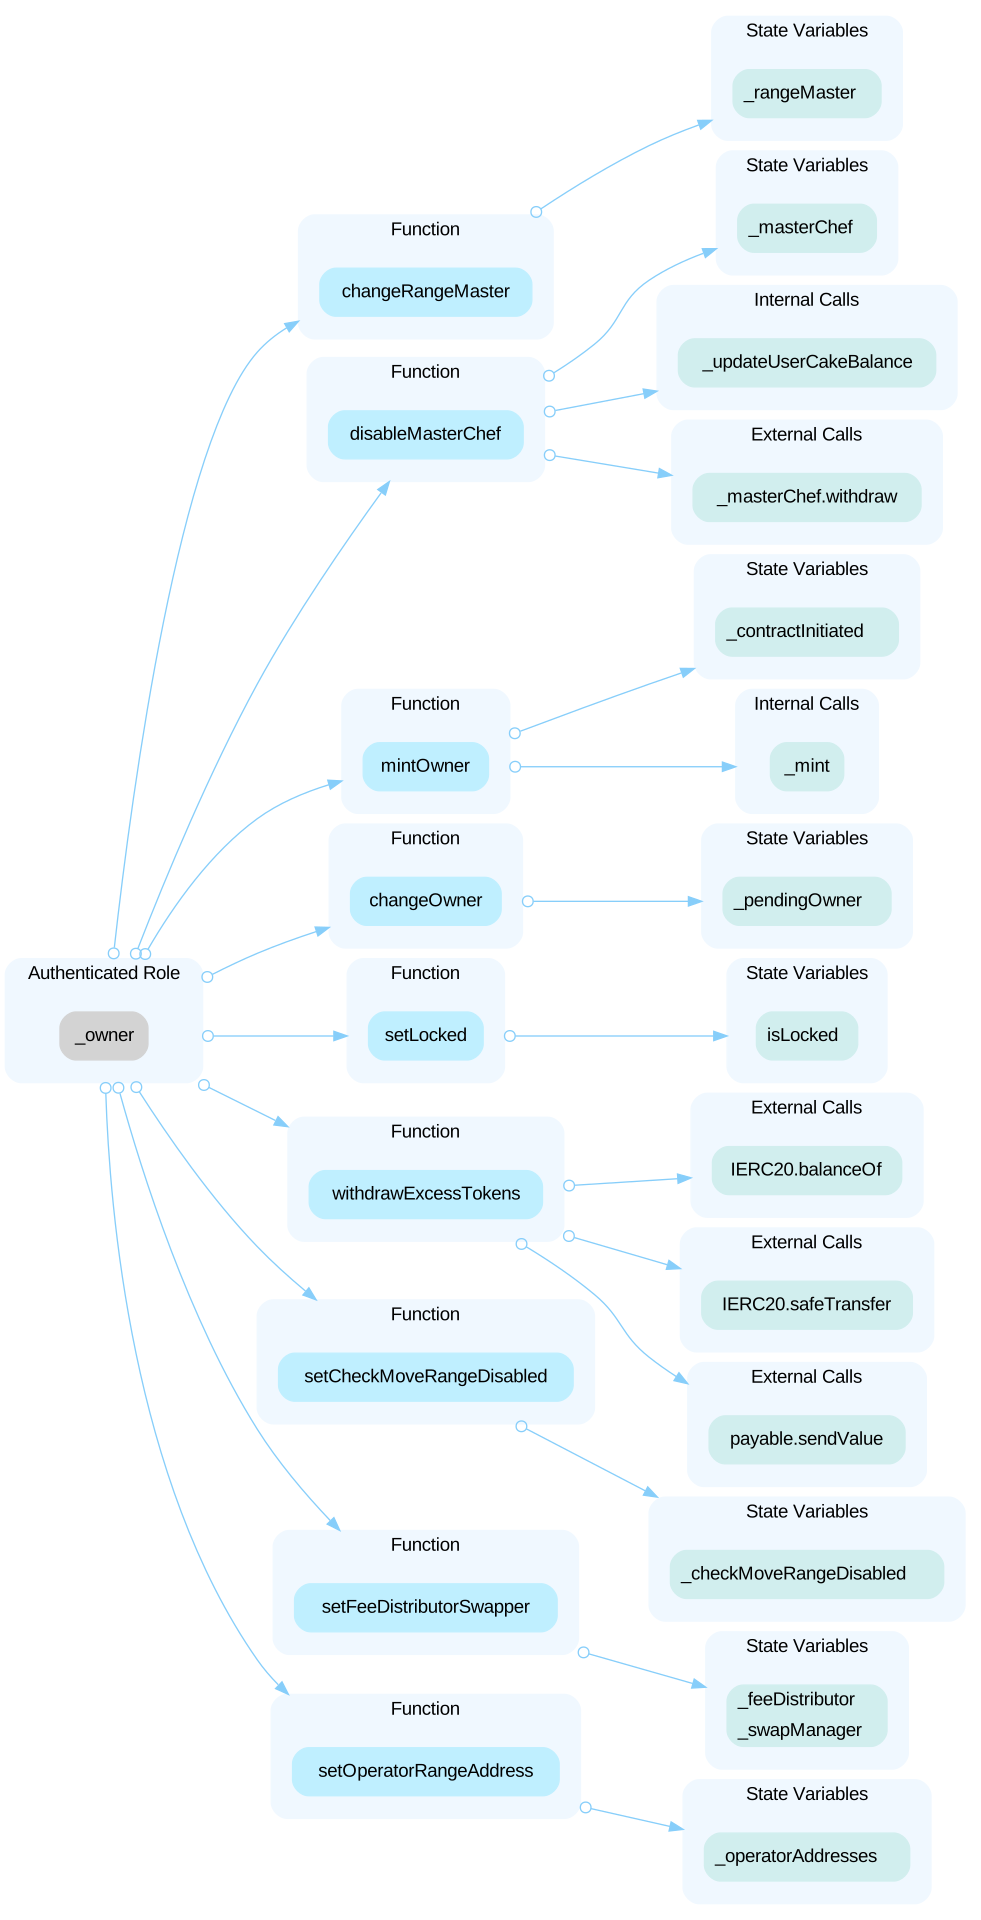 --- In the contract `RangePositionManager` the role `_rangeMaster` has authority over the functions `decreaseLiquidityUser()` and `userCollect()`. Any compromise to the `_rangeMaster` account may allow the hacker to take advantage of this authority and collect or decrease liquidity on behalf of a user without their consent. --- In the contract `RangePositionManager` the role `feeReceiver` has authority over the functions shown in the diagram below. Any compromise to the `feeReceiver` account may allow the hacker to take advantage of this authority and change the `feeReceiver` to an address they have the sole control of to always receive the fees. 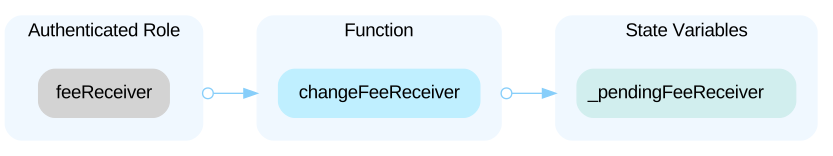 --- In the contract `RangePositionManager` the role `_operatorAddresses` has authority over the functions `moveRange()` and `increaseLiquidityAuto()`. Any compromise to the `_operatorAddresses` account may allow the hacker to take advantage of this authority and move the liquidity so it is at a different position, this includes swapping sub-optimally or so that most of the liquidity is not added to liquidity. In addition, they could increase a users position with the users token0 and token1 balance without their consent. --- ### Swap Manager In the contract `SwapManager` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do the following: - Transfer any ETH or ERC20 token held by the contract to themselves; - Transfer the owner role to an account they have the sole control over. 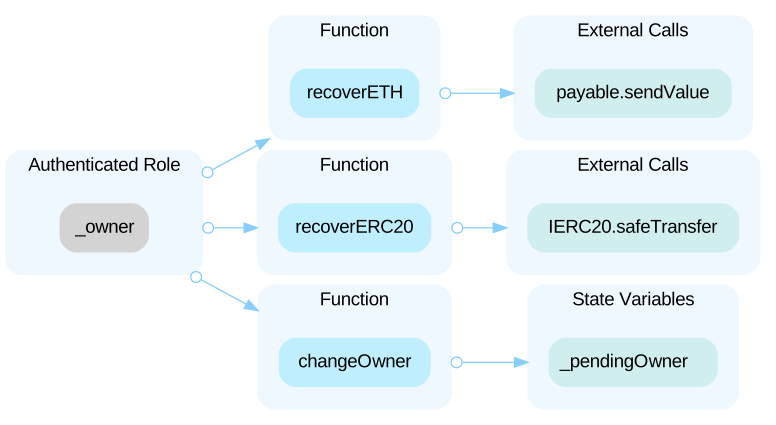 --- ### RewardNFT In the contract `RewardNFT` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do the following: - Change the base URI. - Mint tokens to themselves or any other account up to the `MAX_SUPPLY`. - Set a malicious address as an allowed caller to set users NFTs in use when they are not to den
LowPrice Manipulations Can Affect Ability To Call `mOpen
The `canMoveRange()` function uses the `currentTick` to determine if the range can be moved. The `currentTick` is determined using `slot0` and thus can be manipulated by other entities. A malicious entity could ensure that the range is not moved, when it should be, by manipulating the price just before the transaction so that the `currentTick` lies between the `hardLimitTickUpper` and `hardLimitTickLower`. Similarly, an entity given the privilege to call `moveRange()` could manipulate the tick so it is outside of the `hardLimitTickUpper` and `hardLimitTickLower` allowing them to move the range.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (9)
- contracts/libraries/LiquidityAmounts.sol
- contracts/RangePositionManager.sol
- contracts/FeeDistributor.sol
- contracts/libraries/TickMath.sol
- contracts/RangeMaster.sol
- contracts/libraries/FullMath.sol
- contracts/SwapManager.sol
- contracts/RewardNFT.sol
- contracts/libraries/FixedPoint96.sol
Part of YieldFlow’s security record
 YieldFlow
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us