FlyingClub
CertiK reviewed FlyingClub on 25 Aug 2022: 4 findings, 0 critical; 2 acknowledged, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings4
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 0 | 2 | 0 |
HighCentralization Related RisksOpen
In the contract, `PaperPlane`, the role, `_owner`, has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and disrupt the operation of the NFT token contract. 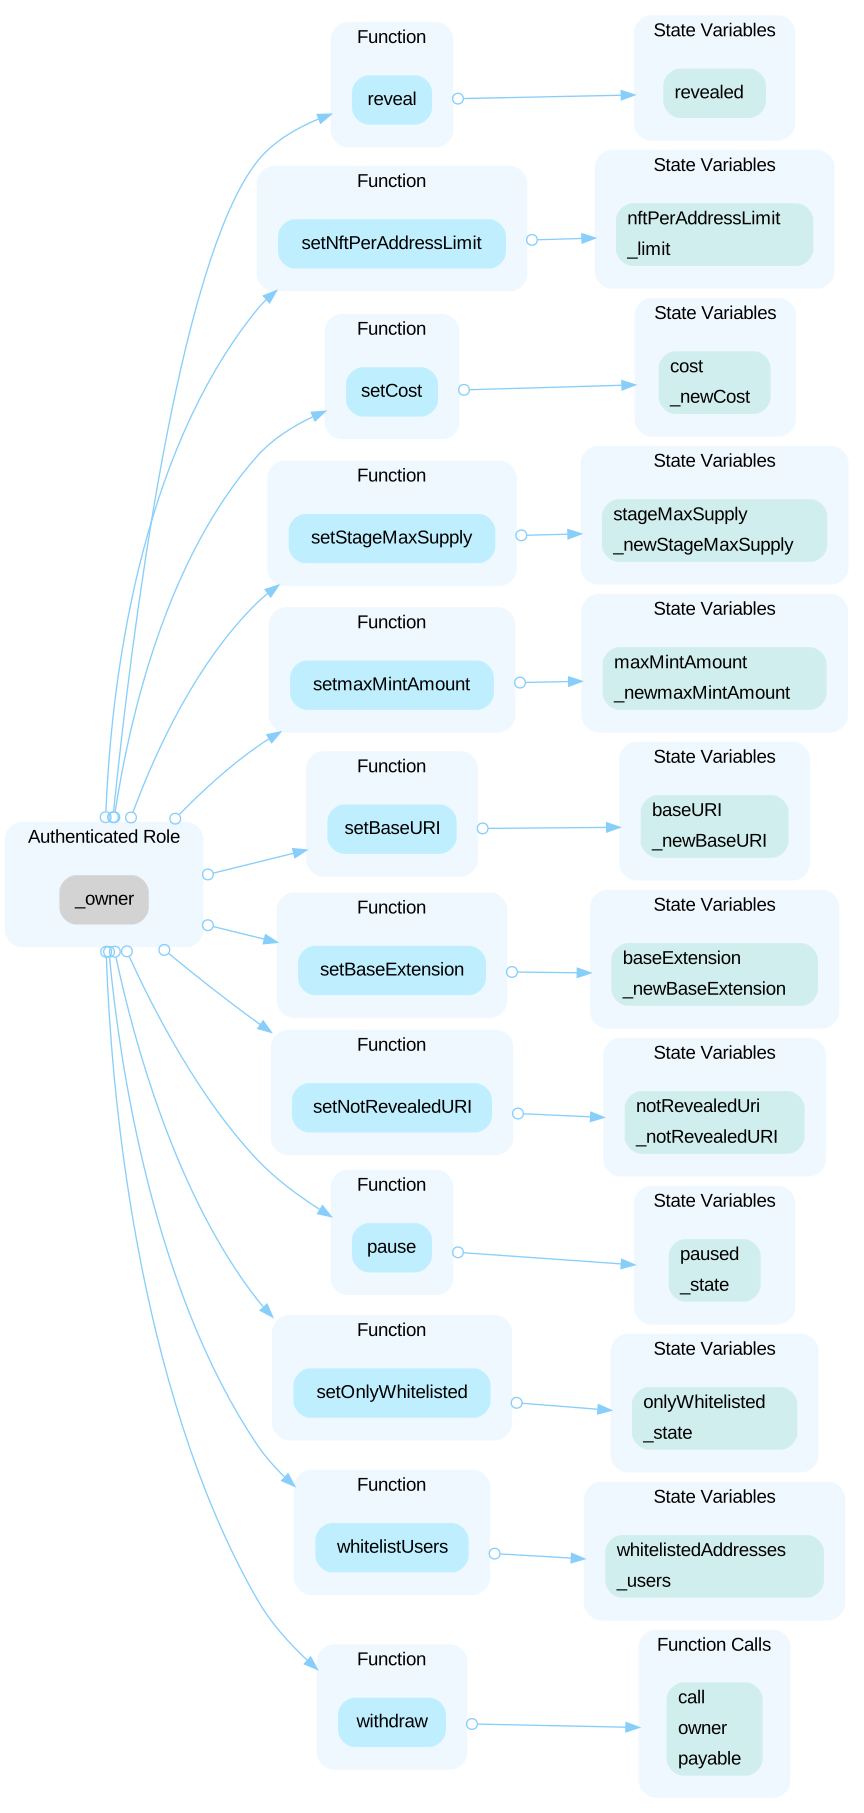
HighContract Owner Can Mint Tokens at No CostOpen
The current implementation allows contract owner to bypass the sanity checks in `mint()` function and mint NFT tokens without paying. ```solidity= if (msg.sender != owner()) { if(onlyWhitelisted == true) { require(isWhitelisted(msg.sender), "user is not whitelisted"); } require(msg.value >= cost * _mintAmount, "insufficient funds"); require(supply + _mintAmount <= stageMaxSupply, "max NFT limit of this stage exceeded"); uint256 ownerMintedCount = addressMintedBalance[msg.sender]; require(ownerMintedCount + _mintAmount <= nftPerAddressLimit, "max NFT per address exceeded"); } for (uint256 i = 1; i <= _mintAmount; i++) { addressMintedBalance[msg.sender]++; _safeMint(msg.sender, supply + i); } ``` Any compromise to the `owner` account may allow the hacker to take advantage of this and over-mint NFT tokens which may damage the whole tokenomics.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- PPTest.sol
Part of FlyingClub’s security record
 FlyingClub
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us