Credbull
CertiK reviewed Credbull on 13 May 2024: 8 findings, 0 critical; 4 marked fixed, 4 acknowledged.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings8
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 0 |
| Medium | 0 | 0 | 2 |
| Low | 0 | 2 | 2 |
HighCentralization Related RisksAcknowledged
In the contract `FixedYieldVault` the role `DEFAULT_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and enable/disable security checks, pause/unpause deposits and withdrawals, and update critical variables. Moreover, the account can withdraw tokens from the contract at any time, it could lead to insufficient tokens available for depositors when attempting to withdraw. 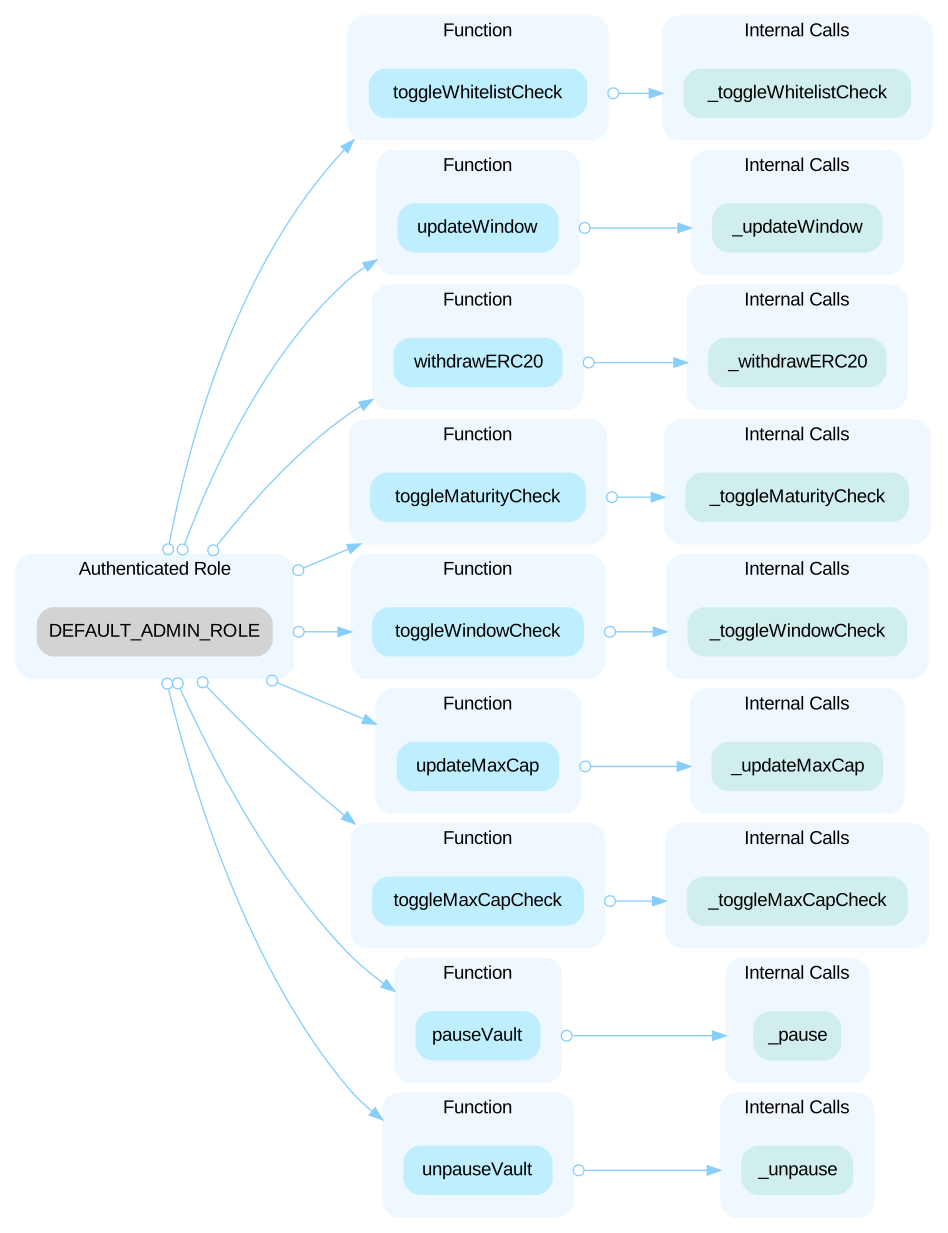 In the contract `FixedYieldVault` the role `OPERATOR_ROLE` has authority over the following function: - mature() Any compromise to the `OPERATOR_ROLE` account may allow a hacker to take advantage of this authority and permit withdrawals. ---- In the contract `UpsideVault` the role `OPERATOR_ROLE` has authority over the following function: - setTWAP() Any compromise to the `OPERATOR_ROLE` account may allow a hacker to take advantage of this authority and set `twap`. ---- In the contract `AccessControl` the role `adminRole` has authority over the following functions: - grantRole() - revokeRole() Any compromise to the `adminRole` account may allow the hacker to take advantage of this authority and grant associated role to any account or revoke the role from any account. Note that `DEFAULT_ADMIN_ROLE` is the admin role for all roles. In the contract `AccessControl` the role `role` has authority over the following function: - renounceRole() Any compromise to the `role` account may allow the hacker to take advantage of this authority and renounce corresponding privileges to functions within other contracts. ----------- In the contract `CredbullKYCProvider` the role `_owner` has authority over the following function: - updateStatus() Any compromise to the `_owner` account may allow a hacker to take advantage of this authority and add/remove addresses from the whitelist. --- In the contract `Ownable` the role `_owner` has authority over the following functions: - transferOwnership() - renounceOwnership() Any compromise to the `_owner` account may allow a hacker to take advantage of this authority and transfer or renounce the ownership. --- In the contract `CredbullFixedYieldVaultFactory` the role `OPERATOR_ROLE` has authority over the following function: - createVault() Any compromise to the `OPERATOR_ROLE` account may allow a hacker to take advantage of this authority and deploy a new `CredbullFixedYieldVault` contract. --- In the contract `CredbullUpsideVaultFactory` the role `OPERATOR_ROLE` has authority over the following function: - createVault() Any compromise to the `OPERATOR_ROLE` account may allow a hacker to take advantage of this authority and deploy a new `CredbullFixedYieldVaultWithUpside` contract. --- In the contract `CredbullVaultFactory` the role `DEFAULT_ADMIN_ROLE` has authority over the following functions: - allowCustodian() - removeCustodian() Any compromise to the `DEFAULT_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and add/remove an account from `allowedCustodians`.
HighCentralization Related Risks in `CUSTODIAN` AddreAcknowledged
The `CredbullBaseVault` contract utilizes a designated `CUSTODIAN` address to receive tokens from depositors. This setup centralizes the control of deposited assets to a single account. If this custodian account is compromised, malicious actors could misuse the assets, potentially resulting in the contract not having sufficient funds to fulfill withdrawal requests by legitimate depositors.
LowIncompatibility With Deflationary Tokens (Non-staAcknowledged
The vault contracts are not equipped to handle non-standard ERC20 tokens, including deflationary or rebase tokens, which may apply transaction fees or adjust balances dynamically. The contract's reliance on `transferFrom()` and `transfer()` methods without validating the actual transferred amounts could result in discrepancies between expected and actual token balances. This issue is particularly critical because it could lead to insufficient tokens available for depositors when attempting to withdraw, potentially disrupting contract functionality and user transactions.
LowThird-Party DependenciesAcknowledged
The contract is serving as the underlying entity to interact with third-parties asset token and collateral token. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (15)
- packages/contracts/src/plugins/WindowPlugIn.sol
- packages/contracts/src/factories/CredbullUpsideVaultFactory.sol
- packages/contracts/src/vaults/FixedYieldVault.sol
- packages/contracts/src/CredbullKYCProvider.sol
- packages/contracts/src/factories/CredbullFixedYieldVaultFactory.sol
- packages/contracts/src/CredbullFixedYieldVaultWithUpside.sol
- packages/contracts/src/base/CredbullBaseVault.sol
- packages/contracts/src/plugins/MaxCapPlug.sol
- packages/contracts/src/interface/IKYCProvider.sol
- packages/contracts/src/interface/ICredbull.sol
- packages/contracts/src/vaults/UpsideVault.sol
- packages/contracts/src/CredbullFixedYieldVault.sol
- packages/contracts/src/plugins/WhitelistPlugIn.sol
- packages/contracts/src/extensions/MaturityVault.sol
- packages/contracts/src/factories/CredbullVaultFactory.sol
Part of Credbull’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us