VaporFi
CertiK reviewed VaporNodes (VaporFi) on 3 Nov 2022: 15 findings, 0 critical; 1 marked fixed, 14 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings15
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 6 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 8 | 0 | 1 |
HighCentralization Risks in MasterChef.solOpen
In the contract `MasterChef` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 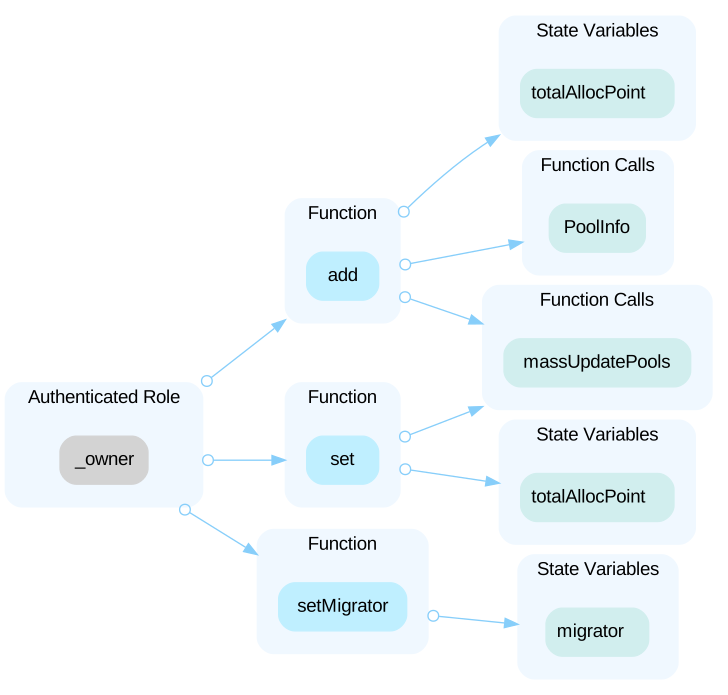 In the contract `MasterChef` the role `devaddr` has authority over the functions shown in the diagram below. Any compromise to the `devaddr` account may allow the hacker to take advantage of this authority. 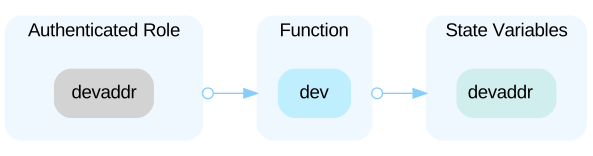
HighCentralization Risks in Migrator.solOpen
In the contract `Migrator` the role `chef` has authority over the functions shown in the diagram below. Any compromise to the `chef` account may allow the hacker to take advantage of this authority. 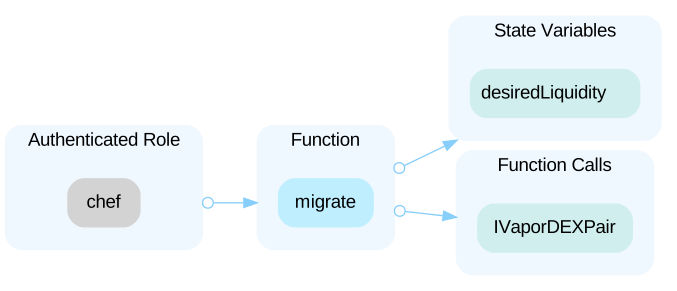
HighCentralization Risks in MoneyMaker.solOpen
In the contract `MoneyMaker` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 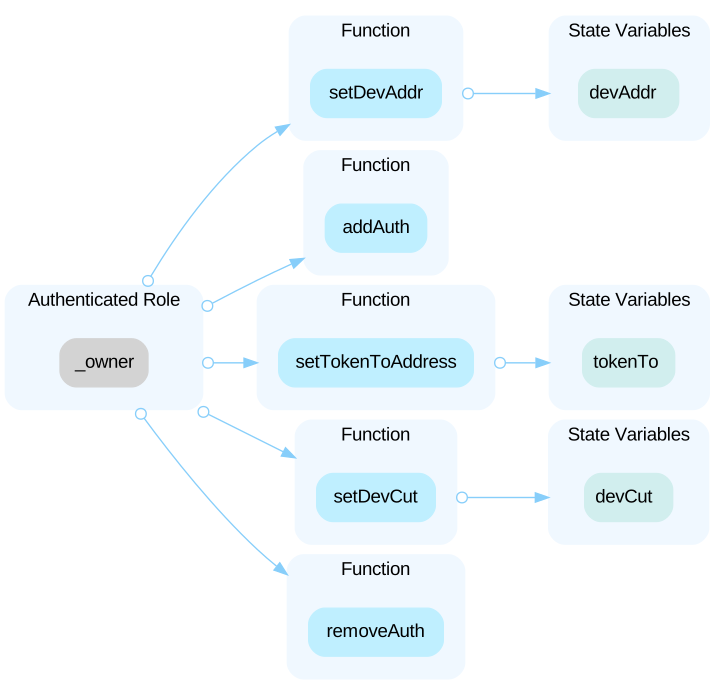
HighCentralization Risks in StableVapeStaking.solOpen
In the contract `StableVapeStaking` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 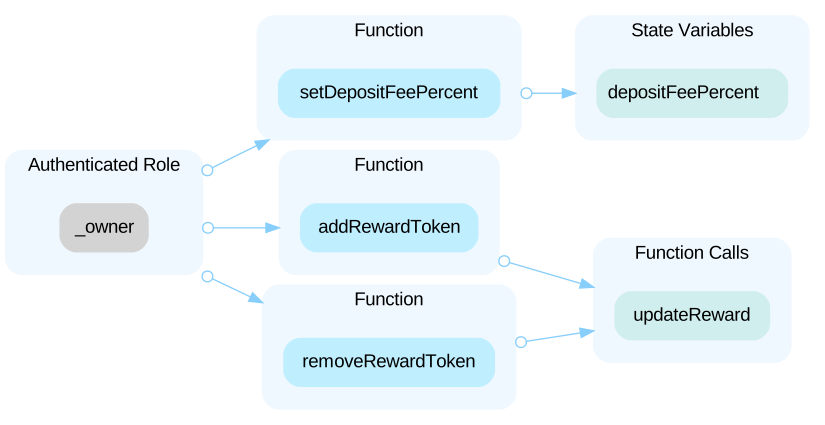
HighCentralization Risks in VapeToken.solOpen
In the contract `VapeToken` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 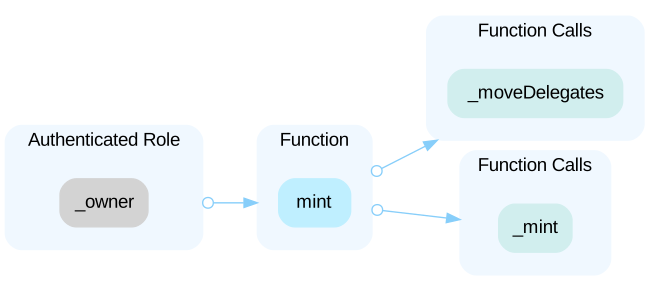
HighCentralized Control of Contract UpgradeOpen
StableVapeStaking are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
Low`add()` Function Not RestrictedOpen
When the same LP token is added into a pool more than once in function `add()`, the total amount of reward in function `updatePool()` will be incorrectly calculated. The current implementation is relying on the operation correctness to avoid repeatedly adding the same LP token to the pool, as the function will only be called by the owner.
LowImproper Usage of `public` and `external` TypeOpen
`public` functions that are never called by the contract could be declared as `external`. `external` functions are more efficient than `public` functions.
LowIncompatibility With Deflationary TokensOpen
When transferring standard ERC20 deflationary tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user stakes 100 deflationary tokens (with a 10% transaction fee) in a MasterChef, only 90 tokens actually arrived in the contract. However, the user can still withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. The MasterChef takes the pool token balance(the `lpSupply`) into account when calculating the users' reward. An attacker can repeat the process of deposit and withdraw to lower the token balance(`lpSupply`) in a deflationary token pool and cause the contract to increase the reward amount. Reference: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f
LowMisleading Result of Multiplier CalculationOpen
In the function `MasterChef.getMultiplier()`, the multiplier should be calculated by the following formula: ```solidity (number of blocks with bonus) * BONUS_MULTIPLIER + (number of blocks without bonus) ``` However, `startBlock`, which is set in L96, is not considered in the calculation. When the function is triggered by `MasterChef.pendingVape()` and `MasterChef.updatePool()`, the input variables `_from` and `_to` are always greater than `startBlock`, so it is unnecessary to consider `startBlock`. Given the `MasterChef.getMultiplier()` is a public function, which means it can be called externally, all possibilities of the input need to be fully considered. For example, if `_from < startBlock` and `_to < startBlock`, the multiplier should be `_from.sub(startBlock).mul(BONUS_MULTIPLIER)`, rather than `_to.sub(_from).mul(BONUS_MULTIPLIER)` which is calculated in the function.
Show 4 more
LowMissing Emit EventsOpen
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
LowOver Minted TokenOpen
`updatePool()` function minted 100% + 10% (dev fee is included as 10% of the 100%) of total rewards.
LowPotential Reentrancy RisksOpen
Please check out if there are any `checks-effects-interactions` violations in the above functions.
LowVariables That Could Be Declared as ImmutableOpen
The linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (6)
- VapeToken.sol
- Migrator.sol
- MasterChef.sol
- MoneyMaker.sol
- VapeBar.sol
- StableVapeStaking.sol
Part of VaporNodes’s security record
 VaporNodes
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us