WEMIX Swap & DIOS(Dollar in and out Stabilizer)
CertiK reviewed WEMIX (WEMIX Swap & DIOS(Dollar in and out Stabilizer)) on 18 Oct 2022: 24 findings, 0 critical; 15 marked fixed, 9 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings24
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 4 | 0 | 1 |
| Medium | 1 | 0 | 1 |
| Low | 4 | 0 | 13 |
HighCentralization Related Risks in `owner` roleOpen
In the contract `DollarInAndOutStaking` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 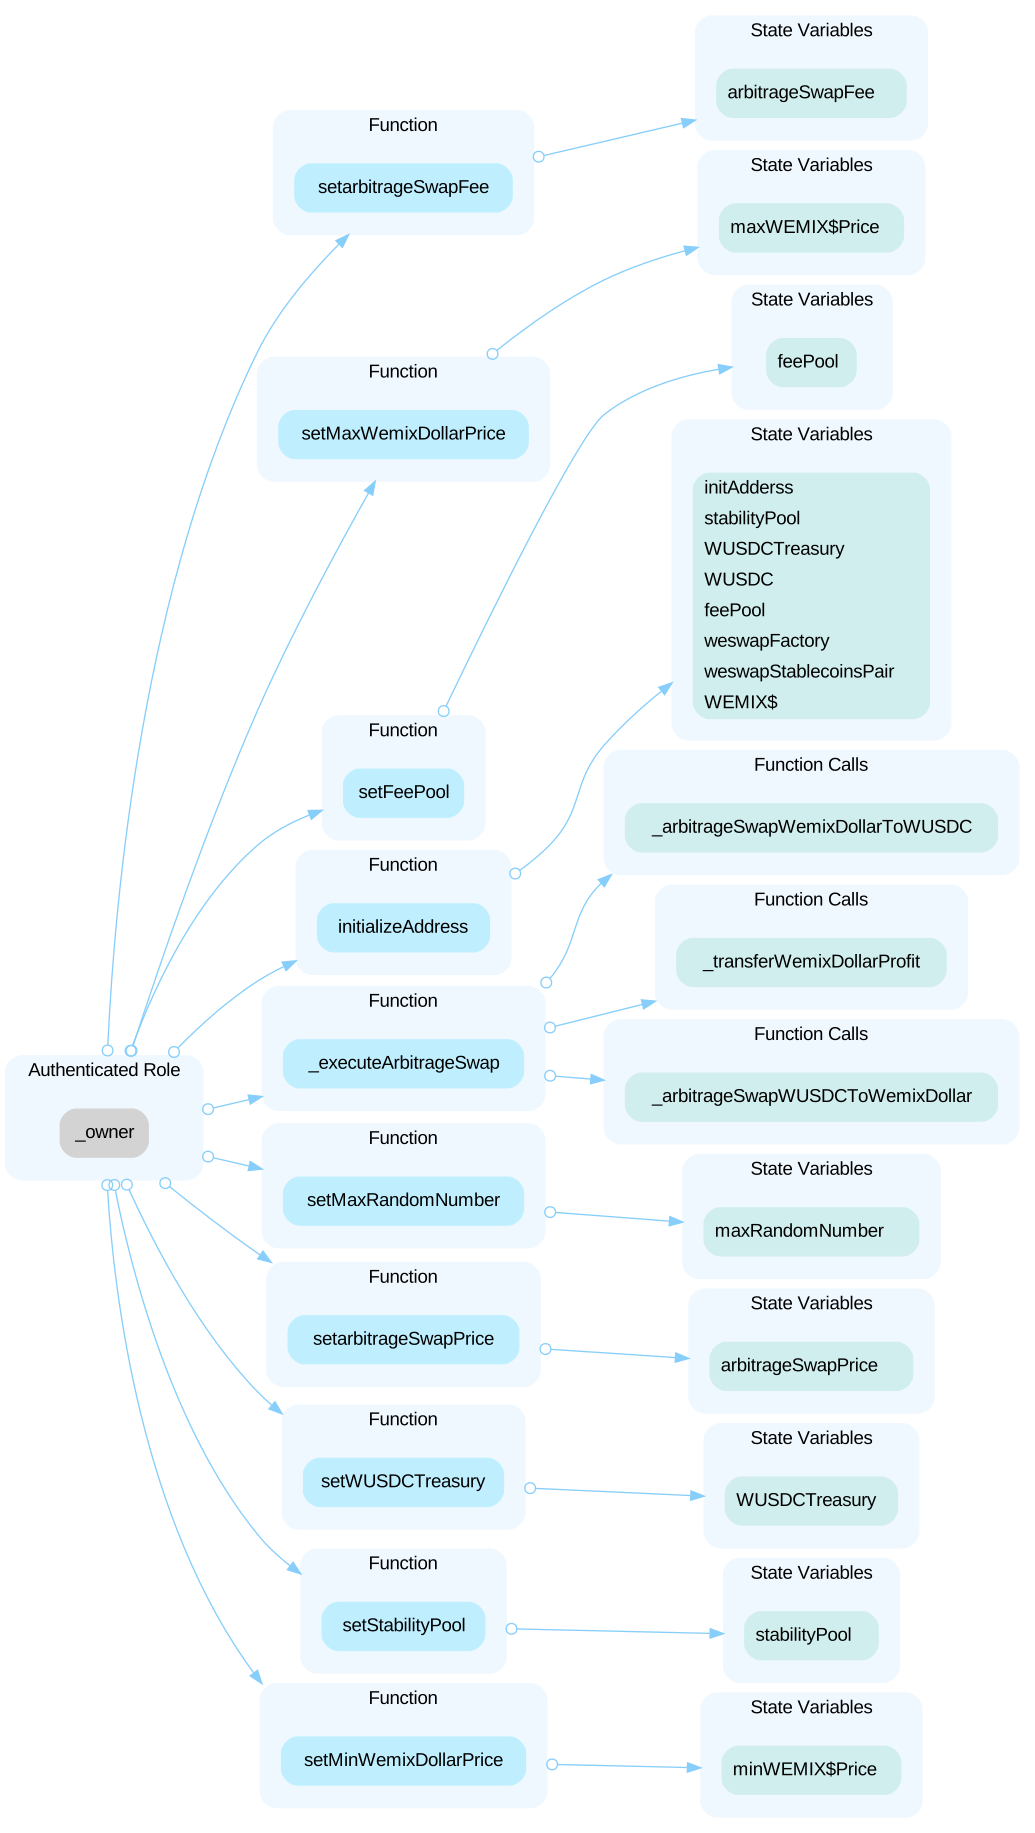 In the contract `WUSDCTreasury` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 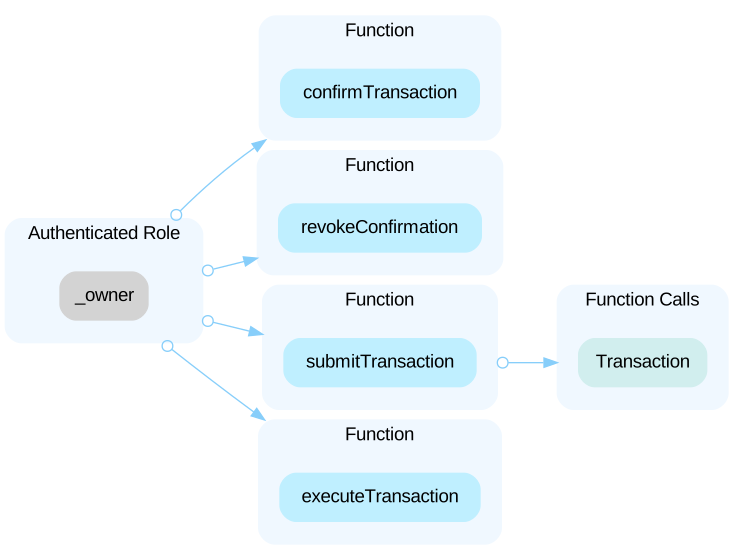 In the contract `WemixDollar` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 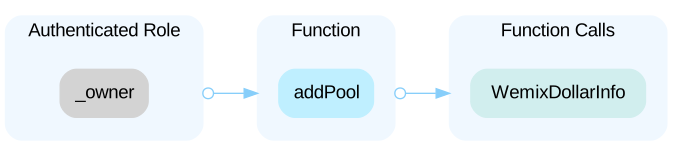 In the contract `WeswapFactory` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 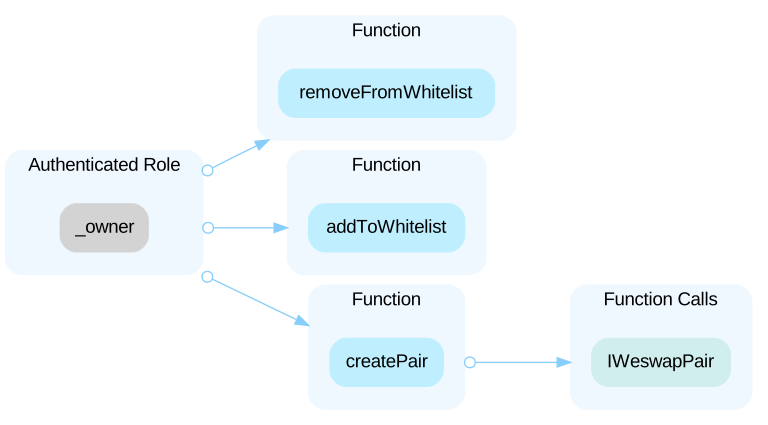 In the contract `ZapBase` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 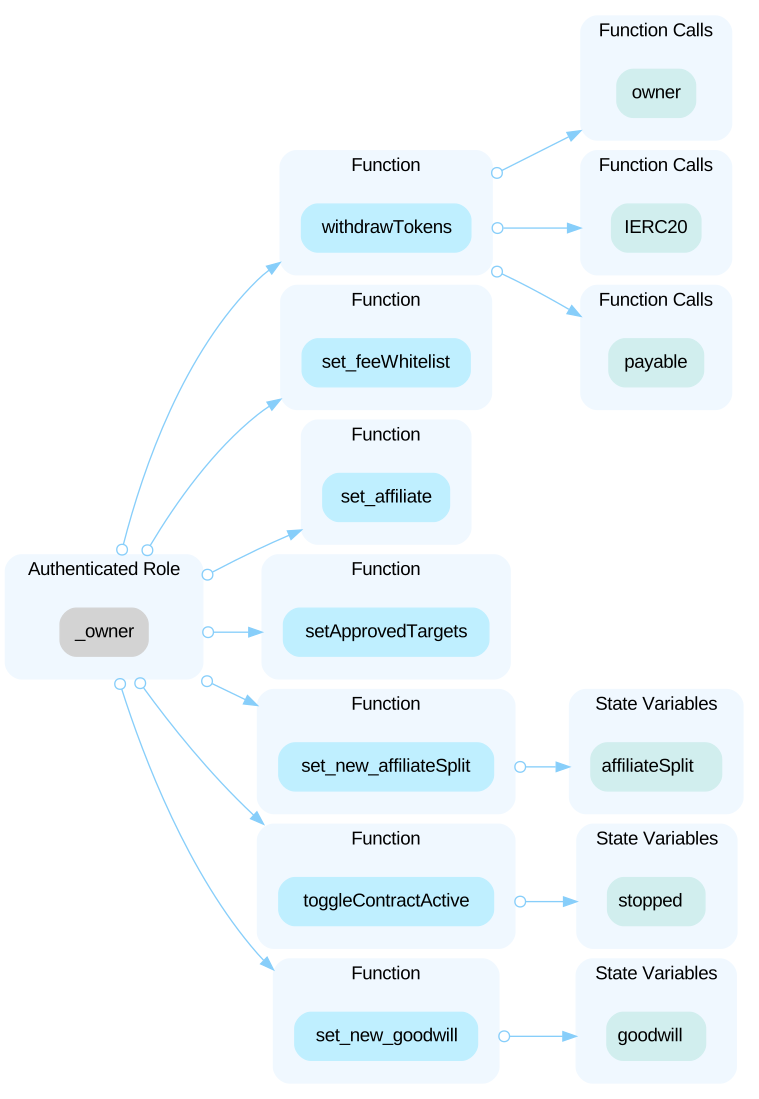 In the contract `WemixDollarExchange` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority. 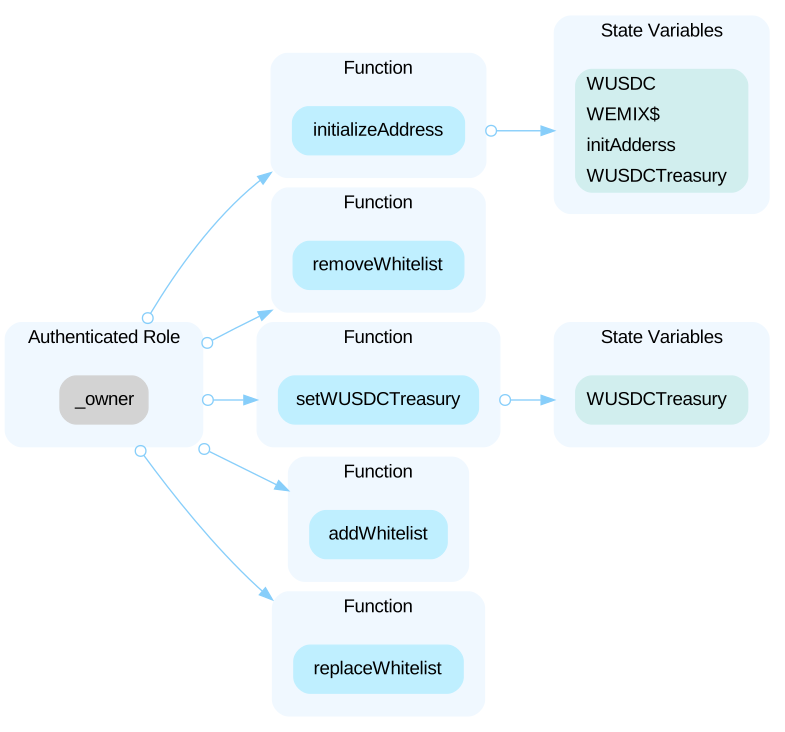
HighCentralization Related Risks in the `breaker` andOpen
In the contract `DollarInAndOutStaking` the role `breaker` has authority over the functions shown in the diagram below. Any compromise to the `breaker` account may allow the hacker to take advantage of this authority. 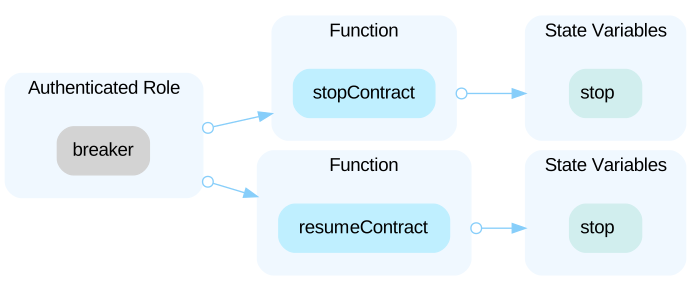 In the contract `WemixDollarExchange` the role `breaker` has authority over the functions shown in the diagram below. Any compromise to the `breaker` account may allow the hacker to take advantage of this authority. 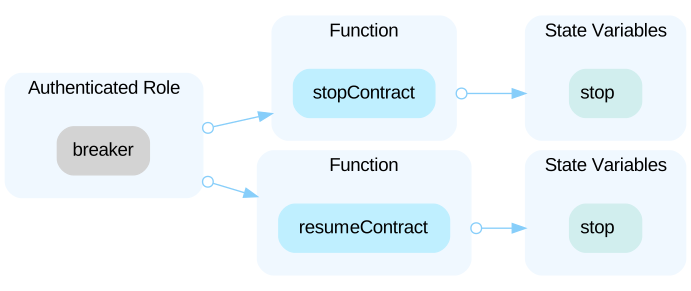 In the contract `WeswapPair` the role `breaker` has authority over the functions shown in the diagram below. Any compromise to the `breaker` account may allow the hacker to take advantage of this authority. 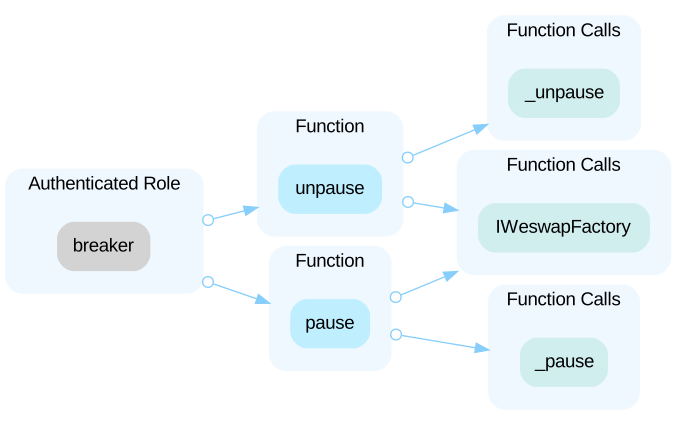 In the contract `DollarInAndOutStaking` the role `breakerSetter` has authority over the functions shown in the diagram below. Any compromise to the `breakerSetter` account may allow the hacker to take advantage of this authority. 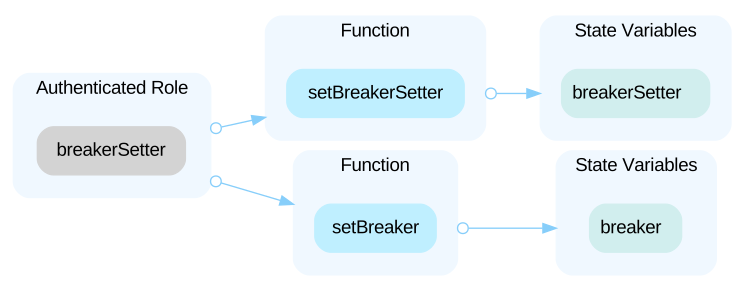 In the contract `WemixDollarExchange` the role `breakerSetter` has authority over the functions shown in the diagram below. Any compromise to the `breakerSetter` account may allow the hacker to take advantage of this authority and [fixme, describe what hacker can do and the impact]. 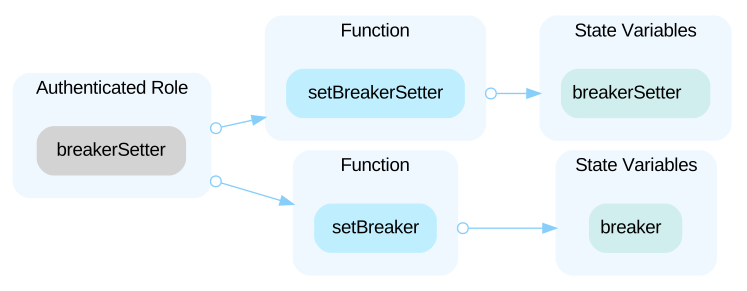 In the contract `WeswapFactory` the role `breakerSetter` has authority over the functions shown in the diagram below. Any compromise to the `breakerSetter` account may allow the hacker to take advantage of this authority. 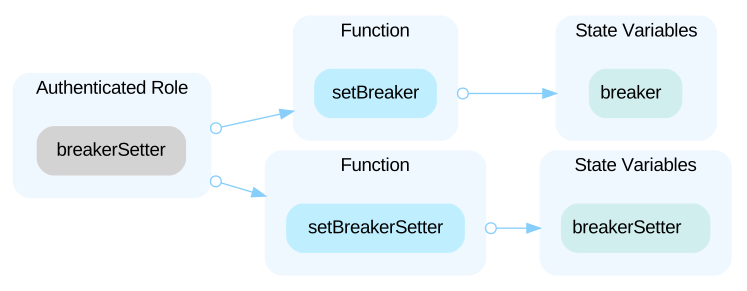 Also, in the contract `WeswapPair` the role `factory` has authority over the functions shown in the diagram below, however, this role would be granted to the `WeswapFactory` to make it work, which would lower the risk. 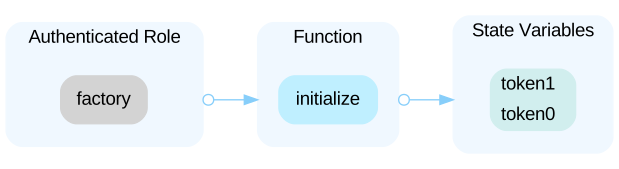
HighCentralization Related Risks in the `WhitelistAddOpen
In the contract `WemixDollar`, the role `WhitelistAddress` has authority over the following functions: - function mint(), the privileged role could mint any amount of `WemixDollar` unlimitedly to anyone. - function burn(), the privileged role could burn any amount of `WemixDollar` from anyone. Any compromise to the `WhitelistAddress` account may allow a hacker to take advantage of this authority.
HighCentralization Risks in `feeToSetter` roleOpen
In the contract `WeswapFactory` the role `feeToSetter` has authority over the functions shown in the diagram below. Any compromise to the `feeToSetter` account may allow the hacker to take advantage of this authority. 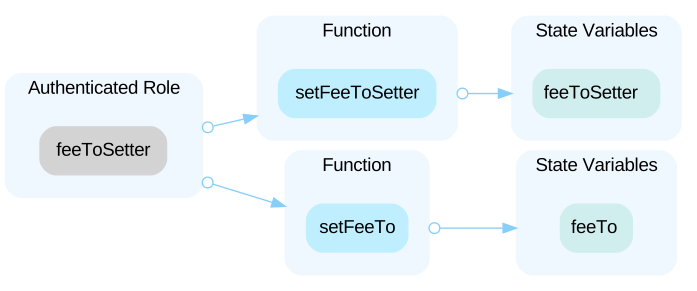
MediumFinancial ModelsOpen
In the project `Wemix`, the team designed a pair of tokens, the `WemixDollar` and `WUSDC`, they could always be swapped to each other by the ratio of 1:1. The codes of `WUSDC` is unknown, yet the `WemixDollar` could be unlimited minting, the reserves of the `WemixDollar-WUSDC` pool are always changing, hence there are huge arbitrage opportunities here that investors may change the higher price token to the lower and swap back by the 1:1 ratio to win profits. Hence these two tokens could be regarded as algorithm stable tokens. Besides, the protocol wrapped the `addliquidity()` and `removeliquidity()` functions and provided the investors more functions to call, which they could add or remove liquidity with one or two of the paired tokens, or any other tokens, while more taxes will be charged as `goodwill` or `affiliation`. Also, the `WWEMIX` token is issued to replace the function of `WETH`.
LowExplanation on the use of `_swapTarget`Open
In the function `_fillQuote()`, the `_swapTarget` address is used to receive ETH and execute some external functions which are unknown, could you please provide with us more information about the `_swapTarget`?
LowMathematical calculationsOpen
Please provide with us more documentation about the design of these mathematical calculations.
LowNull wallet adddressOpen
The `WEMIXAddress` as `0xEeeeeEeeeEeEeeEeEeEeeEEEeeeeEeeeeeeeEEeE` is a null wallet address.
LowUnknown implementation when calling `executeTransOpen
When calling `executeTransaction()`, the executing codes are passed by `transaction.data` and unknown to the audit scope. Besides, there are ETHs transferred to the `to` address, we would also like to know the source of the ETHs.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (34)
- contracts/interfaces/IWeswapZapIn.sol
- contracts/WeswapERC20.sol
- contracts/interfaces/IWUSDC.sol
- contracts/WemixDollarExchange.sol
- contracts/interfaces/IWeswapZapOut.sol
- contracts/WUSDCTreasury.sol
- contracts/WeswapRouter.sol
- contracts/WeswapFactory.sol
- contracts/interfaces/IWemixDollarExchange.sol
- contracts/libraries/WeswapV2LiquidityMathLibrary.sol
- contracts/interfaces/IWWEMIX.sol
- contracts/extensions/HellowWorld.sol
- contracts/libraries/WeswapLibrary.sol
- contracts/interfaces/IWemixDollar.sol
- contracts/libraries/Math.sol
- contracts/interfaces/IWeswapCallee.sol
- contracts/libraries/TransferHelper.sol
- contracts/DollarInAndOutStaking.sol
- contracts/interfaces/IDollarInAndOutStaking.sol
- contracts/tokens/WemixDollar.sol
- contracts/WeswapZapIn.sol
- contracts/libraries/UQ112x112.sol
- contracts/interfaces/IWeswapPair.sol
- contracts/interfaces/IWUSDCTreasury.sol
- contracts/interfaces/IWeswapERC20.sol
- contracts/tokens/WWEMIX.sol
- contracts/interfaces/IWeswapFactory.sol
- contracts/interfaces/IERC20.sol
- contracts/WeswapPair.sol
- contracts/WeswapZapOut.sol
- contracts/utils/Utils.sol
- contracts/ZapBase.sol
- contracts/libraries/Babylonian.sol
- contracts/interfaces/IWeswapRouter.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,044 projects reviewed · 1,393 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us