Kudoe Audit
CertiK reviewed DOE on SOL (Kudoe Audit) on 14 Mar 2023: 18 findings, 3 critical; 7 marked fixed, 11 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings18
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 3 |
| High | 2 | 0 | 1 |
| Medium | 0 | 0 | 0 |
| Low | 9 | 0 | 3 |
HighCentralization Risks in DOEStaking.solOpen
In the contract `DOEStaking` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and - set the reward, duration, nft reward weight, and maximum NFT eligible for rewards through `setRewardParams()` - enable or disable reward for multiple nfts through `setMultiNftReward()` - set the gDoe address through `setgDOE()` - withdraw all reward tokens through `withdrawReward()` 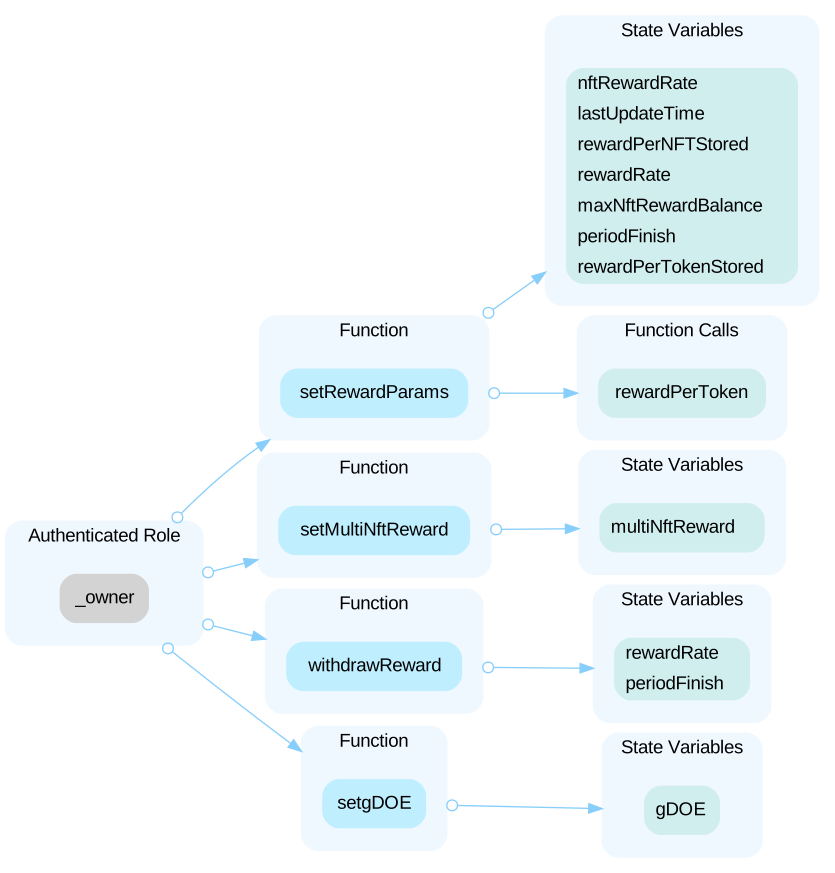
HighInitial Token DistributionOpen
All of the `Kudoe` tokens are sent to the contract deployer when deploying the contract. This could be a centralization risk as the deployer can distribute tokens without obtaining the community's consensus. ```solidity=226 _tOwned[_owner] = _tTotal; ``` The designed allocation are explained in the documentation (https://kudoe-tm.gitbook.io/kudoe-tm/kdoe-token/token-allocation). As of 01/27/2023, the project is deployed and `Kudoe` tokens are distributed to multiple addresses. - Approximately 34% are in the `Team Finance Lock` contract. - Approximately 10% are in the `KDOERewards` contract. - Approxmately 10% are in the project's liquidity wallet. - Approximately 2.6% are in the project's staking wallet. - Approximately 2% are in the project's gaming wallet. - Approximately 1% are in the project's team wallet. - Approximately 1% are in the project's development wallet. - Approximately 0.75% are in the project's marketing wallet. The detailed holder list can be found on the Ethereum address [0x5f190f9082878ca141f858c1c90b4c59fe2782c5](https://etherscan.io/token/0x5f190f9082878ca141f858c1c90b4c59fe2782c5#balances)
Low`gDOEstakers` Status in `withdraw()`Open
In the current control flow, once the user calls `stakeForgDOE()`, `gDOEstaker` would be set true and cannot be set back to false thus the user will not be able to withdraw `stakedToken` through `withdraw()`.
LowIncompatibility With Deflationary TokensOpen
When transferring standard ERC20 deflationary tokens, the input amount may not be equal to the received amount due to the charged transaction fee. The contract takes the staked token balance into account when calculating the users' reward. An attacker can repeat the process of deposit and withdrawing to lower the token balance in a deflationary token pool and cause the contract to increase the reward amount.
LowMissing Emit EventsOpen
The function that affects the status of sensitive variables should be able to emit events as notifications to users.
LowMissing Error MessagesOpen
The **require** can be used to check for conditions and throw an exception if the condition is not met. It is better to provide a string message containing details about the error that will be passed back to the caller.
LowPotential Incorrect Checks for Fee RatiosOpen
When setting the ratios of fees that will be distributed to liquidity, marketing, development and burn account, the following require statement is applied to ensure the total ratio are smaller than the sum of buy and sell fees. ```solidity=448 function setRatios(uint16 liquidity, uint16 marketing, uint16 development, uint16 burn) external onlyOwner { _ratios.liquidity = liquidity; _ratios.marketing = marketing; _ratios.development = development; _ratios.burn = burn; _ratios.totalSwap = liquidity + marketing + development; uint256 total = _taxRates.buyFee + _taxRates.sellFee; require(_ratios.totalSwap + _ratios.burn <= total, "Cannot exceed sum of buy and sell fees."); } ``` However, the `_ratios` represent the portion of the **charged fees** that will be distributed to different addresses, rather than the portion of the transferred amount. Therefore, the `require` statement is not reasonable and may lead to unexpected revert when changing ratios. For example, the current ratio is set as ```text liquidity: 400 marketing: 200 development: 400 burn: 200 totalSwap: 1000 ``` and the fee is: ```text buyFee: 700 sellFee: 700 transferFee: 0 ``` If both the buy fee and sell fee are decreased to 500, the ratio number of burn and totalSwap will become invalid. Thus, if the team wants to keep the same ratio, both the burn ratio and the total swap ratio need to be changed accordingly.
LowPotential Incorrect Hardcode AddressOpen
In the contract's `constructor()` function, Kudoe is initialized to exclude the fee for PinkLock and Unicrypt (ETH). However, there is no similar logic to check the `block.chainid` for these three lock address. - PinkLock([0x407993575c91ce7643a4d4cCACc9A98c36eE1BBE](https://bscscan.com/address/0x407993575c91ce7643a4d4ccacc9a98c36ee1bbe#code)) was deployed in the Binance Smart Chain, while in the Ethereum, [0x407993575c91ce7643a4d4cCACc9A98c36eE1BBE]{https://etherscan.io/address/0x407993575c91ce7643a4d4ccacc9a98c36ee1bbe} is an EOA address - Unicrypt ([0x663A5C229c09b049E36dCc11a9B0d4a8Eb9db214]{https://etherscan.io/address/0x663a5c229c09b049e36dcc11a9b0d4a8eb9db214}) was deployed in the Ethereum, while in the Binance Smart Chain, it's an EOA address. Same situation with another Unicrypt address (0xDba68f07d1b7Ca219f78ae8582C213d975c25cAf)
LowPotential Insufficient RewardOpen
According to the code logic, the calculation of nft rewards is based on the number of reward tokens acquired and the number of nft staked by the user, and this part of the calculation can be difficult to predict. There may be a shortage of reward tokens, and particularly users may suffer losses if the reward tokens and staked tokens are the same.
LowReturn Values Not HandledOpen
The return values of the low-level calls to transfer ETH are not properly handled. ```solidity=589 if (ratios.marketing > 0) { (success,) = _taxWallets.marketing.call{value: marketingBalance, gas: 35000}(""); } if (ratios.development > 0) { (success,) = _taxWallets.development.call{value: developmentBalance, gas: 35000}(""); } if (ratios.liquidity > 0) { (success,) = _taxWallets.liquidity.call{value: liquidityBalance, gas: 35000}(""); } ``` Therefore, if the call fails to transfer ETH to the corresponding address, it may result in the loss of some ETH as a fee for the corresponding address.
Show 1 more
LowWithdrawing `stakedToken` through `gDOE`Open
`_gDOEstakers` may get extra `stakedToken` through `withdrawForgDOE()`.
Contracts in scope3
| Address | Chain | Source code |
|---|---|---|
| 0x5f190f9082878ca141f858c1c90b4c59fe2782c5 | Chain: Ethereum | Source code: Verified source |
| 0xef732cd262076e3cec7a1d4e96b052d57b383e69 | Chain: Ethereum | Source code: Verified source |
| 0xf541ab2f4dba2071b12da99a9ee83b0c4b719d95 | Chain: Ethereum | Source code: Verified source |
Part of DOE on SOL’s security record
 DOE on SOL
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us