IDRX
CertiK reviewed IDRX on 7 Jul 2023: 10 findings, 0 critical; 6 marked fixed, 4 acknowledged.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings10
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 4 | 1 |
| Medium | 0 | 0 | 2 |
| Low | 0 | 0 | 3 |
HighArbitrary account blacklisting leading to potentiAcknowledged
The contract provides an arbitrary account blacklisting feature, where a privileged role (holder of `BLACKLIST_ROLE`) can blacklist a user's account, and then destroy any funds held in the blacklisted account.
HighCentralization Related RisksAcknowledged
In the contract `IDRX` the priviledge roles have authority over the functions shown in the diagram below. 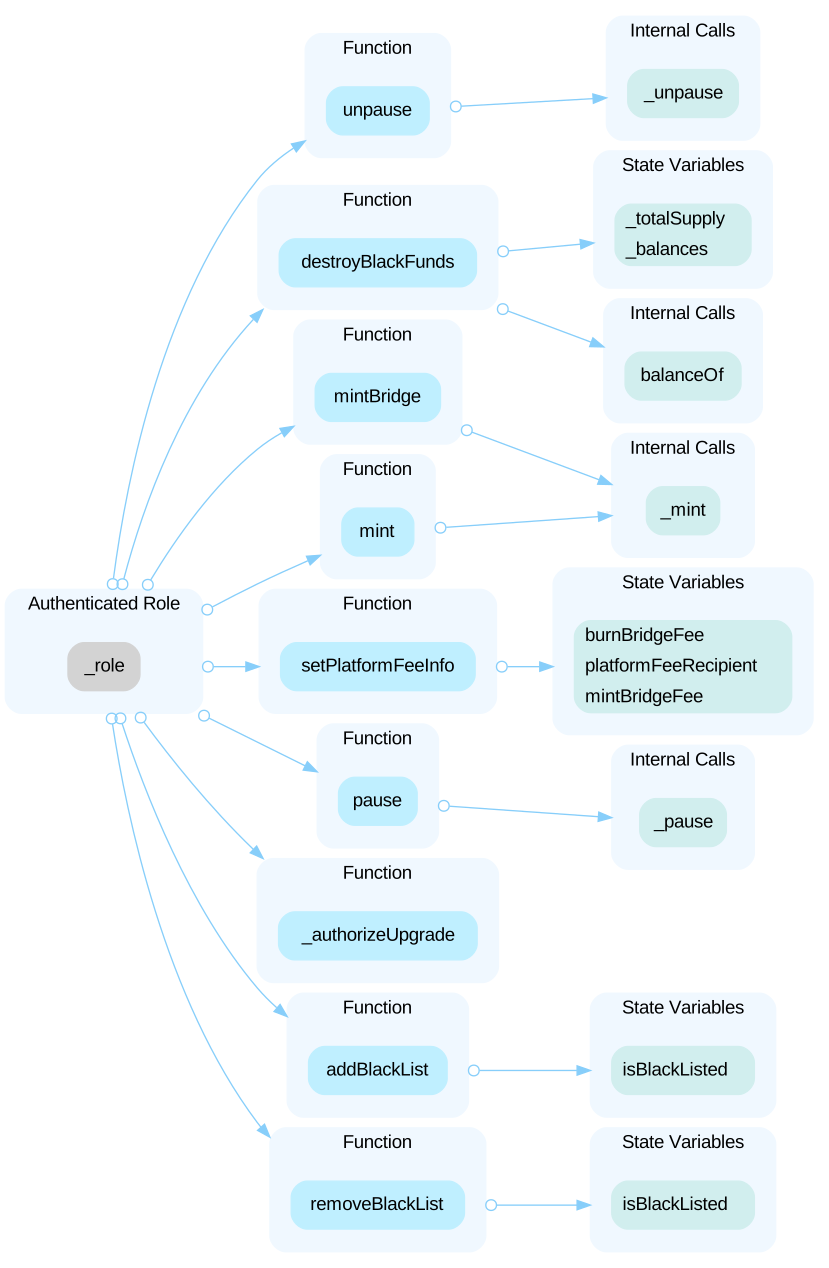 - `pause()`: Pauses all token transfer functionality. Only accessible to addresses with the `PAUSER_ROLE`. - `unpause()`: Unpauses the token transfer functionality. Only accessible to addresses with the `PAUSER_ROLE`. - `mint(address to, uint256 amount)`: Mints the specified amount of tokens to the specified address. Only accessible to addresses with the `MINTER_ROLE`. - `mintBridge(address to, uint256 amount, uint fromChain, uint fromChainBridgeNonce)`: Mints tokens and transfers them to a bridge after deducting a fee. Only accessible to addresses with the `MINTER_ROLE`. - `_authorizeUpgrade(address newImplementation)`: Authorizes a new implementation for the contract. Only accessible to addresses with the `UPGRADER_ROLE`. - `addBlackList(address _evilUser)`: Adds the specified address to the blacklist. Only accessible to addresses with the `BLACKLIST_ROLE`. - `removeBlackList(address _clearedUser)`: Removes the specified address from the blacklist. Only accessible to addresses with the `BLACKLIST_ROLE`. - `destroyBlackFunds(address _blackListedUser)`: Destroys the funds of a blacklisted address. Only accessible to addresses with the `BLACKLIST_ROLE`. - `setPlatformFeeInfo(address _platformFeeRecipient, uint64 _burnBridgeFee, uint64 _mintBridgeFee)`: Sets the platform fee recipient and the fees for burning and minting on the bridge. Only accessible to addresses with the `MINTER_ROLE`. Any compromise to the `_role` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project.
HighCentralized Balance ManipulationAcknowledged
In the contract `IDRX`, the role `MINTER_ROLE` has the authority to update the token balance of an arbitrary account without sanity restriction. Any compromise to the `MINTER_ROLE` account may allow a hacker to take advantage of this authority and manipulate users' balances by calling `mint()` and/or `mintBridge()` functions
HighCentralized Control of Contract UpgradeAcknowledged
The privileged role has the authority to update the implementation contract behind the proxy contract. Any compromise to the privileged account may allow a hacker to take advantage of this authority and change the implementation contract which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
Contracts in scope2
| Address | Chain | Source code |
|---|---|---|
| 0x20fad183dc35f4ae0d1d125ae2f3c4c43a53bbd0 | Chain: Polygon (POS) | Source code: Verified source |
| 0x649a2da7b28e0d54c13d5eff95d3a660652742cc | Chain: Polygon (POS) | Source code: Verified source |
Part of IDRX’s security record
 IDRX
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us