Wemix Retainer 38 (DEX Contract)
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 38 (DEX Contract)) on 31 Jul 2023: 22 findings, 1 critical; 14 marked fixed, 8 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings22
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 2 | 0 | 1 |
| Medium | 1 | 0 | 5 |
| Low | 5 | 0 | 7 |
HighCentralization Related RisksOpen
In the contract `Faucet` the role `MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MANAGER_ROLE` account may allow the hacker to take advantage of this authority and set cool time, drip unit and drippers. 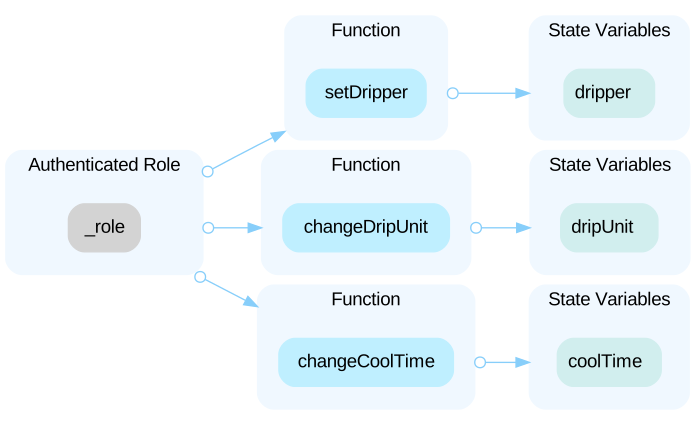 In the contract `Faucet` the role `drippers/holder` has authority over the functions shown in the diagram below. Any compromise to the `drippers`/`holder` account may allow the hacker to take advantage of this authority and drip tokens from the holder to the receiver. 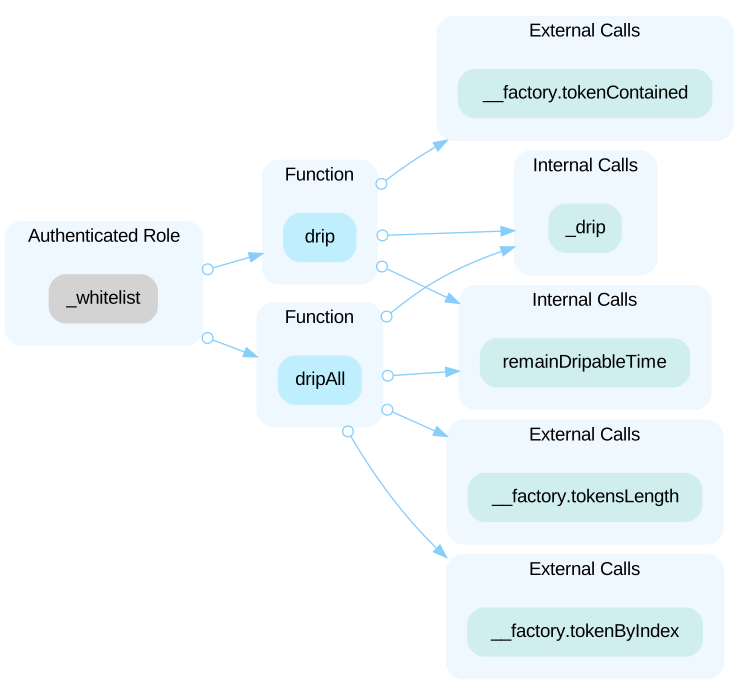 ----- In the contract `PNIXToken` the role `MINTER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MINTER_ROLE` account may allow the hacker to take advantage of this authority and mint tokens to any address. 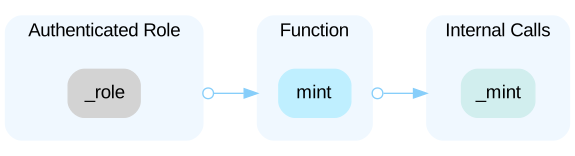 ----- In the contract `TradingRewarder` the role `MASTER_ADMIN_ROLE/GOVERNOR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MASTER_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and set `epochBufferSize`/ `maxRewardsAmountPerEpoch`/ `maxMakerScoreKOnEpoch` and upgrade the contract. Any compromise to the `GOVERNOR_ROLE` account may allow the hacker to take advantage of this authority and set `rewardsAmountPerEpoch`/ `makerScoreKOnEpoch 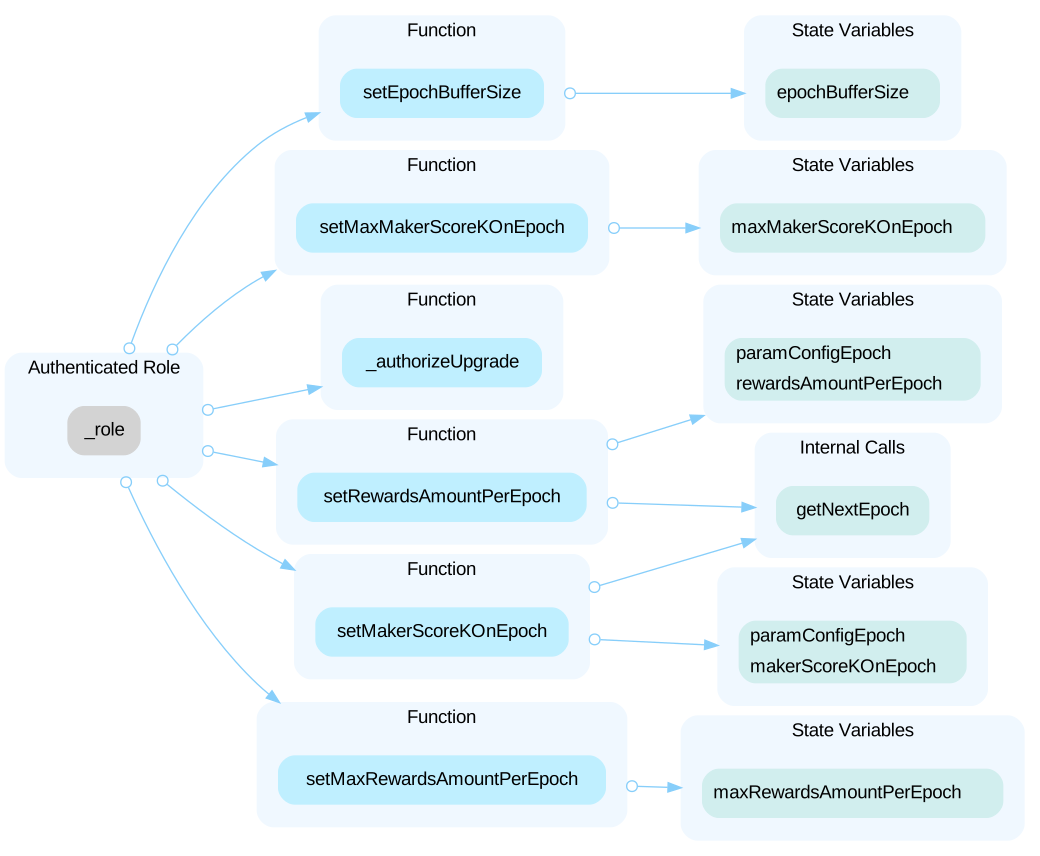 ----- In the contract `Router` the role `_eoa` has authority over the functions shown in the diagram below. Any compromise to the `_eoa` account may allow the hacker to take advantage of this authority and place/cancel stop order and place OCO order. 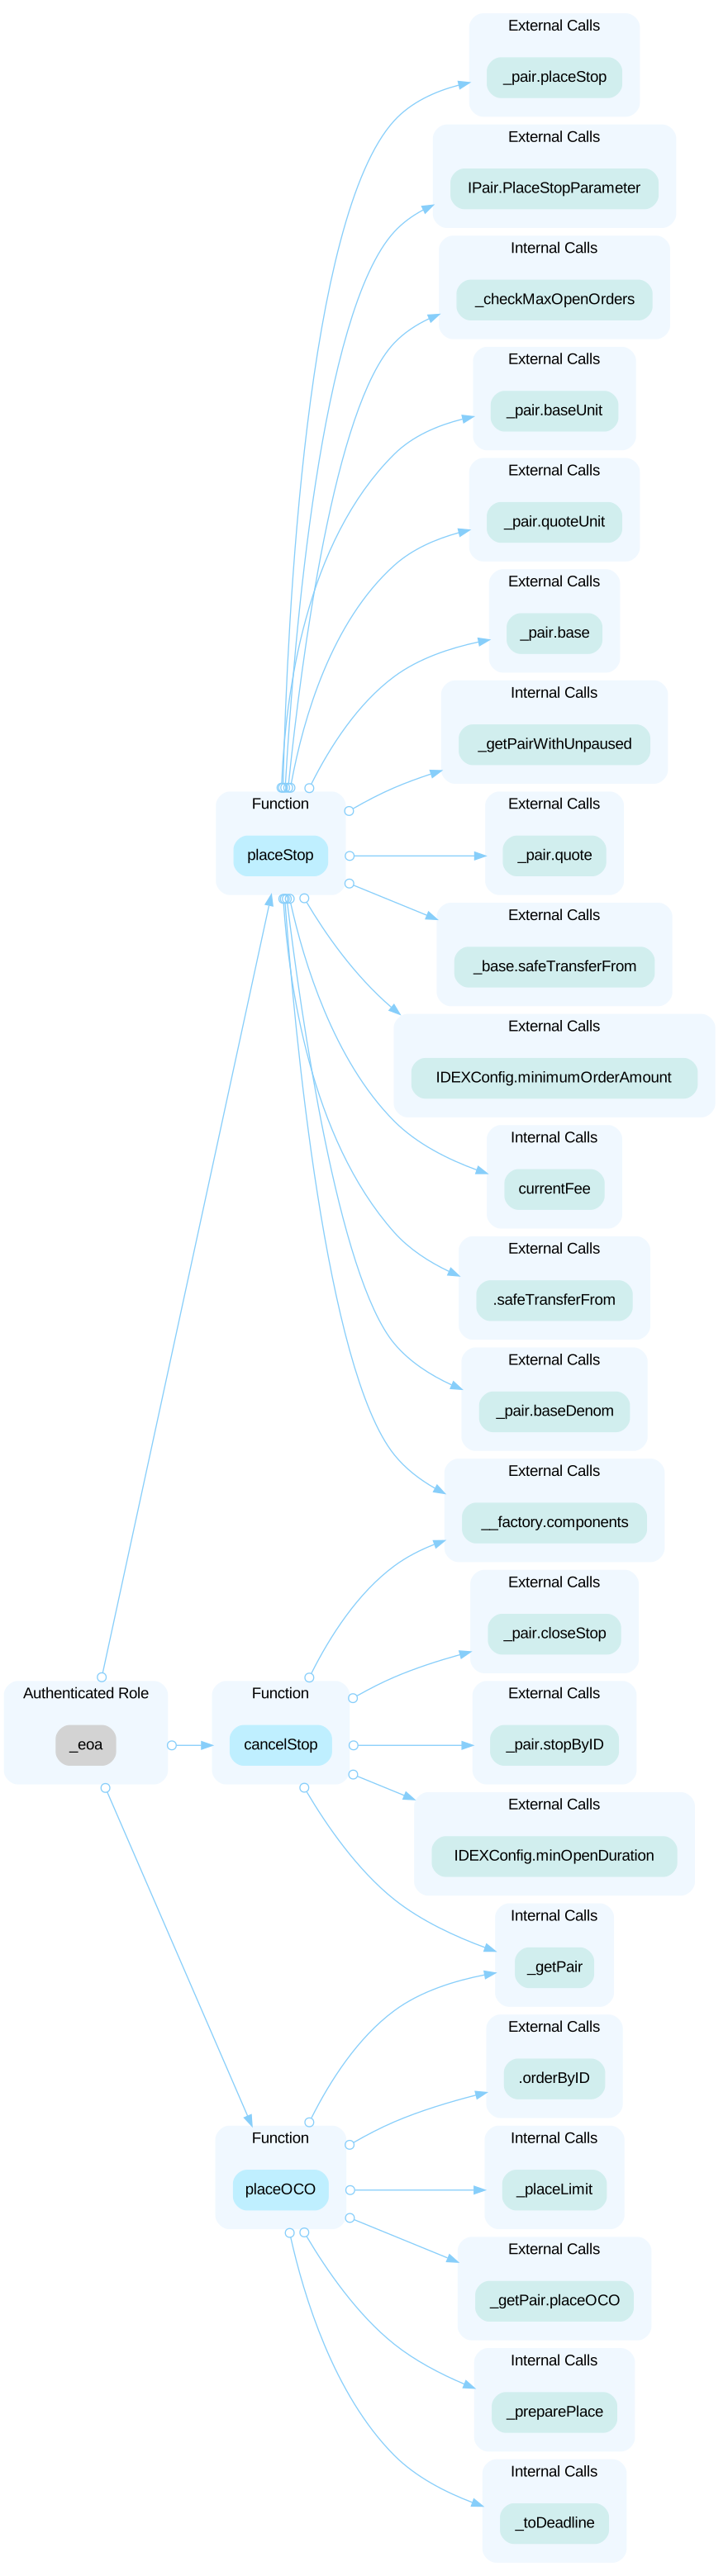 In the contract `Router` the role `_eoaorworker` has authority over the functions shown in the diagram below. Any compromise to the `_eoaorworker` account may allow the hacker to take advantage of this authority and place limit/market order on the buy/sell side and cancel the order. 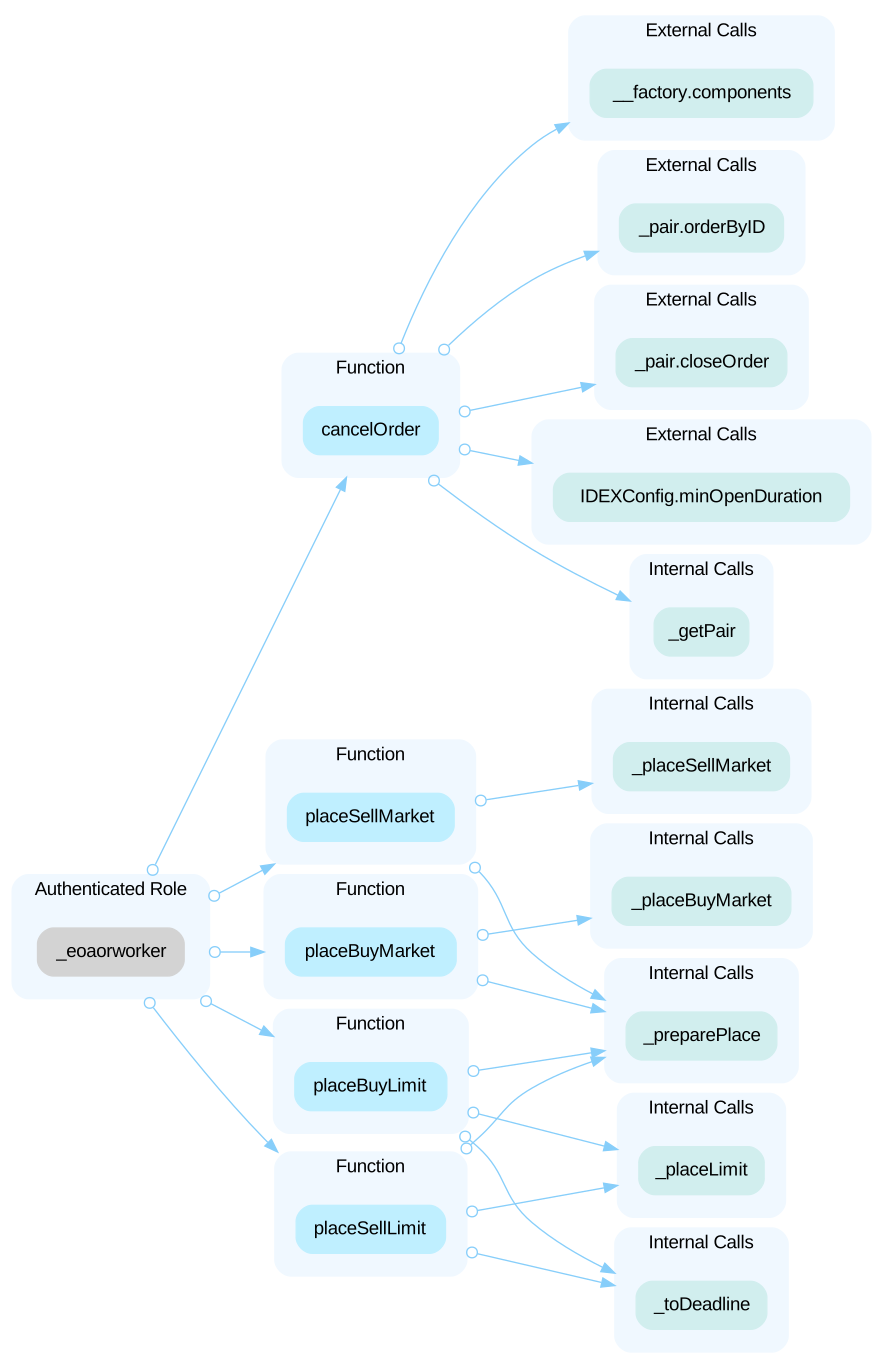 In the contract `Router` the role `MANAGER_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MANAGER_ROLE` account may allow the hacker to take advantage of this authority and transfer the balance excluding the locked reserve and emergency close order. 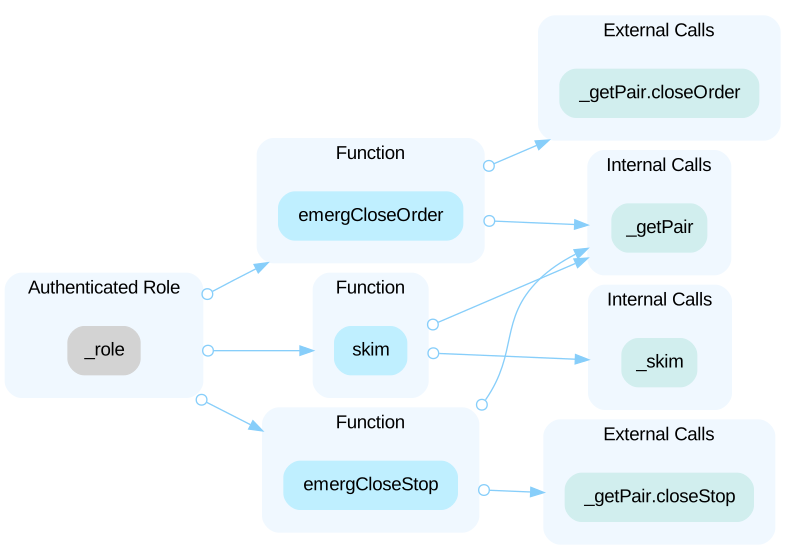 ----- In the contract `Pair` the role `MASTER_ADMIN_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `MASTER_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and transfer the balance excluding the locked reserve. 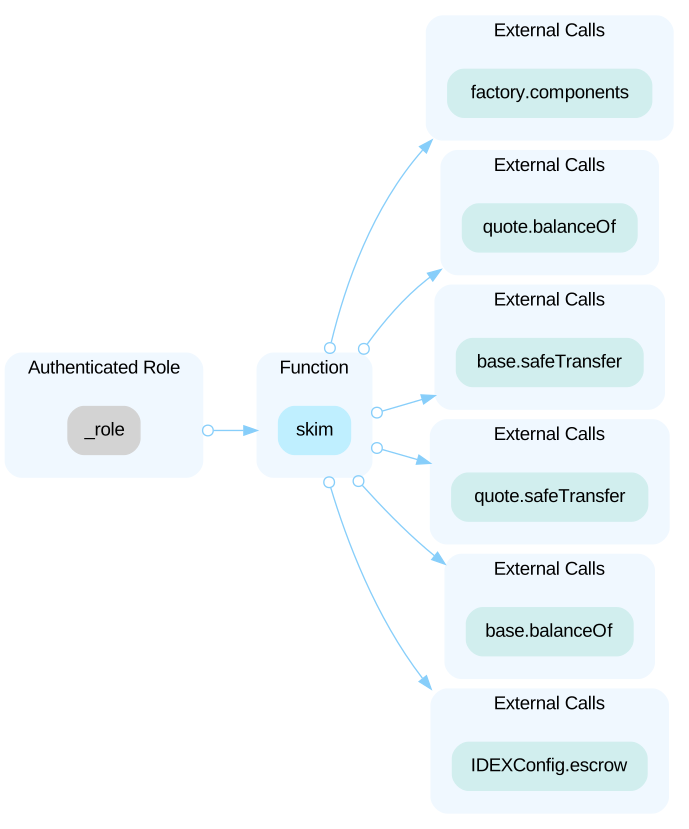 ----- In the contract `FeeTable` the role `GOVERNOR_ROLE` has authority over the functions shown in the diagram below. Any compromise to the `GOVERNOR_ROLE` account may allow the hacker to take advantage of this authority and update fees and set/remove discounts. 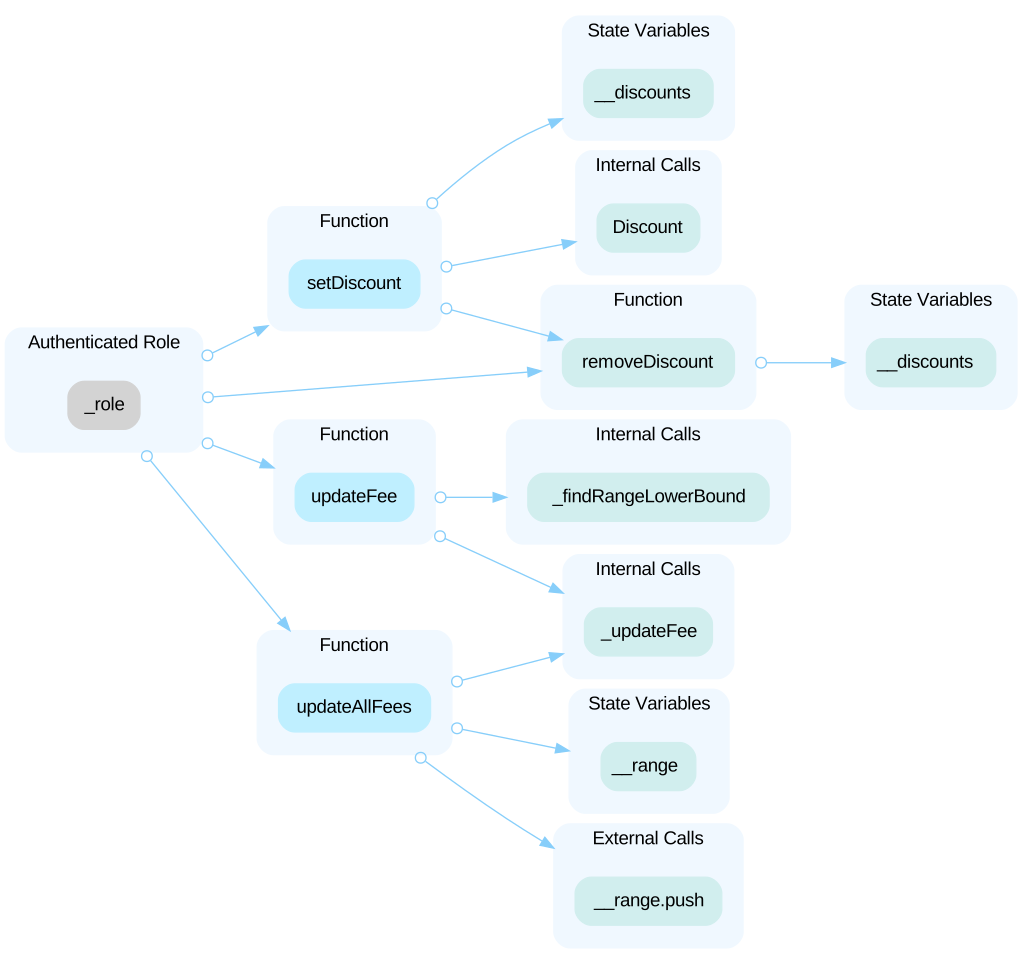 ----- In the contract `Factory` the roles `GOVERNOR_ROLE`/`MANAGER_ROLE`/`MASTER_ADMIN_ROLE`/`RoleAdmin` have authority over the functions shown in the diagram below. Any compromise to the `GOVERNOR_ROLE` account may allow the hacker to take advantage of this authority and pause/unpause the pair and set the base/quote token unit of the pair. Any compromise to the `MANAGER_ROLE` account may allow the hacker to take advantage of this authority and create a pair. Any compromise to the `MASTER_ADMIN_ROLE` account may allow the hacker to take advantage of this authority and set components. Any compromise to the `RoleAdmin` account may allow the hacker to take advantage of this authority and set the role admin. 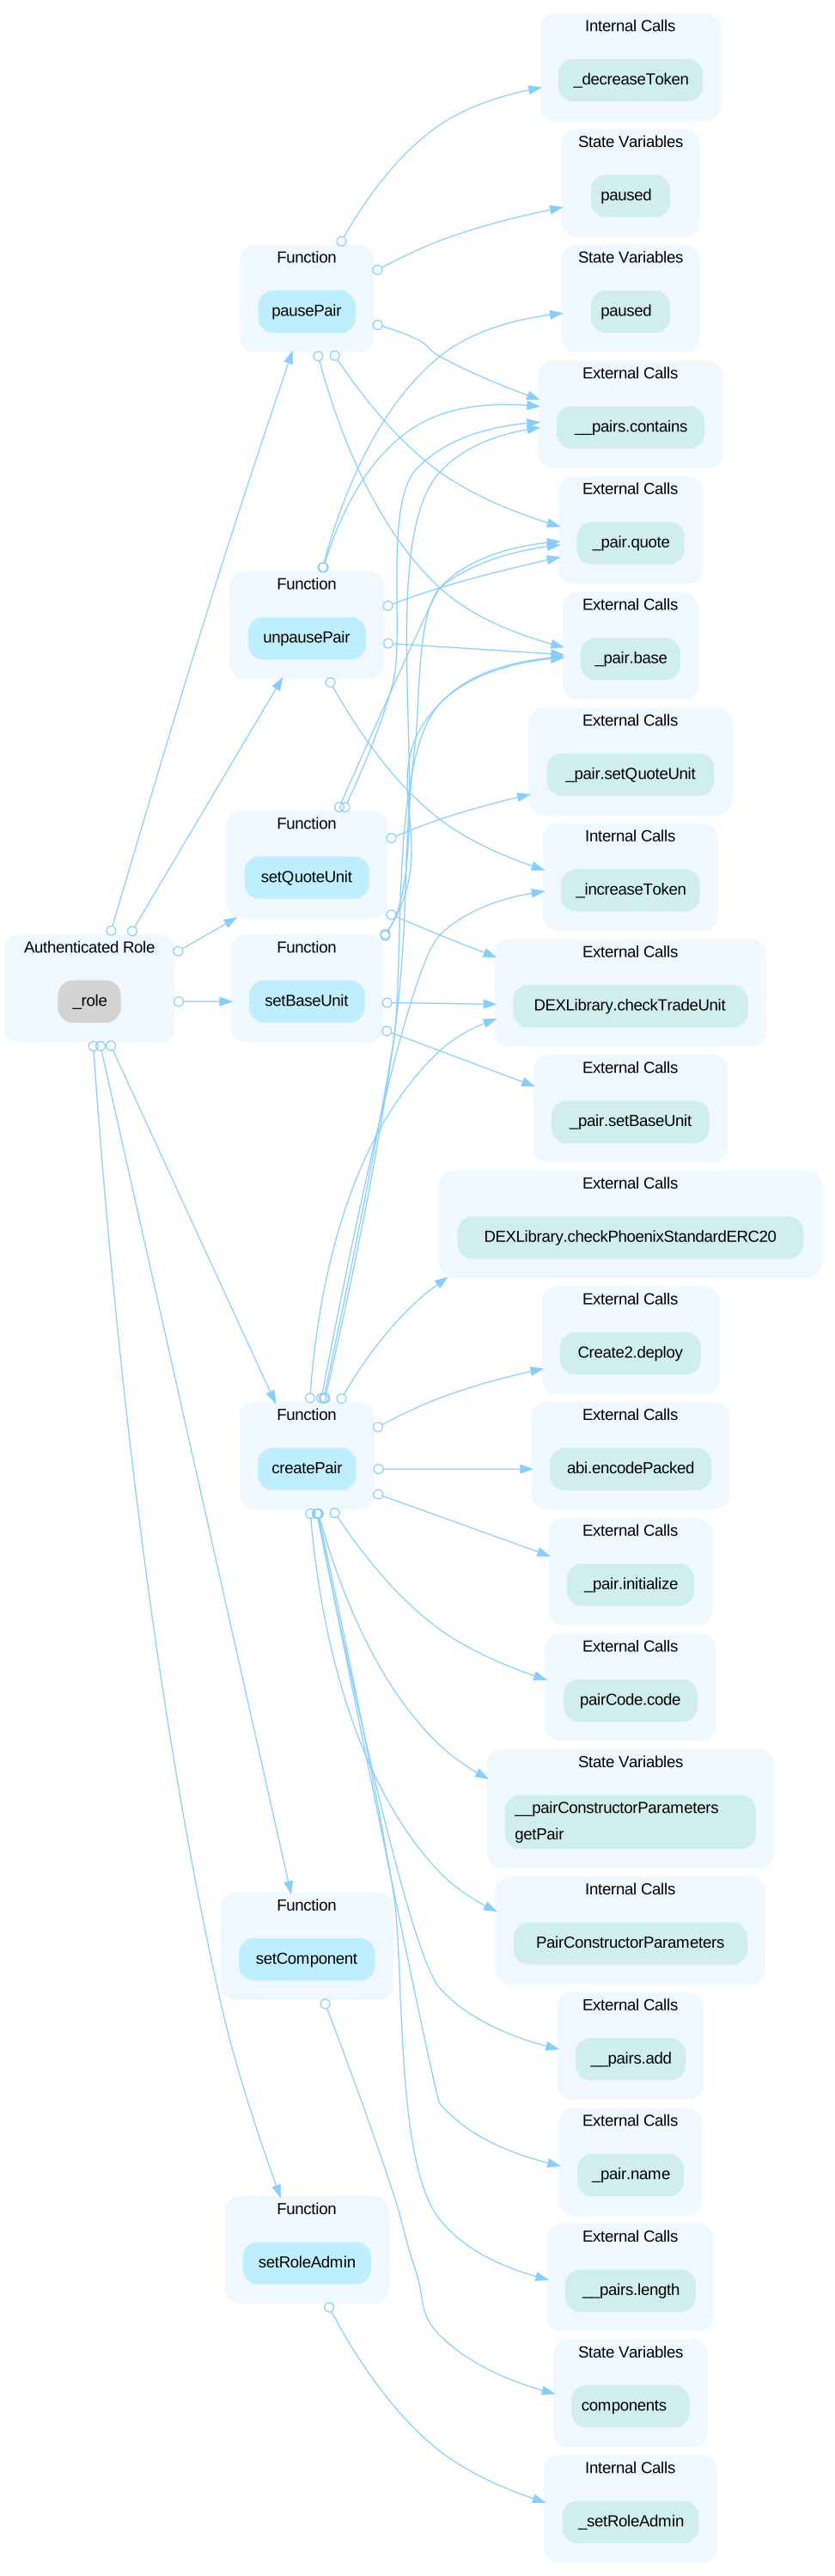 ----- In the contract `DEXConfig` the roles `MASTER_ADMIN_ROLE`/`GOVERNOR_ROLE`/`MANAGER_ROLE` have authority over the functions shown in the diagram below. Any compromise to
HighCentralized Control of Contract UpgradeOpen
In the contract `TradingRewarder`, the role `MASTER_ADMIN_ROLE` has the authority to update the implementation contract behind the proxy contract. Any compromise to the `MASTER_ADMIN_ROLE` account may allow a hacker to take advantage of this authority and change the implementation contract, which is pointed by proxy and therefore execute potential malicious functionality in the implementation contract.
MediumThird-Party Dependency UsageOpen
The contract is serving as the underlying entity to interact with one or more third-party protocols. The scope of the audit treats third-party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. ```solidity=71 function orderClosed(IPair.Order memory _order, uint _refund) external override onlyPair returns (bool) { ``` - The function `PairEventHub.orderClosed` interacts with the third-party contract with `IOrderClosedListener` interface via `_order`. ```solidity=47 function orderExchanged(uint _taker, uint _maker, uint _amount, uint _volume) external override onlyPair returns (bool) { ``` - The function `PairEventHub.orderExchanged` interacts with the third-party contract with `IOrderExchangedListener` interface via `_order`.
LowCall the function `_checkMaxStopOrders()` beforeOpen
In the `placeOCO()` function, the `_checkMaxStopOrders()` function verifies whether the owner's count of stop orders exceeds the maximum allowable number. However, if the condition `_order.id == _id && _order.payoff == 0` is evaluated to false, the function does not generate a stop order.
LowFailure to Check if the order count exceeds theOpen
In the `stackStop()` function, a new order is placed based on the stop order when certain conditions are satisfied. However, it lacks a control mechanism to check if this operation will lead to exceeding the maximum number of permissible orders.
LowIncompatibility with Deflationary TokensOpen
When transferring deflationary ERC20 tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user sends 100 deflationary tokens (with a 10% transaction fee), only 90 tokens actually arrived to the contract. However, a failure to discount such fees may allow the same user to withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction.
LowLack Of Access ControlOpen
The `triggerStop()` and `stackStop()` functions are unrestricted and can be invoked by anyone, allowing any user to trigger a stop order and place a new order based on the stop order. However, this is inconsistent with the provided comments which indicate that "The triggerStop and stackStop functions are executed by the staker".
LowPotential Gas ExhaustionOpen
The computation for each iteration is complex, it could lead to gas insufficiency.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (29)
- contracts/Router.sol
- contracts/interfaces/IFaucet.sol
- contracts/interfaces/IFeeTable.sol
- contracts/FeeTable.sol
- contracts/interfaces/IRouter.sol
- contracts/DEXConfig.sol
- contracts/interfaces/IFactory.sol
- contracts/libraries/PairConst.sol
- contracts/interfaces/IEpochHelper.sol
- contracts/interfaces/IPairEventHub.sol
- contracts/interfaces/ISimulator.sol
- contracts/governance/PNIXToken.sol
- contracts/Pair.sol
- contracts/interfaces/ITradingRewarder.sol
- contracts/interfaces/IPriceLog.sol
- contracts/PriceLog.sol
- contracts/periphery/PairViewer.sol
- contracts/libraries/DEXLibrary.sol
- contracts/interfaces/IGovToken.sol
- contracts/periphery/Faucet.sol
- contracts/periphery/Simulator.sol
- contracts/interfaces/IPair.sol
- contracts/interfaces/IDEXConfig.sol
- contracts/governance/PNIXTimelockController.sol
- contracts/helpers/EpochHelper.sol
- contracts/Factory.sol
- contracts/governance/PNIXGovernor.sol
- contracts/PairEventHub.sol
- contracts/TradingRewarder.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us