Wemix Retainer #27 (Play Auto Burn)
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer #27 (Play Auto Burn)) on 16 May 2023: 12 findings, 0 critical; 5 marked fixed, 7 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings12
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 2 |
| Low | 6 | 0 | 3 |
HighCentralization Related RisksOpen
In the contract `AccessContractRegistry` the role `_owner` has authority over the function shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set the address of `contractRegistry`. 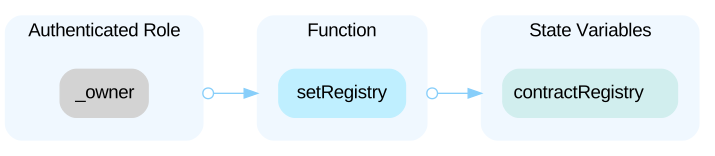 In the contract `ContractRegistry` the role `_owner` has authority over the function shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and register the newly deployed contract. 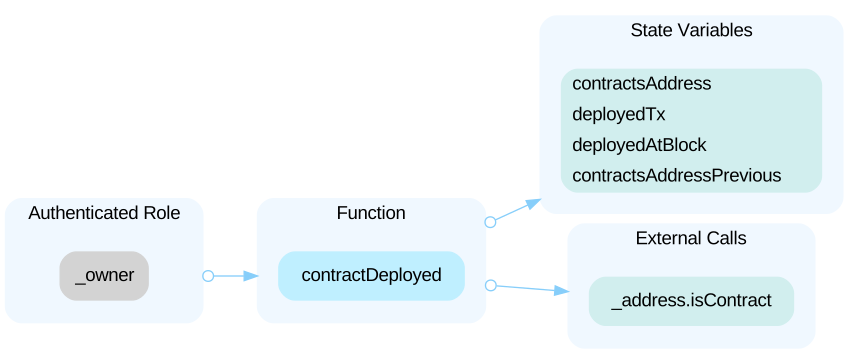 In the contract `CypressSettler` the roles `owner` and `_validator` have authority over the functions shown in the diagram below. Any compromise to the `owner` or `_validator` account may allow the hacker to take advantage of this authority to settle the WEMIX Classic and transfer the WEMIX Classic to the Wemix vault (main net). 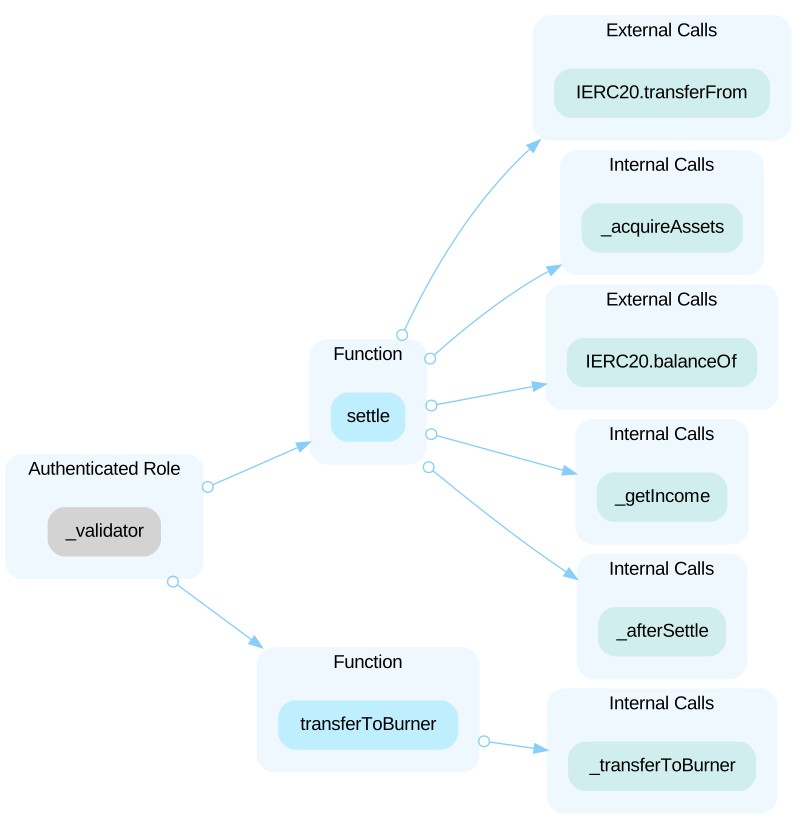 In the contract `PlaySettler` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and `setMinVal`, call `setPeriod()` to set the swap deadline period, and `setCurrencyVault`. 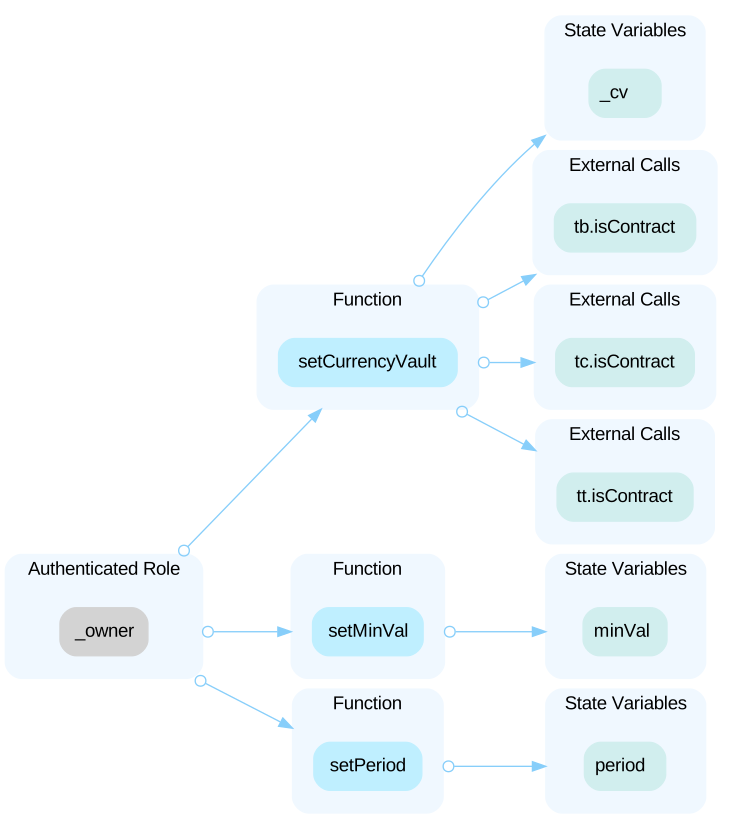 In the contract `PlaySettler` the roles `owner` and `_validator` have authority over the functions shown in the diagram below. Any compromise to the `owner` or `_validator` account may allow the hacker to take advantage of this authority and settle tokens, transfer `p.wemix` and `p.wemix$` to the Wemix vault (main net), call `changeSwapOption()` to change `swapOption`, call `setSettleDexInfo()` to initialize the balance of vault, and call `insertSettleDexInfo()` to manually add swap settlement information. 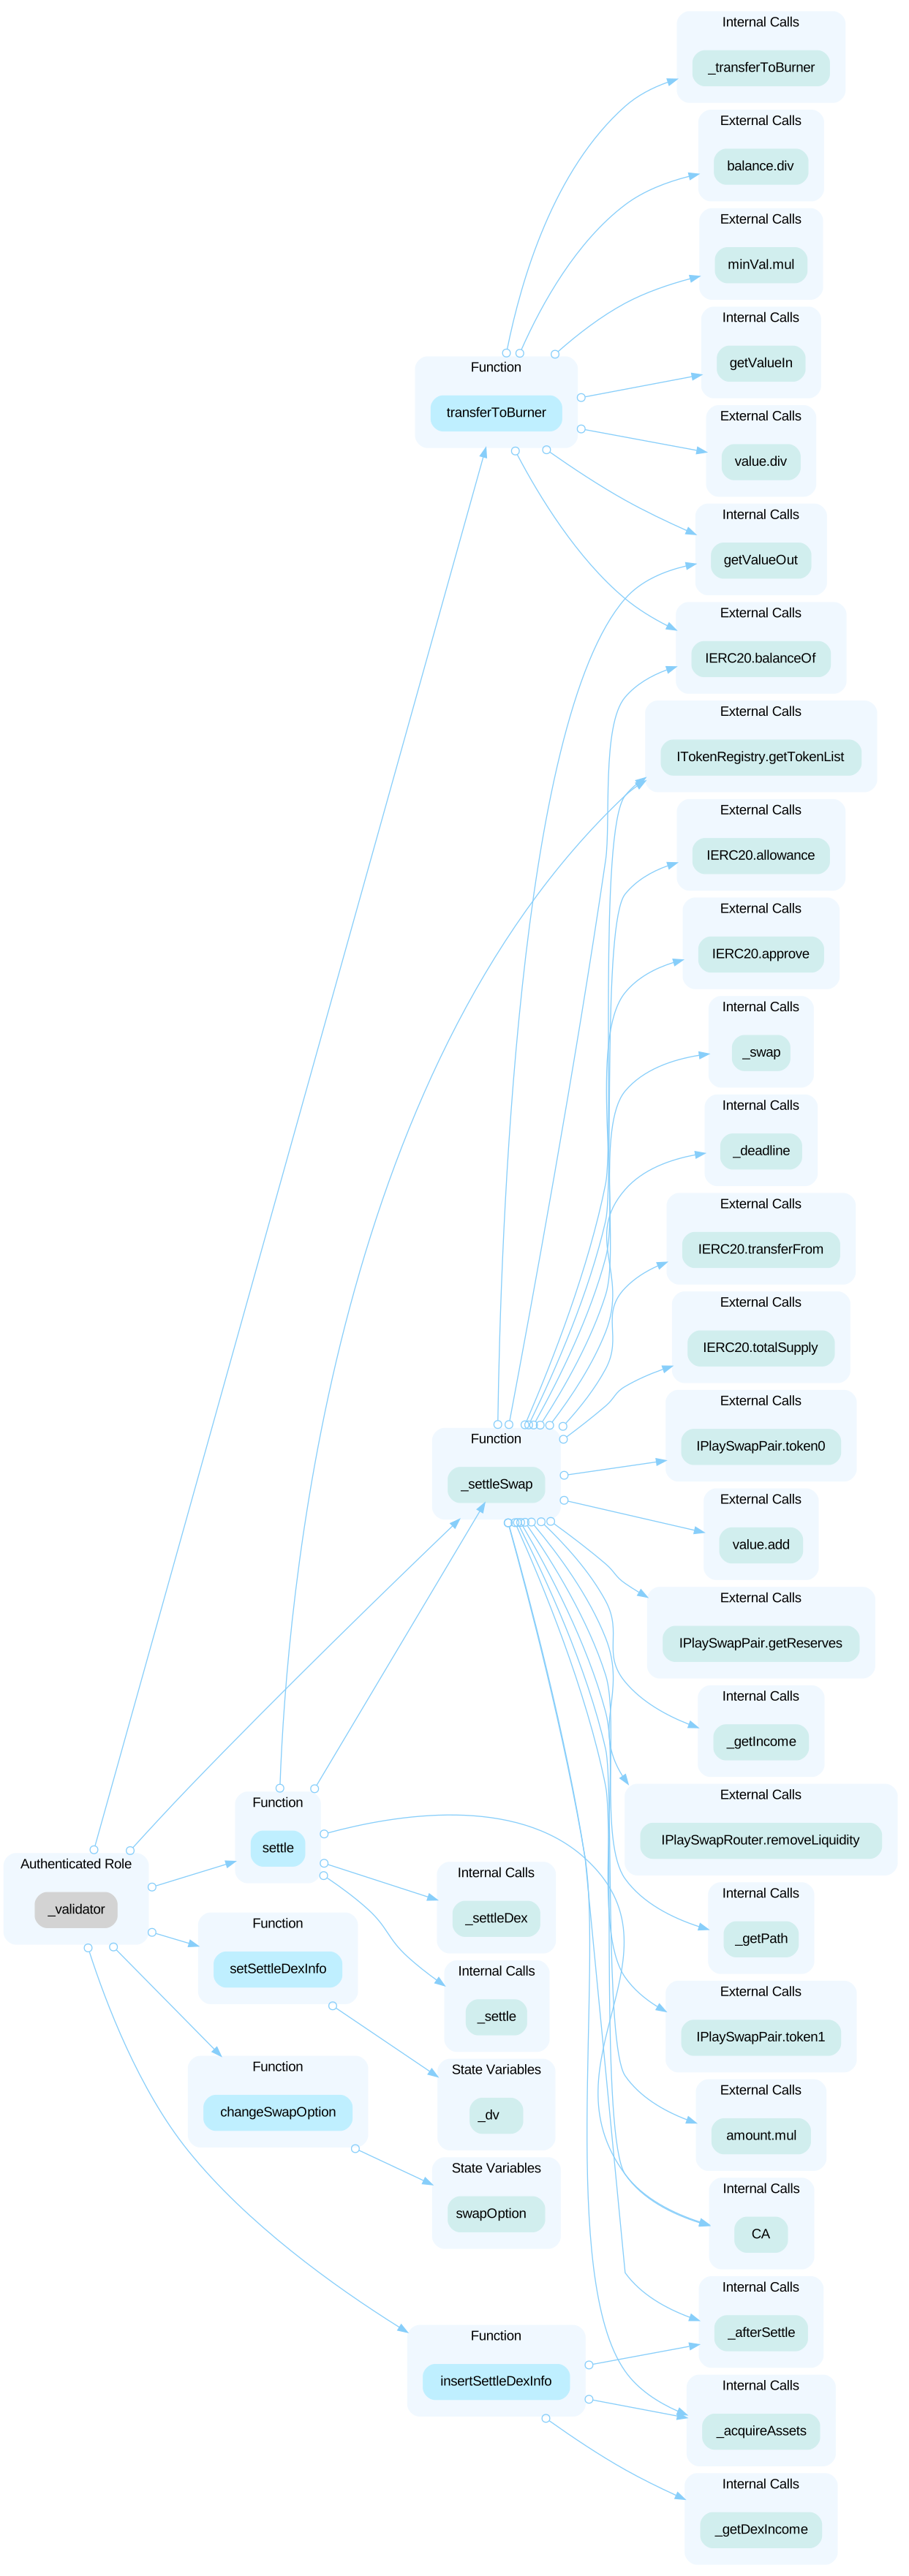 In the contract `SettlerBase` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority to withdraw tokens, call `setAcquirePercent()` to set close to 100% acquire rate, call `setTokenVault()` to set token vault, and call `setBurner()` to set burner address. 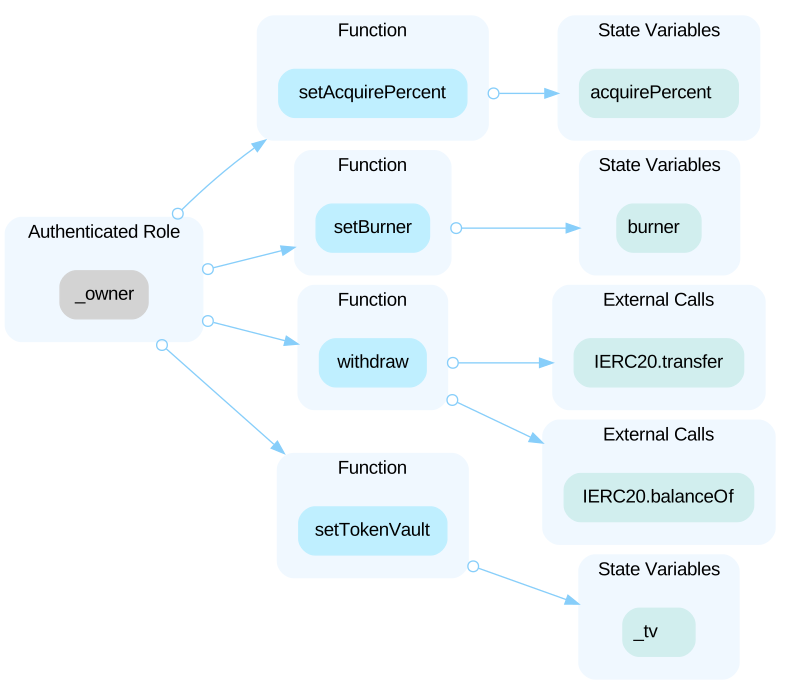 In the contract `SettlerBase` the roles `owner` and `_validator` have authority over the functions shown in the diagram below. Any compromise to the `owner` or `_validator` account may allow the hacker to take advantage of this authority to call `setSettleInfo()` to initialize the balance of vault, call `insertSettleInfo()` to manually add settlement information, and call `insertTransferInfo()` to manually add transfer history. 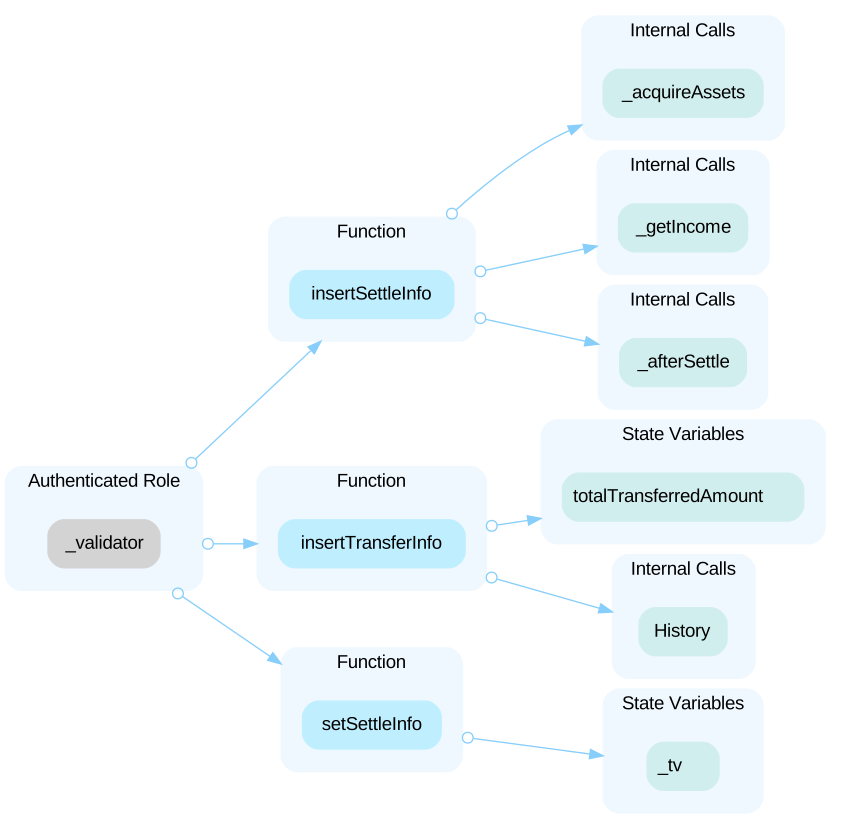
LowMissing Emit EventsOpen
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
LowMissing Error MessagesOpen
The **require** can be used to check for conditions and throw an exception if the condition is not met. It is better to provide a string message containing details about the error that will be passed back to the caller.
LowNo Upper Limits for Acquire RateOpen
There is no upper limit restricting the parameter of `setAcquirePercent()`, potentially enabling close to 100% of the acquire rate on transactions. If the `acquirePercent` is too high, swap settlement will remove a significant amount of liquidity, which could seriously affect the token price.
LowState Variable Should Be Declared ConstantOpen
State variables that never change should be declared as `constant` to save gas. ```solidity=57 uint public denominator = 1 ether; // denominator for calculate settle amount ``` - `denominator` should be declared `constant`.
LowThe currency vault `tokenBridge` is not used forOpen
The comment for the `tokenBridge` vault indicates that it is the vault of a bridge. ```solidity=24 struct CurrencyVault { address tokenBridge; // TokenBridgeTrade or TokenBridgeTradeV2 ``` In the `settle()` function, the `_settle()` function is called to handle `TRANSFER` and `BRIDGE` type settlements for currency tokens. If the settlement type is `BRIDGE`, the vault used for the settlement is `_tv[settleType].account` but not `_cv[token].tokenBridge`.
LowThird-Party Dependency UsageOpen
The contract is serving as the underlying entity to interact with one or more third party protocols. The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts, such as increasing fees of third parties, migrating to new LP pools, etc. - The contract `PlaySettler` interacts with third party contract with `IPlaySwapRouter` interface via `psr`.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (4)
- contracts/ContractRegistry.sol
- contracts/System/Settler/SettlerBase.sol
- contracts/System/Settler/PlaySettler.sol
- contracts/System/Settler/CypressSettler.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us