XCN Token (Base) - Audit
CertiK reviewed Onyx Protocol (XCN Token (Base) - Audit) on 22 Jul 2024: 2 findings, 0 critical; 1 acknowledged, 1 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings2
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 1 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 1 | 0 | 0 |
HighCentralization Risks and Third-Party DependencyAcknowledged
In the contract `OptimismMintableERC20`, the `_bridge` contract has authority over the functions shown in the diagram below. Any compromise to the `_bridge` contract may allow the hacker to take advantage of this authority and mint tokens to arbitrary addresses or burn tokens from arbitrary addresses . 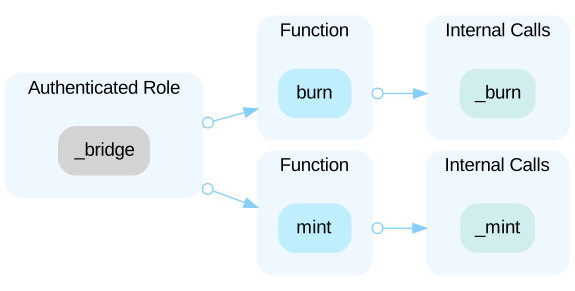 The scope of the audit treats third party entities as black boxes and assumes their functional correctness. However, in the real world, third parties can be compromised and this may lead to lost or stolen assets. In addition, upgrades of third parties can possibly create severe impacts.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Part of Onyx Protocol’s security record
 Onyx Protocol
Security firm
 CertiK
1,044 projects reviewed · 1,393 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us