ShibaSaga
CertiK reviewed Shiba Saga (ShibaSaga) on 15 Oct 2023: 8 findings, 0 critical; 7 marked fixed, 1 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings8
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 2 |
| Medium | 0 | 0 | 1 |
| Low | 0 | 0 | 4 |
HighCentralization Related RisksFixed
In the contract `VestingPoolFactory` the role `_owner` has authority over the functions shown in the diagram below. 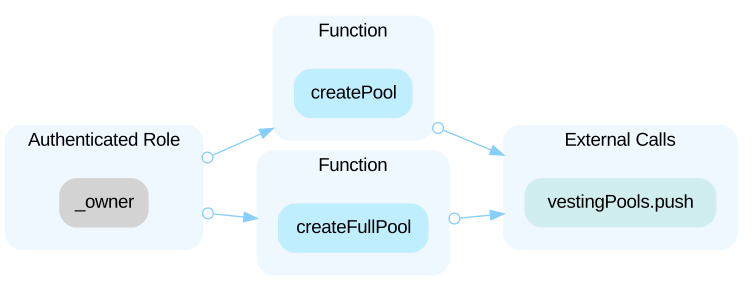 - `createPool()`: This function is used to create a new vesting pool. The pool is created with the specified parameters: `_name`, `_token`, `_startTime`, and `_vestingDuration`. Once the pool is created, its address is added to the `vestingPools` array. The privileged role that has access to call this function is the `Owner`. - `createFullPool()`: This function is used to create a new full vesting pool. The pool is created with the specified parameters: `_name`, `_token`, `_startTime`, and `_vestingDuration`. Once the pool is created, its address is added to the `vestingPools` array. The privileged role that has access to call this function is the `Owner`. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functionalities of the project. ----- In the contract `Crowdsale` the role `_owner` has authority over the functions shown in the diagram below. 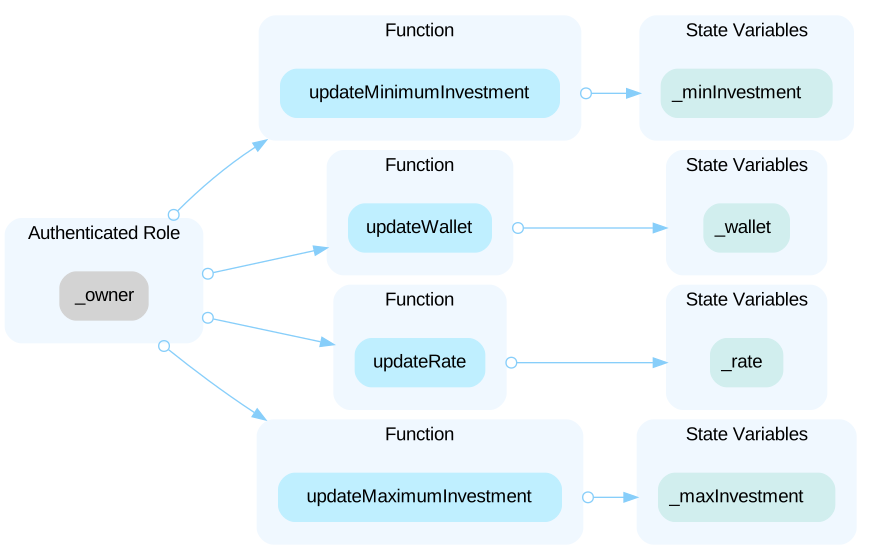 - `updateMaximumInvestment(uint256 newMaxInvestment)`: Allows the owner to update the maximum investment limit for participants. Only the contract owner can call this function. - `updateMinimumInvestment(uint256 newMinInvestment)`: Allows the owner to update the minimum investment limit for participants. Only the contract owner can call this function. - `updateWallet(address payable newWallet)`: Allows the owner to change the recipient wallet where the funds are forwarded. Only the contract owner can call this function. - `updateRate(uint256 newRate)`: Allows the owner to update the conversion rate between USDT and the token being sold. Only the contract owner can call this function. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functionalities of the project. ----- In the contract `SHIA` the role `_owner` has authority over the functions shown in the diagram below. 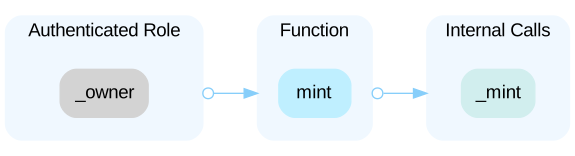 - `mint(address to, uint256 amount)`: This function allows the minting of a specific amount of SHIA tokens to a given address. The privileged role that has access to call this function is the **Owner** of the contract. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functionalities of the project.
HighCentralized Balance ManipulationFixed
In the contract `SHIA`, the role `owner` has the authority to update the token balance of an arbitrary account without sanity restriction. Any compromise to the `owner` account may allow a hacker to take advantage of this authority and manipulate users' balances by calling the `mint function to mint any amount of tokens to an arbitrary address.
MediumMisassumption of USDT Decimals Can Lead to IncorrFixed
The function `_forwardFunds` assumes that `_usdt` (presumably the USDT token contract) operates with 6 decimals, which it tries to adjust with a hardcoded division by `10 ** 12`. However, there's no guarantee that `_usdt` indeed operates with 6 decimals, leading to potential incorrect value transfers.
LowMissing Zero Address ValidationFixed
Addresses are not validated before assignment or external calls, potentially allowing the use of zero addresses and leading to unexpected behavior or vulnerabilities. For example, transferring tokens to a zero address can result in a permanent loss of those tokens. ```solidity=93 _usdt = usdt; ``` - `usdt` is not zero-checked before being used. ```solidity=139 _wallet = newWallet; ``` - `newWallet` is not zero-checked before being used.
LowRedundant Code ComponentsFixed
The linked statements do not affect the functionality of the codebase and appear to be either leftovers from test code or older functionality. ```solidity=92 function _extendTime(uint256 newClosingTime) internal { require(!hasClosed(), "TimedCrowdsale: already closed"); // solhint-disable-next-line max-line-length require( newClosingTime > _closingTime, "TimedCrowdsale: new closing time is before current closing time" ); emit TimedCrowdsaleExtended(_closingTime, newClosingTime); _closingTime = newClosingTime; } ```
LowUnnecessary Use of SafeMathFixed
The `SafeMath` library is used unnecessarily. With Solidity compiler versions 0.8.0 or newer, arithmetic operations will automatically revert in case of integer overflow or underflow. ```solidity=8 using SafeMath for uint256; ``` - `SafeMath` library is used for `uint256` type in `VestingPoolFactory` contract.
LowVariables That Could Be Declared as ImmutableFixed
The linked variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
Contracts in scope2
| Address | Chain | Source code |
|---|---|---|
| 0x24c1b2ba959bd6713f0282318bb8d8281aa26b48 | Chain: Ethereum | Source code: Verified source |
| 0x2da32d5c8c6f6b58ed0a16eeb163ce92e7687acd | Chain: Ethereum | Source code: Verified source |
Part of Shiba Saga’s security record
 Shiba Saga
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us