Wemix Retainer 49 - BYLOManager, VaultManager
Part of CertiK’s retainer series
CertiK reviewed WEMIX (Wemix Retainer 49 - BYLOManager, VaultManager) on 7 Aug 2023: 6 findings, 0 critical; 4 marked fixed, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings6
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 1 | 0 | 0 |
| Medium | 0 | 0 | 0 |
| Low | 1 | 0 | 4 |
HighCentralization RisksOpen
In the contract `BYLOManager` the role `_setter` has authority over the functions shown in the diagram below. Any compromise to the `_setter` account may allow the hacker to take advantage of this authority and change critical parameters of the project. 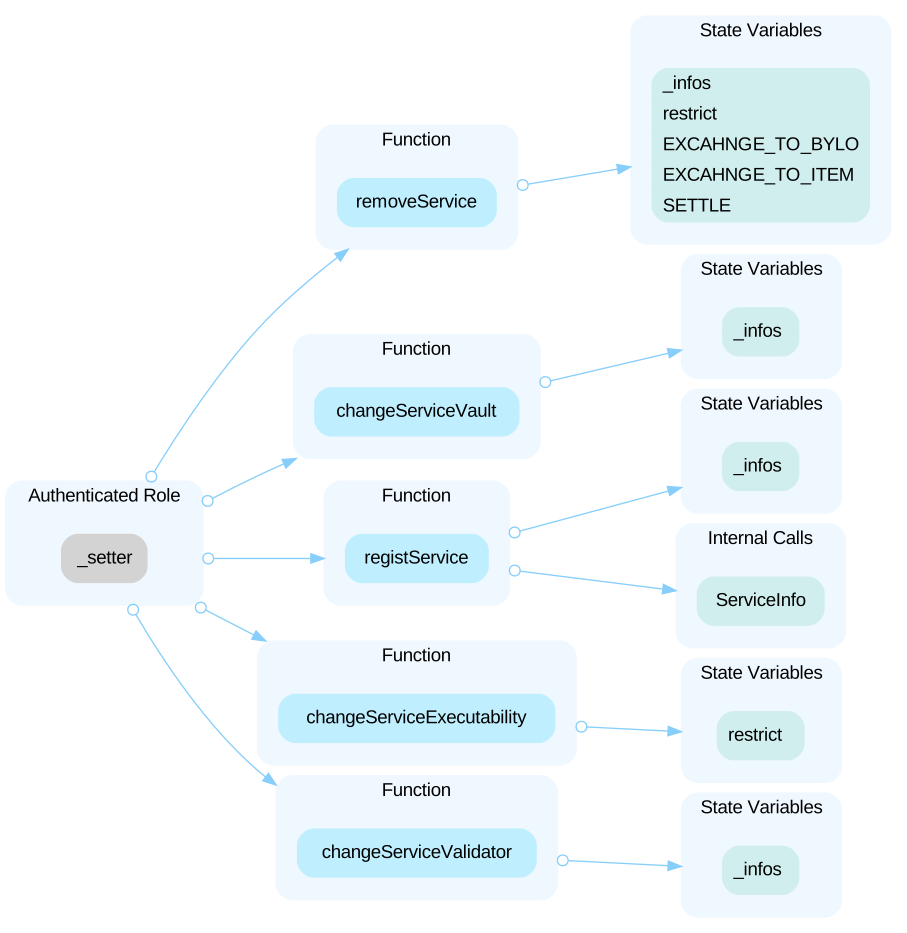 In the contract `VaultManagerDeployer` the role `_deployerrole` has authority over the functions shown in the diagram below. Any compromise to the `_deployerrole` account may allow the hacker to take advantage of this authority and deploy potentially defective or malicious vault manager contracts. 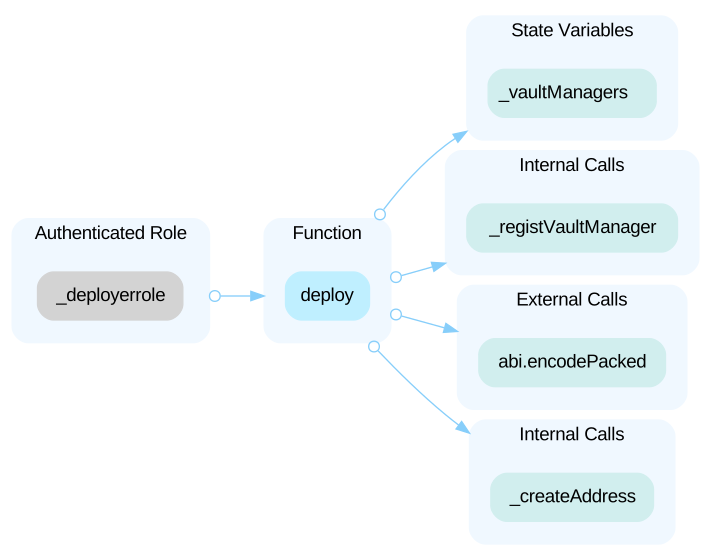 In the contract `ScheduleStorage` the role `_setter` and `_vaultmanager` have authority over the functions shown in the diagrams below. 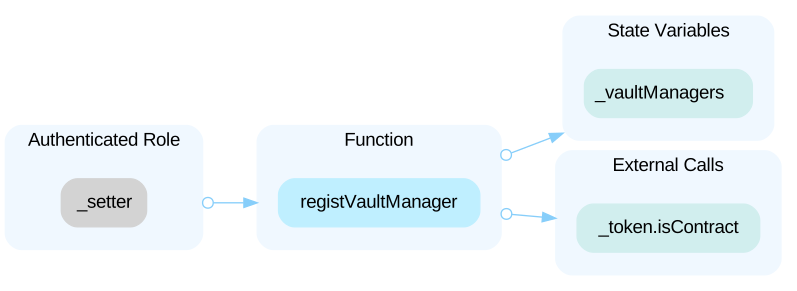 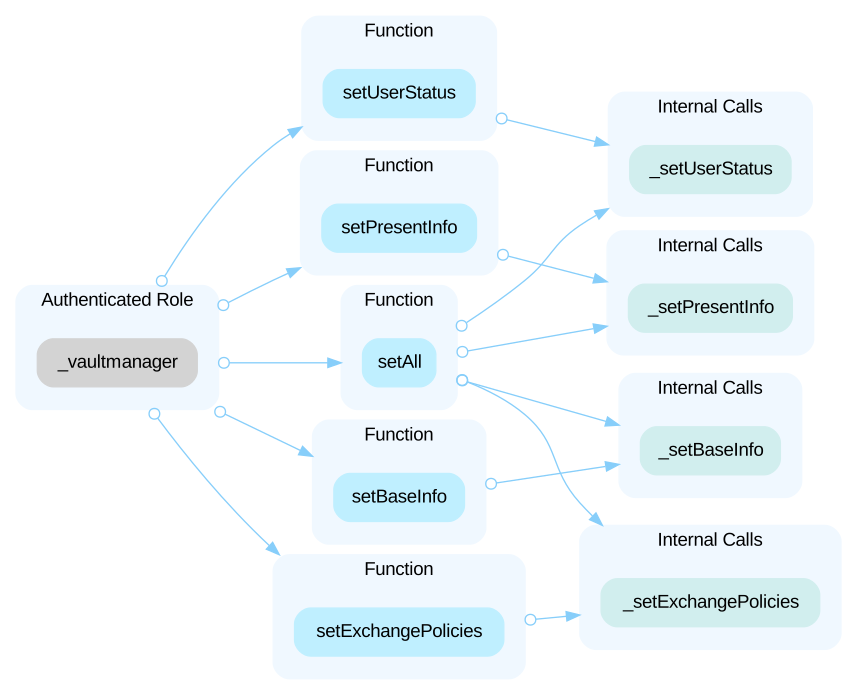 Any compromise to the `_setter` or `_vaultmanager` account may allow the hacker to take advantage of this authority and change critical storage variables. In the contract `VaultManager` the role `_setter` and `navigator` have authority over the functions shown in the diagrams below. 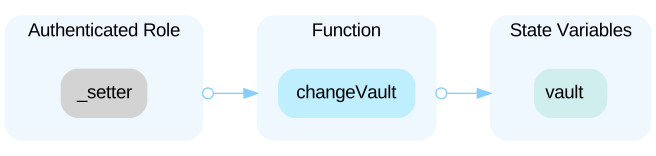 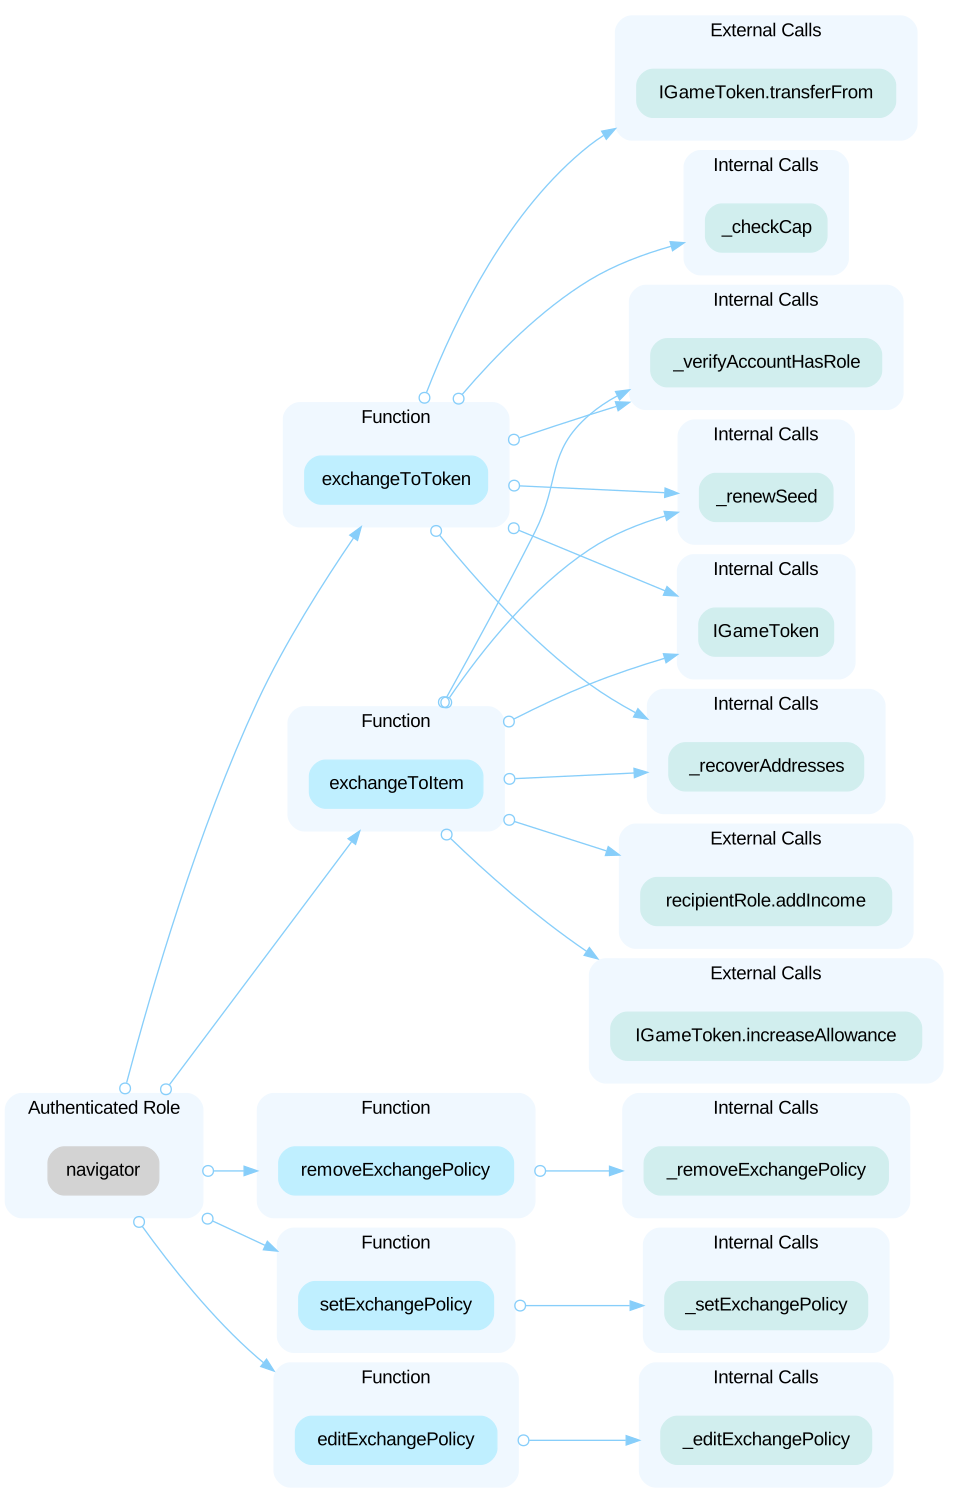 Any compromise to the `_setter` or `navigator` account may allow the hacker to take advantage of this authority and change vault address and other critical parameters of the project.
LowThird-Party DependenciesOpen
The audited code base interacts with several contracts outside of the scope of this particular audit, as well as database off-chain related to game items, and relies on the `validator` signature for important verifications. Access control of some of these external parties are also critical for the security for the system overall. For example, in the `VaultManager` contract, we assume that the `Navigator` provides correct inputs to the `exchangeToToken()` and `exchangeToItem()` functions, and that the `sender` correctly corresponds to the user intending to perform the transaction. Otherwise, user funds could be misappropriated without the user's consent. The scope of the audit treats these entities as black boxes and assumes their functional correctness. However, in the real world, these external parties can be compromised and this may lead to lost or stolen assets.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (5)
- Bylo/contracts/BYLOManager.sol
- GameToken/contracts/VaultManager/ExchangePoliciesStorage/ScheduleStorage.sol
- ContractDeployer/contracts/VaultManagerDeployer/VaultManagerDeployer.sol
- GameToken/contracts/VaultManager/VaultManager.sol
- GameToken/contracts/VaultManager/ExchangeManager/ExchangeManager.sol
Part of WEMIX’s security record
 WEMIX
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us