ApeIron - Token Contract
CertiK reviewed Apeiron (ApeIron - Token Contract) on 11 Oct 2022: 34 findings, 3 critical; 20 marked fixed, 11 acknowledged, 3 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings34
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 2 | 0 | 1 |
| High | 0 | 11 | 3 |
| Medium | 0 | 0 | 1 |
| Low | 1 | 0 | 15 |
HighCentralization Risks in AccessProtected.solAcknowledged
In the contract `AccessProtected` the role `_owner` has authority over the function `setAdmin` as shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set the desired account address as admin. 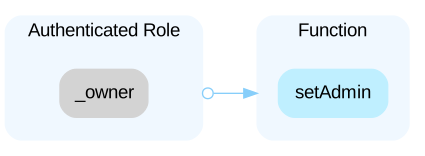
HighCentralization Risks in AccessProtectedUpgradableAcknowledged
In the contract `AccessProtectedUpgradable` the role `_owner` has authority over the function `setAdmin` as shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and set the desired account address as admin. 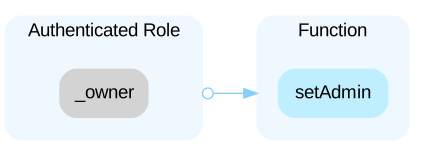
HighCentralization Risks in ANIMAchild.solAcknowledged
In the contract `AnimaChild` the role `_owner` has authority over the functions `pause` and `unpause` as shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and pause and unpause the contract. 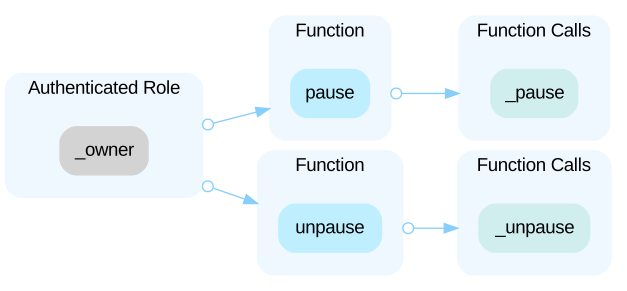
HighCentralization Risks in ANIMAroot.solAcknowledged
In the contract `AnimaRoot` the role `_owner` has authority over the functions `pause` and `unpause` as shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and pause and unpause the contract. 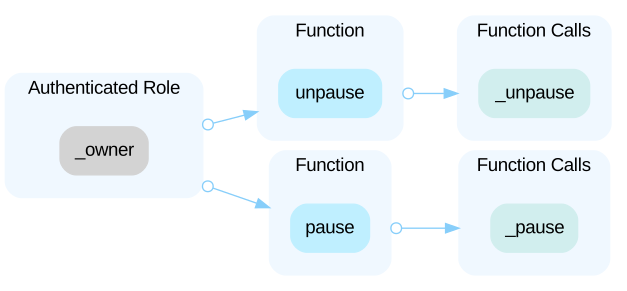
HighCentralization Risks in APRSchild.solAcknowledged
In the contract `ApeirosChild` the role `_owner` has authority over the functions `pause` and `unpause` as shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and pause and unpause the contract. 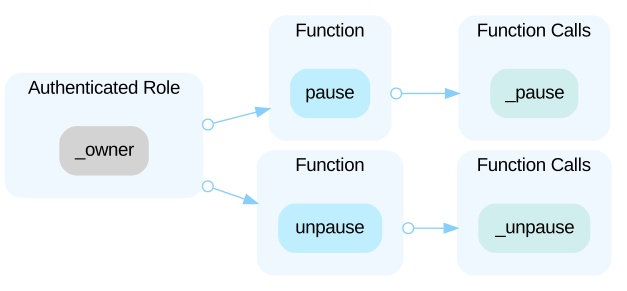
HighCentralization Risks in APRSroot.solAcknowledged
In the contract `ApeirosRoot` the role `_owner` has authority over the functions `pause` and `unpause` as shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and pause and unpause the contract. 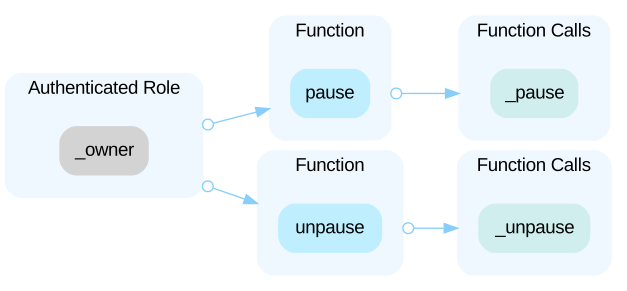
HighCentralization Risks in APRSVesting.solAcknowledged
In the contract `ApeirosVesting` the role `_owner` has authority over the functions `_authorizeUpgrade`, `revokeVestingAccount`, `setVestingAccount`, `addVestingAmount` and `setVestingToken` as shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and authorize the upgrade. In addition, this compromise will also allow the hacker to take advantage of this authority and set and/or revoke the vesting account, as well as set the vesting token and add the vesting amount. 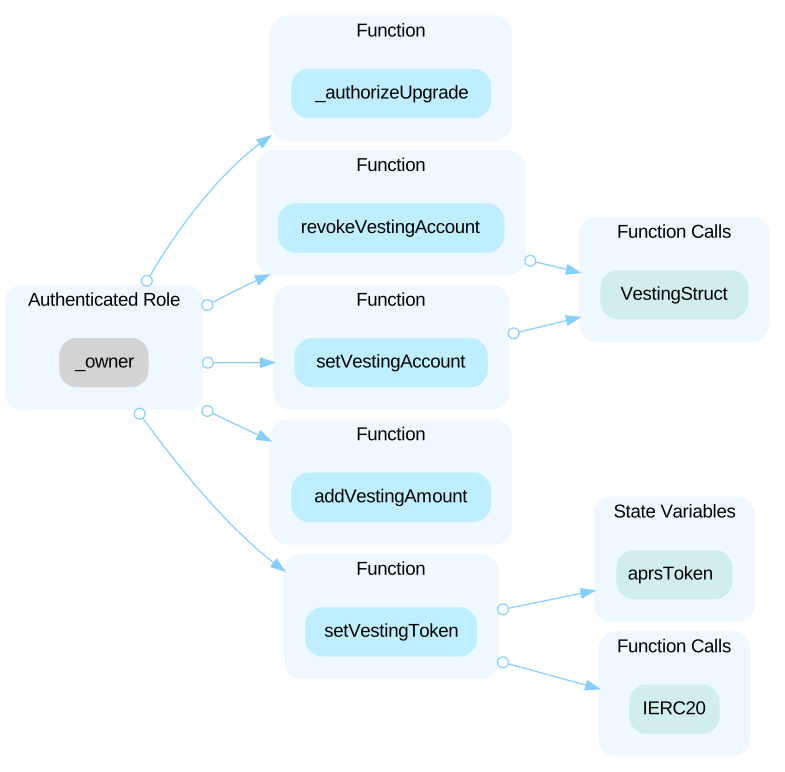
HighCentralization Risks in ExpeditionPrizes.solAcknowledged
In the contract `ExpeditionPrizes` the role `_owner` has authority over the functions `_authorizeUpgrade` and `setExpedition` as shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and authorize the upgrade as well as set the expedition to link up with the NebulaExpedition contract. 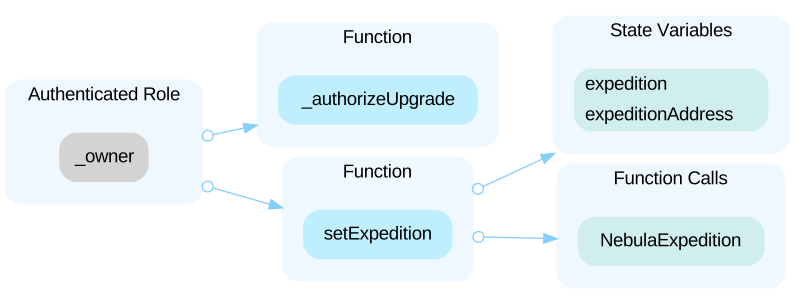
HighCentralization Risks in ExpeditionStakingAndKeys.Acknowledged
In the contract `ExpeditionStakingAndKeys` the role `_owner` has authority over the functions `setAssetType`, `setupExchangeConfig`, `withdrawFunds`, and `_authorizeUpgrade` as shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and permanently lock users' funds by calling the setAssetType() function and setting all assets to the type ASSET_TYPE_NONE. In addition, in case of hacker taking advantage of this authority, they will also be able to setup the exchange keys, withdraw the funds to the desired address, and authorize the upgrade. 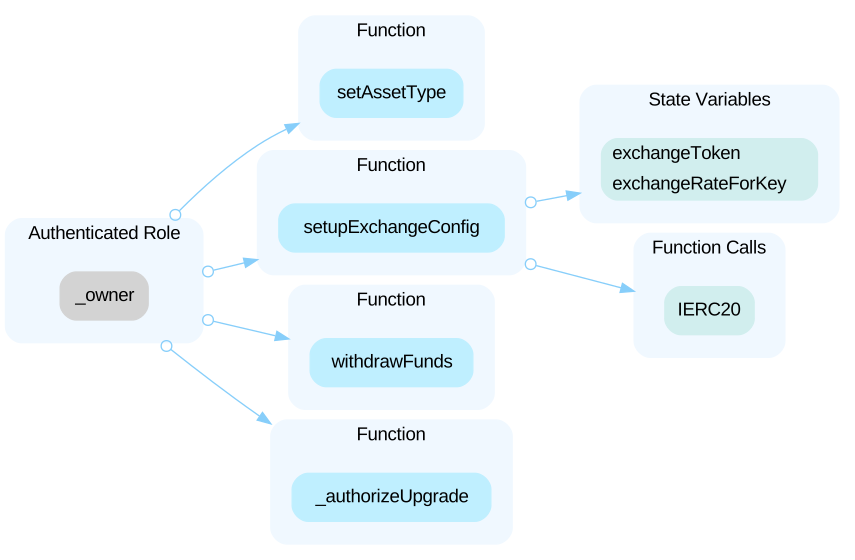
HighCentralization Risks in NebulaExpedition.solAcknowledged
In the contract `NebulaExpedition` the role `_owner` has authority over the functions `_authorizeUpgrade` and `setStakingAndKeys` as shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and authorize the upgrade and set the staking and keys to link up with `ExpeditionStakingAndKeys` contract. 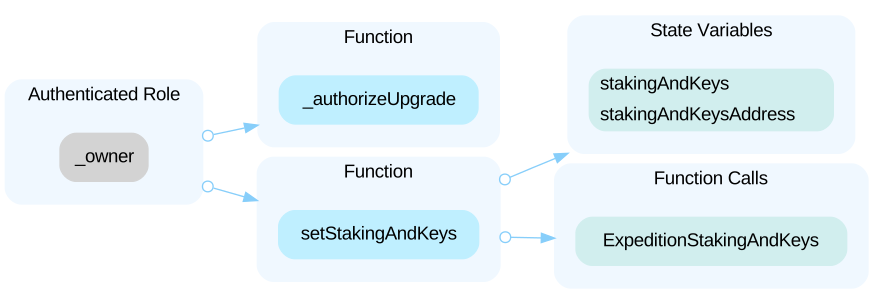
Show 1 more
HighCentralized Control of Contract UpgradeAcknowledged
`APRSVesting.sol`, `ExpeditionPrizes.sol`, `ExpeditionStakingAndKeys.sol`, `NebulaExpedition.sol` and `AccessProtectedUpgradable.sol` are upgradeable contracts, the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (20)
- contracts/ApeironGodiverseCollection.sol
- contracts/APRSVesting.sol
- contracts/utils/AccessProtectedUpgradable.sol
- contracts/NebulaExpedition.sol
- contracts/ExpeditionMeta.sol
- contracts/interfaces/IApeironPlanet.sol
- contracts/utils/AccessControlMixin.sol
- contracts/StakeAssetMeta.sol
- contracts/ANIMAroot.sol
- contracts/ANIMA.sol
- contracts/ANIMAchild.sol
- contracts/interfaces/IApeironStar.sol
- contracts/APRSroot.sol
- contracts/interfaces/IApeironGodiverseCollection.sol
- contracts/utils/IMintableERC20.sol
- contracts/APRSchild.sol
- contracts/ExpeditionPrizes.sol
- contracts/ExpeditionStakingAndKeys.sol
- contracts/utils/IChildToken.sol
- contracts/utils/AccessProtected.sol
Part of Apeiron’s security record
Security firm
 CertiK
1,044 projects reviewed · 1,393 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us