L2Finance
CertiK reviewed L2Finance on 2 May 2023: 11 findings, 0 critical; 7 marked fixed, 4 acknowledged.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings11
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 0 | 2 | 0 |
| Medium | 0 | 2 | 1 |
| Low | 0 | 0 | 6 |
HighCentralization Risks in L2Finance.solAcknowledged
In the contract `Ownable` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and transfer the ownership to any address. 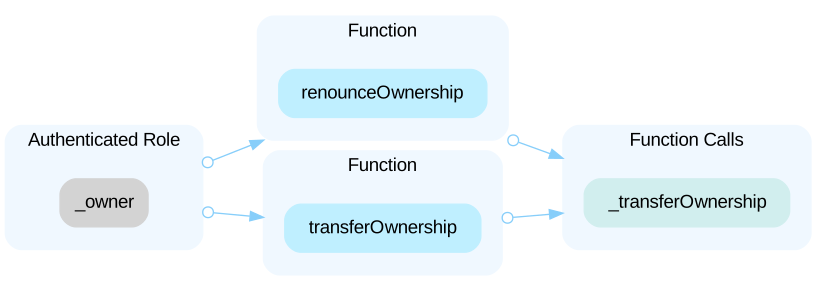 In the contract `HasNoEther` the role `_owner` has authority over the functions shown in the diagram below. This centralization risk may lead to a single point of failure and gives the owner significant control over the contract's behavior: 1. `reclaimEther()` - allows the owner to transfer all ether in the contract to the owner. 2. `reclaimToken()` - allows the owner to transfer any type of ERC20 in the contract to the owner. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and bring unpredictable damages to the project. 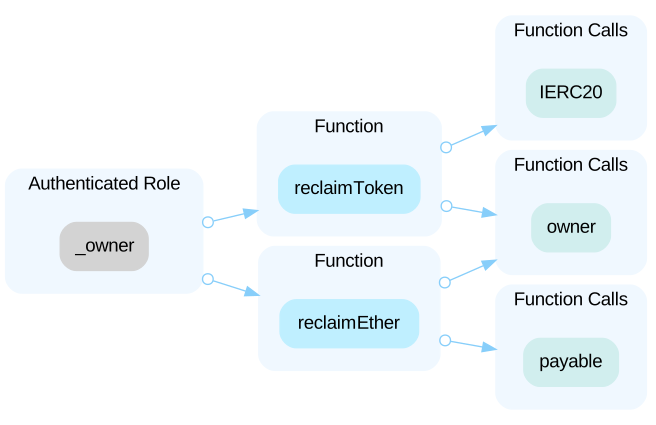 In the contract `L2Finance` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and change the `sellBurnFee`, set the `excludeFee`/`_open`/`_key`, set the `_swap` and `_swapAllow` to block certain users from swapping functionality. 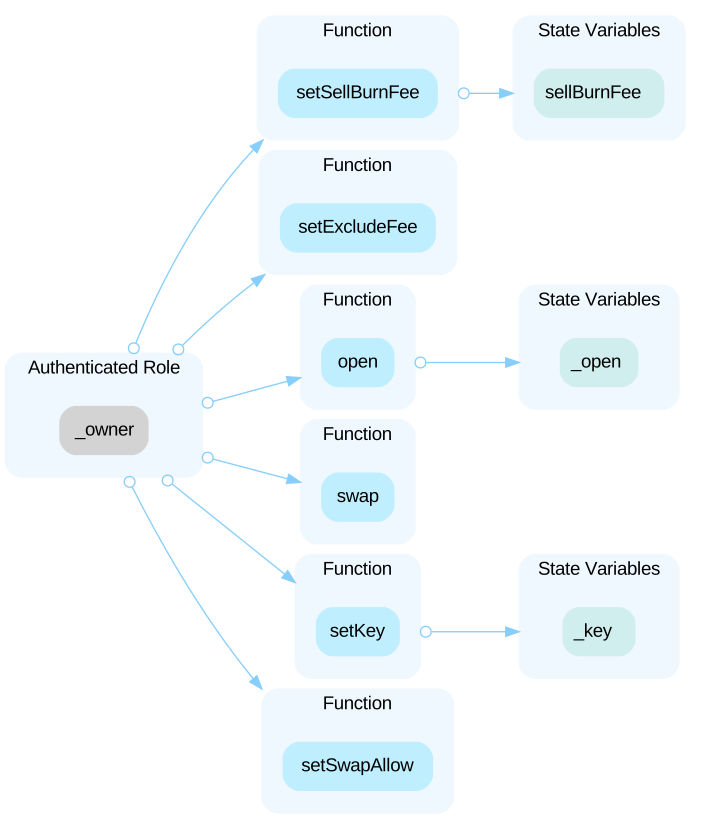
HighInitial Token DistributionAcknowledged
All L2FI tokens are sent to the deployer when deploying the contract. This could be a centralization risk as the deployer can distribute tokens without obtaining the consensus of the community.
MediumIncompatibility with Deflationary TokensAcknowledged
When transferring deflationary ERC20 tokens, the input amount may not be equal to the received amount due to the charged transaction fee. For example, if a user sends 100 deflationary tokens (with a 10% transaction fee), only 90 tokens actually arrived to the contract. However, a failure to discount such fees may allow the same user to withdraw 100 tokens from the contract, which causes the contract to lose 10 tokens in such a transaction. Reference: https://thoreum-finance.medium.com/what-exploit-happened-today-for-gocerberus-and-garuda-also-for-lokum-ybear-piggy-caramelswap-3943ee23a39f ```solidity=843 bool success = IERC20(_usdtAddr).transferFrom(_msgSender(), address(this), amountUSDTIn); ``` - Transferring tokens by `amountUSDTIn`. ```solidity=841 uint256 amountL2FIOut = _getL2FIOut(amountUSDTIn, poolL2FIBal, poolUSDTBal); ``` - This function call executes the following operation. - In `L2Finance._getL2FIOut`, - `uint256 denominator = poolUSDTBal.add(amountUSDTIn);` - In `SafeMath.add`, - `uint256 c = a + b;` - The `amountUSDTIn` appears to be used for bookkeeping purposes without compensating the potential transfer fees. --- ```solidity=861 bool success = IERC20(_usdtAddr).transferFrom(_msgSender(), address(this), amountUSDTIn); ``` - Transferring tokens by `amountUSDTIn`. ```solidity=859 uint256 amountL2FIOut = _getL2FIOut(amountUSDTIn, poolL2FIBal, poolUSDTBal); ``` - This function call executes the following operation. - In `L2Finance._getL2FIOut`, - `uint256 denominator = poolUSDTBal.add(amountUSDTIn);` - In `SafeMath.add`, - `uint256 c = a + b;` - The `amountUSDTIn` appears to be used for bookkeeping purposes without compensating the potential transfer fees.
MediumLogical issues in reclaimToken functionAcknowledged
The function `reclaimToken()` can be called by the owner to drain all ERC20 tokens in the contract, including the USDT and the L2FI. This is both a centralization issue and a logical issue.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- src/L2Finance.sol
Part of L2Finance’s security record
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us