Momentum
CertiK reviewed Momentum on 4 Jul 2023: 26 findings, 0 critical; 22 marked fixed, 4 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings26
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 3 | 0 | 4 |
| Medium | 1 | 0 | 7 |
| Low | 0 | 0 | 11 |
HighCentralization Related RisksOpen
In the contract `MOMToken`, the role `PAUSER_ROLE` has authority over the functions shown below: - function pause(): Accounts assigned the `PAUSER_ROLE` can pause the contract, which will prevent the transfer of `MOM` tokens. - function unpause(): Accounts assigned the `PAUSER_ROLE` can unpause the contract, which will allow the transfer of `MOM` tokens. Any compromise to the `PAUSER_ROLE` accounts may allow the hacker to take advantage of this authority and allow or unpause `MOM` tokens to be transferred. --- In the contract `MOMToken`, the role `MINTER_ROLE` has authority over the functions shown below: - function mint(): Accounts assigned the `MINTER_ROLE` can mint arbitrary amounts of `MOM` tokens to any account. Any compromise to the `MINTER_ROLE` accounts may allow the hacker to take advantage of this authority and mint large number of `MOM` tokens to any accounts. --- In the contract `MOMToken`, the role `BURNER_ROLE` has authority over the functions shown below: - function burn(): Accounts assigned the `BURNER_ROLE` can burn their own `MOM` tokens. - function burnFrom(): Accounts that have been assigned the `BURNER_ROLE` can use their allowance to burn `MOM` tokens belonging to other accounts. Any compromise to the `BURNER_ROLE` accounts may allow the hacker to take advantage of this authority and burn `MOM` tokens randomly. --- In the contract `MOMToken`, there is also `DEFAULT_ADMIN_ROLE` role inherited from `AccessControl` contract. Accounts granted with `DEFAULT_ADMIN_ROLE` can grant or revoke other roles as mentioned above. By default, the deployer of `MOMToken` contract has been granted all these roles. * DEFAULT_ADMIN_ROLE * PAUSER_ROLE * MINTER_ROLE * BURNER_ROLE Any compromise to the `DEFAULT_ADMIN_ROLE` accounts may allow the hacker to take advantage of this authority and operate the same actions as mentioned above. 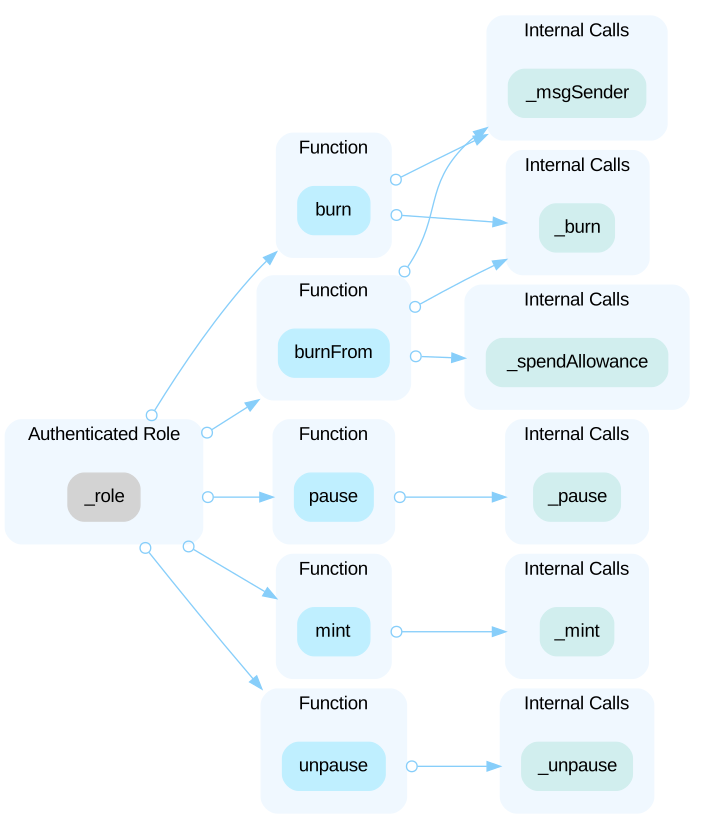 --- In the contract `DADToken`, the role `BURNER_ROLE` has authority over the functions shown below: - function burn(): Accounts assigned the `BURNER_ROLE` can burn their own `DAD` tokens. - function burnFrom(): Accounts that have been assigned the `BURNER_ROLE` can use their allowance to burn `DAD` tokens belonging to other accounts. Any compromise to the `BURNER_ROLE` accounts may allow the hacker to take advantage of this authority and burn `DAD` tokens randomly. --- In the contract `DADToken`, the role `TRANSFER_ROLE` has authority over the functions shown below: - function transfer(): Accounts assigned the `TRANSFER_ROLE` can transfer their own `DAD` tokens. - function transferFrom(): Accounts that have been assigned the `TRANSFER_ROLE` can use their allowance to transfer `DAD` tokens belonging to other accounts. Any compromise to the `TRANSFER_ROLE` accounts may allow the hacker to take advantage of this authority and transfer `DAD` tokens randomly. --- In the contract `DADToken`, the role `DEFAULT_ADMIN_ROLE` inherited from `AccessControl` contract has authority over the functions shown below: - function pause(): Accounts assigned the `DEFAULT_ADMIN_ROLE` can pause the contract, which will prevent the transfer of `DAD` tokens. - function unpause(): Accounts assigned the `DEFAULT_ADMIN_ROLE` can unpause the contract, which will allow the transfer of `DAD` tokens. - function mint(): Accounts assigned the `DEFAULT_ADMIN_ROLE` can mint arbitrary amounts of `DAD` tokens to any account. Accounts granted with `DEFAULT_ADMIN_ROLE` can grant or revoke other roles. By default, the deployer of `DADToken` contract has been granted all these roles. * DEFAULT_ADMIN_ROLE * TRANSFER_ROLE * BURNER_ROLE Any compromise to the `DEFAULT_ADMIN_ROLE` accounts may allow the hacker to take advantage of this authority and pause/unpause `DAD` tokens to be transferred, mint large number of `DAD` tokens to any account, as well as operate the same actions as mentioned above. 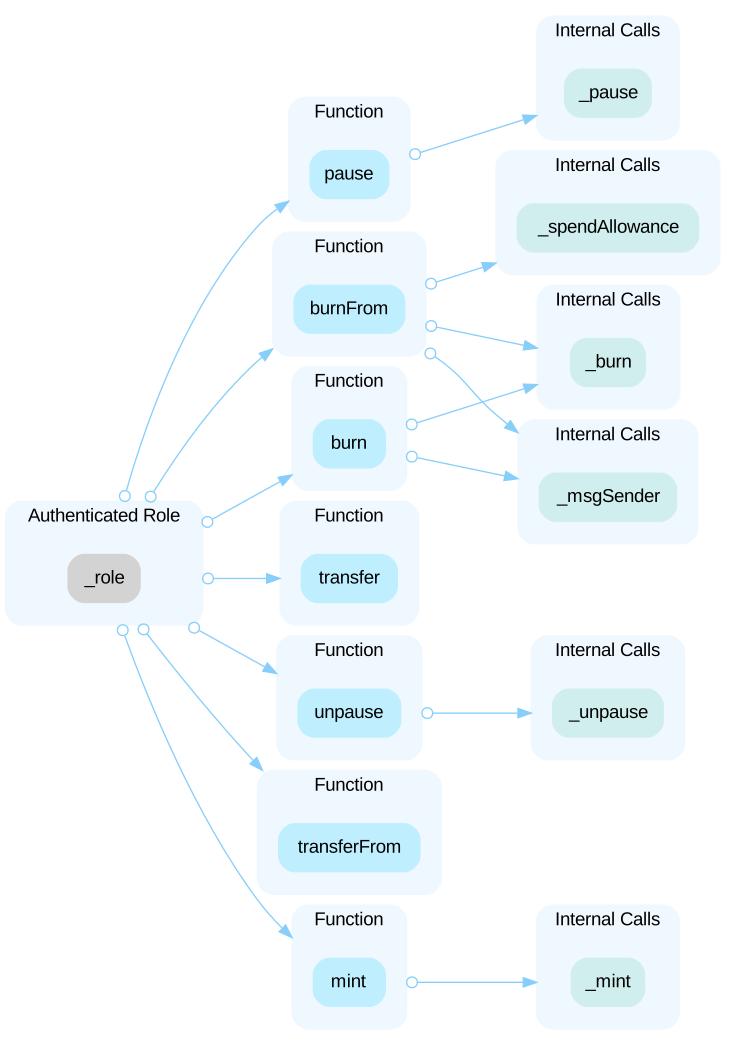 --- In the contract `OdysseyNFT` the role `_owner` has authority over the functions shown in the diagram below. 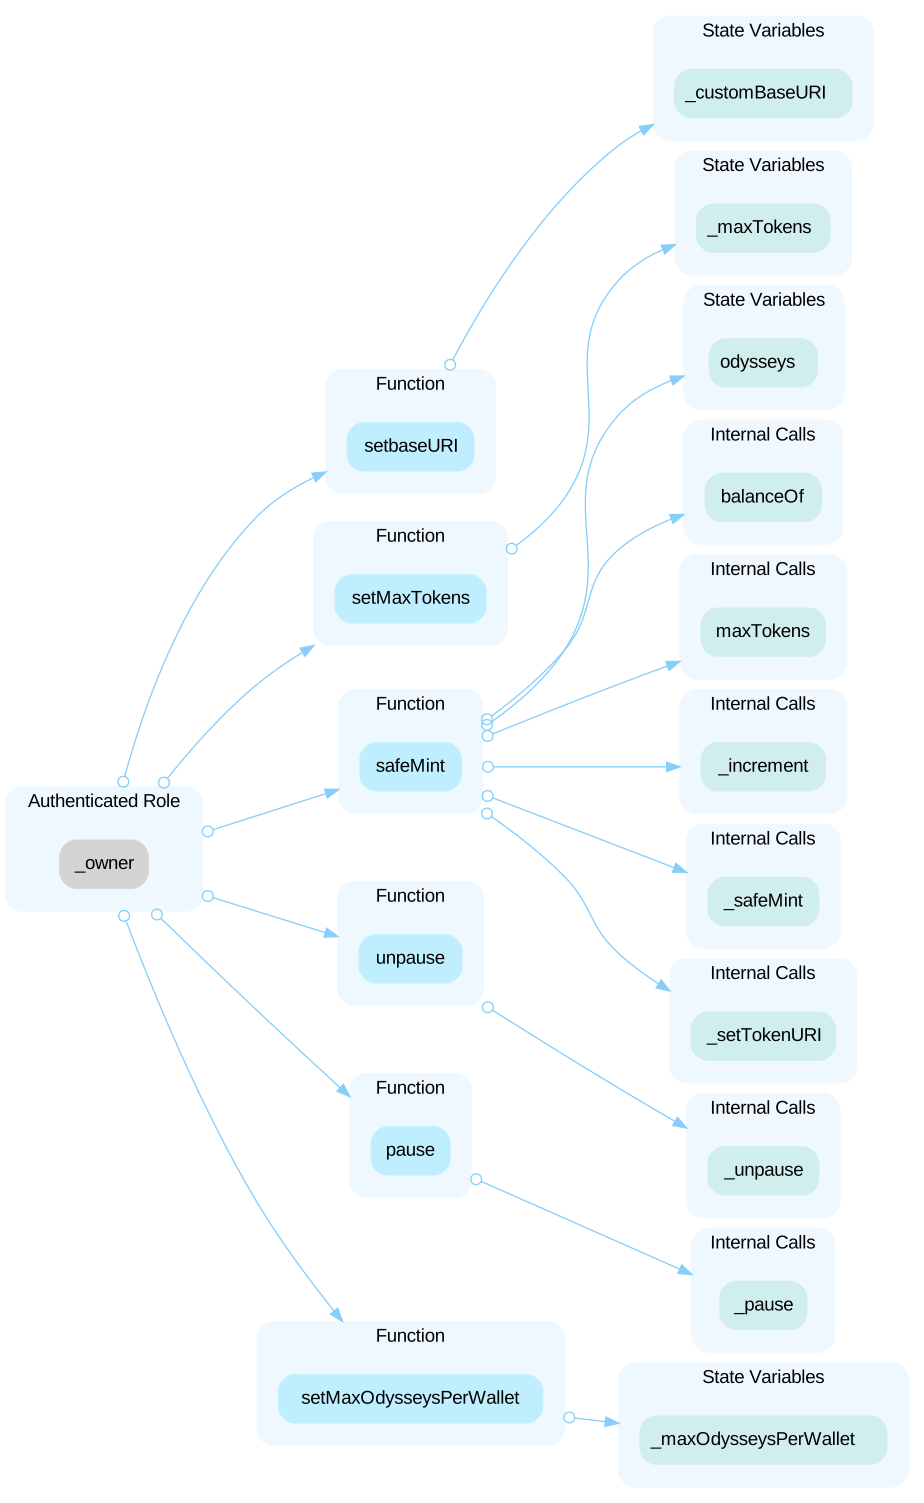 Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and execute the following actions: * execute function `pause()` to permit the contract to mint or transfer; * execute function `unpause()` to allow the contract to mint or transfer; * execute function `setMaxTokens()` to set an unexpected maximum number as `_maxTokens`; * execute function `setMaxOdysseysPerWallet()` to set an unexpected maximum number as `_maxOdysseysPerWallet`; * execute function `safeMint()` to mint OdysseyNFT ; * execute function `setbaseURI()` to set an
HighCentralized Control of Contract UpgradeOpen
The `Staking` is an upgradeable contract, meaning the owner can upgrade the contract without the community's commitment. If an attacker compromises the account, he can change the implementation of the contract and drain tokens from the contract.
HighInitial Token DistributionOpen
All of the initial supply of `MOM` tokens are sent to the contract deployer when deploying the contract. This is a potential centralization risk as the deployer can distribute `MOM` tokens without the consensus of the community.
MediumPossible for Stakes to Be Locked in the ContractOpen
The function `_unstake()` requires the `odyssey_id` to exist while unstaking. ```solidity=451 function _unstake(uint256 odyssey_id, Token token) private onlyMintedOdyssey(odyssey_id) { ``` Similarly, the function `_restake()` requires the `from_odyssey_id` to exist when removing a staking amount. ```solidity=513 function _restake(uint256 from_odyssey_id, uint256 to_odyssey_id, uint256 amount, Token token) private onlyMintedOdyssey(to_odyssey_id) onlyMintedOdyssey(from_odyssey_id) { ``` However, Odysseys may be burned, meaning that a previously existed ID may not longer exist in the future. In this situation, users' stakes will be locked in the contract.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (4)
- contracts/token/MomToken.sol
- contracts/nft/OdysseyNFT.sol
- contracts/token/DADToken.sol
- contracts/staking/Staking.sol
Part of Momentum’s security record
Security firm
 CertiK
1,045 projects reviewed · 1,376 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us