y8u
CertiK reviewed Y8U on 18 Apr 2024: 16 findings, 0 critical; 11 marked fixed, 5 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings16
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 0 |
| Medium | 0 | 0 | 1 |
| Low | 3 | 0 | 10 |
HighCentralization Related RisksOpen
In the contract `Y8uDistributor` the role `_owner` has authority over the functions shown in the diagram below. Any compromise to the `_owner` account may allow the hacker to take advantage of this authority and do the following: - Set the merkle roots for the private sale, strategic sale 1, and strategic sale 2, allowing themselves to claim tokens when they should not be able to or deny other users the ability to claim tokens they should be able to. - Set the `tgeTimestamp` to a time other than the token generation event to either cause tokens to be vested sooner or later than they are supposed to. - Claim the tokens that have vested for marketing, airdrops, ecosystem, team, AI mining, development, and treasury for themselves so they are not allocated for their intended purposes. 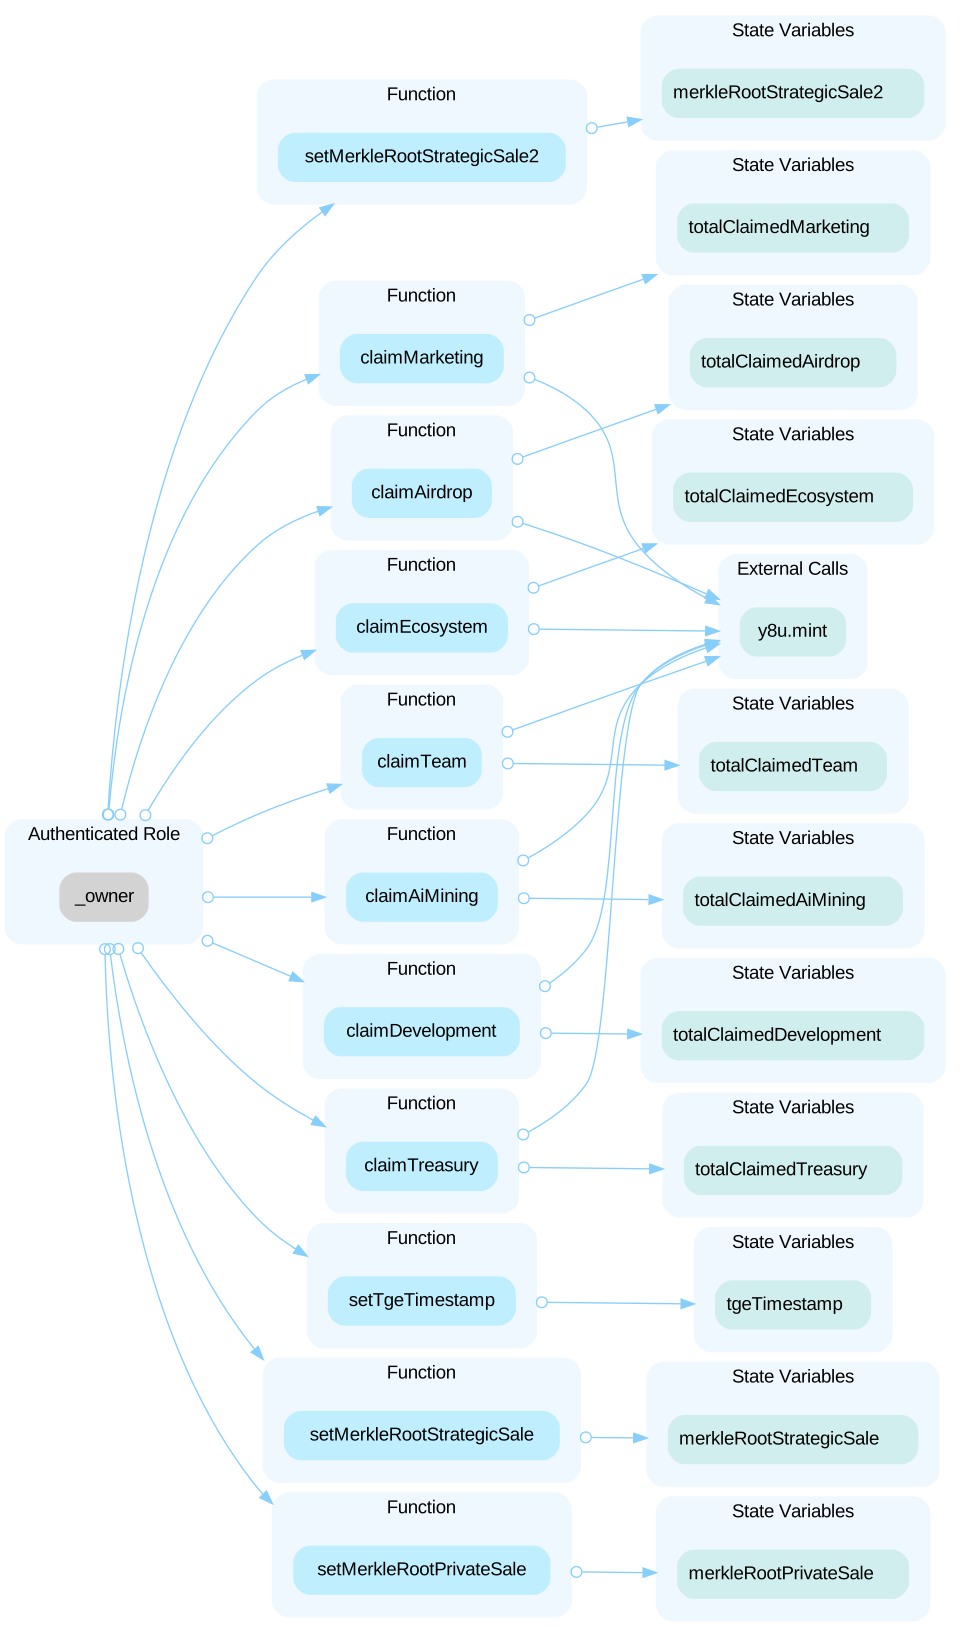 In addition, the merkle roots are determined by a merkle tree, which should allocate funds to users that in total adds up to the total allocated amounts of each sale. If the tree allocates more funds to users than this amount, then when the contract has minted the total amount for each sale it will revert if users try to claim any more tokens.
HighInitial Token DistributionOpen
85,000,000 `Y8U` tokens are sent to the address `0xe8707Ed7E5e7A230c12d4DcC037827B7F4dC355c` when deploying the contract and more can be claimed as they become vested. This can be a centralization risk as the address can distribute tokens without obtaining the consensus of the community. Any compromise to address [0xe8707Ed7E5e7A230c12d4DcC037827B7F4dC355c](https://bscscan.com/address/0xe8707Ed7E5e7A230c12d4DcC037827B7F4dC355c) that holds undistributed tokens may allow the attacker to steal and sell tokens on the market, resulting in severe damage to the project.
LowCases Not Explicitly HandledOpen
The following functions have cases that are not be explicitly handled. While these will result in a revert when `claimable` is calculated to be zero, the cases can be explicitly handled so that it reverts sooner, saving gas if called during these cases. - In the function `claimTeam()`, the cases when `monthOfDistribution < 11` are not explicitly handled. - In the function `claimMarketing()`, the cases when `monthOfDistribution < 7` are not explicitly handled. - In the function `claimTreasury()`, the cases when `monthOfDistribution < 13` are not explicitly handled. - In the function `claimDevelopment()`, the cases when `monthOfDistribution < 2` are not explicitly handled. - In the function `claimAiMining()`, the cases when `monthOfDistribution < 4` are not explicitly handled.
LowCustom Errors Can Be UsedOpen
From Solidity `v0.8.4`, there are more gas-efficient ways to explain to users why an operation failed than through strings. Using custom errors can significantly reduce the size of the deployed bytecode and reduce the gas cost when calls revert.
LowSpecific Imports Are Not UsedOpen
Specific imports are recommended to be used to avoid unpredictable pollution of the namespace. For example: import {A, B, C} from "X";
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (1)
- contracts/Y8uDistributor.sol
Part of Y8U’s security record
 Y8U
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us