Token Liquidity Foundation
CertiK reviewed Token Liquidity Foundation on 14 Mar 2023: 6 findings, 1 critical; 4 marked fixed, 2 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings6
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 1 |
| High | 1 | 0 | 1 |
| Medium | 0 | 0 | 0 |
| Low | 1 | 0 | 2 |
HighCentralization Related RisksOpen
In the contract `ERC3643Liquid`, the role `_owner` has authority over the following functions: - `initialize()` to initialize the `ERC3643Liquid` token contract; - `finalize()` to prevent changes to initialization parameters and active token; - `enableBridging()` to update the state of `bridgingEnabled`; - `active()` to set the state of `isActive` as true; - `allowPreactive()` to set the `allowedPreactive` state for the input `account`; - `approveBridgeMintBurn()` to approve mint/burn limits for bridging; - `transferExternalTokens()` to transfer tokens sent to the contract address. 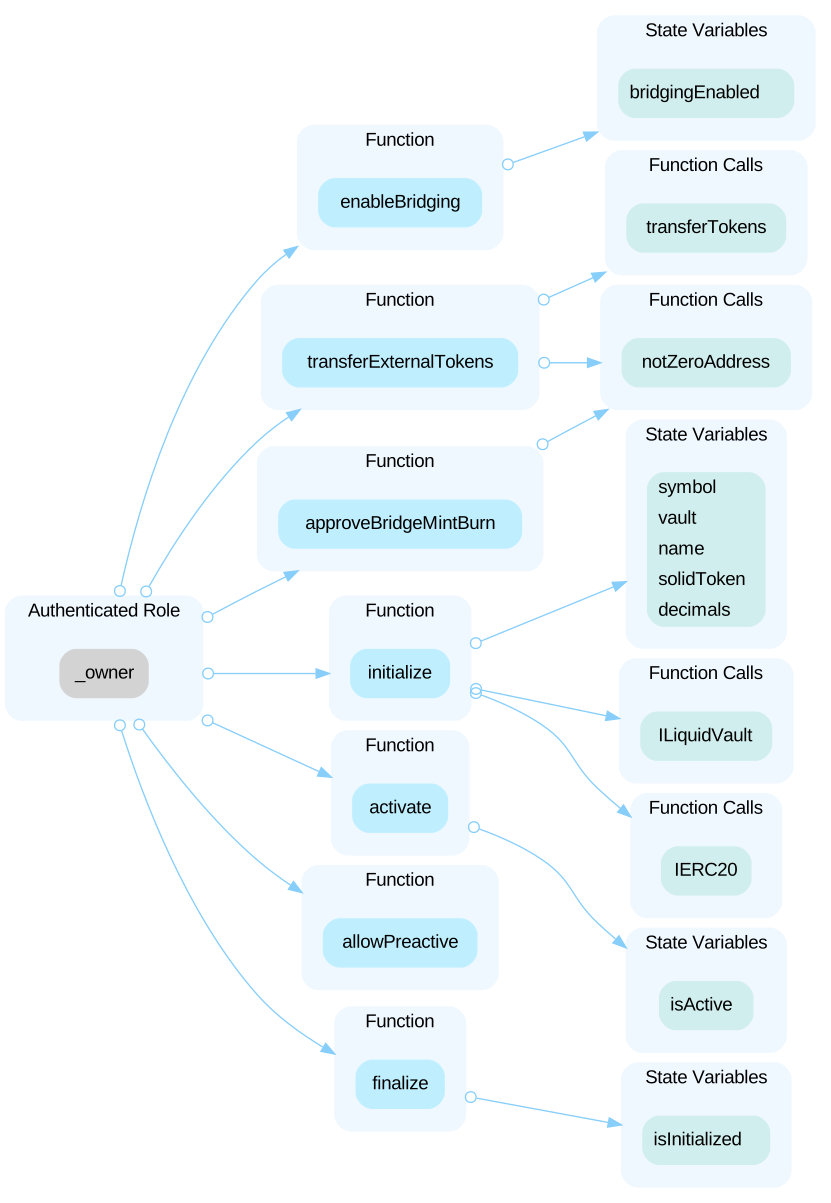 --- In the contract `ERC3643LiquidDeployer`, the role `_owner` has authority over the following functions: - `updateVaultAddress()` to update the vault address for the solid tokens; - `updateDeployers()` to update the allowed token deployers; - `transferExternalTokens()` to transfer tokens from the current contract to the address associated with the input `to`. 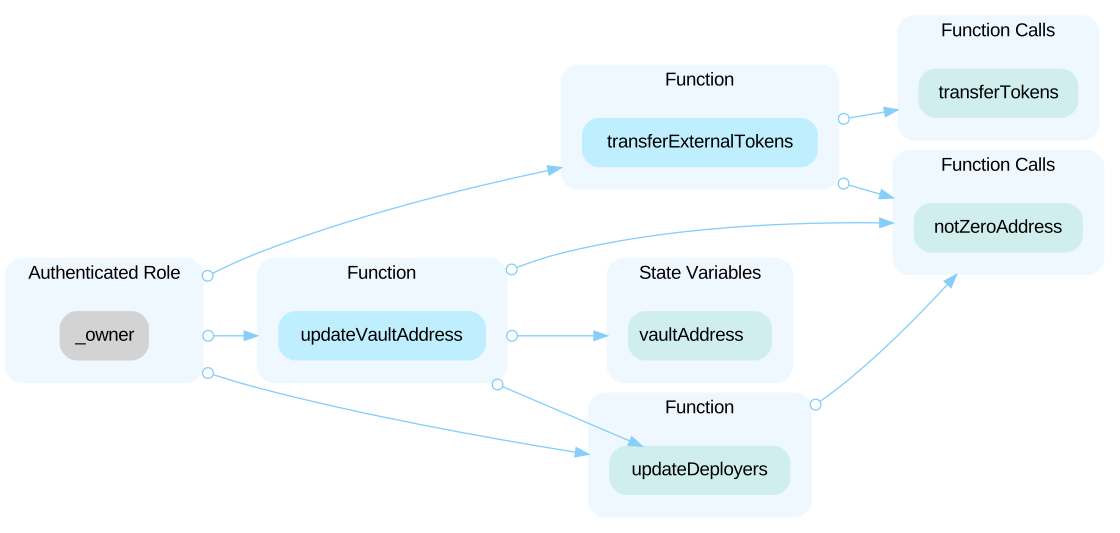 --- In the contract `LiquidVault` the role `_owner` has authority over the following functions: - `updateDeployerAddress()` to change the liquid token deployer; - `deployAndRegisterToken()` to register new solid token and deploy corresponding liquid token; - `registerToken()` to register new token pair; - `updateFees()` to update fees; - `updateFeeReceiver()` to update the recipient of fees; - `transferTokenOwnership()` to transfer the ownership to a new address associated with `newOwner`; - `transferEth()` to transfer fees to the fee recipient; - `transferExtraTokens()` to transfer extra tokens from the vault to a recipient. 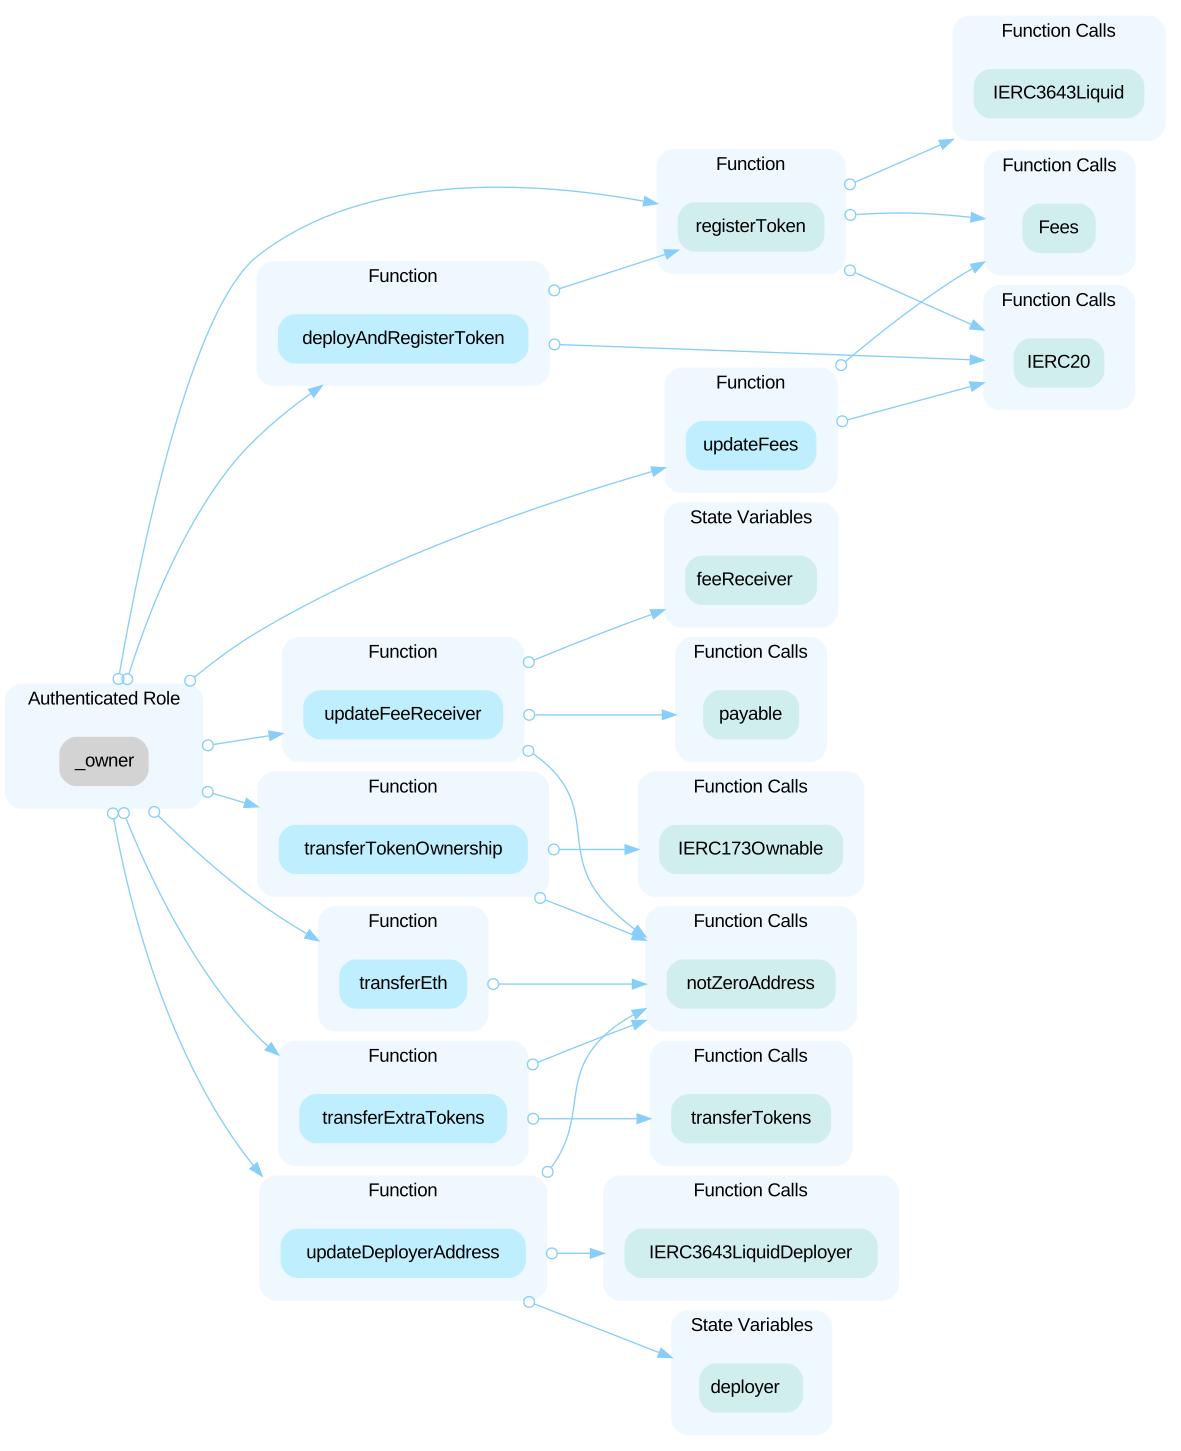 --- In the contract `NameRegistrable`, the role `_owner` has authority over the following functions: - `ensClaim()` to transfer ownership of the reverse ENS record associated with the calling account; - `ensClaimWithResolver()` transfer ownership of the reverse ENS record with the given resolver; - `ensSetName()` to set the `name()` record for the reverse ENS record associated with the calling account. 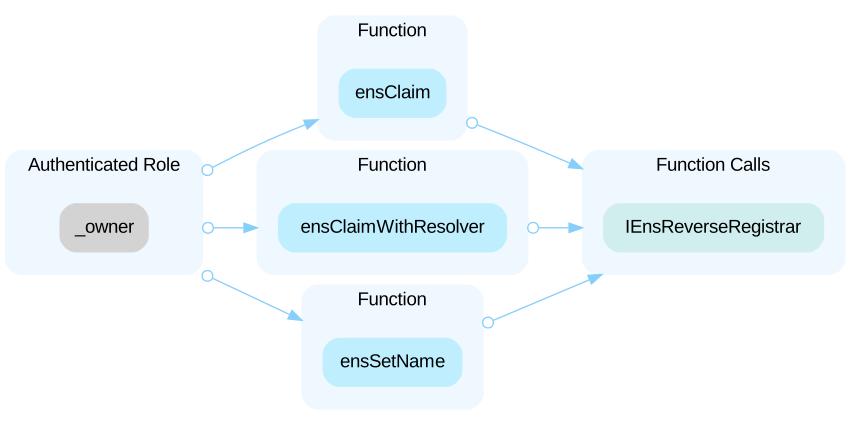 --- In the contract `VoteProxy`, the role `_owner` has authority over the following functions: - `updateGovernor()` to set the `governors` associated with the input `solidTokenAddress`; - `clearGovernor()` to clear the `governors` associated with the input `solidTokenAddress`; - `propose()` to create a new proposal; - `execute()` to execute a proposal; - `castVote()` to cast a vote on a proposal; - `castVoteWithReason()` to cast a vote on a proposal and provide a reason; - `queue()` to queue a proposal. 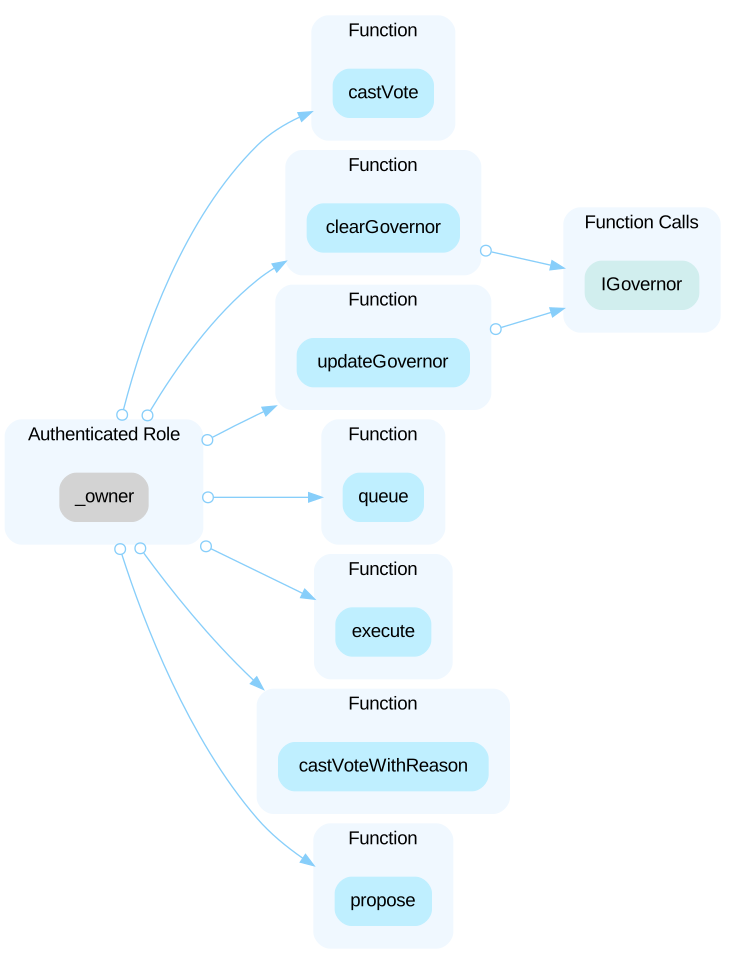 Any compromise to the `_owner` account may allow the hacker to take advantage of this authority, modify the sensitive state variables and transfer tokens to the malicious account.
LowOutdated `vaultAddress` for Deployed `liquidTokenOpen
The linked function can change the `vaultAddress`. In `ERC3643Liquid` contract, the vault contract at `vaultAddress` performs the liquify/solidify operations, converting the `liquid` and `solid` tokens for contract users. For a specific `solidToken`, `liquidToken` is also fixed due to the function `Create2.deploy()` in line 108. Neither the solid token nor the vault address can be changed after the `finalize()` function of the `ERC3643Liquid` contract is invoked. For example, a liquid token contract `X` was deployed with a solid token `USDC` and a vault `vaultA`. If the `ERC3643-LiquidDeployer` contract changes a new vault `vaultB`, the solid token `USDC` can still be registered with the existing liquid token `X` at the new vault address by calling `registerToken()`. However, the pair of `X` and `USDC` will keep using `vaultA` instead of `vaultB`.
Contracts in scope
No deployed address is recorded for this audit.
The report names a repository or files. Open the report to see its scope.
Repository and files the report names (22)
- Contracts/src/lib/Address.sol
- Contracts/src/interfaces/IERC20-Metadata.sol
- Contracts/src/interfaces/ILiquidVault.sol
- Contracts/src/lib/Context.sol
- Contracts/src/ERC3643-Liquid.sol
- Contracts/src/interfaces/IAnySwap.sol
- Contracts/src/interfaces/ICompliance.sol
- Contracts/src/interfaces/IERC3643.sol
- Contracts/src/interfaces/IERC20-Token.sol
- Contracts/src/interfaces/IERC3643-LiquidDeployer.sol
- Contracts/src/mock/ComplianceShim.sol
- Contracts/src/interfaces/IERC173-Ownable.sol
- Contracts/src/interfaces/IERC3643-Liquid.sol
- Contracts/src/interfaces/IGovernor.sol
- Contracts/src/ERC3643-LiquidDeployer.sol
- Contracts/src/lib/Create2.sol
- Contracts/src/lib/SafeERC20.sol
- Contracts/src/interfaces/IEnsReverseRegistrar.sol
- Contracts/src/LiquidVault.sol
- Contracts/src/lib/ERC173-Ownable.sol
- Contracts/src/lib/NameRegistrable.sol
- Contracts/src/lib/VoteProxy.sol
Part of Token Liquidity Foundation’s security record
 Token Liquidity Foundation
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us