Baby Doge DEX
CertiK reviewed Baby Doge (Baby Doge DEX) on 6 Oct 2022: 18 findings, 0 critical; 7 marked fixed, 11 open.
Report hosted on skynet.certik.com.
Trustblock does not review code.
Findings18
Statuses are the security firm’s own, from its report.
| Severity | Open | Acknowledged | Fixed |
|---|---|---|---|
| Critical | 0 | 0 | 0 |
| High | 2 | 0 | 1 |
| Medium | 0 | 0 | 1 |
| Low | 9 | 0 | 5 |
HighCentralization Related RiskOpen
In the contract TreasuryFeeManager.sol at the address of [0x1B6878aDfB16B949a8ceF2fB28228AFC84FCb6a8](https://bscscan.com/address/0x1B6878aDfB16B949a8ceF2fB28228AFC84FCb6a8), the role `MANAGER_ROLE` has authority over the following functions: - `addLP()` - `replaceLP()` - `unwrapTokens()` Any compromise to the `MANAGER_ROLE` account may allow a hacker to take advantage of this authority and execute sensitive functions and update the sensitive settings of the project.
HighCentralization Related RisksOpen
In the contract, `BabyDogeV2Factory`, the role, `feeToSetter`, has authority over the functions shown in the diagram below. 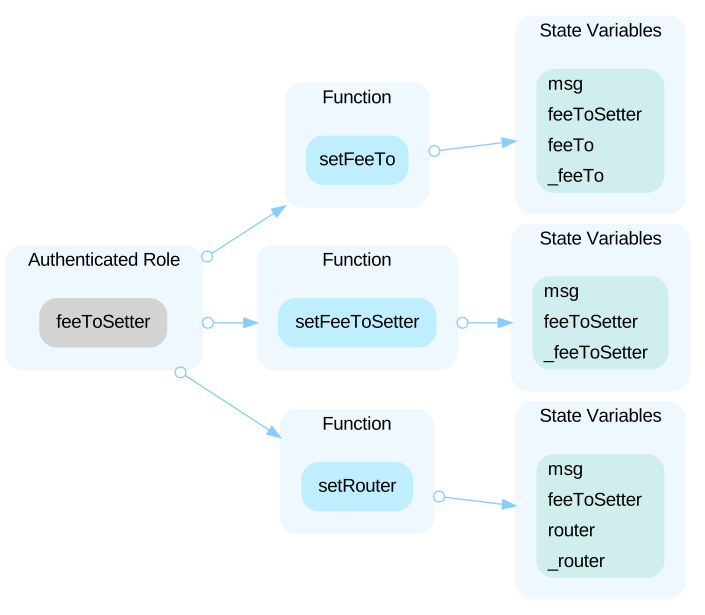 --- In the contract, `BabyDogeV2Pair`, the role, `factory`, has authority over the functions shown in the diagram below. 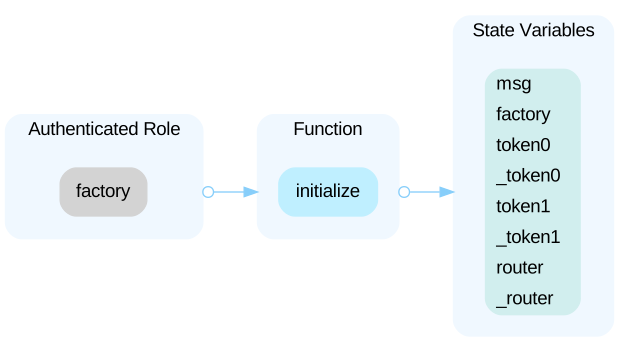 In the contract, `BabyDogeV2Pair`, the role, `router`, has authority over the functions shown in the diagram below. 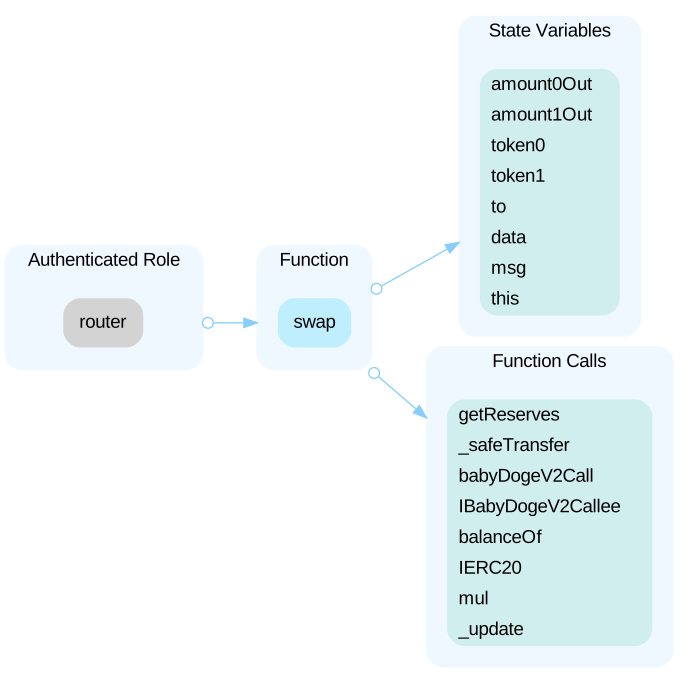 --- In the contract, `BabyDogeV2Router02`, the role, `WETH`, has authority over the functions shown in the diagram below. 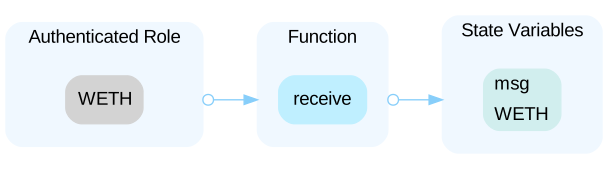 In the contract, `BabyDogeV2Router02`, the role, `feeSetter`, has authority over the functions shown in the diagram below. 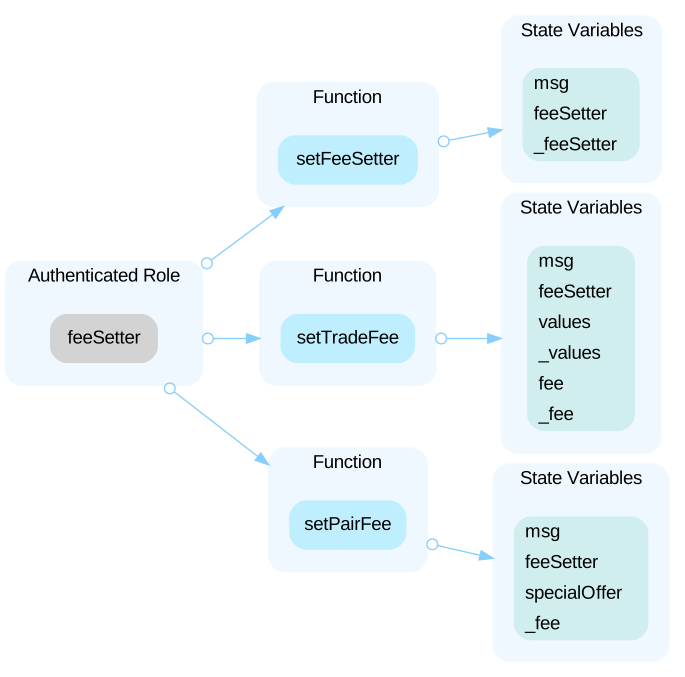 --- In the contract, `SmartChefInitializable`, the role, `SMART_CHEF_FACTORY`, has authority over the functions shown in the diagram below. 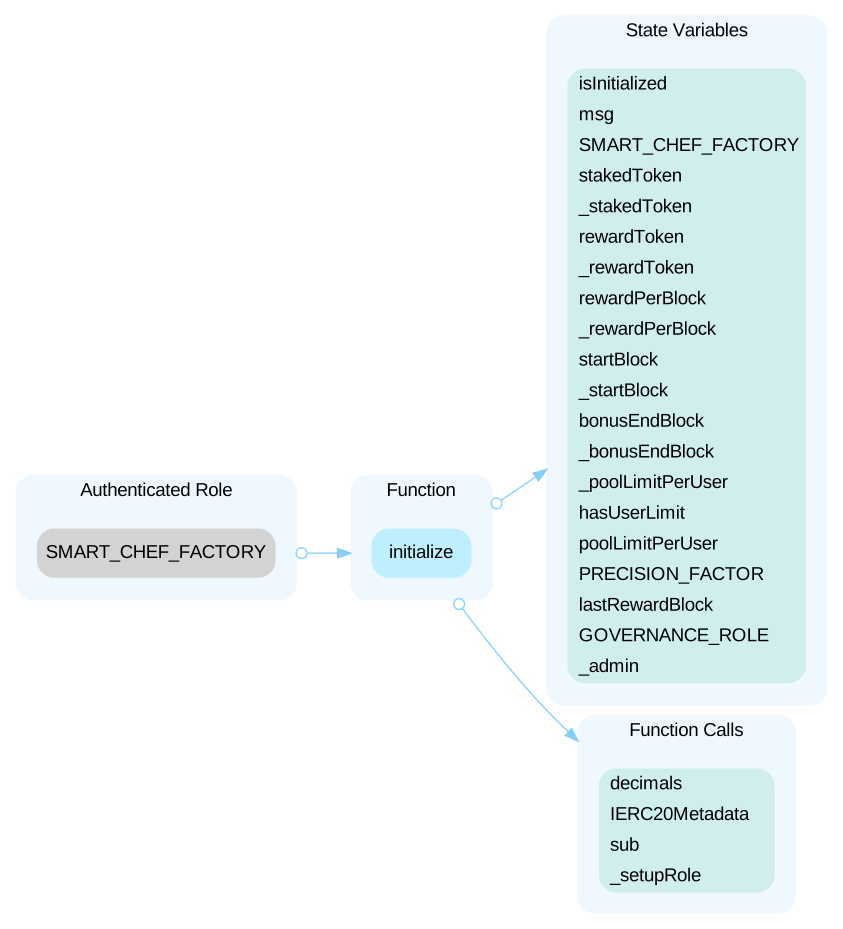 Moreover, the role,`GOVERNANCE_ROLE`, in the contract `SmartChefInitializable` has authority over the following functions: - `emergencyRewardWithdraw()` - `recoverWrongTokens()` - `stopReward()` - `updatePoolLimitPerUser()` - `updateRewardPerBlock()` - `updateStartAndEndBlocks()` --- In the contract, `dexFeeManager`, the role,`GOVERNANCE_ROLE`, in the contract `SmartChefInitializable` has authority over the following functions: - `addLP()` - `setAllocationSettings()` - `setTreasuryAddress()` - `setBuybackTokens()` - `replaceLP()` - `swaptoBuyBack()` - `sendBuyBackToBurnWallet()` - `withdrawETH()` - `withdrawERC20()` --- Any compromise to the privileged account may allow the hacker to take advantage of this authority and update the sensitive settings and execute sensitive functions of the project.
LowImproper Usage of `public` and `external` TypeOpen
`public` functions that are never called by the contract could be declared as `external`. `external` functions are more efficient than `public` functions.
LowIncompatibility With Deflationary TokensOpen
When users add or remove LP tokens into the router, and the `mint` and `burn` operations are performed. When transferring standard ERC20 deflationary tokens, the input amount may not be equal to the received amount due to the charged transaction fee. As a result, the amount inconsistency will occur and the transaction may fail due to the validation checks.
LowMissing Emit EventsOpen
There should always be events emitted in the sensitive functions that are controlled by centralization roles.
LowMissing Error MessagesOpen
The **require** can be used to check for conditions and throw an exception if the condition is not met. It is better to provide a string message containing details about the error that will be passed back to the caller.
LowPotential Sandwich AttacksOpen
A sandwich attack might happen when an attacker observes a transaction swapping tokens or adding liquidity without setting restrictions on slippage or minimum output amount. The attacker can manipulate the exchange rate by frontrunning (before the transaction being attacked) a transaction to purchase one of the assets and make profits by backrunning (after the transaction being attacked) a transaction to sell the asset. The following functions are called without setting restrictions on slippage or minimum output amount, so transactions triggering these functions are vulnerable to sandwich attacks, especially when the input amount is large: - `swapExactTokensForTokens()` - `swapExactTokensForTokensSupportingFeeOnTransferTokens()`
LowUnlocked Compiler VersionOpen
The contract has unlocked compiler version. An unlocked compiler version in the source code of the contract permits the user to compile it at or above a particular version. This, in turn, leads to differences in the generated bytecode between compilations due to different compiler versions. This can lead to an ambiguity when debugging as compiler specific bugs may occur in the codebase that would be hard to identify over a span of multiple compiler versions rather than a specific one.
LowUnnecessary Array as CounterOpen
The usage of `allPairs` array is as a counter to maintain the number of created pairs.
LowVariables That Could Be Declared As `constant`Open
The highlighted variables could be declared as `constant` since these state variables are never modified.
Show 1 more
LowVariables That Could Be Declared as `immutable`Open
The highlighted variables assigned in the constructor can be declared as `immutable`. Immutable state variables can be assigned during contract creation but will remain constant throughout the lifetime of a deployed contract. A big advantage of immutable variables is that reading them is significantly cheaper than reading from regular state variables since they will not be stored in storage.
Contracts in scope2
| Address | Chain | Source code |
|---|---|---|
| 0xbda7c402f9de8ad737cedc3ab7cbfecd53f29c74 | Chain: BNB Chain | Source code: Verified source |
| 0x1b6878adfb16b949a8cef2fb28228afc84fcb6a8 | Chain: BNB Chain | Source code: Verified source |
Part of Baby Doge’s security record
 Baby Doge
Security firm
 CertiK
1,044 projects reviewed · 1,375 reports · latest May 2025
See CertiK’s auditsSomething wrong on this page? A missing report, a wrong date, a finding that was fixed since. Tell us and we check it against its source.
Tell us